> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/active-directory/enumeration/ldapsearch.md).
# LDAP-Suche
Sicherheitsnotizen zur LDAP-Suche für Active Directory, einschließlich Enumerierung, Kerberos, Anmeldedaten, ACL-Missbrauch, lateraler Bewegung, Ausnutzungsablauf und Validierungsschritte.
### Anonyme LDAP-Zugriffe testen
{% code overflow="wrap" %}
```bash
ldapsearch -x -H ldap://172.16.0.100 -b "DC=whoami,DC=local"
```
{% endcode %}
Dieser Befehl versucht, LDAP ohne Authentifizierung abzufragen.
In vielen modernen Umgebungen ist anonymer Zugriff eingeschränkt oder deaktiviert.
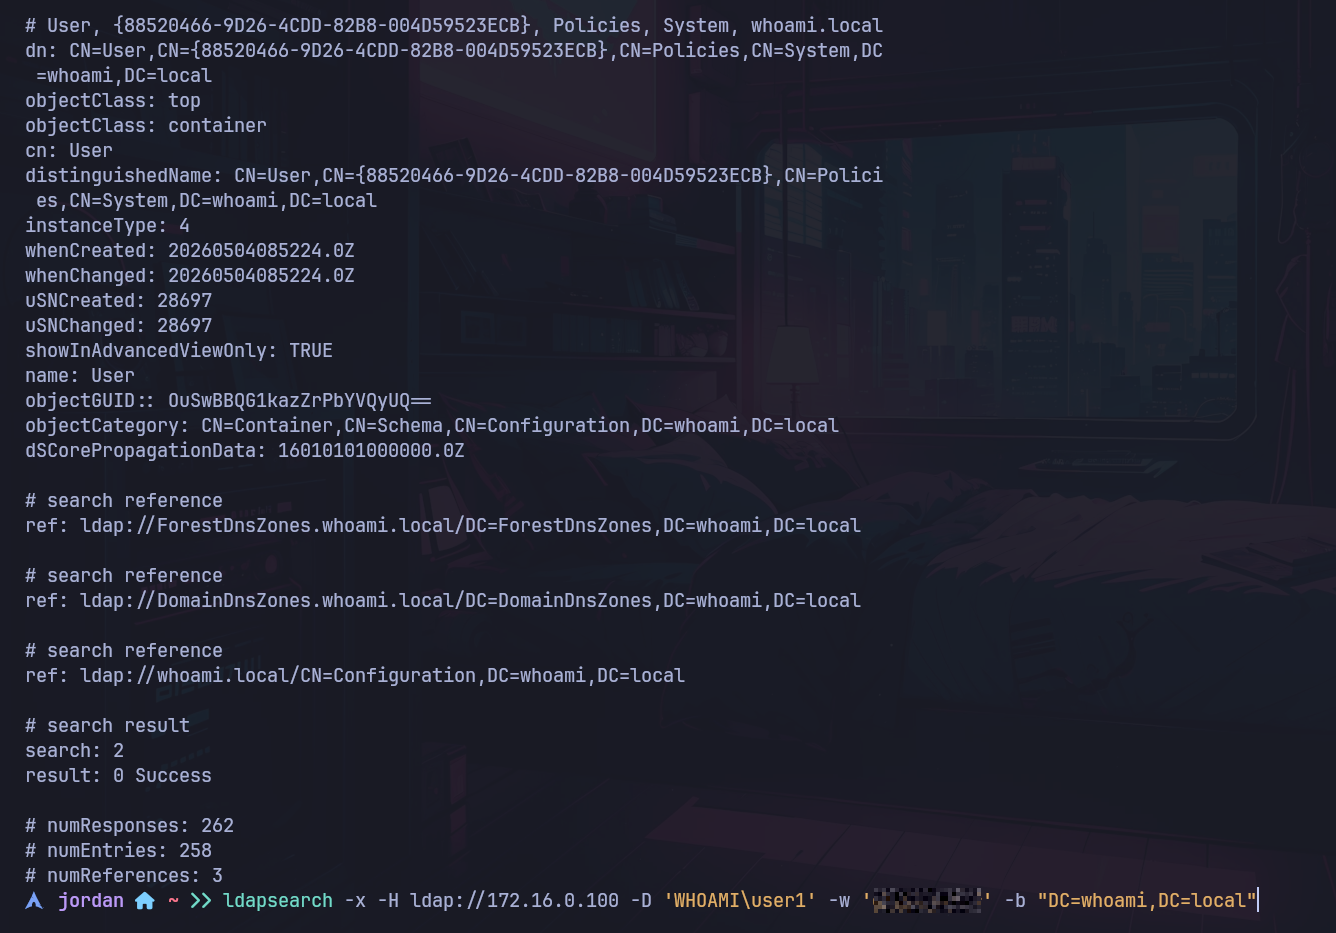
### LDAP-Verbindung mit Anmeldedaten
{% code overflow="wrap" %}
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "DC=whoami,DC=local"
```
{% endcode %}
Erläuterung:
| Option | Rolle |
| ------ | ---------------------------------- |
| `-x` | Einfache Authentifizierung |
| `-H` | LDAP-Serveradresse |
| `-D` | Zur Anmeldung verwendete Identität |
| `-w` | Passwort |
| `-b` | DN-Datenbank durchsuchen |
### Benutzer auflisten in `CN=Users`
{% code overflow="wrap" %}
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "CN=Users,DC=whoami,DC=local"
```
{% endcode %}
Hier suchen wir im Standardcontainer `Users`.
### Eine OU auflisten
Wenn sich die Benutzer in einer organisatorischen Einheit befinden, verwenden wir `OU` anstelle von `CN`:
{% code overflow="wrap" %}
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "OU=Users,DC=whoami,DC=local"
```
{% endcode %}
Wichtiger Unterschied:
| Element | Bedeutung |
| ------- | ------------------------------------------ |
| `CN` | Common Name, Container oder Standardobjekt |
| `OU` | Organisationseinheit |
| `DC` | Domänenkomponente |
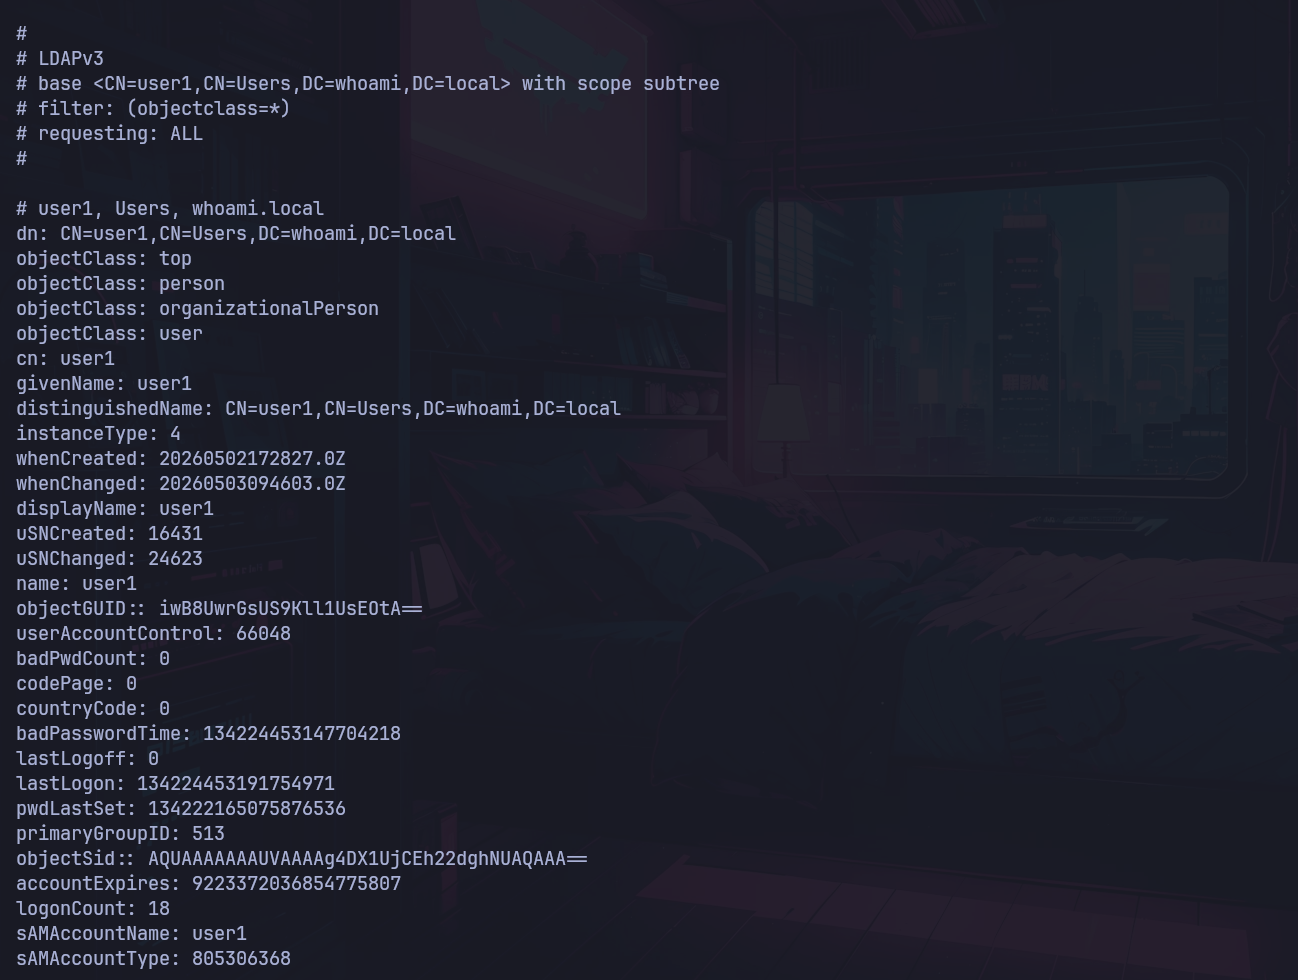
### Nach einem bestimmten Benutzer suchen
{% code overflow="wrap" %}
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "CN=user1,CN=Users,DC=whoami,DC=local"
```
{% endcode %}
Dieser Befehl zielt direkt auf das `user1` Objekt.
### Computer auflisten
{% code overflow="wrap" %}
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "CN=computers,DC=whoami,DC=local"
```
{% endcode %}
Bitte beachten: In Active Directory heißt der Standardcontainer im Allgemeinen `CN=Computers`.
### Die integrierte Administratorengruppe auflisten
{% code overflow="wrap" %}
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "CN=Administrators,CN=Builtin,DC=whoami,DC=local"
```
{% endcode %}
Dieser Befehl zielt auf die integrierte lokale Gruppe `Administrators` im `Builtin` Container.
### Den DN eines Benutzers finden
```bash
ldapsearch -x -H ldap://172.16.0.100 -D 'WHOAMI\user1' -w 'password' -b "CN=user1,CN=Users,DC=whoami,DC=local" | grep dn
```
Beispielergebnis:
```bash
CN=user1,CN=Users,DC=whoami,DC=local
```
* Das **DN**oder **Distinguished Name**, ist der vollständige LDAP-Pfad des Objekts.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/active-directory/enumeration/ldapsearch.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.