> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/business-logic/inconsistent-security-controls.md).
# Inkonsistente Sicherheitskontrollen
Notizen zu inkonsistenten Sicherheitskontrollen für die Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungsablauf, Payload-Tests, Burp-Suite-Validierung und Behebungskontext.
### Inkonsistente Sicherheitskontrollen
**Lernziel**
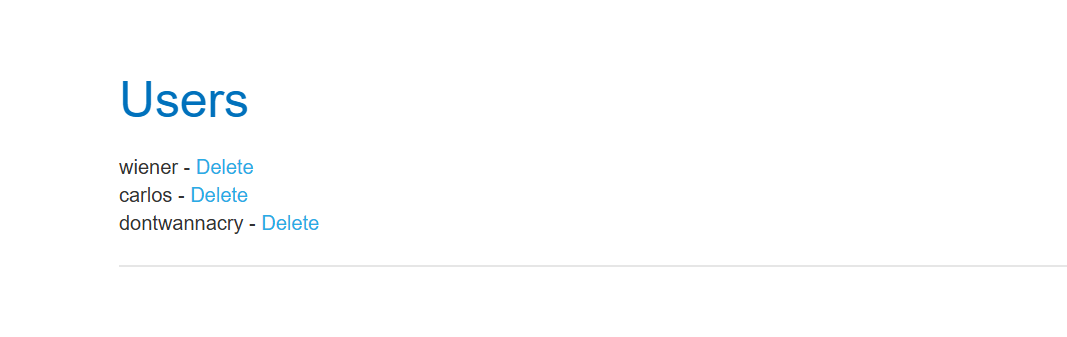
Dieses Labor weist einen logischen Fehler im Zusammenhang mit inkonsistenten Sicherheitsprüfungen auf. / Beliebige Benutzer können auf administrative Funktionen zugreifen, die normalerweise Mitarbeitern des Unternehmens vorbehalten sind. / Ziel ist es, auf das Administrationspanel zuzugreifen und den Benutzer zu löschen **carlos**.
**Erste Beobachtung**
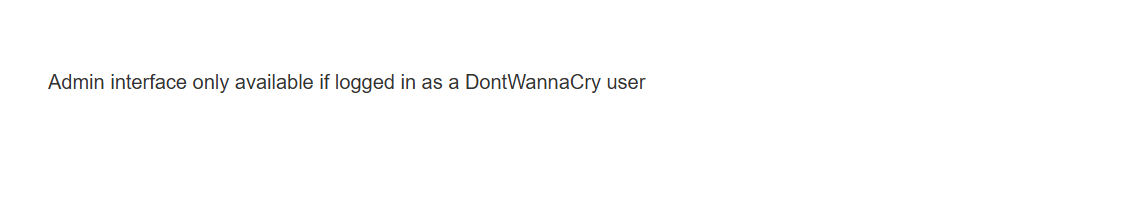
Beim direkten Versuch, auf die Administrationsoberfläche zuzugreifen, erscheint die folgende Meldung:
> *Admin-Oberfläche nur verfügbar, wenn Sie als DontWannaCry-Benutzer angemeldet sind*
Zugriff auf `/admin` ist daher auf Benutzer beschränkt, die zur **DontWannaCry** Domäne vorhanden sind.
**Registrierungsversuch**
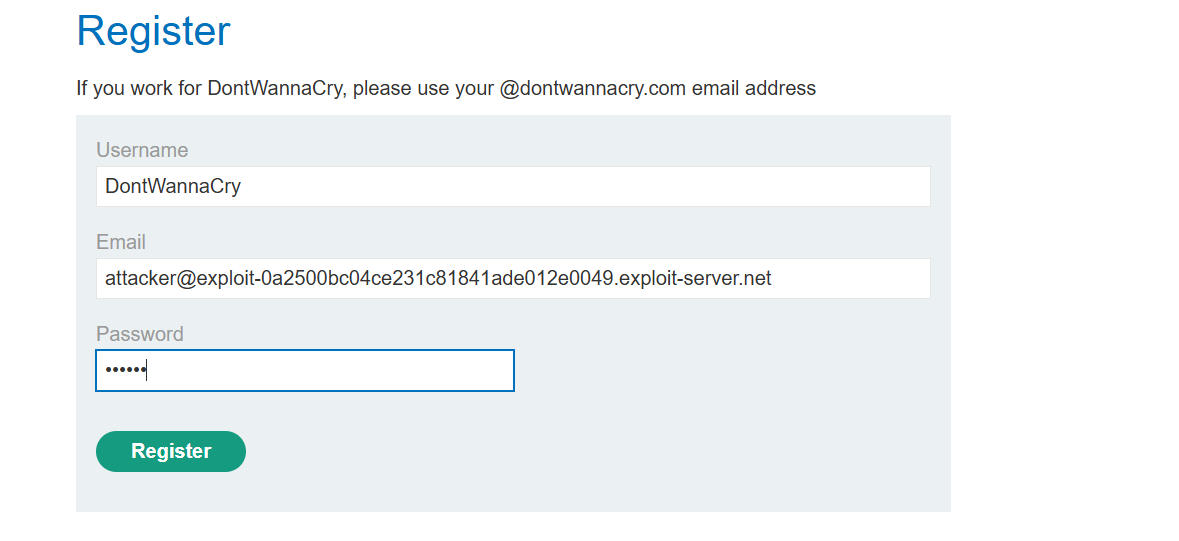
Ein neuer Benutzer wird mit folgenden Daten registriert:
* **Benutzername**: `DontWannaCry` (bereits vorhanden)
* **E-Mail-Adresse**: eine vom Angreifer kontrollierte Adresse/ `attacker@exploit-0a2500bc04ce231c81841ade012e0049.exploit-server.net`
Nach dem Absenden des Formulars zeigt die Anwendung an:
> *Bitte prüfen Sie Ihre E-Mails auf Ihren Link zur Kontoregistrierung*
**Kontobestätigung**
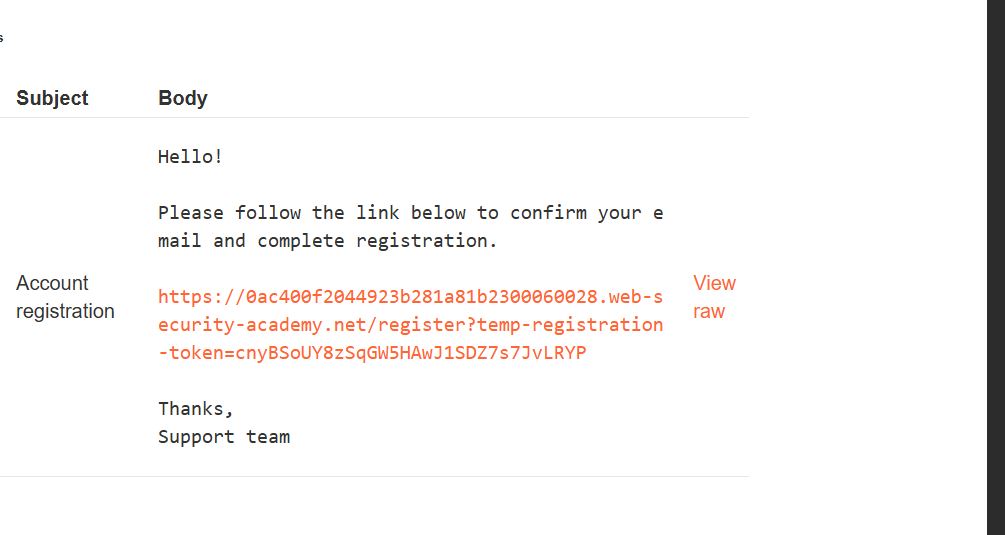
Es wird eine Bestätigungs-E-Mail mit einem Link empfangen, der ein Token enthält.
Verwendet werden die folgenden Zugangsdaten:
* **Benutzer**: `DontWannaCry`
* **Passwort**: `jordan`
Die Verbindung funktioniert ordnungsgemäß.
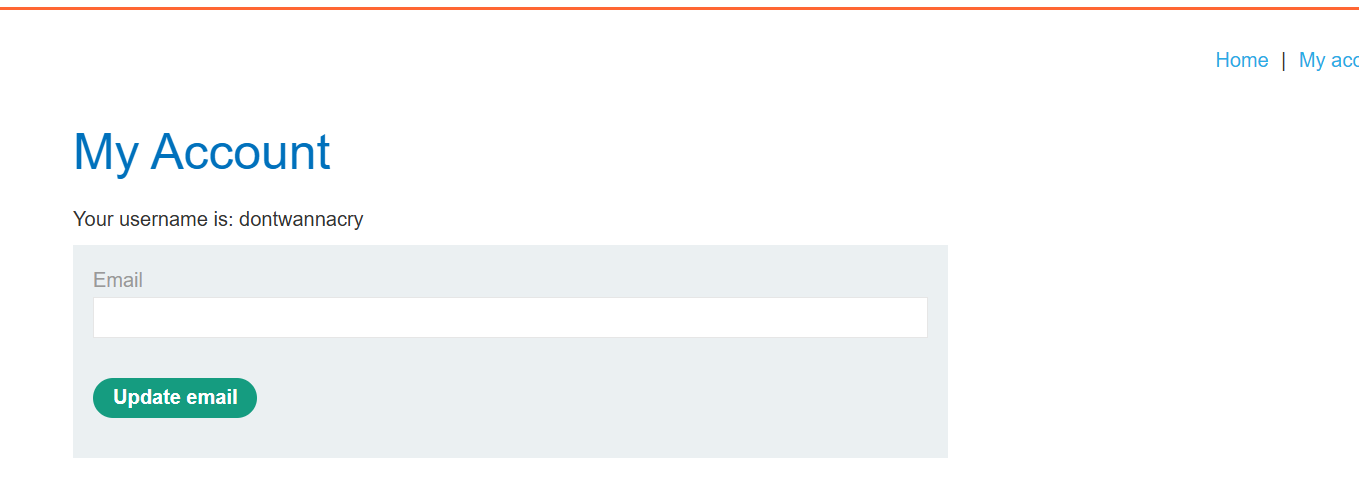
**Änderung der E-Mail-Adresse**
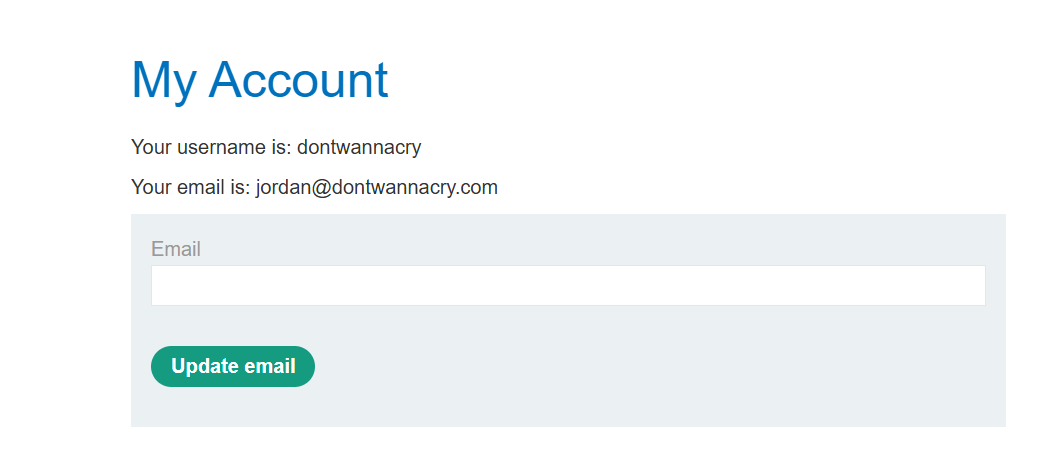
Nach der Anmeldung ändern Sie die E-Mail-Adresse des Kontos ohne zusätzliche Validierung mithilfe von:
```bash
jordan@dontwannacry.com
```
Die Rechtmäßigkeit dieser Änderung wird nicht überprüft.
**Zugriff auf die Administrationsoberfläche**
Nach der Änderung der E-Mail wird der Benutzer nun als zur Domain gehörig betrachtet **DontWannaCry**. / Zugriff auf die `/admin` Oberfläche wird dann erlaubt.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/business-logic/inconsistent-security-controls.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.