> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/essential-skills/quick-detection-with-a-target-scan.md).
# Schnelle Erkennung mit einem Zielscan
Notizen zur schnellen Erkennung mit einem Zielscan für die Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungsablauf, Payload-Tests, Burp-Suite-Validierung und Behebungskontext.
### Schwachstellen schnell mit gezieltem Scannen entdecken
#### Laborkontext
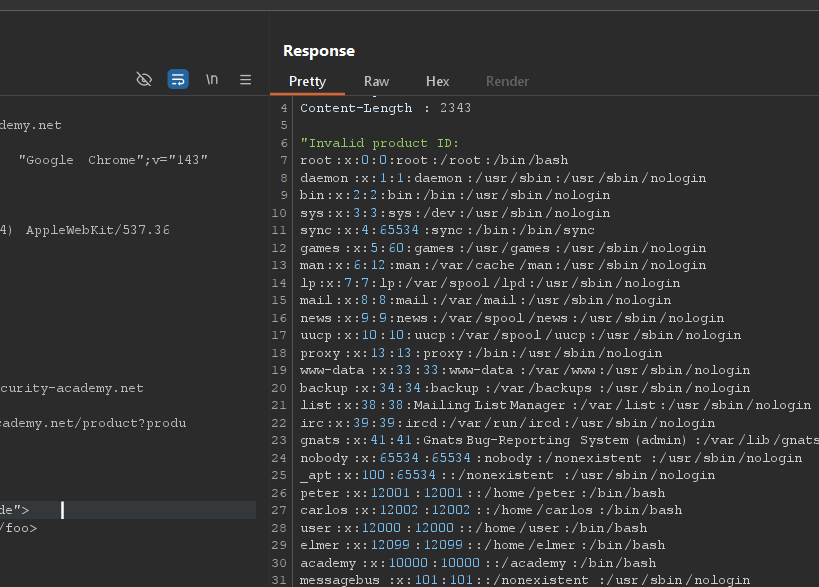
Dieses Lab enthält eine Schwachstelle, mit der man **beliebige Dateien auf dem Server zu lesen**. / Das Ziel ist es, **den Inhalt der `/etc/passwd` Datei in weniger als 10 Minuten wiederherzustellen**.
Aufgrund dieser Zeitvorgabe wird empfohlen, **Burp Scanner** anstatt eines vollständigen Anwendungs-Audits.
#### Zeitbeschränkung
* Ein \*\*10-Minuten-Timer\*\* ist vom Start des Labs an aktiv.
* Ein vollständiger Site-Scan kann zu langsam sein.
* Daher ist es vorzuziehen, **potenziell verwundbare Einstiegspunkte gezielt anzuvisieren**.
#### Vorgehensweise
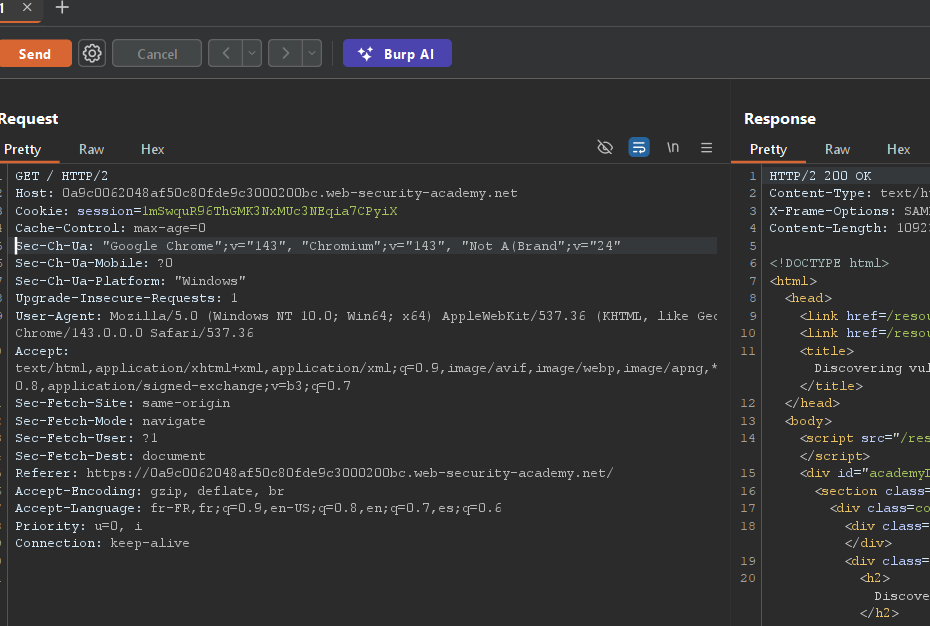
1. **Fange eine relevante HTTP-Anfrage ab** mit Burp Proxy ab.
Analysiere schnell die Logik der Abfrage, um einen interessanten Endpunkt zu identifizieren.
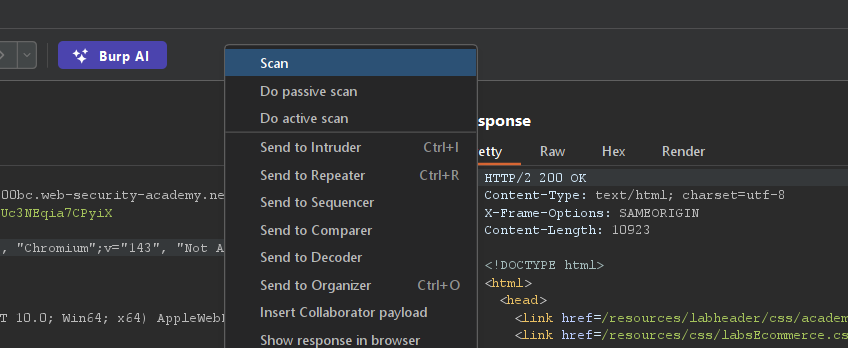
Führe einen gezielten Scan über **Burp Scanner** diese spezifische Anfrage aus.
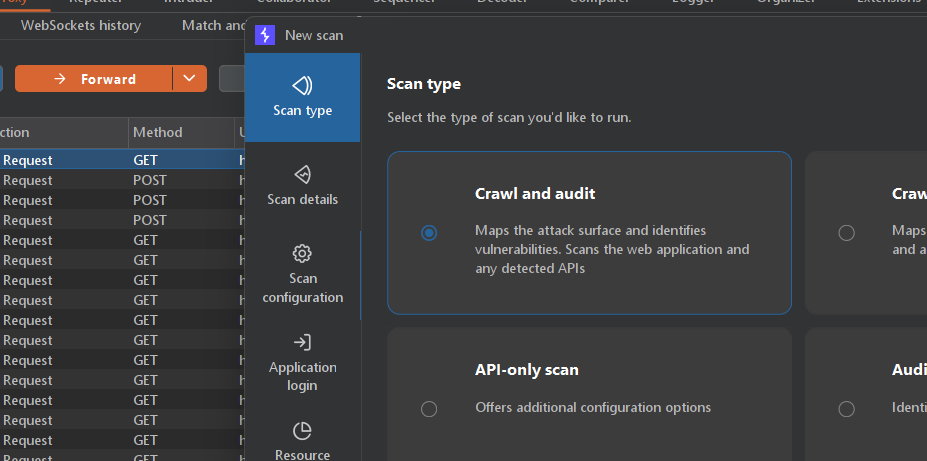
#### Burp-Scan-Konfiguration
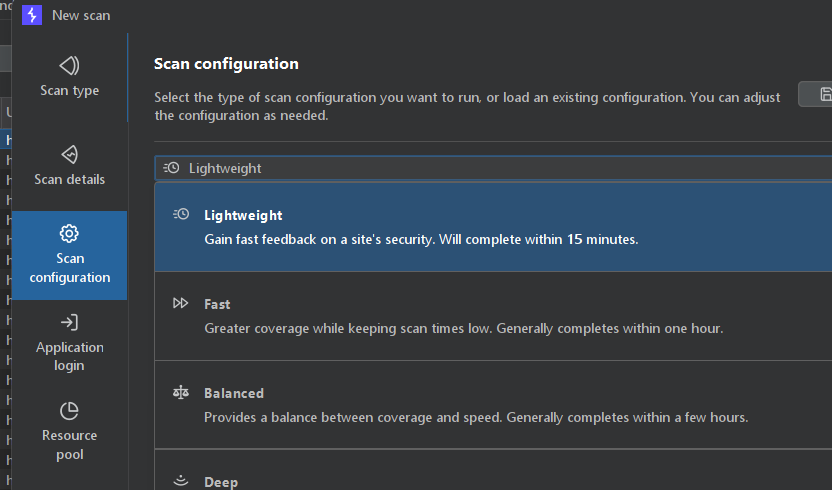
* Ausgewählter Scan-Typ: **Crawlen und Prüfen**
* Modus: **Schneller Scan**
Ziel: schnell einen ausnutzbaren Angriffsvektor identifizieren
#### Schwachstelle identifiziert
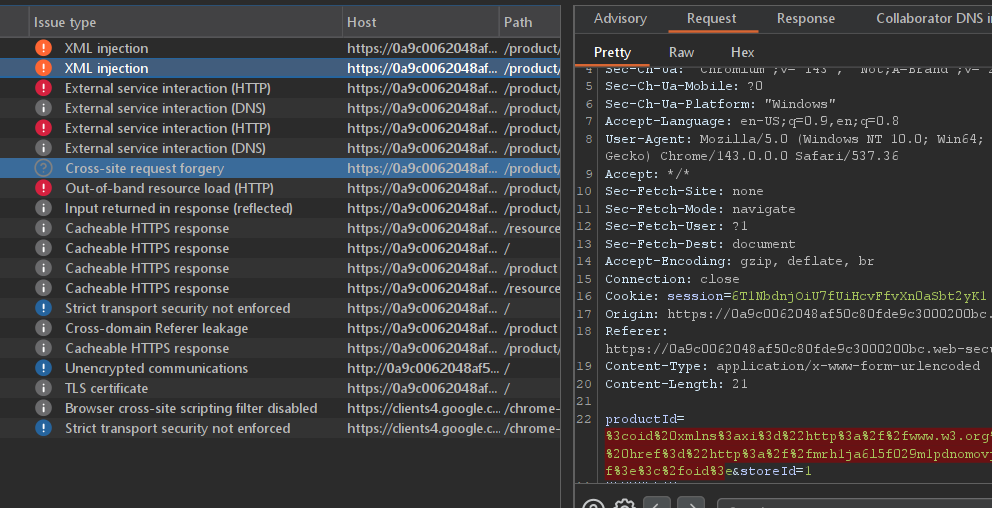
Der Scan zeigt eine Schwachstelle des Typs **XML-Injektion (XInclude)**.
Vom Burp Scanner erkannte Initial-Payload:
{% code overflow="wrap" %}
```xml
```
{% endcode %}
Dies bestätigt, dass der Server **XInclude** Entitäten ohne Einschränkung verarbeitet.
#### Ausnutzung: Lesen von `/etc/passwd`
Die Payload wird geändert, um eine lokale Systemdatei einzuschließen:
{% code overflow="wrap" %}
```http
productId=
id>&storeId=1
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/essential-skills/quick-detection-with-a-target-scan.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.