> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/active-directory/acl-security-descriptors-and-permissions/permissions-audit-and-permission-entries.md).
# Permisos, auditoría y ACE
Notas de seguridad de Active Directory para Permisos, auditoría y ACE, que cubren enumeración, Kerberos, credenciales, abuso de ACL, movimiento lateral, flujo de explotación y pasos de validación.
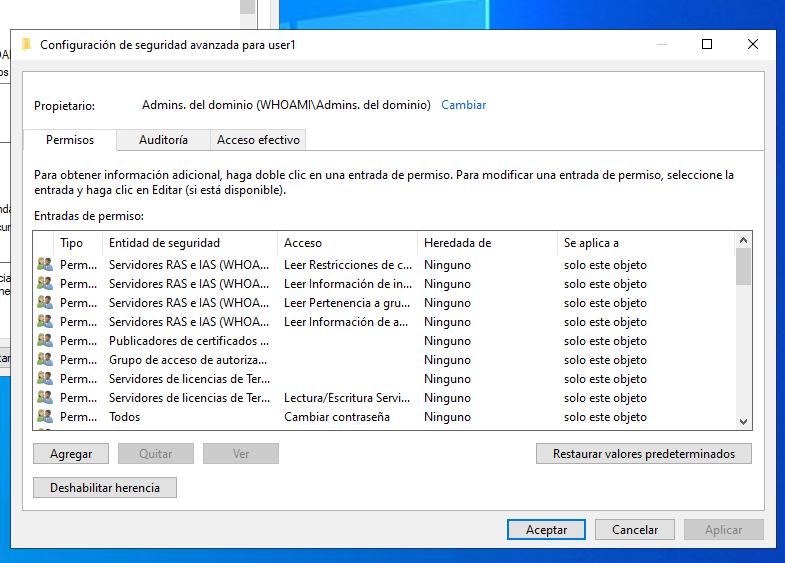
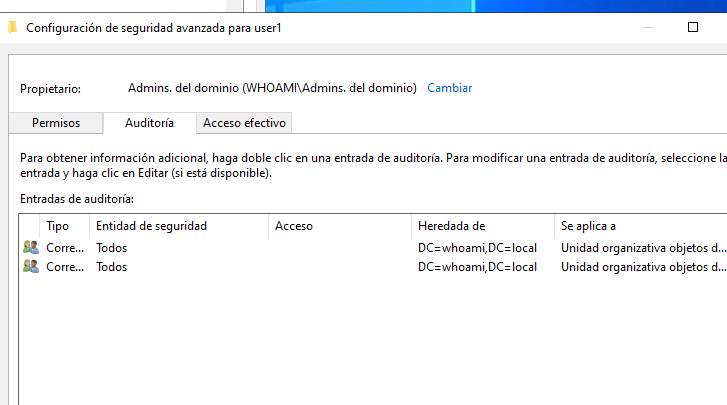
En la configuración de seguridad avanzada de un objeto de Active Directory, generalmente hay varias partes importantes.
#### Permisos
El **Permisos** la pestaña muestra los usuarios o grupos que tienen derechos sobre el objeto.
Ejemplos de permisos posibles:
* leer el objeto;
* modificar ciertos atributos;
* cambiar el propietario;
* modificar permisos;
* añadir miembros a un grupo;
* eliminar el objeto.
#### Auditoría
El **Auditoría** la pestaña permite definir qué accesos deben registrarse.
Se utiliza para hacer seguimiento de cuándo un usuario realiza ciertas acciones sobre el objeto.
Ejemplos:
* intento de lectura;
* modificación;
* cambio de permisos;
* eliminación;
* Acceso denegado.
#### Entradas de permisos
**Entradas de permiso** corresponden a las líneas detalladas presentes en una ACL.
Cada entrada se denomina un **ACE**, o **Entrada de control de acceso**.
Un ACE indica:
* el usuario o grupo en cuestión;
* el tipo de acceso;
* los derechos concedidos;
* el objeto en cuestión;
* si el permiso se hereda o no.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/active-directory/acl-security-descriptors-and-permissions/permissions-audit-and-permission-entries.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.