> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/reconnaissance/web-fuzzing.md).
# Fuzzing web
Metodología de fuzzing web para descubrir directorios, archivos, extensiones, parámetros y recursos expuestos ocultos con herramientas como Gobuster y Wfuzz.
El fuzzing web ayuda a descubrir directorios, archivos, extensiones, parámetros, hosts virtuales y recursos expuestos ocultos durante el reconocimiento de aplicaciones web.
{% hint style="info" %}
Existen muchas herramientas y métodos para descubrir directorios y archivos en sitios web, ya sea desde la línea de comandos o mediante recursos en línea. Estos son los principales enfoques y las herramientas más útiles:
{% endhint %}
## Gobuster:
> Gobuster es una herramienta rápida y eficaz para realizar ataques de fuerza bruta en directorios y archivos de sitios web.
### **Solo directorios:**
```bash
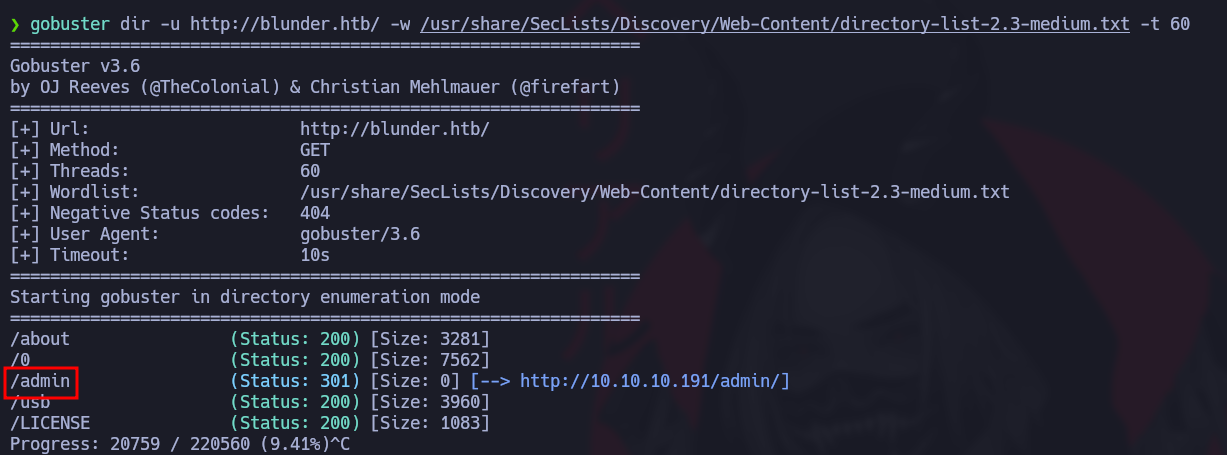
gobuster dir -u http://website.com/ -w /usr/share/SecLists/Discovery/Web-Content/directory-list-2.3-medium.txt -t 100
```
* **-u**: URL del sitio objetivo.
* **-w**: Ruta del archivo que contiene la lista de palabras clave (wordlist).
* **-t**: Número de hilos usados para la búsqueda.
### **Archivos con extensiones específicas:**
```bash
gobuster dir -u http://website.com/ -w /usr/share/SecLists/Discovery/Web-Content/quickhits.txt -t 100 -x html,php,txt
```
* **-x**: Especifica las extensiones que se deben buscar.
### **Añadir filtros específicos a las respuestas:**
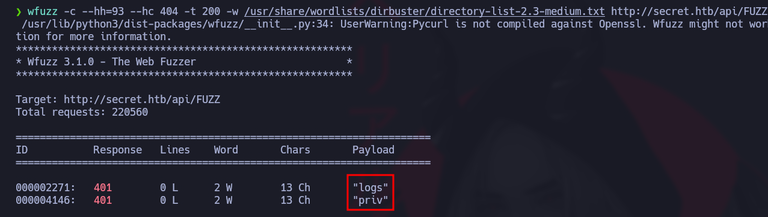
* **-hh**: Filtra por tamaño del cuerpo en bytes.
* **-hc**: Excluye respuestas con códigos de estado específicos (por ejemplo, 404).
## Wfuzz:
> Wfuzz permite búsquedas avanzadas y configurables mediante ataques de fuerza bruta, ya sea para directorios o parámetros en las URL.
### **Solo directorios:**
```bash
wfuzz -c -t 100 -w /usr/share/SecLists/Discovery/Web-Content/directory-list-2.3-medium.txt http://website.com/FUZZ
```
* **-c**: Muestra la salida en color.
* **FUZZ**: Indica dónde se inyectarán las palabras clave.
### **Archivos con extensiones específicas:**
```bash
wfuzz -c -t 100 -w /usr/share/SecLists/Discovery/Web-Content/quickhits.tx -z list,html-txt-php http://website.com/
```
* **-z**: Define extensiones adicionales que se usarán en la búsqueda (list permite definir varias extensiones).
### **Valores de parámetros dinámicos (`?product_id=`) :**
```bash
wfuzz -c -t 100 -z range,1-200000 'http://website.com/shop/buy/detail?product_id=FUZZ'
```
* **-z range,1-200000**: Realiza un ataque de fuerza bruta con un rango de números del 1 al 200,000.
## **Métodos adicionales:**
### Descubrimiento en fuentes públicas:
Si prefieres métodos visuales de fuentes públicas, utiliza el catálogo mantenido en [Herramientas de OSINT e investigación](/es/hacking-tools/osint.md).
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/reconnaissance/web-fuzzing.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.