> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/fr/active-directory/acl-security-descriptors-and-permissions/permissions-audit-and-permission-entries.md).
# Permissions, audit et ACE
Notes de sécurité Active Directory pour Permissions, audit et ACE, couvrant l'énumération, Kerberos, les identifiants, l'abus d'ACL, le mouvement latéral, le flux d'exploitation et les étapes de validation.
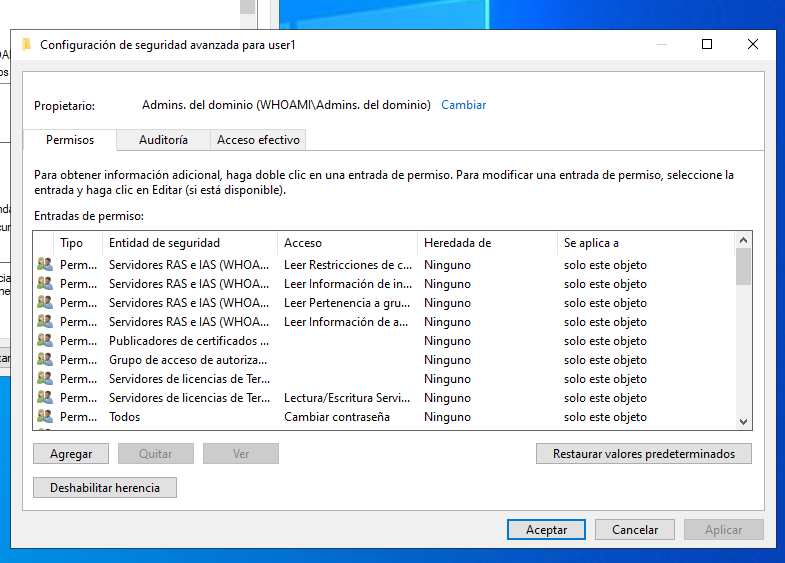
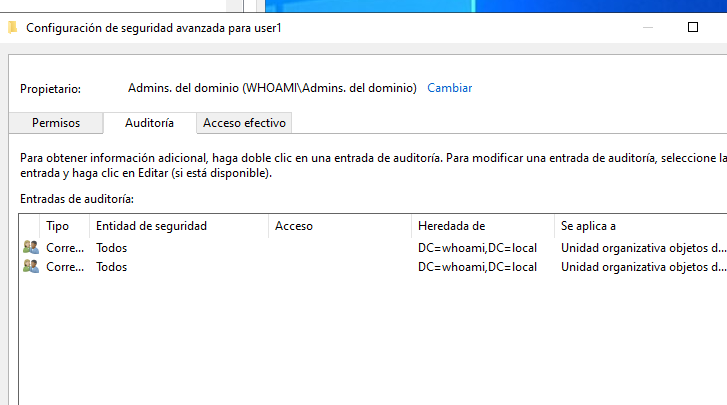
Dans les paramètres de sécurité avancés d’un objet Active Directory, il existe généralement plusieurs éléments importants.
#### Autorisations
Le **Autorisations** affiche les utilisateurs ou les groupes qui disposent de droits sur l’objet.
Exemples d’autorisations possibles :
* lire l’objet ;
* modifier certains attributs ;
* changer le propriétaire ;
* modifier les autorisations ;
* ajouter des membres à un groupe ;
* supprimer l’objet.
#### Audit
Le **Audit** onglet vous permet de définir quels accès doivent être journalisés.
Il est utilisé pour suivre quand un utilisateur effectue certaines actions sur l’objet.
Exemples :
* tentative de lecture ;
* modification ;
* changement d’autorisation ;
* suppression ;
* Accès refusé.
#### Entrées d’autorisations
**Entrées d’autorisations** correspondent aux lignes détaillées présentes dans une ACL.
Chaque entrée est appelée une **ACE**, ou **Entrée de contrôle d’accès**.
Une ACE indique :
* l’utilisateur ou le groupe concerné ;
* le type d’accès ;
* les droits accordés ;
* l’objet concerné ;
* si l’autorisation est héritée ou non.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/fr/active-directory/acl-security-descriptors-and-permissions/permissions-audit-and-permission-entries.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.